


19296 results
 Pierluigi Paganini
 April 21, 2025
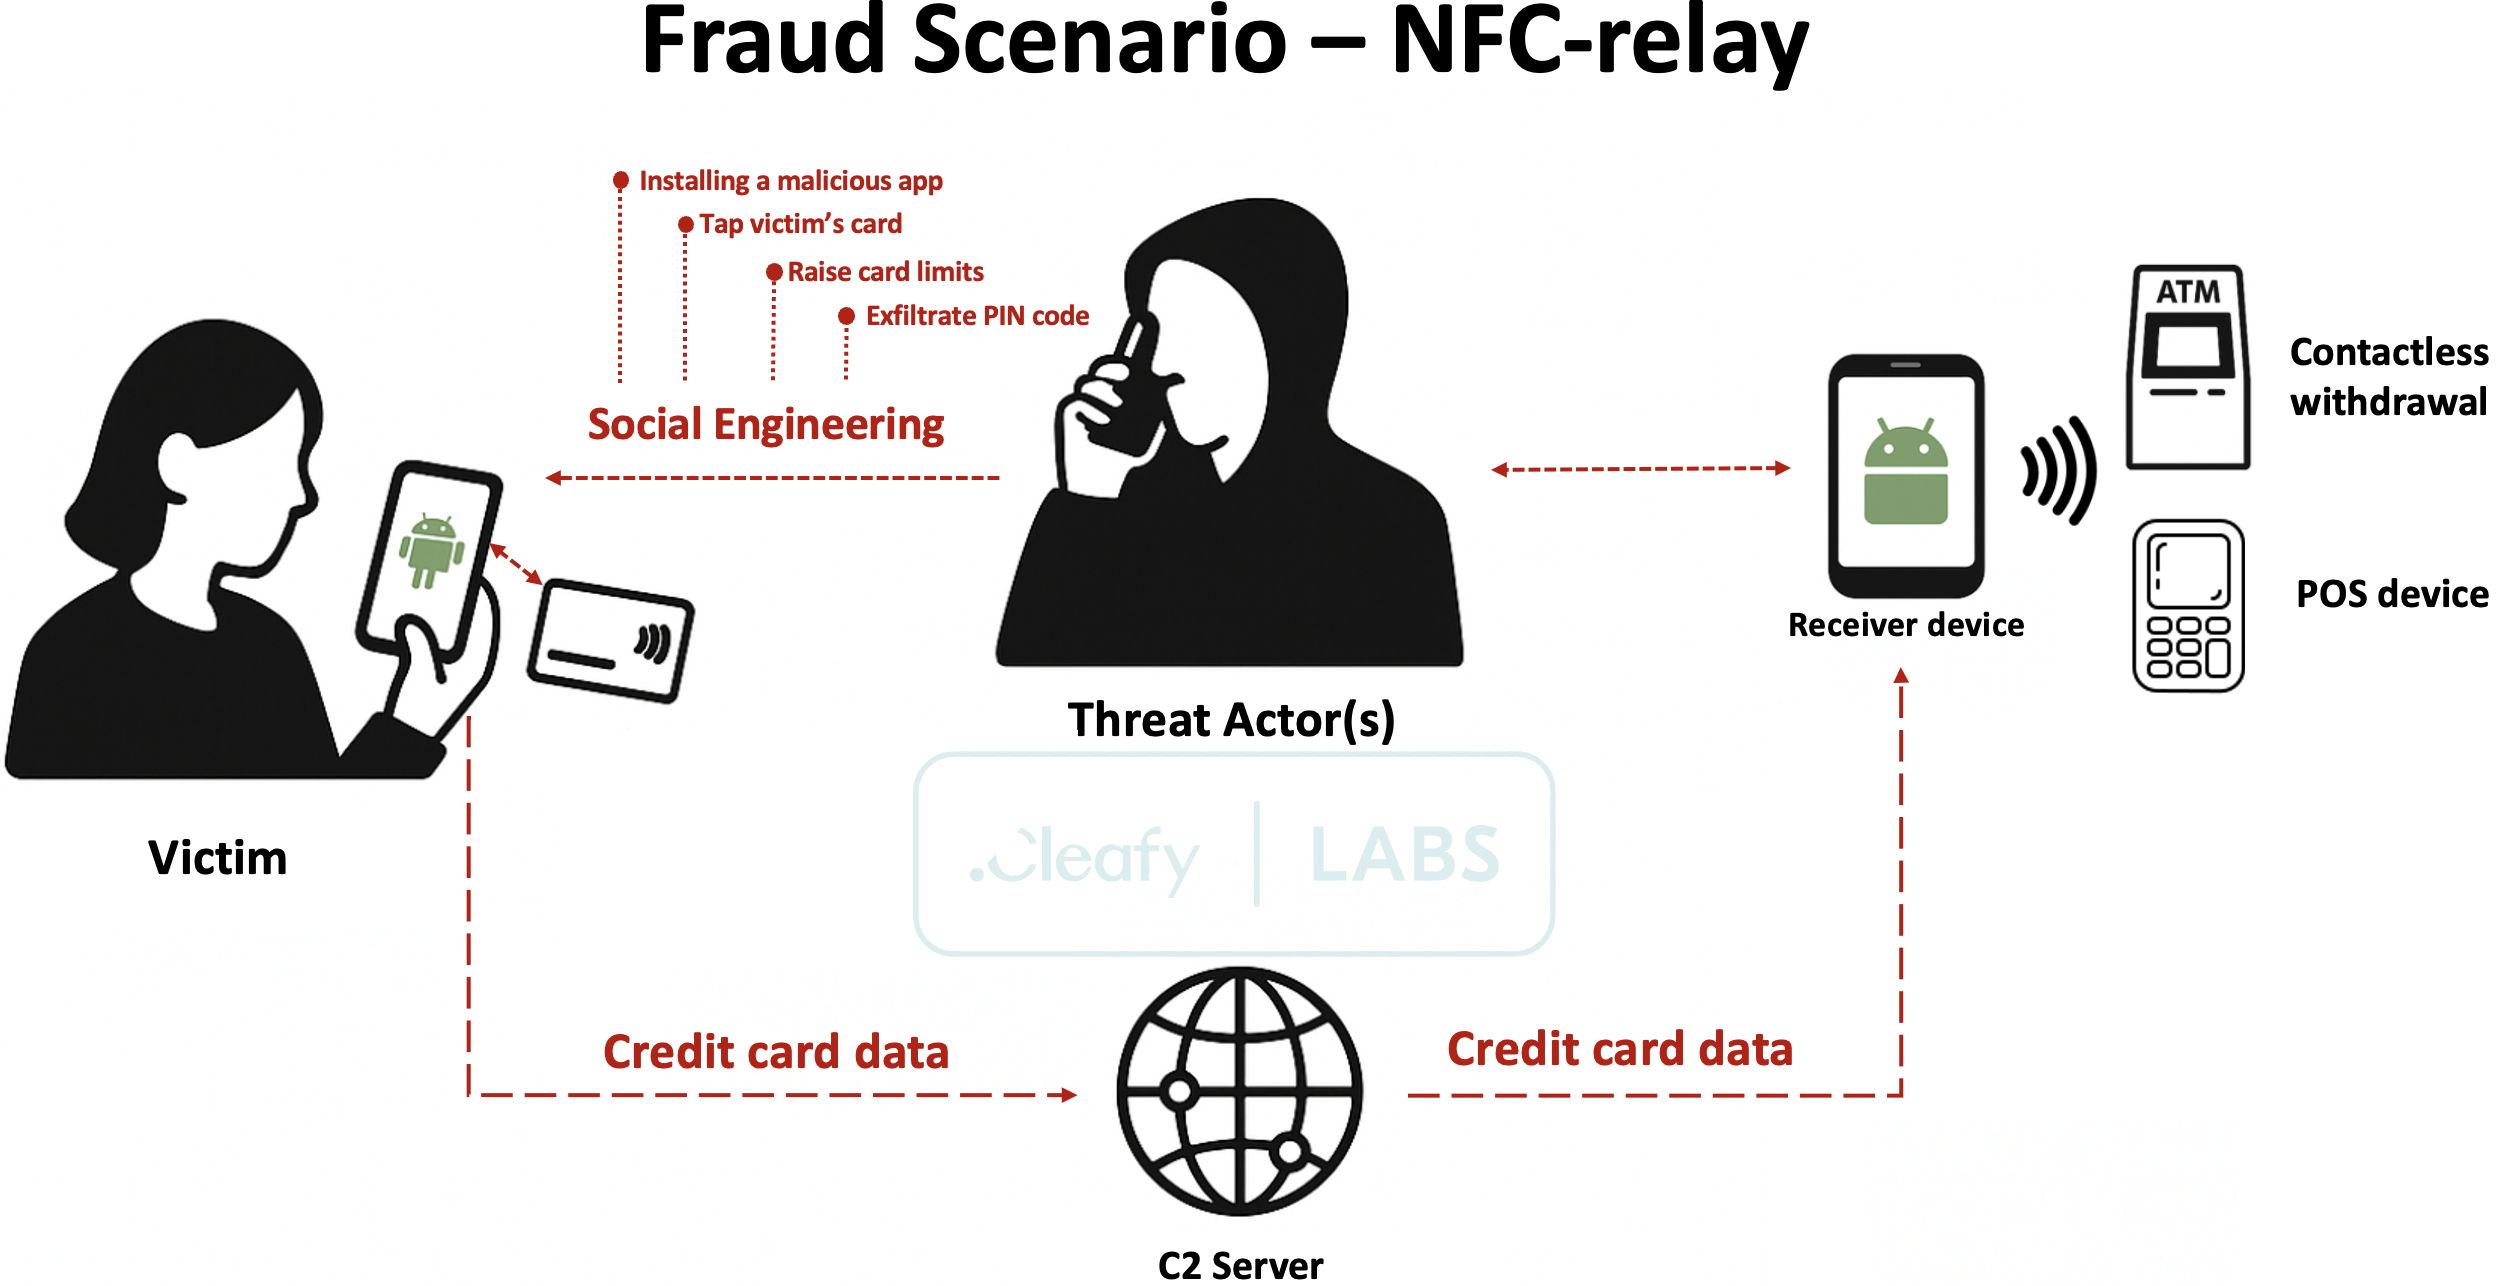
‘SuperCard X’ – a new MaaS – targets Androids via NFC relay attacks, enabling fraudulent POS and ATM transactions with stolen card data. Cleafy researchers discovered a new malware-as-a-service (MaaS) called SuperCard X targeting Android devices with NFC relay attacks for fraudulent cash-outs. Attackers promote the MaaS through Telegram channels, analysis shows SuperCard X builds […]
 Pierluigi Paganini
April 21, 2025
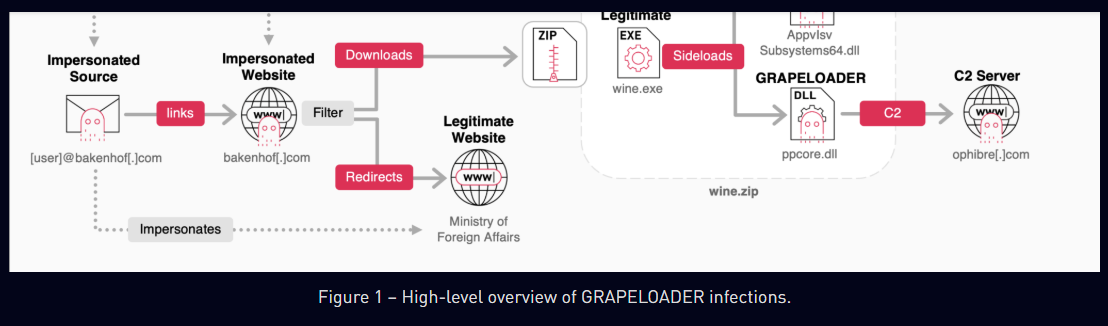
Russia-linked group APT29 targeted diplomatic entities across Europe with a new malware loader codenamed GRAPELOADER. Check Point Research team reported that Russia-linked cyberespionage group APT29 (aka SVR group, Cozy Bear, Nobelium, BlueBravo, Midnight Blizzard, and The Dukes) is behind a sophisticated phishing campaign targeting European diplomatic entities, using a new WINELOADER variant and a previously unknown malware called GRAPELOADER. “While the […]
 Pierluigi Paganini
April 20, 2025
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malicious NPM Packages Targeting PayPal Users New Malware Variant Identified: ResolverRAT Enters the Maze Nice chatting with you: what connects cheap Android smartphones, WhatsApp and cryptocurrency theft? BPFDoor’s Hidden Controller Used Against Asia, Middle East […]
 Pierluigi Paganini
April 19, 2025
Threat actors are actively exploiting a remote code execution flaw in SonicWall Secure Mobile Access (SMA) appliances since January 2025. Arctic Wolf researchers warn that threat actors actively exploit a vulnerability, tracked as CVE-2021-20035 (CVSS score of 7.1), in SonicWall Secure Mobile Access (SMA) since at least January 2025. The vulnerability is an OS Command […]
 Pierluigi Paganini
April 18, 2025
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Apple products and Microsoft Windows NTLM flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Apple products and Microsoft Windows NTLM vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog. Below are the descriptions of the flaws: This week Apple released out‑of‑band […]
 Pierluigi Paganini
April 18, 2025
Legends International disclosed a data breach from November 2024 that affected employees and visitors to its managed venues. Legends International is a global leader in sports and entertainment venue management, specializing in delivering comprehensive solutions for stadiums, arenas, and attractions. The company offers a 360-degree service platform that includes strategic planning, sales, partnerships, hospitality, merchandise, […]
 Pierluigi Paganini
April 17, 2025
China-linked APT group Mustang Panda deployed a new custom backdoor, MQsTTang, in recent attacks targeting Europe, Asia, and Australia. China-linked APT group Mustang Panda (aka Camaro Dragon, RedDelta or Bronze President). deployed a new custom backdoor, tracked as MQsTTang, in recent attacks targeting entities in Europe, Asia, and Australia. Mustang Panda has been active since […]
 Pierluigi Paganini
April 17, 2025
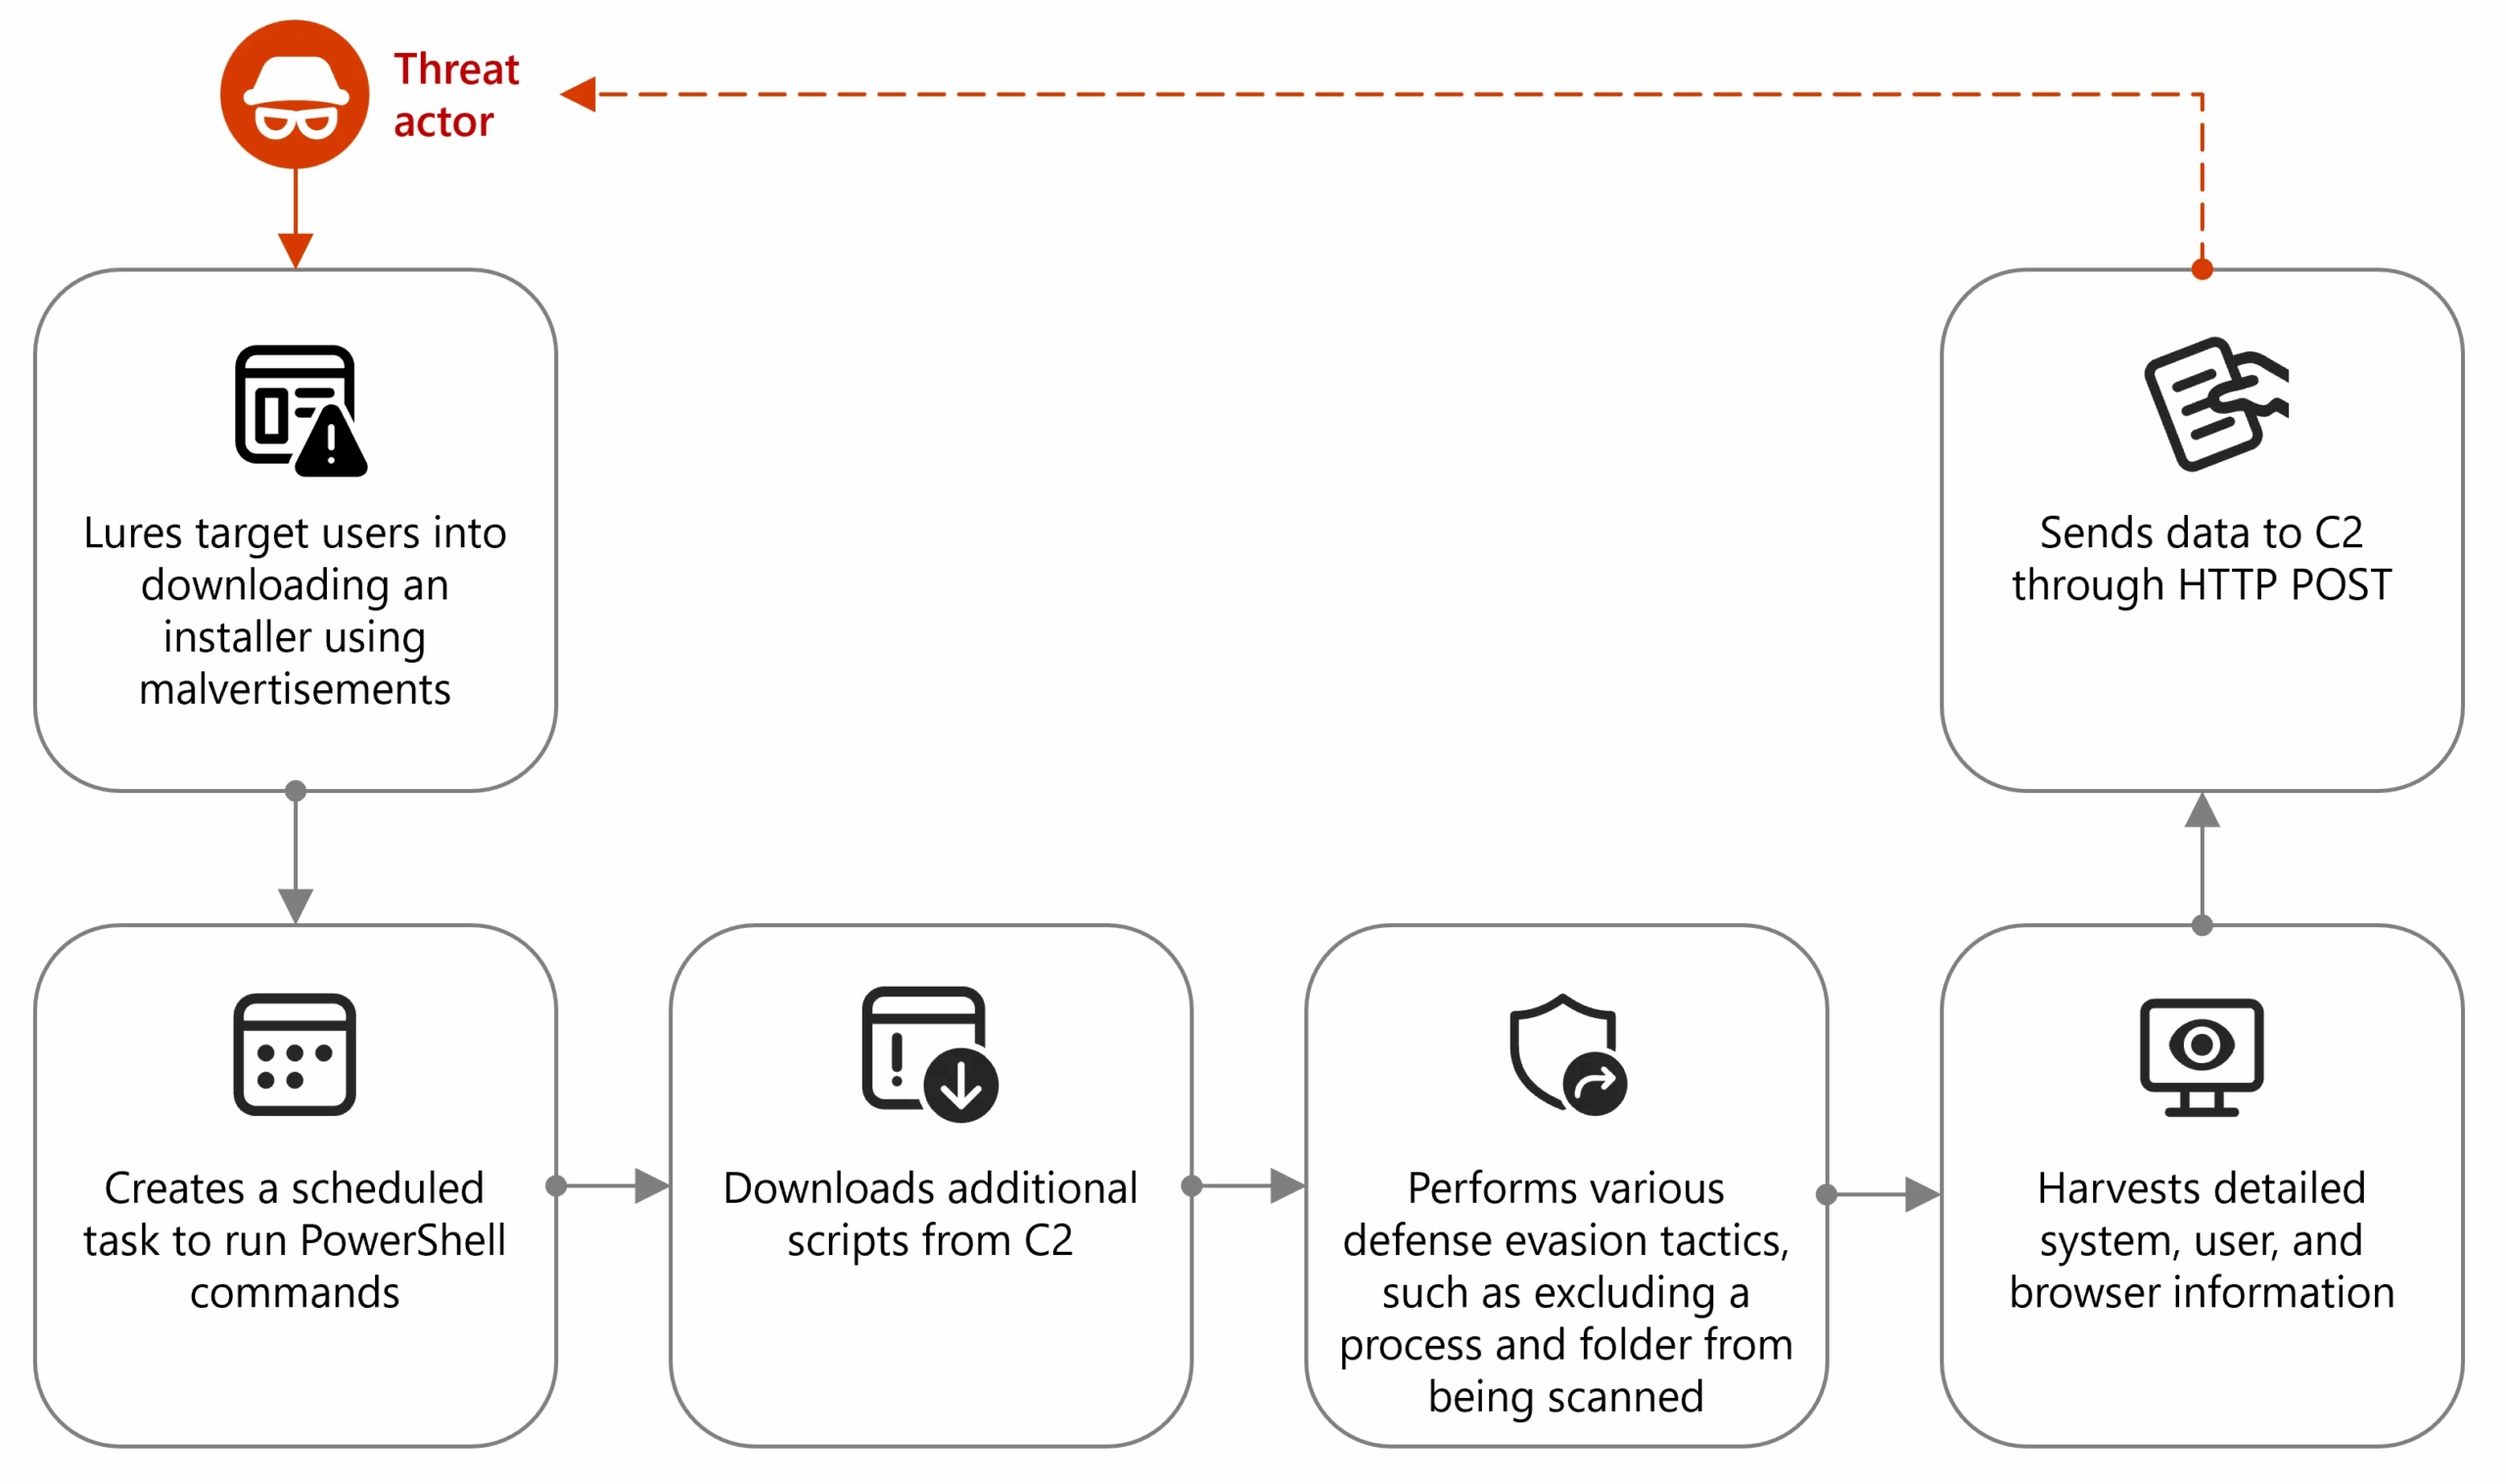
Microsoft warns of a malvertising campaign using Node.js to deliver info-stealing malware via fake crypto trading sites like Binance and TradingView. Microsoft has observed Node.js increasingly used in malware campaigns since October 2024, including an ongoing crypto-themed malvertising attack as of April 2025. Threat actors are increasingly using Node.js to deploy malware, shifting from traditional […]
 Pierluigi Paganini
April 17, 2025
Apple released emergency updates to fix iOS, iPadOS & macOS vulnerabilities actively exploited in sophisticated attacks. Apple released out‑of‑band security updates to address two vulnerabilities, tracked as CVE-2025-31200 and CVE-2025-31201, impacting iOS, iPadOS & macOS. The company confirmed that the flaws have been exploited in a small number of “extremely sophisticated” attacks against iOS targets. […]
Pierluigi Paganini
April 17, 2025
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds SonicWall SMA100 Appliance flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a SonicWall SMA100 Appliance flaw, tracked as CVE-2021-20035, to its Known Exploited Vulnerabilities (KEV) catalog. The vulnerability is an OS Command Injection Vulnerability in the SMA100 management interface. A […]







