19292 results
 Pierluigi Paganini
 December 03, 2024
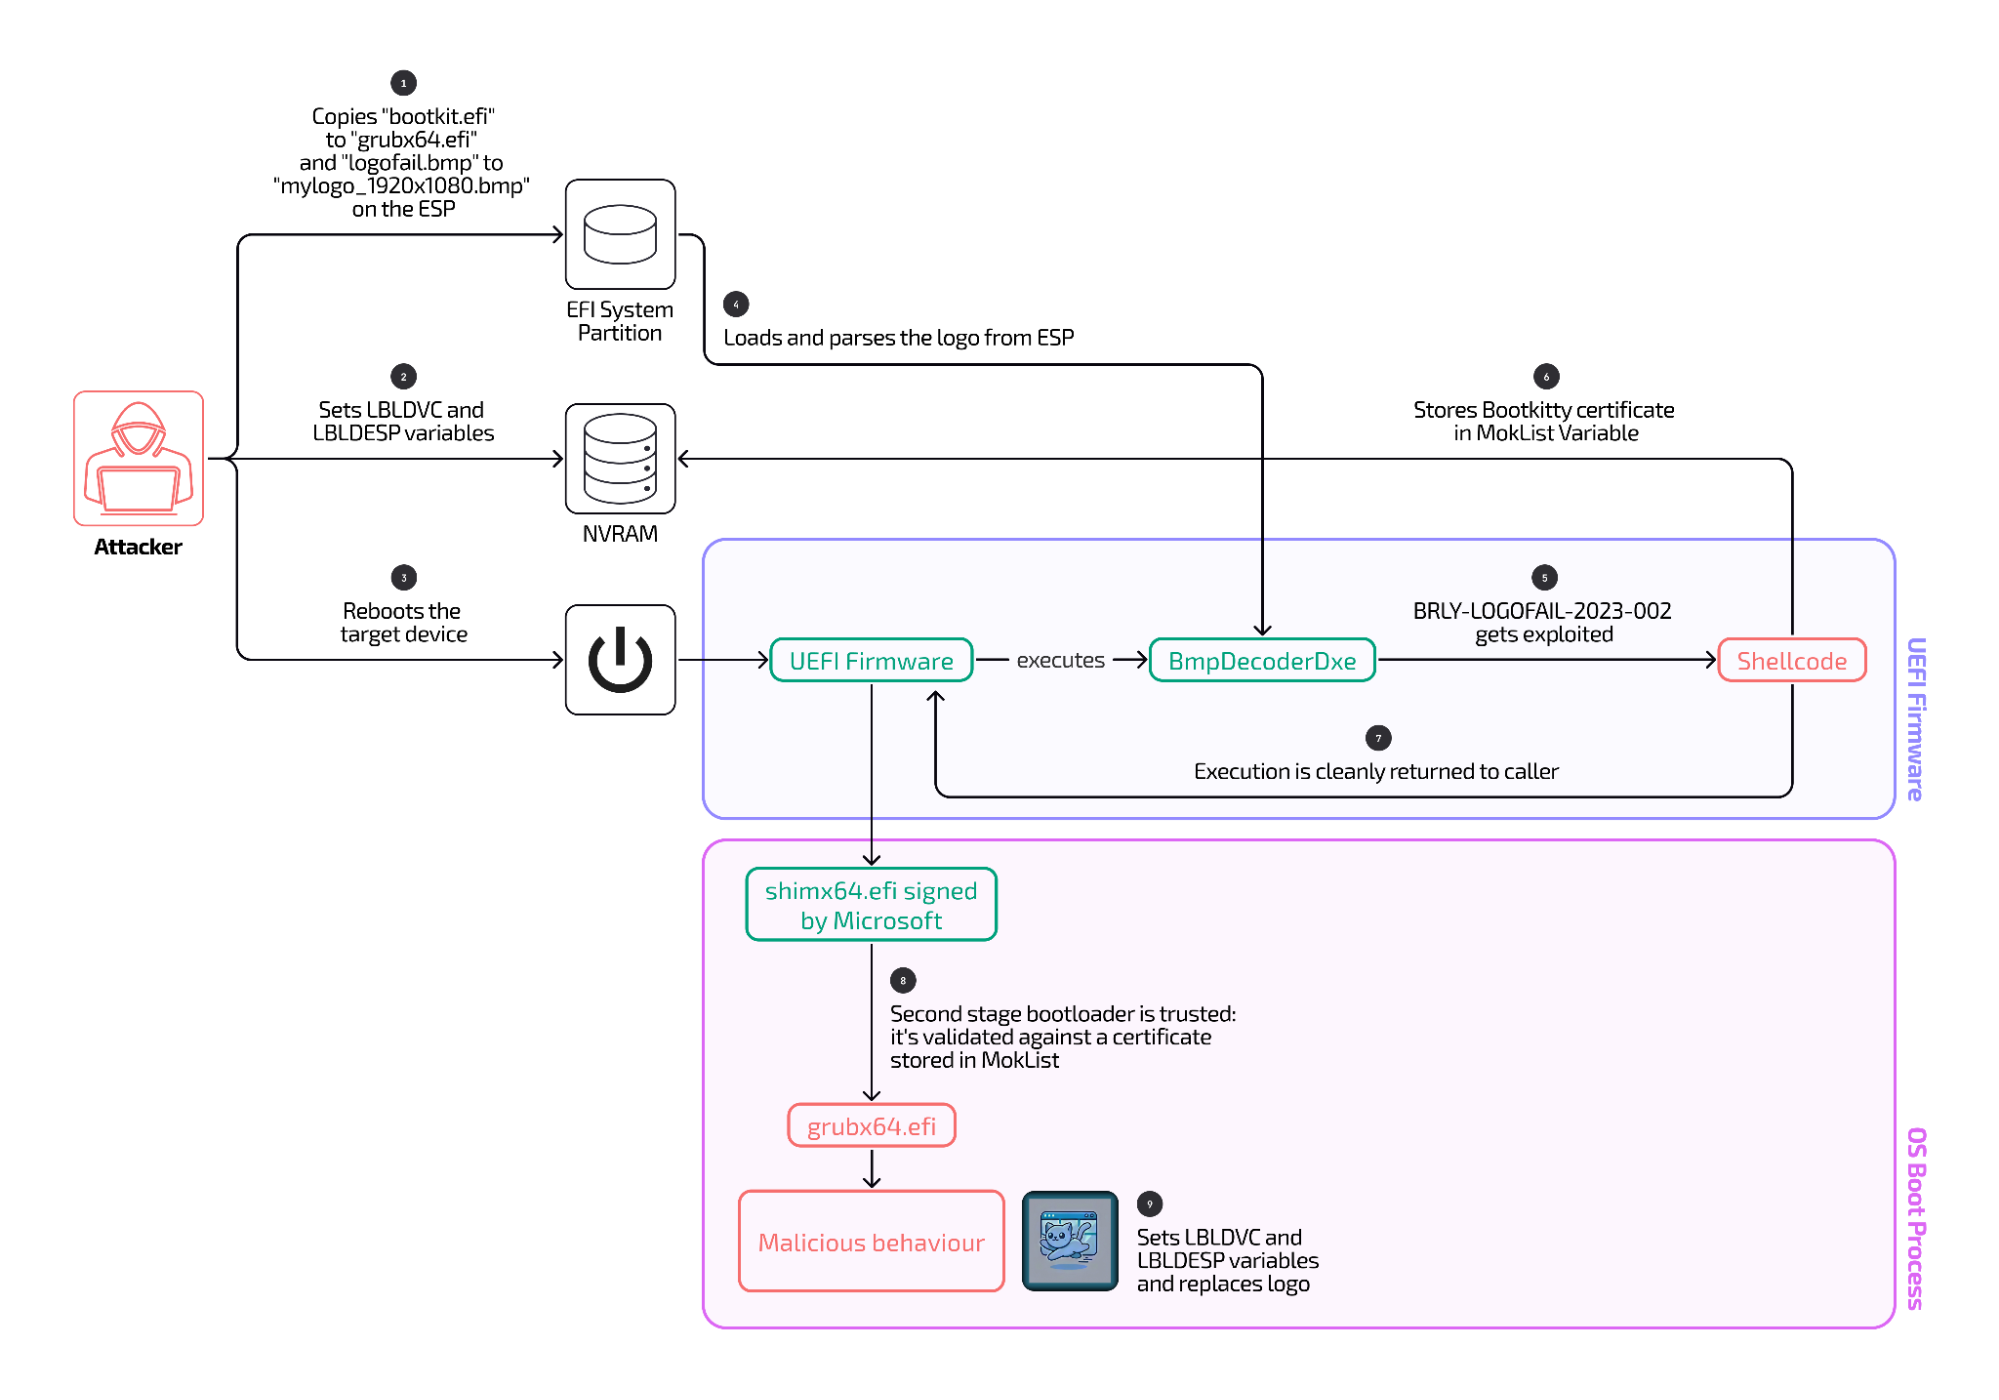
The ‘Bootkitty’ Linux UEFI bootkit exploits the LogoFAIL flaws (CVE-2023-40238) to target systems using vulnerable firmware. Cybersecurity researchers from ESET recently discovered the first UEFI bootkit designed to target Linux systems, called by its authors Bootkitty. The bootkit allows attackers to disable the kernel’s signature verification feature and to preload two as yet unknown ELF […]
 Pierluigi Paganini
December 02, 2024
The Tor Project seeks help deploying 200 WebTunnel bridges by year-end to counter government censorship. Recent reports from Russia show increased censorship targeting the Tor network, including blocking bridges, pluggable transports, and circumvention apps. Russian watchdog Roskomnadzor is making some bridges inaccessible, highlighting the urgent need for more WebTunnel bridges. WebTunnel is a stealthy bridge […]
 Pierluigi Paganini
December 02, 2024
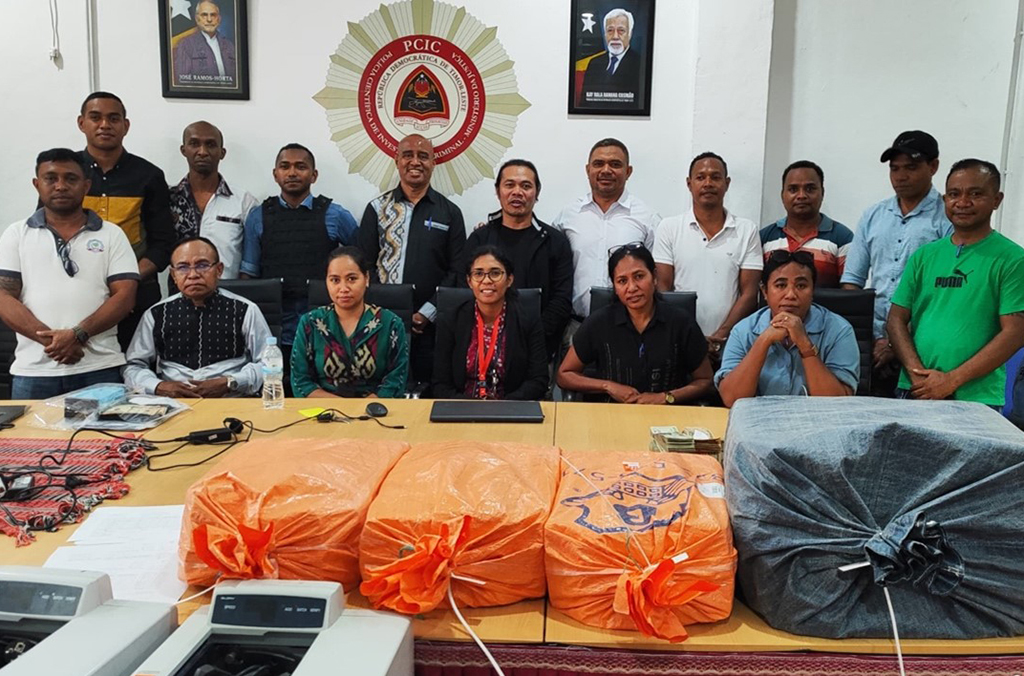
International law enforcement operation Operation HAECHI-V led to more than 5,500 suspects arrested and seized over $400 million. A global operation code-named Operation HAECHI V, involving 40 countries, resulted in 5,500+ arrests and seized $400M in assets. Operation HAECHI V (July-Nov 2024) targeted cyber frauds like phishing, romance scams, sextortion, investment fraud, online gambling, BEC, […]
 Pierluigi Paganini
December 02, 2024
Generative Artificial Intelligence (GAI) is rapidly revolutionizing various industries, including cybersecurity, allowing the creation of realistic and personalized content. The capabilities that make Generative Artificial Intelligence a powerful tool for progress also make it a significant threat in the cyber domain. The use of GAI by malicious actors is becoming increasingly common, enabling them to […]
 Pierluigi Paganini
December 01, 2024
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape. A Case-Control Study to Measure Behavioral Risks of Malware Encounters in Organizations PyPI Python Library “aiocpa” Found Exfiltrating Crypto Keys via Telegram Bot Bootkitty: Analyzing the first UEFI bootkit for Linux Hudson Rock Announces First Comprehensive […]
 Pierluigi Paganini
December 01, 2024
Financially-motivated threat actors hacked Uganda ‘s central bank system, government officials confirmed this week. Ugandan officials confirmed on Thursday that the national central bank suffered a security breach by financially-motivated threat actors. The police’s Criminal Investigations Department and the Auditor General are investigating the incident. A senior government official at the finance ministry confirmed that […]
 Pierluigi Paganini
November 30, 2024
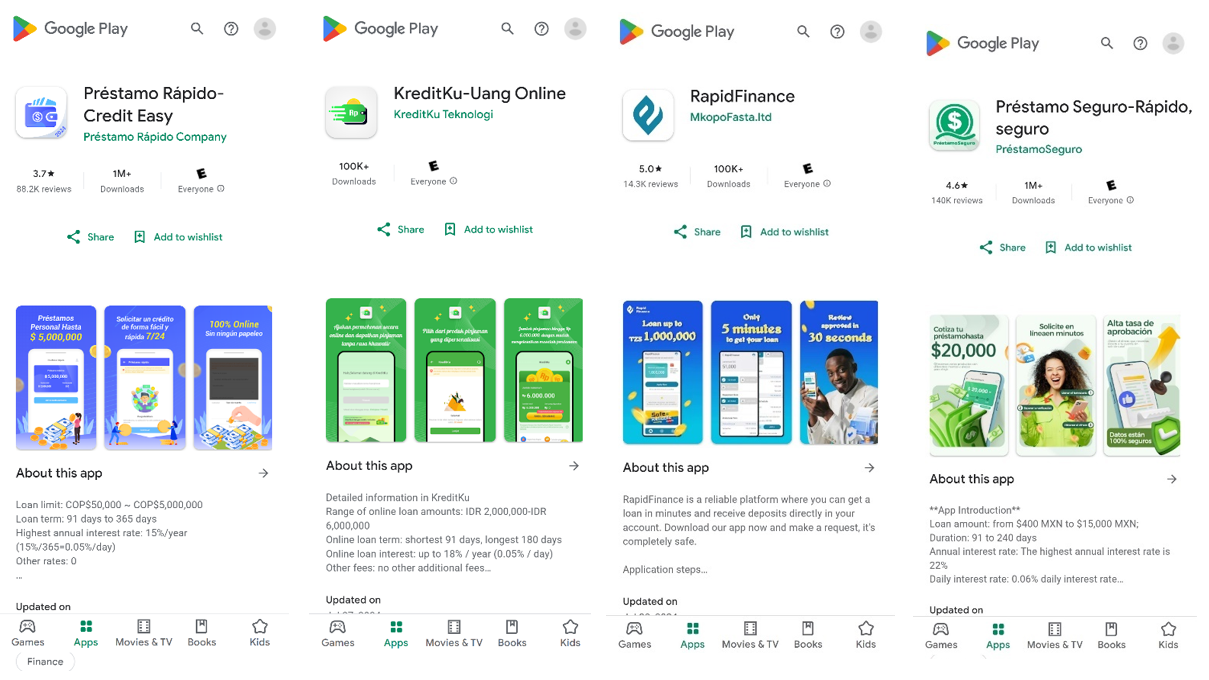
McAfee researchers discovered 15 SpyLoan Android apps on Google Play with a combined total of over 8 million installs. 15 SpyLoan apps with a combined total of 8M+ installs were found on Google Play, targeting users in South America, Southeast Asia, and Africa. SpyLoan apps exploit social engineering to gain sensitive user data and excessive […]
 Pierluigi Paganini
November 30, 2024
Russian authorities arrested ransomware affiliate Mikhail Matveev, aka Wazawaka, for developing malware and ties to hacking groups. Russian authorities arrested a ransomware affiliate, Mikhail Pavlovich Matveev (also known as Wazawaka, Uhodiransomwar, m1x, and Boriselcin), and charged him for developing malware and his role in several hacking groups. The man was arrested in Kaliningrad, Russia, law […]
 Pierluigi Paganini
November 29, 2024
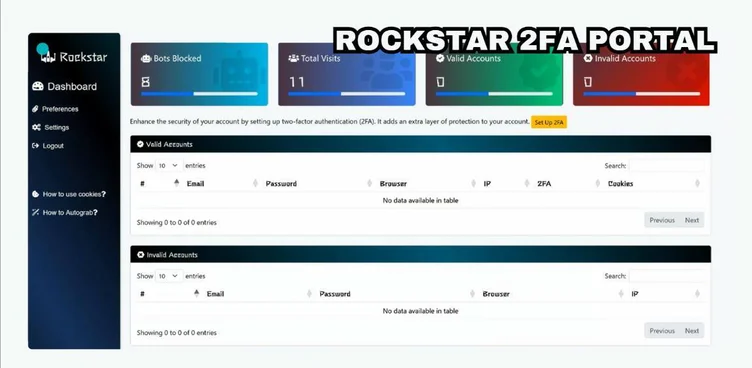
Phishing tool Rockstar 2FA targets Microsoft 365 credentials, it uses adversary-in-the-middle (AitM) attacks to bypass multi-factor authentication. Trustwave researchers are monitoring malicious activity associated with Phishing-as-a-Service (PaaS) platforms, their latest report focuses on a toolkit called Rockstar 2FA. Rockstar 2FA targets Microsoft 365 accounts and bypasses multi-factor authentication with adversary-in-the-middle (AitM) attacks. In AiTM phishing, threat […]
 Pierluigi Paganini
November 29, 2024
Zello urges customers with accounts created before November 2 to reset passwords following a potential security breach. Zello is warning customers who have an account created before November 2 to reset their passwords, a circumstance that suggests that the incident took place on November 2. Zello is a tech software company in Austin, Texas, U.S., known for the […]