19103 results
 Pierluigi Paganini
 March 02, 2026
Ukrainian citizen Yurii Nazarenko admitted running OnlyFake, an AI-driven site that sold over 10,000 fake IDs worldwide. Ukrainian man Yurii Nazarenko pleaded guilty to operating OnlyFake, an AI-powered site that generated and sold more than 10,000 counterfeit IDs globally. “United States Attorney for the Southern District of New York, Jay Clayton, and Assistant Director in Charge […]
 Pierluigi Paganini
January 18, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Gogs 0-Day Exploited in the Wild SHADOW#REACTOR – Text-Only Staging, .NET Reactor, and In-Memory Remcos RAT Deployment “Untrustworthy Fund”: targeted UAC-0190 cyberattacks against SOU using PLUGGYAPE (CERT-UA#19092) Hiding in Plain Sight: Deconstructing the Multi-Actor […]
 Pierluigi Paganini
January 07, 2026
Veeam patched a critical RCE flaw in Backup & Replication, CVE-2025-59470, rated CVSS 9.0, along with other vulnerabilities. Veeam released patches for multiple Backup & Replication flaws, including a critical RCE vulnerability tracked as CVE-2025-59470 (CVSS score of 9.0). A Backup or Tape Operator can achieve remote code execution as the postgres user by abusing […]
 Pierluigi Paganini
December 22, 2025
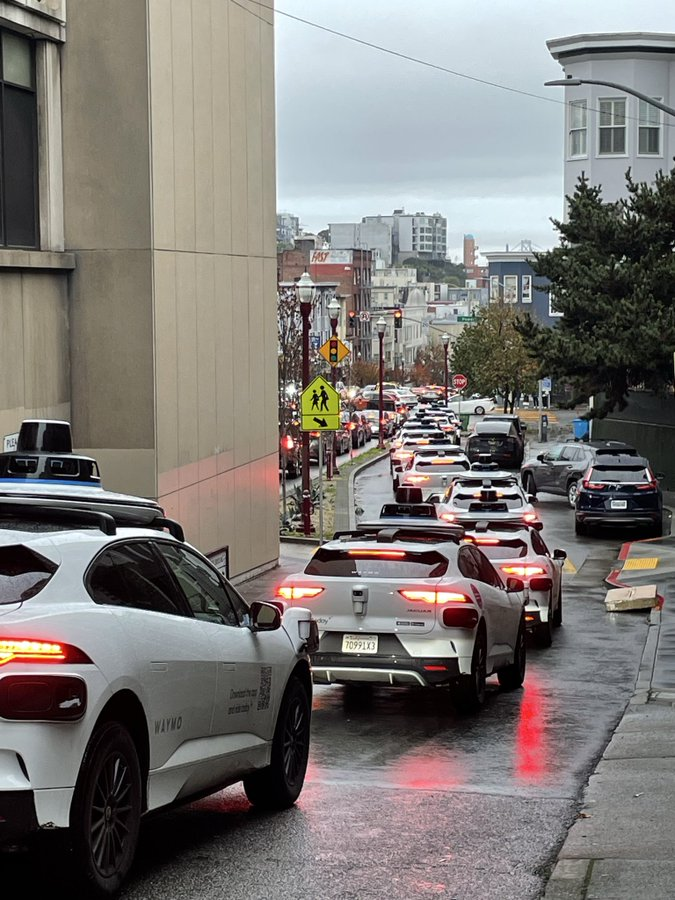
Waymo temporarily halted its San Francisco robotaxi service after a major blackout left multiple autonomous vehicles stranded on city streets. Waymo temporarily halted its robotaxi service in San Francisco after a widespread blackout caused multiple autonomous vehicles to stall on city streets. “We have temporarily suspended our ride-hailing services in the San Francisco Bay Area […]
Pierluigi Paganini
November 30, 2025
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Analysis of ShadowPad Attack Exploiting WSUS Remote Code Execution Vulnerability (CVE-2025-59287) Shai-Hulud 2.0 Supply Chain Attack: 25K+ npm Repos Exposed Spyware Allows Cyber Threat Actors to Target Users of Messaging Applications Morphisec Thwarts Russian-Linked […]
 Pierluigi Paganini
November 27, 2025
OpenAI warns some users that a cyberattack on analytics firm Mixpanel may have exposed their data. Mixpanel is a product analytics platform that companies use to understand how people interact with their apps or websites. Many tech companies use Mixpanel to make data-driven decisions about features, performance, and customer journeys. OpenAI is alerting some users about […]
 Pierluigi Paganini
November 16, 2025
Five pleaded guilty to aiding North Korea ’s illicit revenue via IT worker fraud, violating international sanctions. The U.S. Department of Justice announced that five people have pleaded guilty to helping North Korea secretly generate revenue by running illegal IT-worker schemes that violated international sanctions. The individuals – Audricus Phagnasay (24), Jason Salazar (30), Alexander […]
 Pierluigi Paganini
November 14, 2025
ASUS fixed a critical auth-bypass flaw (CVE-2025-59367) in DSL routers that let remote, unauthenticated attackers access devices with ease. ASUS patched a critical auth-bypass flaw, tracked as CVE-2025-59367 (CVSS score of 9.3), in multiple DSL routers that allows remote, unauthenticated attackers to easily access unpatched devices. The vulnerability impacts DSL-AC51, DSL-N16, DSL-AC750 router families, the […]
 Pierluigi Paganini
November 07, 2025
Cisco patched a critical flaw in its Unified Contact Center Express (UCCX) software that allowed attackers to execute commands with root privileges. Cisco released security updates to address a critical vulnerability, tracked as CVE-2025-20354 (CVSS score 9.8), in the Unified Contact Center Express (UCCX) software. An attacker can exploit the flaw to execute commands with root […]
 Pierluigi Paganini
November 03, 2025
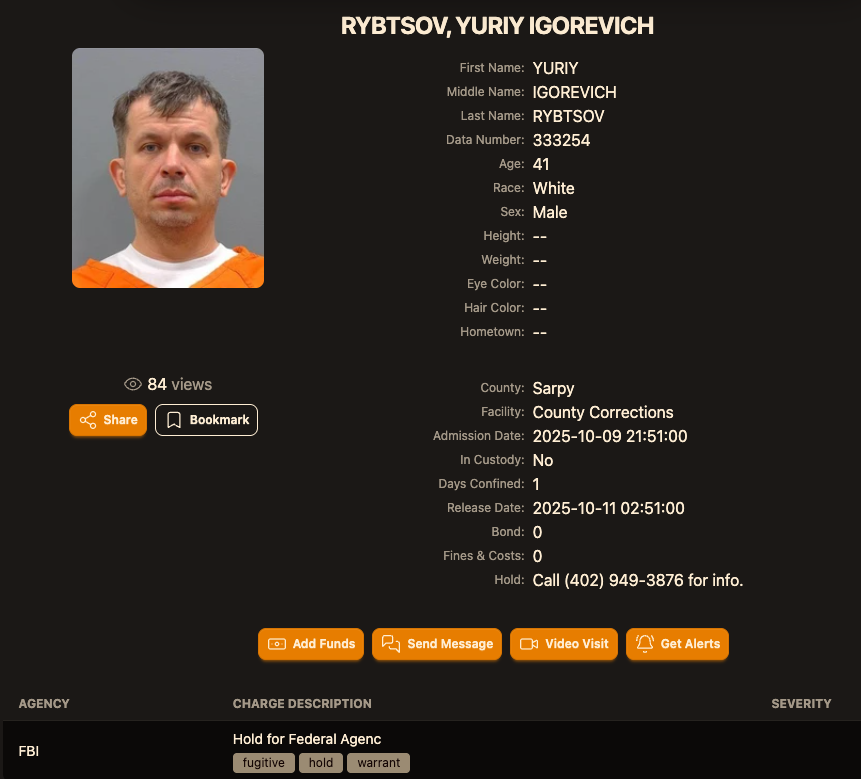
Ukrainian Yuriy Rybtsov, aka MrICQ, a suspected Jabber Zeus developer, was extradited from Italy to the US to face cybercrime charges. Ukrainian national Yuriy Igorevich Rybtsov (41), aka MrICQ, an alleged Jabber Zeus developer, was arrested in Italy, lost his extradition appeal, and has been sent to the US to face cybercrime charges. After a […]