19034 results
 Pierluigi Paganini
 February 22, 2017
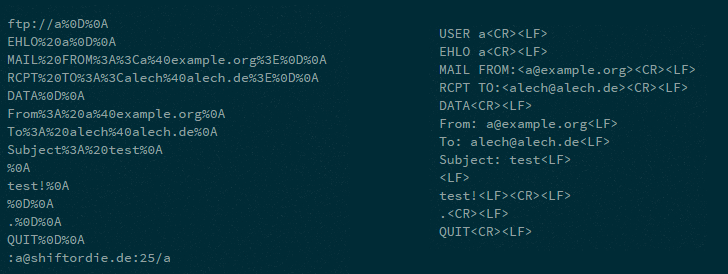
The two programming languages, Java and Python, are affected by serious FTP Injection flaws that can be exploited by hackers to bypass any firewall. Attackers can trick Java and Python applications to execute rogue FTP commands that would open ports in firewalls The unpatched flaws reside in the way the two programming languages handle File Transfer […]
 Pierluigi Paganini
February 22, 2017
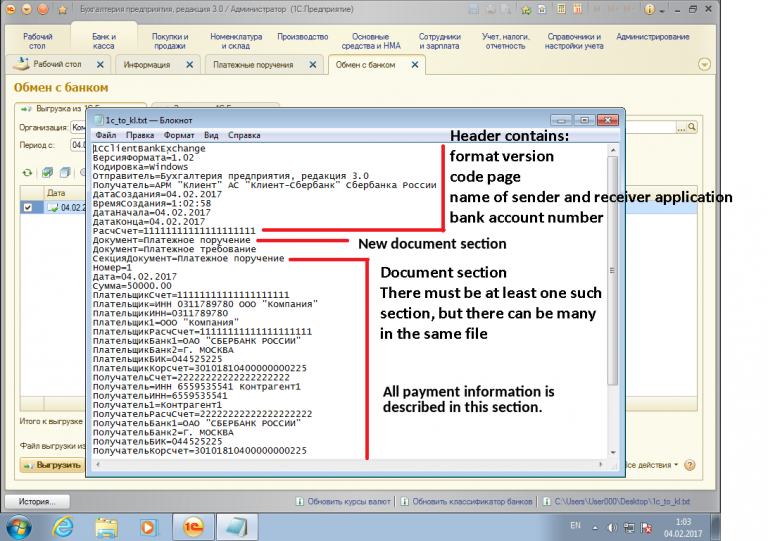
Researchers at ESET are monitoring the activity of a cybercrime group tracked as RTM that focuses its criminal operations on Remote Banking Systems. Experts at software firm ESET are monitoring the activity of a cybercrime group tracked as RTM that using a sophisticated malware written in Delphi language to target Remote Banking Systems (RBS). The […]
 Pierluigi Paganini
February 21, 2017
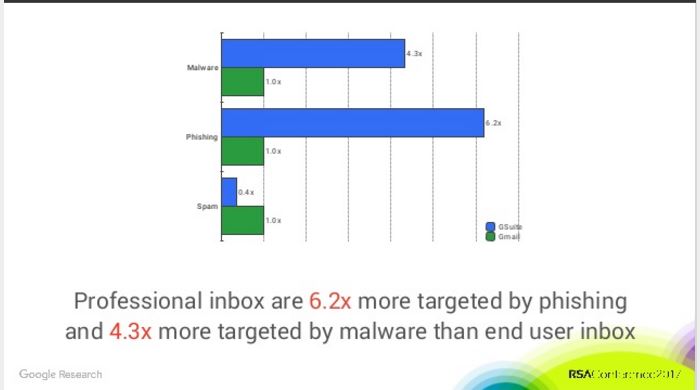
At the RSA security conference in San Francisco, the experts at Google Research explained that Corporate email addresses are privileged targets for hackers. At the RSA security conference in San Francisco, the experts at the Google Research team at the Google Research team have shared the results of an interesting study on cyber attacks against emails accounts. Corporate […]
 Pierluigi Paganini
February 21, 2017
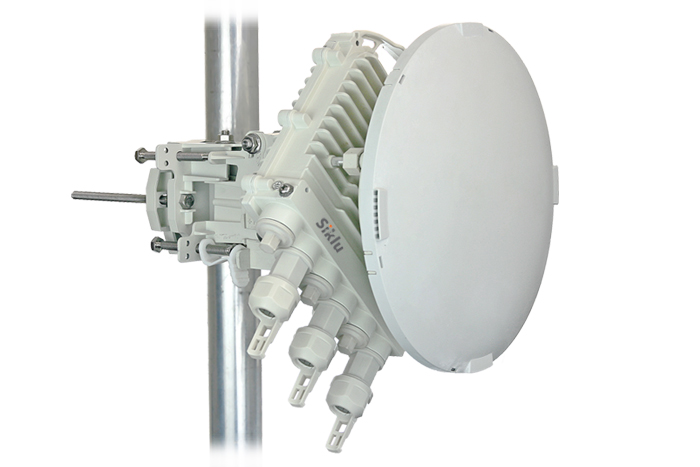
The security researcher Ian Ling discovered a serious remote command execution (RCE) flaw in the Siklu EtherHaul Radios devices. Security expert Ian Ling has discovered a severe remote command execution (RCE) vulnerability in the Siklu’s EtherHaul wireless point-to-point radios. The flaw could be exploited by remote unauthenticated attackers to execute commands and retrieve sensitive information, including […]
 Pierluigi Paganini
February 21, 2017
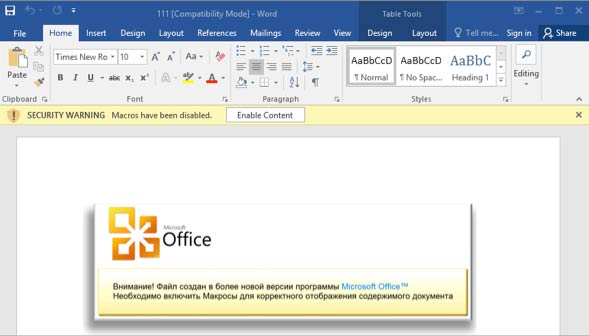
Security firm CyberX uncovered the Operation Bugdrop, a cyber espionage campaign that mostly targeted Ukrainian organizations. Researchers at Security firm CyberX have discovered a cyber espionage campaign that siphoned more than 600 gigabytes from about 70 targets in several industries, including critical infrastructure and news media. The list of targets includes: A company that designs […]
 Pierluigi Paganini
February 21, 2017
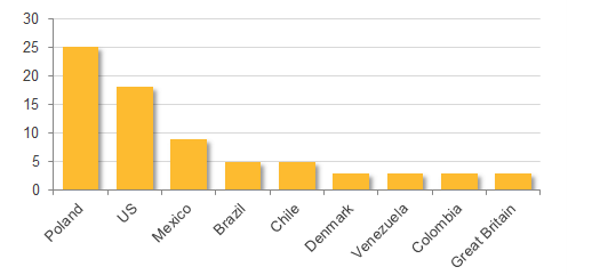
Security experts who analyzed the malware used in the attacks against the Polish banks discovered false flags in the Lazarus malicious code. A few weeks ago, security experts reported that the systems of several Polish banks were targeted by hackers. The systems were infected with a malware after their staff visited the site of the […]
 Pierluigi Paganini
February 20, 2017
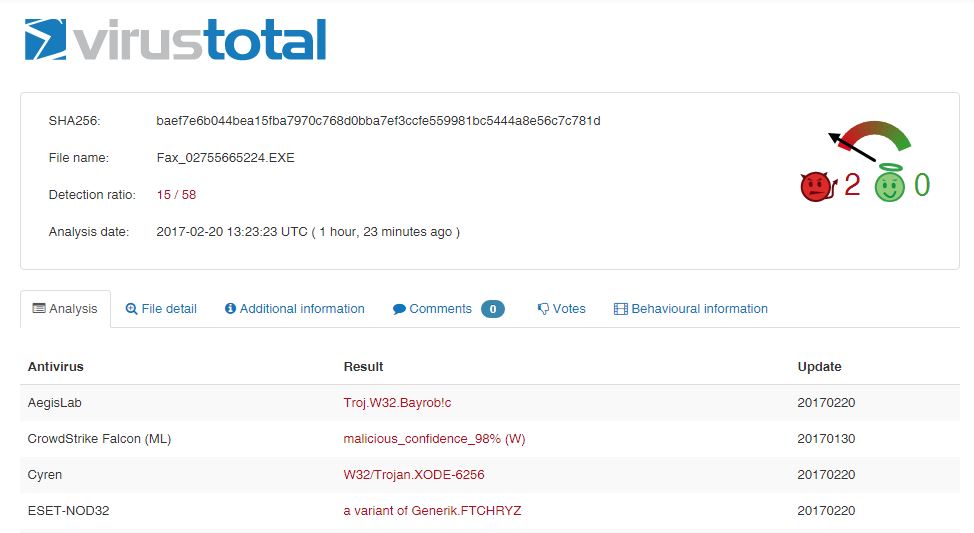
Security experts from Heimdal Security discovered a new spam campaign over the weekend leveraging the TeamSpy malware to spy in victims. Security experts from Heimdal Security have uncovered a new spam campaign emerged over the weekend. The crooks used the notorious TeamSpy malware to gain full access to the target computers. It’s a long time we have no […]
 Pierluigi Paganini
February 20, 2017
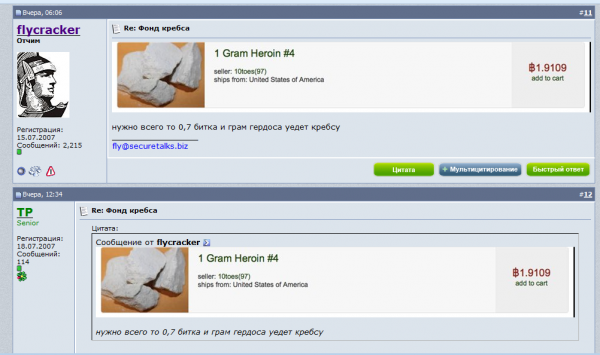
The Ukrainian Cybercriminal who tried to get revenge on Brian Krebs for exposing him was sentenced to 41 months in prison in the US. The Ukrainian cybercriminal Sergey Vovnenko (31, aka “Sergey Vovnencko,” “Tomas Rimkis,” “Flycracker,” “Flyck,” “Fly,” “Centurion,” “MUXACC1,” “Stranier” and “Darklife.”) who attempted to get revenge on the notorious cyber security investigator Brian […]
 Pierluigi Paganini
February 20, 2017
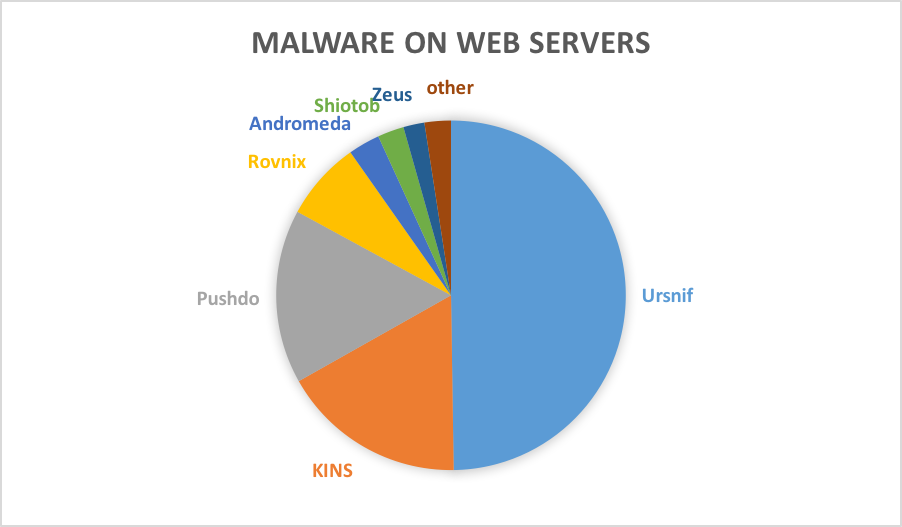
The security experts at Palo Alto Networks published a detailed analysis of the architecture used to spread the Ursnif banking Trojan worldwide. Malware researchers from Palo Alto Networks are monitoring the diffusion of the Ursnif banking Trojan worldwide and have identified the architecture used to spread it. The Ursnif Trojan is spread via spam emails that contain […]
 Pierluigi Paganini
February 20, 2017
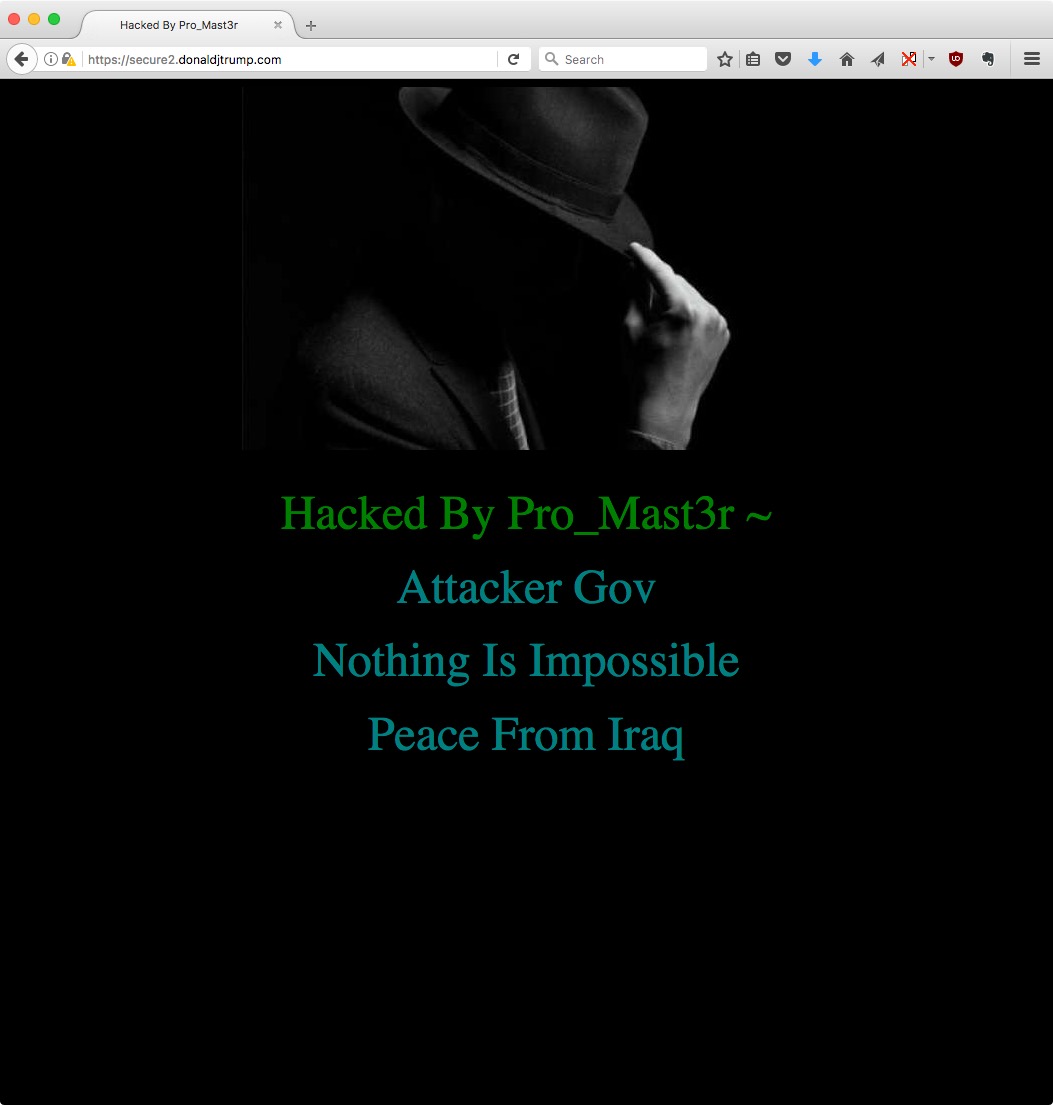
The group of Iraqi hackers called “Pro_Mast3r” has breached the server hosting a Trump website associated with campaign donations. A group of hackers who is calling themselves “Pro_Mast3r” has defaced a website associated with President Donald Trump’s presidential campaign fundraising on Sunday. The website was hosted on the server secure2.donaldjtrump.com that is managed by the Cloudflare content […]


Artificial Intelligence / September 19, 2026