19323 results
 Pierluigi Paganini
 February 25, 2015
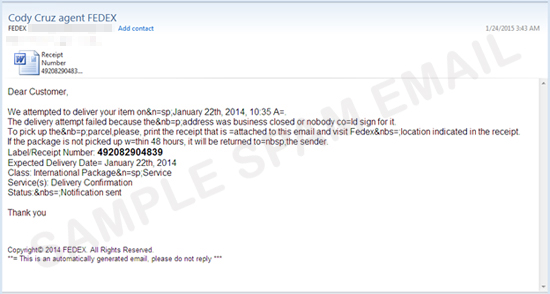
Security experts at TrendMicro observed significant improvements in VAWTRAK banking trojan which couples use malicious macros and Windows PowerShell. Early 2015 the Microsoft Malware Protection Center (MMPC) issued an alert about a surge in the infections of malware using macros to spread their malicious code. The experts MMPC have observed a significant increase in enable-macros […]
 Pierluigi Paganini
February 25, 2015
The McAfee Labs Threat Report: February 2015 analyzes security level of mobile apps and the evolution of principal cyber threats. Last year the Carnegie Mellon University’s Computer Emergency Response Team (CERT) analyzed the level of security implemented by Android applications, in particular the experts focused their investigation on Android applications that failed to properly validate SSL certificates. The […]
 Pierluigi Paganini
February 24, 2015
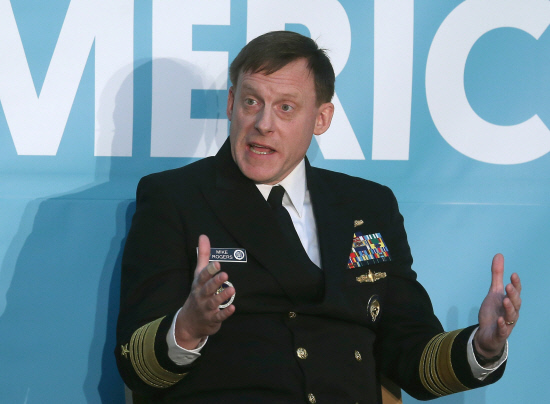
The NSA Director Rogers urges the creation of an independent legal framework to regulate the operations conducted US authorities. The NSA director and commander of U.S. Cyber Command, Admiral Michael Rogers, told a Washington cybersecurity forum that legislators need the creation of a legal framework to regulate the operations conducted by law enforcement and intelligence-gathering organizations worldwide. […]
 Pierluigi Paganini
February 24, 2015
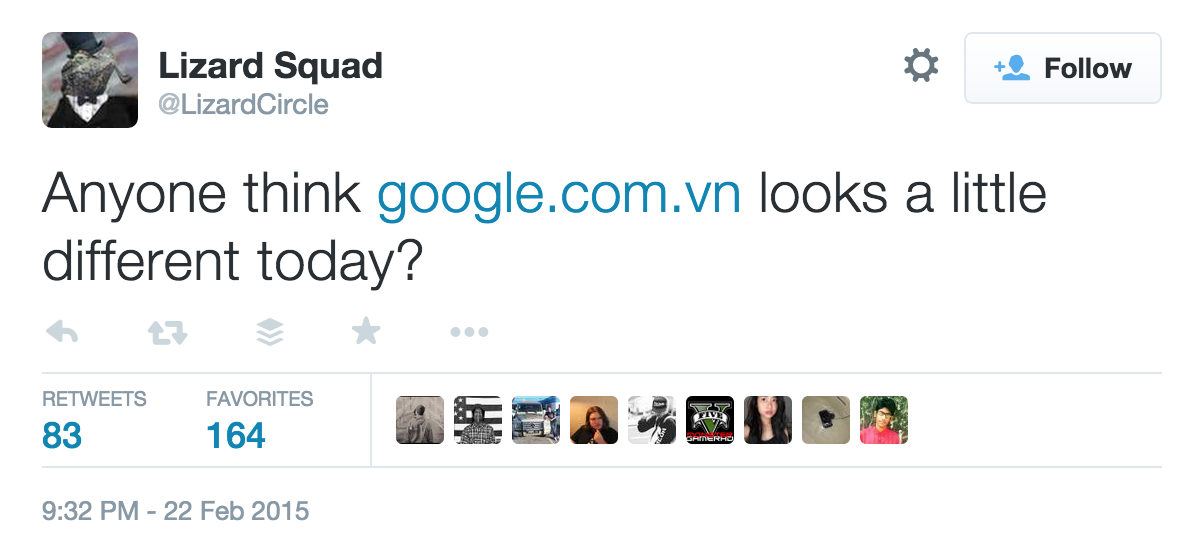
Alleged Hacker belonging to the hacking crew Lizard Squad run a DNS hajacking attack against the Google Vietnam domain. A nasty surprise for Internet users who visited the Google Vietnam website that was presented with a picture of a man taking a selfie, along with a message that claimed the website site was hacked by the […]
 Pierluigi Paganini
February 24, 2015
CVE-2015-0240 is a critical security flaw in Samba that resides in the smbd file server daemon and can be exploited by a malicious Samba client remotely. Linux administrators urge to update their systems due to the discovery of a critical vulnerability the open source Linux-and-Windows-compatibility software Samba. The vulnerability in Samba, coded as CVE-2015-0240, affects versions […]
 Pierluigi Paganini
February 24, 2015
Experts at Facebook have discovered at least ten more applications using the Komodia library that allows Superfish adware traffic hijacking capabilities. Matt Richard security researcher from Facebook revealed that The Social Network has discovered at least ten more software applications using the Komodia library that allow Superfish adware traffic hijacking capabilities. Komodia installs a self-signed […]
 Pierluigi Paganini
February 23, 2015
Lenovo, with the support of Microsoft and McAfee, has developed a removal tool to clean its laptop and delete the Superfish malware. Last week, the news of the presence of Superfish adware in the laptops sold by the Chinese Lenovo has captured the attention of the media. The presence of the Superfish malware exposes Lenovo users to […]
 Pierluigi Paganini
February 23, 2015
The cyber security expert Ashiq JA analyzed the principal characteristics of APT (Advanced Persistent Threat) and AVT (Advanced Volatile Threat) . Cybercriminals and their techniques in the APT and AVT attacks “APT is an attack in the persistent memory that resides in the victims machine without getting noticed and the attacker exfiltrates sensitive information from […]
 Pierluigi Paganini
February 23, 2015
Three months from the incursion in the network of the U.S. State Department e-mail system, US specialists are still working to secure the networks. In November 2014 the State Department has taken the unprecedented step of shutting down its entire unclassified email system in response to a suspected cyber attack. ‘Activity of concern’ was detected in the […]
 Pierluigi Paganini
February 23, 2015
A cyber Manhattan Project seems to have been on the move for over a decade, providing the US with a great advantage related to online surveillance. Despite belief, no defensive purposes have triggered its setting up. Everybody recalls the notorious Manhattan Project at the end of World War II, which has resulted in the development […]