19320 results
 Pierluigi Paganini
 November 28, 2014
Twitter announced app graph, it will now track every mobile app its users have Installed on their smartphones and tables. Privacy advocates arise. Twitter announced the implementation of the “app graph” function that will allow the company to provide “more personal Twitter experience” by serving targeted advertisements by serving targeted advertisements. This means that also Twitter, like […]
 Pierluigi Paganini
November 28, 2014
A group of researchers at the University of Luxembourg have demonstrated that is it possible to de-anonymize Bitcoin users from its transactions. The majority of Bitcoin users consider the virtual currency absolutely anonymous, but researchers at the University of Luxembourg have demonstrated that is it possible to de-anonymize clients in a Bitcoin P2P network. In the paper written […]
 Pierluigi Paganini
November 27, 2014
High profile global websites using the customer management platform Gigya suffered a traffic redirection attack operated by the Syrian Electronic Army. A significant number of popular websites belonging to media organizations appeared to has been hacked by the hacking collective of Syrian Electronic Army on Thursday. The apparently hacked website, including The Independent, Telegraph e […]
 Pierluigi Paganini
November 27, 2014
The industrial supplier Siemens has patched two critical vulnerabilities in its solutions, Siemens WinCC application in use must be updated urgently. The industrial supplier Siemens has patched two critical vulnerabilities in the Siemens application that bad actors are exploiting in the wild. Siemens has also informed its customers that its researchers are already working on updates […]
 Pierluigi Paganini
November 27, 2014
Security experts at IntelCrawler discovered a strain of PoS malware that is also targeting ticket vending machines and electronic kiosks. IntelCrawler cyber threat intelligence firm has detected a new strain of Point-of-Sale malware called “d4re|dev1|” (read dareldevil), which is used by cyber criminals to infect ticket vending machines and electronic kiosks. The experts discovered new POS malware infecting Mass […]
 Pierluigi Paganini
November 26, 2014
The Digital Citizens Alliance Security provided data related to the growth of dark markets like Evolution after the operation Onymous operated by police. Recently law enforcement in a joint effort against cybercrime, dubbed operation Onymous, seized dozens of black markets on Tor Networks. While all the the underground marketplaces in the DeepWeb, including Silk Road 2.0, went […]
 Pierluigi Paganini
November 26, 2014
Adobe has released yesterday an out-of-band update to fix a critical remote code-execution vulnerability CVE-2014-8439 in Flash Player that is being exploited in the wild. Adobe has released an emergency patch to patch a critical remote code-execution vulnerability (CVE-2104-8439) affecting Flash Player that was already fixed last month (Adobe’s Oct. 14th), but that was exploited […]
 Pierluigi Paganini
November 26, 2014
FireEye discovered that the Group of hackers dubbed APT3 that managed the Op Clandestine Fox is now running a new campaign dubbed Operation Double Tap. Researchers at FireEye have uncovered a new advanced persistent threat crew dubbed APT3, which is using exploits targeting recently disclosed vulnerabilities in Windows. The experts at FireEye believe that APT3 is the same […]
 Pierluigi Paganini
November 25, 2014
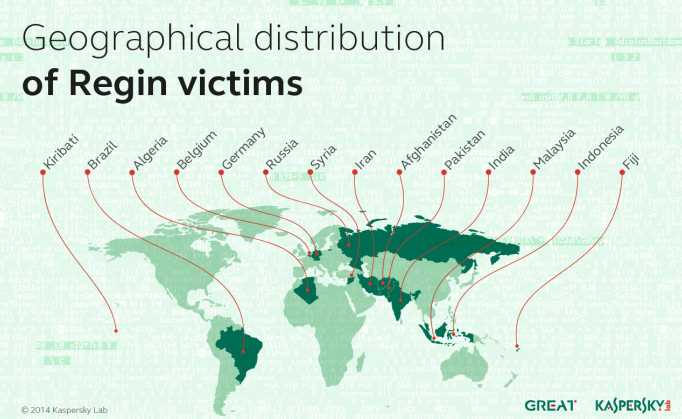
Security experts at Kaspersky Lab issued a detailed paper on the analysis of the backdoor Regin focusing on the attacker’s activity against the GSM networks. The day after the disclosure of the Regin Backdoor by Symantec, which provided the details the new sophisticated cyber espionage tool,the principal security firms published the results of their investigation. As […]
 Pierluigi Paganini
November 25, 2014
TrendMicro explained the mechanisms behind the hacking of RFID payment smartcards, explained how to do it with an Android App. Security experts recently spotted an Android app used to hack the NFC based electronic payment system used in Chile, the “Tarjeta BIP!”. The malicious Android app detected as ANDROIDOS_STIP.A was designed to attack NFC devices and distributed online through forums and blogs. […]