19319 results
 Pierluigi Paganini
 June 30, 2014
Anonymous has announced the campaign dubbed Operation NO2ISIS against some states it accuses of supporting the Islamic terror group ISIS. The group of hacktivists Anonymous has announced a new campaign dubbed Operation NO2ISIS against some nations it accuses of funding or arming the radical Islamic terror group ISIS. In particular Anonymous will target three states suspected of […]
 Pierluigi Paganini
June 29, 2014
ENISA and Europol have signed an agreement with the intent to facilitate the cooperation in the fight to the cyber criminal activities. The fight to the cybercrime needs a joint effort of governments, law enforcement agencies and private entities. Cyber threats are becoming even more sophisticated and bad actors behind them are structured in efficient organizations difficult […]
 Pierluigi Paganini
June 29, 2014
Experts at AdaptiveMobile discovered a rare Android SMS worm dubbed Selfmite which spreads itself by sending SMS including a malicious link to the contact list. Security researchers at AdaptiveMobile have discovered a rare Android malware dubbed Selfmite that propagates via SMS text messages, the worm in fact sends malicious links to 20 contacts present in the device owner’s address book. Selfmite […]
 Pierluigi Paganini
June 28, 2014
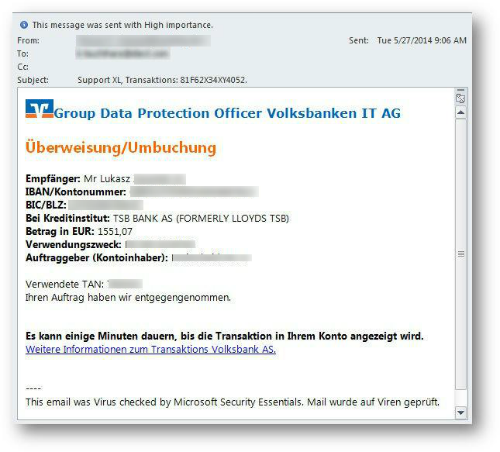
Security Experts at Trend Micro have detected a new banking malware, dubbed EMOTET, which uses also network sniffing capabilities to target bank customers. The number of malware families designed to hit the banking industry is in constant growth, in this first part of the year the number of malicious code used by cyber criminals for […]
 Pierluigi Paganini
June 28, 2014
A serious code-execution vulnerability in Android 4.3 and earlier was patched with latest KitKat Android Operating System version. Are you using the Android 4.3 version and you are convinced to be secure? You are unfortunately wrong, because this version of Android and earlier are affected by a critical code-execution vulnerability. According to data proposed by the Android […]
 Pierluigi Paganini
June 27, 2014
Trend Micro analyzed a targeted attack against a Taiwanese government entity which used a variant of the PlugX RAT that abuses the Dropbox service. Researchers from Trend Micro discovered that a targeted attack against a government agency in Taiwan was conducted using a variant of the PlugX remote access tool (RAT) which abuses the popular file hosting service […]
 Pierluigi Paganini
June 27, 2014
Security experts at Lookout mobile security discovered a phishing campaign against an Israeli bank based which exploited a cloned mobile application. Cloned mobile applications are increasily used as an attack vector for by bad actors, malicious code could be used to steal information, as an essential part of an extortion scheme or for fraudulent activities such as dialing premium numbers. […]
 Pierluigi Paganini
June 26, 2014
A critical vulnerability in the WebShot feature implemented by TimThumb plugin expose WordPress instance to Remote Code Execution attacks. The popular image resizing library TimThumb used in many WordPress themes, 3rd party components and plugins is affected by a critical vulnerability which allows an attacker for certain commands to be remotely executed, without authentication, on the vulnerable website. The discovery of the […]
 Pierluigi Paganini
June 26, 2014
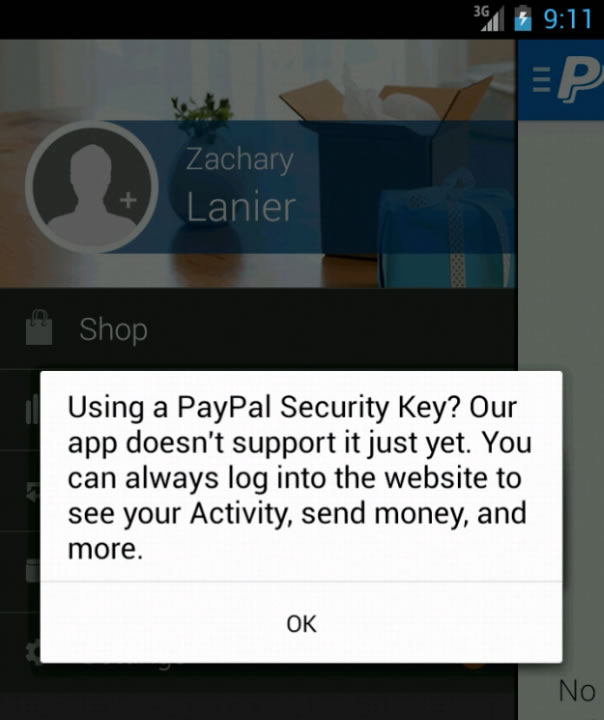
Security experts at Duo Security have discovered a serious flaw in the implementation of two-factor authentication which allow attackers to bypass it. Two-factor authentication processes if flawed could give to companies a false sense of security even if we are discussing of PayPal. In the past we have explained how to by-pass Two-factor authentication in various ways, for example, using […]
 Pierluigi Paganini
June 25, 2014
Security Experts at F-Secure discovered a cyber espionage campaign based in the Havex malware targeting ICS/SCADA systems and vendors. Security Experts at F-Secure have conducted an investigation on the Havex Malware family in the past months, let’s remember that the malicious agent has been used in several targeted attacks against different industry sectors, and according […]