


19314 results
 Pierluigi Paganini
 February 02, 2014
Researcher Dana Taylor is warning on the existence of two critical vulnerabilities in Oracle servers in the wild since a long time. Two serious vulnerabilities affect Oracle’s older database packages, allowing an attacker to remotely access a server bypassing authentication mechanism. Exploiting the flaws the attackers can browse the filesystem of the server accessing any files. […]
 Pierluigi Paganini
February 02, 2014
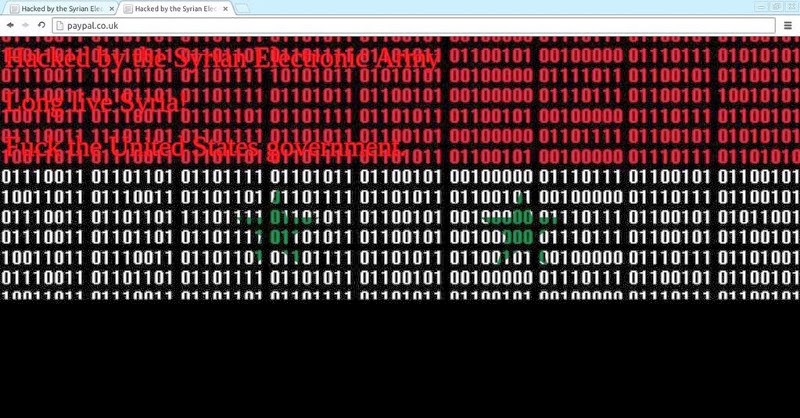
Ebay and PayPal hacked by Syrian Electronic Army, “For denying Syrian citizens the ability to purchase online products” said SEA. The group of hackers Syrian Electronic Army (SEA) has monopolized the attention of the media, the hacking team has practically hit every possible target within government organizations, big enterprises and media agencies. The list of […]
 Pierluigi Paganini
February 01, 2014
Cyber Defense Magazine (CDM) CYBER WARNINGS JANUARY 2014 EDITION is available for free. Yes, 2014 is here and we’re surrounded by more and more personally identifiable information (PII) theft, as predicted. Keep an eye on these at http://www.privacyrights.org and find out that we all have common vulnerabilities and exposures (CVEs) which are searchable here at the National Vulnerability Database […]
 Pierluigi Paganini
February 01, 2014
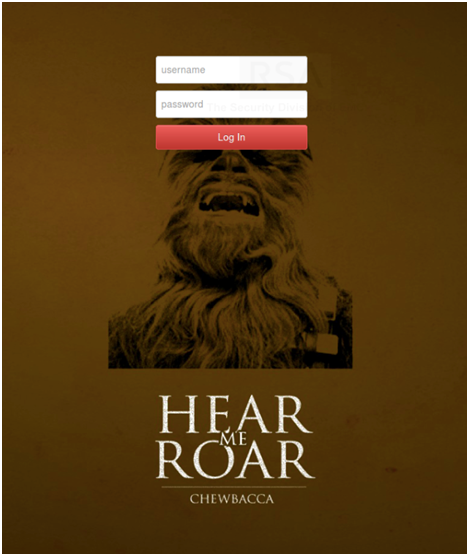
Researchers at RSA discovered a new variant of Tor-based malware ‘ChewBacca’, is able to infect Point-of-Sale stealing Credit Card data. The recent data breaches at US retailers Target, Neiman Marcus and Michaels have raised the alert level of malware-based attacks against POS systems. More than one hundred million Americans is victims of scams that mainly used a malware known as BlackPOS or […]
 Pierluigi Paganini
January 31, 2014
The company has issued a security advisory to warn users that Yahoo Mail Service was hacked, hackers have stolen credentials of its email customers. Yahoo Mail! is considered one of the largest email service providers, millions of people use is every day, it’s clear that it represents an attractive target for cyber criminals. The […]
 Pierluigi Paganini
January 31, 2014
Andreas Lindh has discovered serious vulnerabilities in an unknown number of 3G/4G USB modems that can be exploited by attackers for spear phishing attacks. The researcher Andreas Lindh has discovered serious vulnerabilities in an unknown number of 3G and 4G USB modems that can be exploited by attackers to steal user’s credential. The expert has found a Cross Site […]
 Pierluigi Paganini
January 30, 2014
Interviewed with Mark Collier, CTO and VP of Engineering at Securelogix to better understand the topic of Telephony Denial of Service (TDoS). I briefly interviewed Mark Collier, CTO and VP of Engineering at SecureLogix (Www.securelogix.com) on the topic of Telephony Denial of Service (TDoS). Mark just completed the Hacking Exposed: UC and VoIP book, which covers […]
 Pierluigi Paganini
January 30, 2014
Russian company Doctor Web detected Android.Oldboot, an Android Trojan that resides in the memory of infected devices and starts on OS bootstrapping. The Russian security firm Doctor Web has detected the first mass distributed Android bootkit malware dubbed Android.Oldboot, its principal capability is to re-infect the Smartphone after reboot, even if all its components are […]
 Pierluigi Paganini
January 29, 2014
Edward Snowden revealed to the German public broadcaster ARD TV that the NSA is involved in industrial espionage against foreign governments and businesses. The former NSA contractor Edward Snowden revealed that the National Security Agency is responsible of industrial espionage, for year governments are blaming China for cyber espionage and now the popular whistleblower presented an uncomfortable truth to […]
 Pierluigi Paganini
January 29, 2014
A serious vulnerability inside Mozilla Thunderbird Gecko engine allows hackers to insert malicious code into Emails to exploit recipient browser. A critical vulnerability affects the email client Mozilla Thunderbird 17.0.6, the popular application has a validation and filter bypass vulnerability that could be exploited by hackers to bypass the filter that prevents HTML tags from being used in […]







