19313 results

 Pierluigi Paganini
 August 26, 2013
The FBI claims to have neutralized Anonymous thanks the long series of arrests that hit principal cells of the collective such as LulzSec, Antisec and SABU. FBI in the last months has intensified the investigation on the Anonymous collective, various members of the popular group of hacktivist have been identified and arrested. Lulz Security (Lulzsec) team recognized its responsibility for the Sony Picture […]
 Pierluigi Paganini
August 25, 2013
Security vendor FireEye has published a detailed analysis on the popular Poison Ivy RAT, releasing also a set of tools to analyze infections. Security firm FireEye published an interesting analysis on the popular malware Poison Ivy, a remote access trojan (RAT) used in RSA SecurID attack. Poison IVY was also used in the 2011 Nitro […]
 Pierluigi Paganini
August 24, 2013
Security researcher Dan Melamed has found a serious Pinterest Exploit that exposed user’s information of over 70 Million accounts. The security researcher Dan Melamed has found a Critical Pinterest Exploit that compromised the privacy of over 70 Million Users, the flaw allows hackers to view the email address of any user on Pinterest. Pinterest is a very popular […]
 Pierluigi Paganini
August 23, 2013
The cyber Security Analyst Consultant at Q-CERT Ebrahim Hegazy has found an “Unvalidated Redirection Vulnerability” in the website of the giant security solutions vendor “Kaspersky”. Ebrahim Hegazy (@Zigoo0) has found an “Unvalidated Redirection Vulnerability” in the website of the giant security solutions vendor “Kaspersky”. Ebrahim Hegazy is the cyber Security Analyst Consultant at Q-CERT who found a SQL […]
 Pierluigi Paganini
August 22, 2013
Fraudsters target wire payment switch at US banks to steal millions using DDoS to divert the attention on fraudulent transactions. Cybercriminals are targeting the wire payment switch instead to hit directly into the banking accounts of individuals and businesses, this appears to be the last trend observed for recent attacks against numerous US banks. The wire payment switch […]
 Pierluigi Paganini
August 21, 2013
ENISA issued the ENISA Annual Incident Reports 2012 on significant incidents in the electronic communications sector, which were reported to national regulators in 2012. ENISA published the ENISA Annual Incident Reports 2012, a document that provides an overview of the process and an aggregated analysis of the 79 incident reports of severe outages of electronic […]
 Pierluigi Paganini
August 20, 2013
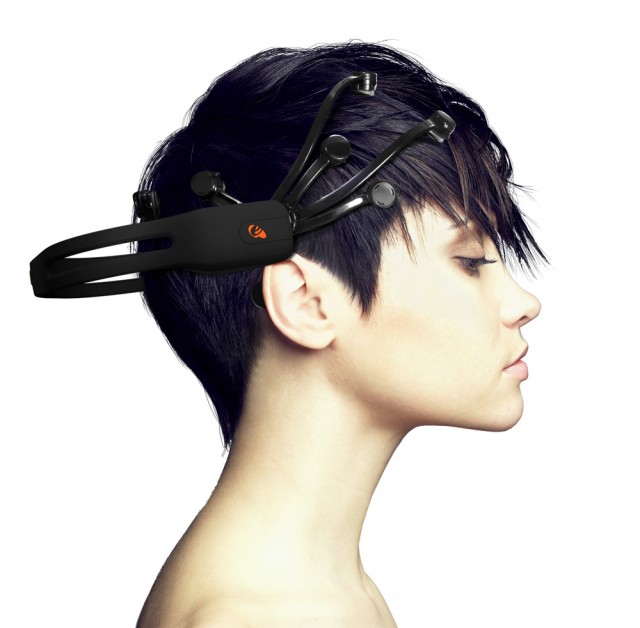
Brain hacking is the act to read the content of the human brain and modify it, is the technology mature to allow hackers to penetrate our mind? Brain hacking refers the possibility to attack the human brain to extract sensitive information such as data and memories, including also the capability to inject new information. Exactly as any other […]
 Pierluigi Paganini
August 19, 2013
Indian hacker reported a Short Password Reset code vulnerability that could allow attackers to brute-force many high profile websites not protected by CAPTCHA verification system. Yesterday we received a vulnerability report in web applications from some unknown Indian Hacker who explained that how Hackers are hijacking Mobile recharge and Free SMS service related websites. He […]
 Pierluigi Paganini
August 19, 2013
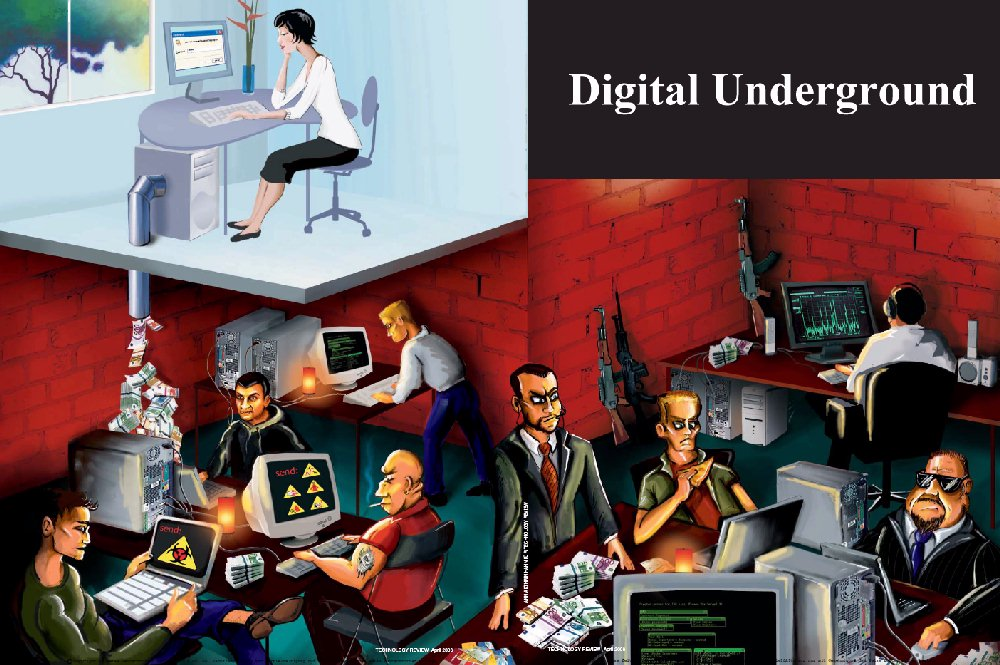
Security expert Dancho Danchev profiled one of the numerous hacking services offered in the underground highlighting new trends in the cybercrime ecosystem. With the term attack-as-a-service model is indicated the practice to outsource all the phases of an attack to specialists instead to rent tools and architecture to conduct personally the illegal activities (Malware-as-a-Service). Danchev […]
 Pierluigi Paganini
August 18, 2013
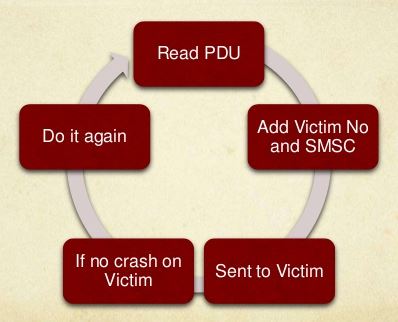
The Indian security expert ‘Rahul Sasi’ found a USB Internet Modems vulnerability that could allow to gain Meterpreter shell or full access to the victim just sending an SMS. The Indian Security expert ‘Rahul Sasi‘ announced to have found a USB Internet Modems vulnerability that could allow an attacker to execute malicious code remotely simply sending an SMS […]