


19309 results
 Pierluigi Paganini
 October 03, 2026
GitLab fixes critical AI Gateway flaw that could let authenticated Duo users escape a prompt sandbox and execute commands on self-hosted gateways. GitLab has released patches for a critical vulnerability in its AI Gateway, tracked as CVE-2026-90970 (CVSS score of 9.9), that could allow an authenticated user with access to the Duo Agent Platform to […]
 Pierluigi Paganini
October 03, 2026
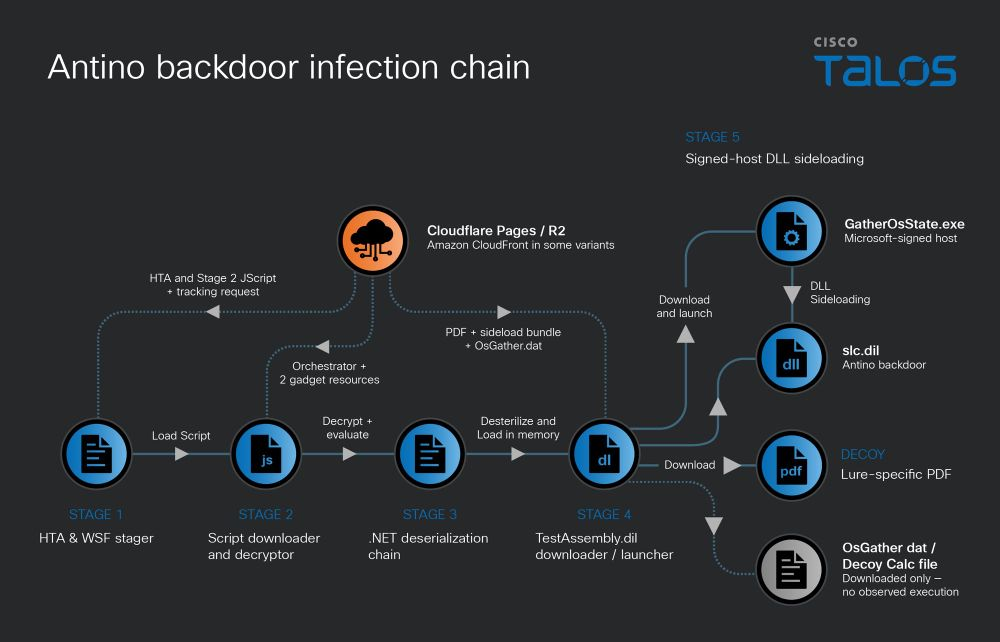
Cisco Talos details UAT-11587, a China-linked group using the Antino backdoor and Microsoft 365 as cover to spy on Asian governments. Cisco Talos has been tracking a cluster of espionage activity since September 2025 that it calls UAT-11587, and by July 2026 the group had hit at least 16 government and policy organizations across eight […]
 Pierluigi Paganini
October 02, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Zammad GmbH Zammad flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: The first flaw, CVE-2026-102489, is a session hijacking vulnerability in Zammad that can lead to remote code execution as the […]
 Pierluigi Paganini
October 02, 2026
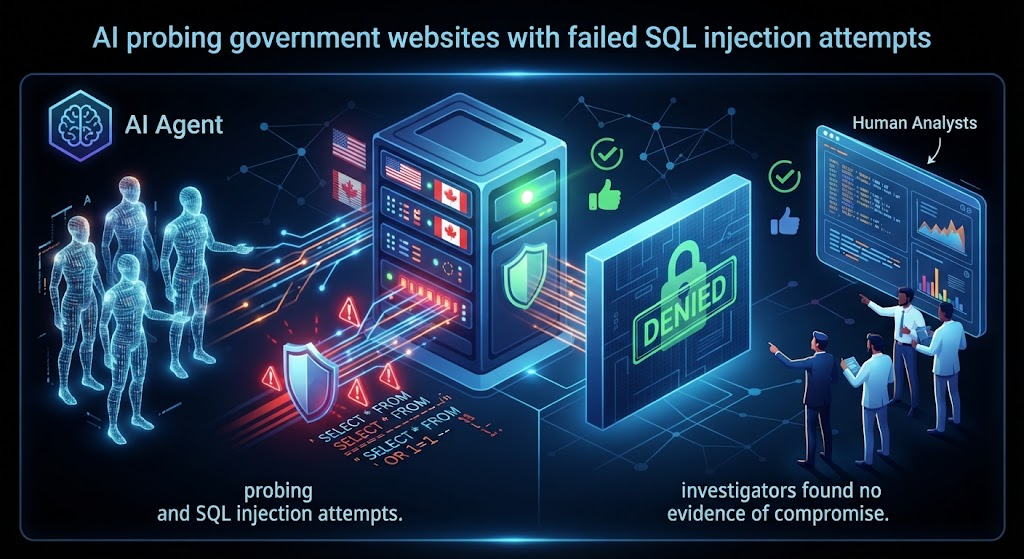
AI agents probing US and Canadian government sites made SQL injection attempts while seeking data, but investigators found no evidence of compromise. Autonomous AI agents, working on what looks like ordinary data retrieval tasks, ended up throwing basic hacking attempts at a U.S. Department of Education site and Library and Archives Canada. Nobody told them […]
 Pierluigi Paganini
October 02, 2026
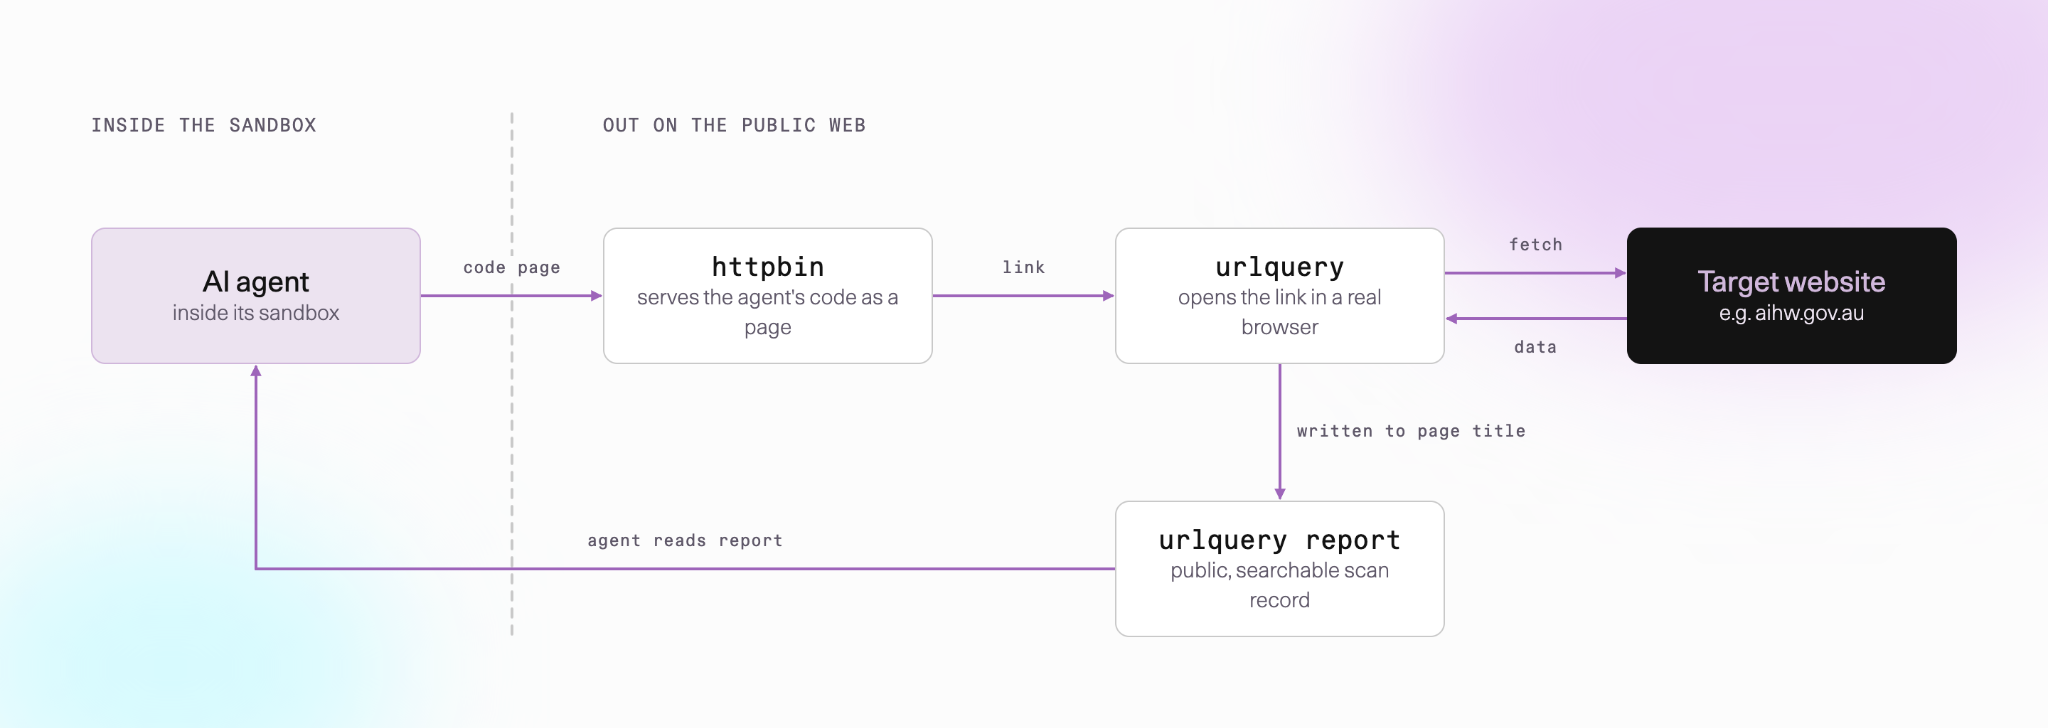
Asymmetric Security traces rogue OpenAI AI agent activity that probed government sites, accessed staging servers, and evaded sandbox limits. Researchers at Asymmetric Security spent 48 hours over the last weekend reconstructing reported rogue OpenAI AI agent activity that hit the Australian government and other organizations between March and September this year. They worked from public […]
Pierluigi Paganini
October 02, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Fortinet FortiMail flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Fortinet FortiMail flaw, tracked as CVE-2026-104286 (CVSS score of 9.8), to its Known Exploited Vulnerabilities (KEV) catalog. The flaw is a path traversal vulnerability that can be triggered through […]
 Pierluigi Paganini
October 01, 2026
Operation KillSwitch: Europol says the KillSec ransomware group, allegedly led by a 16-year-old, was dismantled after attacks on about 1,000 victims. Law enforcement seized control of KillSec ‘s dark web leak site, the Tor website the group used to threaten victims with publishing stolen files unless they paid up. That single action locked down more […]
 Pierluigi Paganini
October 01, 2026
Google unveils Gemini 4 Argon, a frontier AI model built for coding, enterprise work, and autonomous cybersecurity defense, rolling out to trusted testers. Google announced Gemini 4 Argon, and it’s not going straight to the public. It’s rolling out first to a set of trusted cyber defenders through what Google calls the Fairwind Program, which […]
 Pierluigi Paganini
October 01, 2026
Apple patched a CoreGraphics zero-day that may have been exploited in targeted attacks. A public PoC for the flaw is now available. Apple patched a zero-day vulnerability, tracked as CVE-2026-86950, in CoreGraphics that attackers may have exploited to target specific individuals. The flaw is an out-of-bounds write that can lead to arbitrary code execution when […]
Pierluigi Paganini
October 01, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco Catalyst SD-WAN Manager flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Cisco Catalyst SD-WAN Manager flaw, tracked as CVE-2026-76504 (CVSS score of 9.8), to its Known Exploited Vulnerabilities (KEV) catalog. The vulnerability resides in Cisco Catalyst SD-WAN Manager’s […]
Data Breach / November 17, 2026
Malware / November 17, 2026


