19303 results
 Pierluigi Paganini
 February 15, 2026
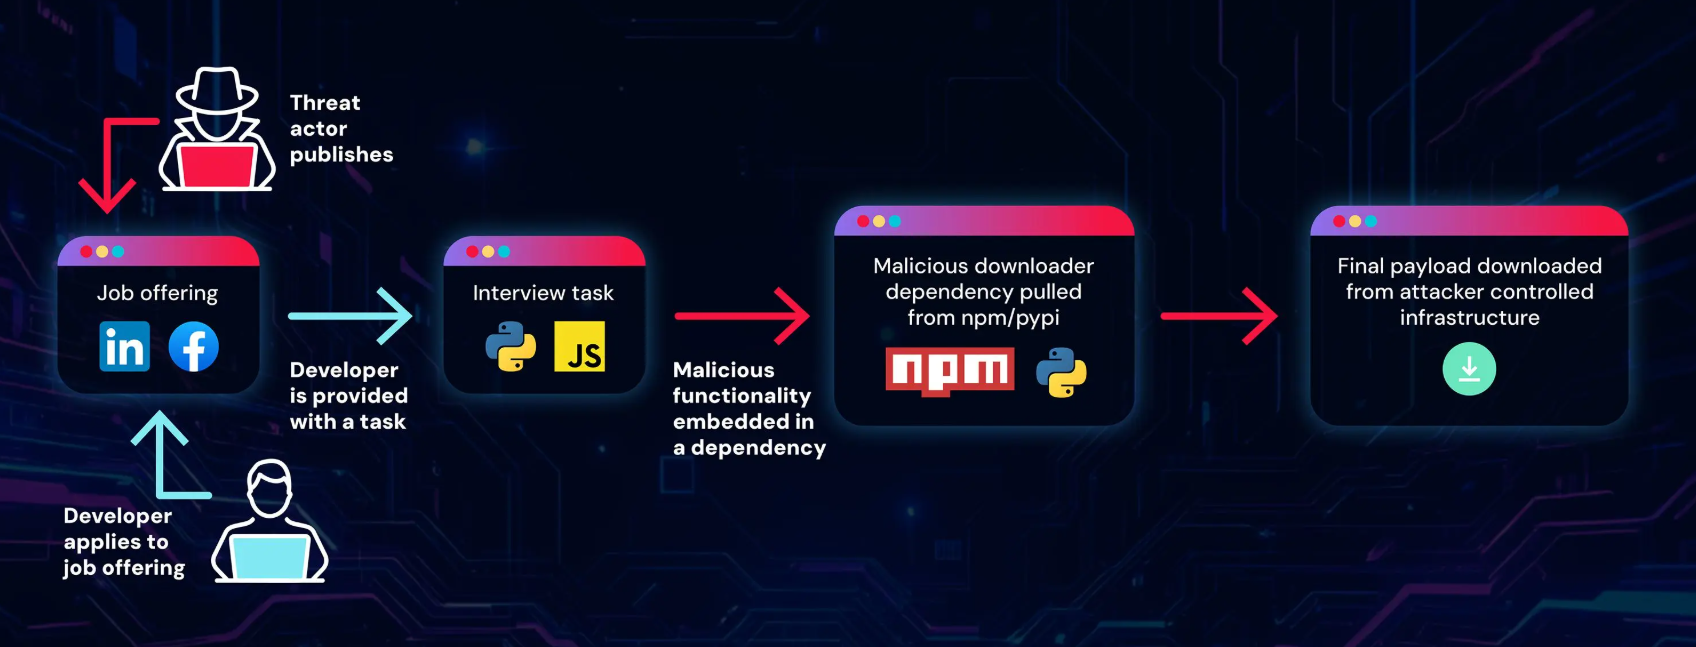
Researchers found malicious npm and PyPI packages tied to a fake recruitment campaign linked to North Korea’s Lazarus Group. ReversingLabs researcher uncovered new malicious packages on npm and PyPI connected to a fake job recruitment campaign attributed to the North Korea-linked Lazarus Group. The campaign uses deceptive hiring themes to trick developers into downloading infected […]
 Pierluigi Paganini
February 15, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Stan Ghouls targeting Russia and Uzbekistan with NetSupport RAT Breaking Down ZeroDayRAT – New Spyware Targeting Android and iOS Old-School IRC, New Victims: Inside the Newly Discovered SSHStalker Linux Botnet Reynolds: Defense Evasion Capability […]
 Pierluigi Paganini
February 14, 2026
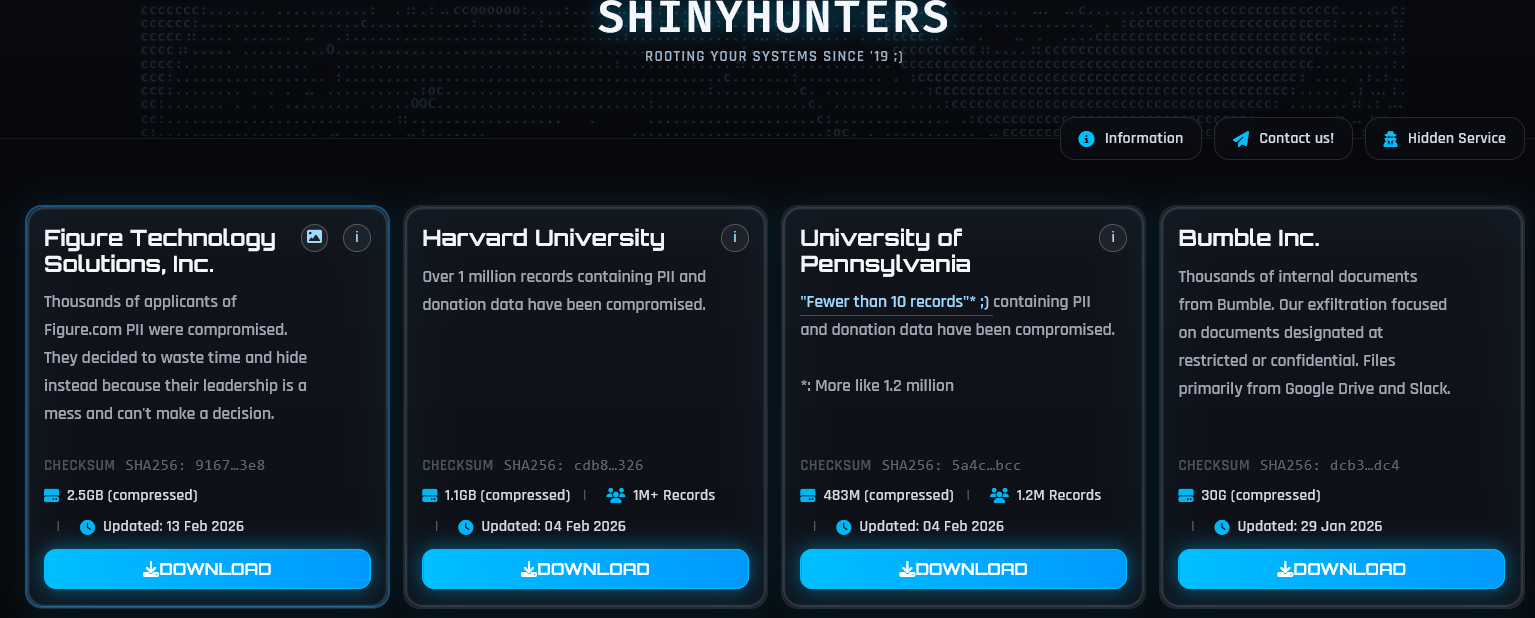
Fintech firm Figure confirmed a data breach after hackers used social engineering to trick an employee and steal a limited number of files. Blockchain-based lending firm Figure confirmed a data breach after an employee fell victim to a social engineering attack. According to a company spokesperson, the incident allowed hackers to access and steal a […]
 Pierluigi Paganini
February 14, 2026
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a flaw in BeyondTrust RS and PRA to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an BeyondTrust RS and PRA vulnerability, tracked as CVE-2026-1731 (CVSS score of 9.9), to its Known Exploited Vulnerabilities (KEV) catalog. This week BeyondTrust released security updates to […]
 Pierluigi Paganini
February 14, 2026
A new alleged Russia-linked APT group targeted Ukrainian defense, government, and energy groups, with CANFAIL malware. Google Threat Intelligence Group identified a previously undocumented threat actor behind attacks on Ukrainian organizations using CANFAIL malware. The group is possibly linked to Russian intelligence services and has targeted defense, military, government, and energy entities at both regional […]
 Pierluigi Paganini
February 13, 2026
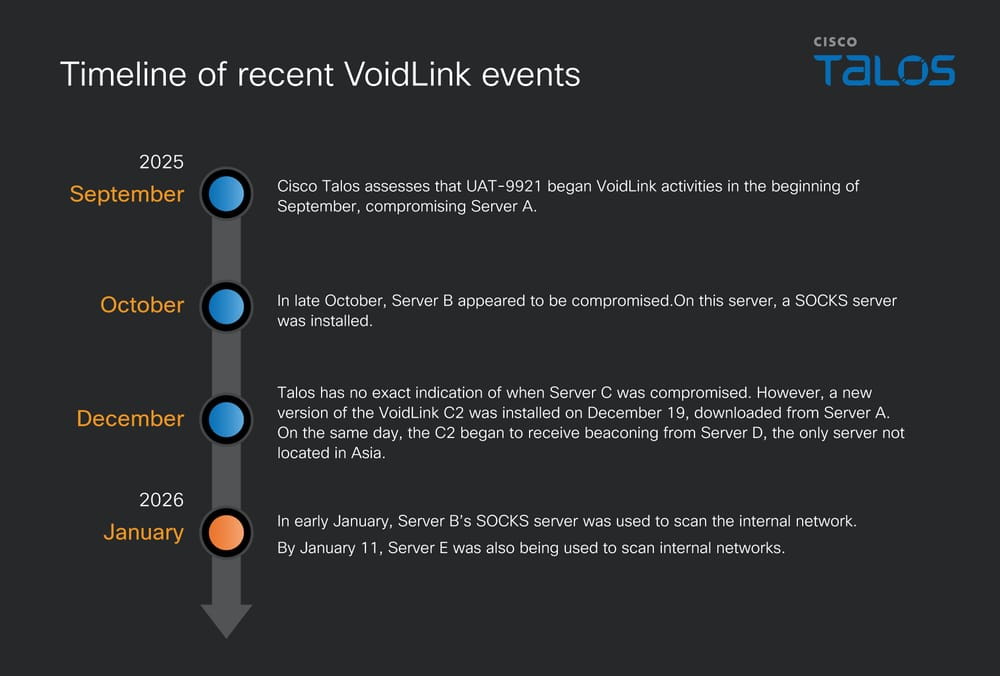
A new threat actor, UAT-9921, uses the modular VoidLink framework to target technology and financial organizations, Cisco Talos reports. Cisco Talos spotted a previously unknown threat actor, tracked as UAT-9921, using a new modular attack framework called VoidLink. The group targets organizations in the technology and financial services sectors. The flexible design of VoidLink suggests […]
 Pierluigi Paganini
February 13, 2026
Attackers quickly targeted BeyondTrust flaw CVE-2026-1731 after a PoC was released, enabling unauthenticated remote code execution. Threat actors rapidly began exploiting a newly patched BeyondTrust vulnerability, tracked as CVE-2026-1731 (CVSS score of 9.9), soon after a proof-of-concept exploit became public. This week BeyondTrust released security updates to address the critical flaw in its Remote Support […]
 Pierluigi Paganini
February 13, 2026
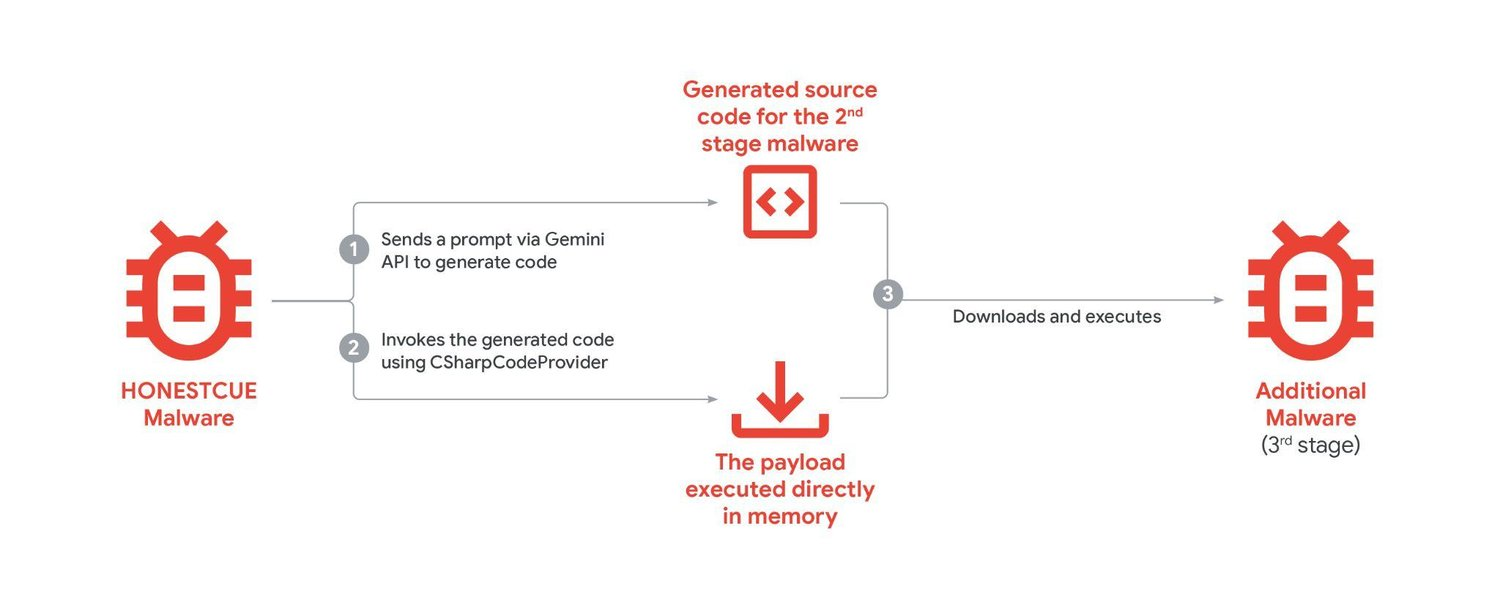
Google says nation-state actors used Gemini AI for reconnaissance and attack support in cyber operations. Google DeepMind and GTIG report a rise in model extraction or “distillation” attacks aimed at stealing AI intellectual property, which Google has detected and blocked. While APT groups have not breached frontier models, private firms and researchers have tried to […]
Pierluigi Paganini
February 13, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds SolarWinds Web Help Desk, Notepad++, Microsoft Configuration Manager, and Apple devices flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added SolarWinds Web Help Desk, Notepad++, Microsoft Configuration Manager, and Apple devices flaws to its Known Exploited Vulnerabilities (KEV) catalog. Below are the flaws […]
 Pierluigi Paganini
February 12, 2026
Hackers accessed data from 6.2 million Odido accounts, exposing names, contacts, bank details, and ID numbers. Subsidiary Ben also warned customers. Hackers broke into Dutch telecom firm Odido and accessed data from 6.2 million accounts. The company confirmed the breach and said attackers took names, addresses, phone numbers, email addresses, bank account details, dates of […]