 Pierluigi Paganini
 March 27, 2020
Researchers at Group-IB observed new financially motivated attacks in Western Europe traced to Russian-speaking threat actors. Group-IB, a Singapore-based cybersecurity company that specializes in preventing cyberattacks, has detected successful attacks in Western Europe carried out in late January 2020 traced to Russian-speaking threat actors. At least two companies operating in pharmaceutical and manufacturing sectors have […]
 Pierluigi Paganini
March 25, 2020
The China-linked group tracked as APT41 exploited vulnerabilities in Citrix, Cisco, and ManageEngine in a campaign on a global scale. The China-linked cyberespionage group tracked as APT41 exploited vulnerabilities in Citrix, Cisco, and Zoho ManageEngine in a campaign on a global scale. The campaign was uncovered by FireEye, threat actor targeted many organizations worldwide the […]
 Pierluigi Paganini
March 24, 2020
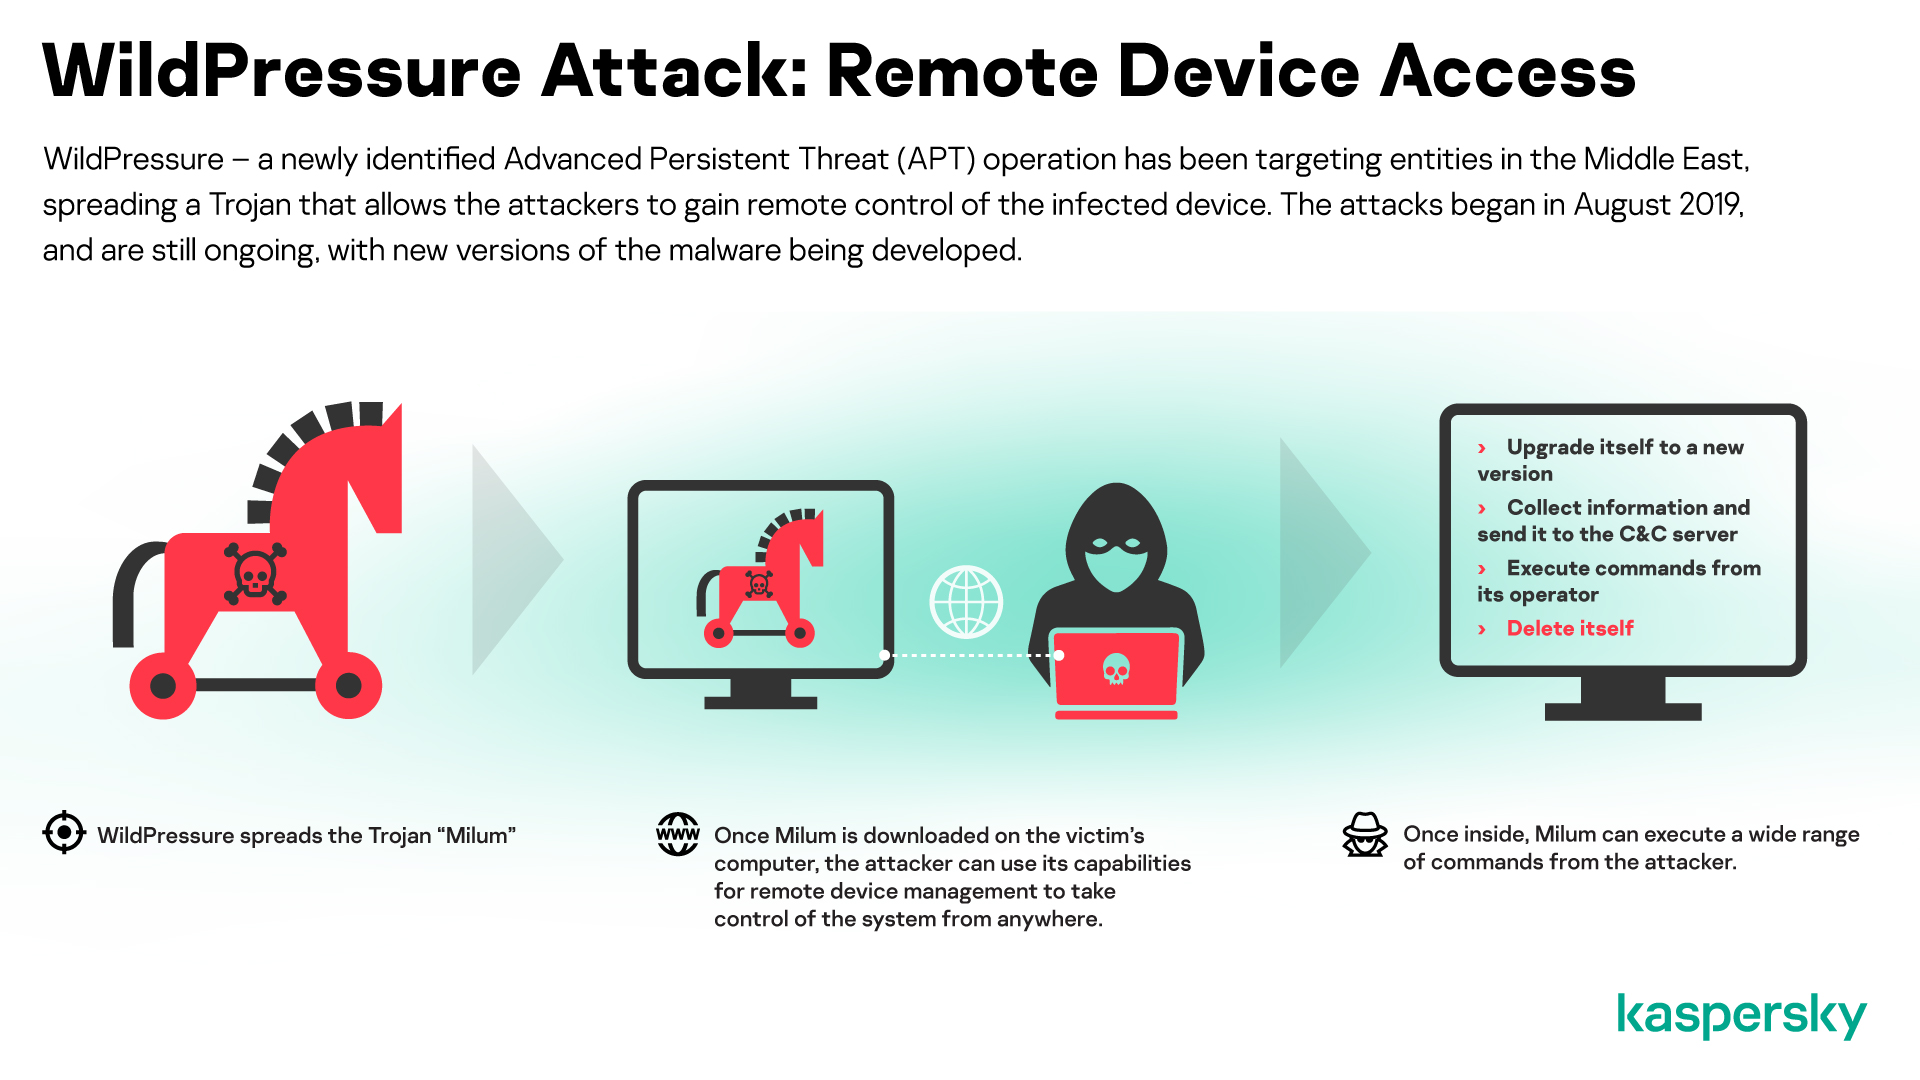
Security experts from Kaspersky Lab have uncovered the activity of a new threat actor, tracked as WildPressure, targeting the industrial sector in the Middle East. The WildPressure was spotted for the first time in August 2019 when researchers detected a never-before-seen malware that has no similarities with other samples analyzed by the experts. “In August […]
 Pierluigi Paganini
March 20, 2020
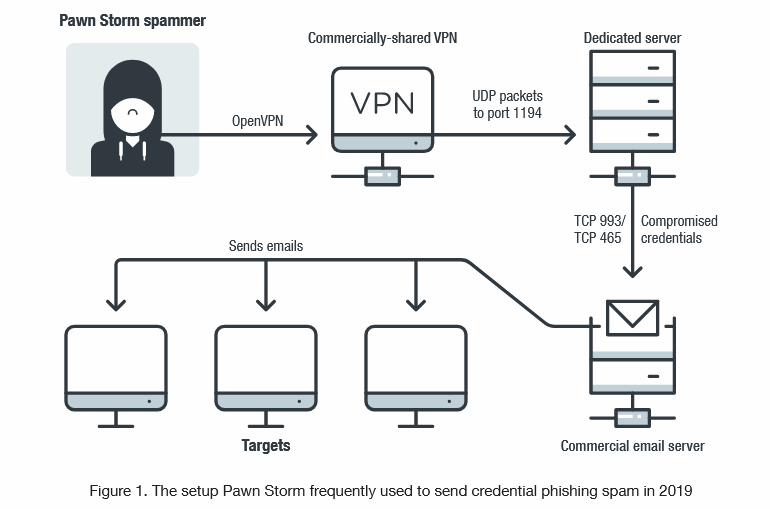
Experts warn of scanning activity conducted by Russia-linked APT28 cyberespionage group, hackers are searching for vulnerable mail servers. According to security researchers from Trend Micro, the Russia-linked APT28 cyberespionage group has been scanning vulnerable email servers for more than a year. The APT28 group (aka Fancy Bear, Pawn Storm, Sofacy Group, Sednit, and STRONTIUM) has been active since at least 2007 and it has […]
 Pierluigi Paganini
March 04, 2020
Chinese security firm Qihoo 360 revealed that the US CIA has hacked Chinese organizations in various sectors for the last 11 years. Chinese security firm Qihoo 360 is accusing that the US Central Intelligence Agency (CIA) of having hacked Chinese organizations for the last 11 years. According to the firm, the US cyber spies are targeting various industry sectors […]
 Pierluigi Paganini
March 03, 2020
Cybaze-Yoroi ZLab analyzed a new implant employed by a North Korea-linked APT group, tracked as Kimsuky, in attacks on South Korea. Introduction Recently we have observed a significant increase in state-sponsored operations carried out by threat actors worldwide. APT34, Gamaredon, and Transparent Tribe are a few samples of the recently uncovered campaigns, the latter was spotted after four […]
 Pierluigi Paganini
February 19, 2020
The DRBControl APT group has been targeting gambling and betting companies worldwide with malware that links to two China-linked APT groups. Security researchers from TrendMicro have uncovered a cyber espionage campaign carried out by an APT group tracked as DRBControl that employed a new family of malware. The attackers aimed at stealing databases and source […]
 Pierluigi Paganini
February 17, 2020
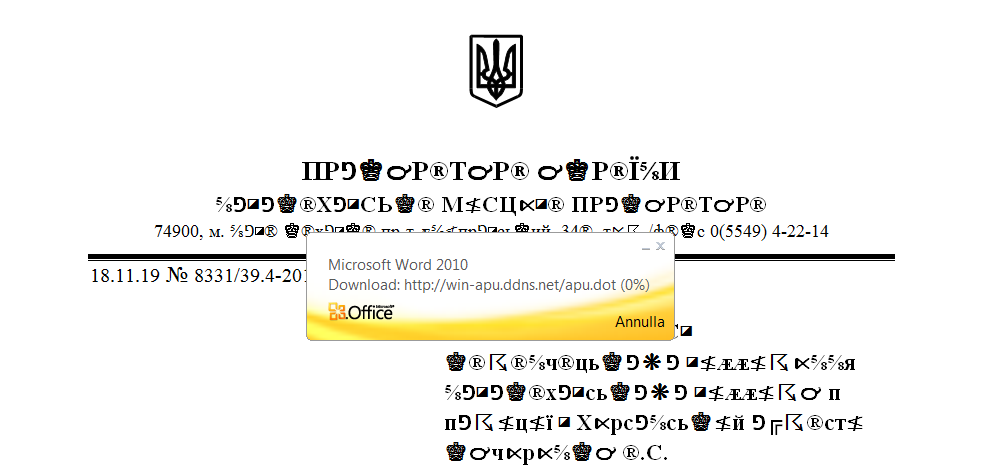
Security experts from Yoroy-Cybaze ZLab have conducted a detailed analysis of an implant used by the Gamaredon APT group in a recent campaign. Introduction Gamaredon Group is a Cyber Espionage persistent operation attributed to Russians FSB (Federal Security Service) in a long-term military and geo-political confrontation against the Ukrainian government and more in general against […]
 Pierluigi Paganini
February 17, 2020
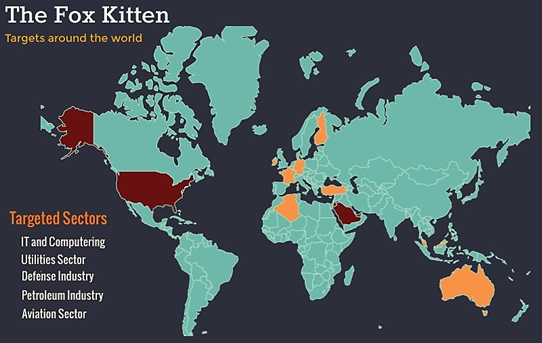
Iranian hackers have been hacking VPN servers to plant backdoors in companies around the world Iran-linked attackers targeted Pulse Secure, Fortinet, Palo Alto Networks, and Citrix VPNs to hack into large companies as part of the Fox Kitten Campaign. During the last quarter of 2019, experts from security firm ClearSky uncovered a hacking campaign tracked […]
 Pierluigi Paganini
February 14, 2020
The Federal Bureau of Investigation (FBI) and Cybersecurity and Infrastructure Security Agency (CISA) released reports on North Korea-linked HIDDEN COBRA malware. The FBI, the US Cyber Command, and the Department of Homeland Security have published technical details of a new North-Korea linked hacking operation. The government experts released new and updated Malware Analysis Reports (MARs) […]