 Pierluigi Paganini
 October 10, 2018
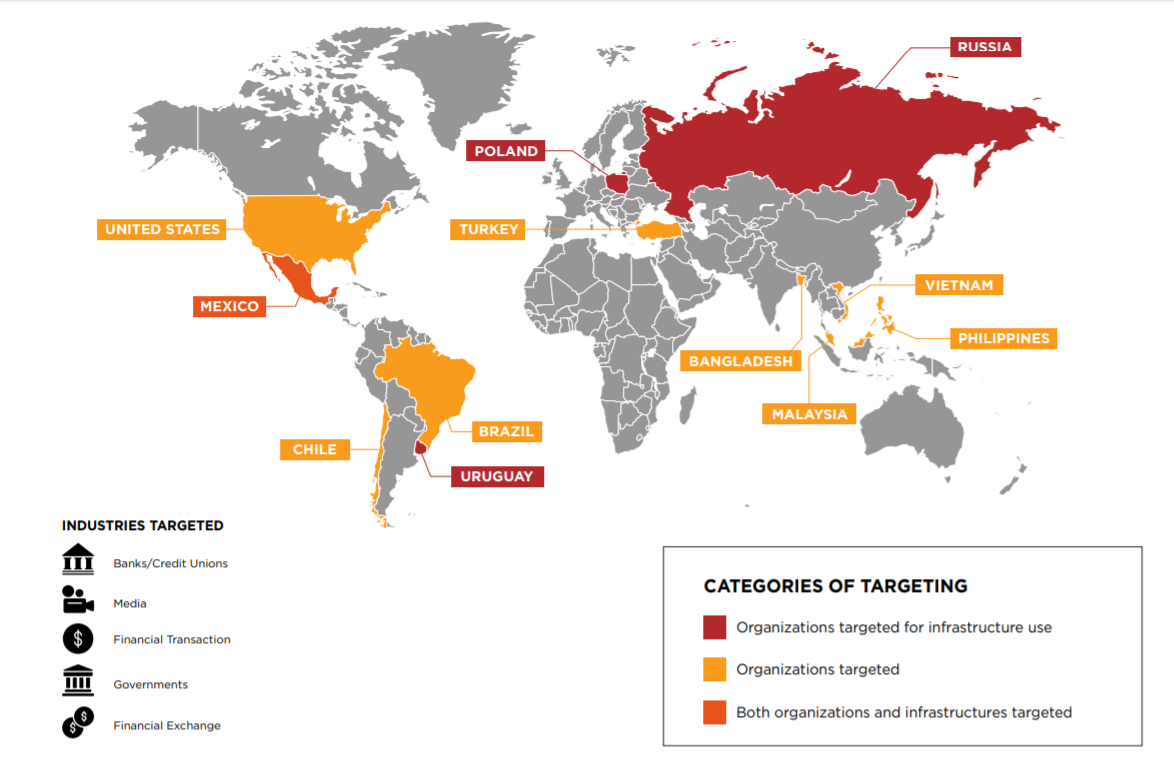
Security firm Group-IB has estimated that in H2 2017-H1 2018 cyber attacks caused $49.4 million (2.96 billion rubles) of damage to Russia’s financial sector Group-IB, an international company that specializes in preventing cyber attacks, has estimated that in H2 2017-H1 2018 cyber attacks caused $49.4 million (2.96 billion rubles) of damage to Russia’s financial sector. […]
 Pierluigi Paganini
October 08, 2018
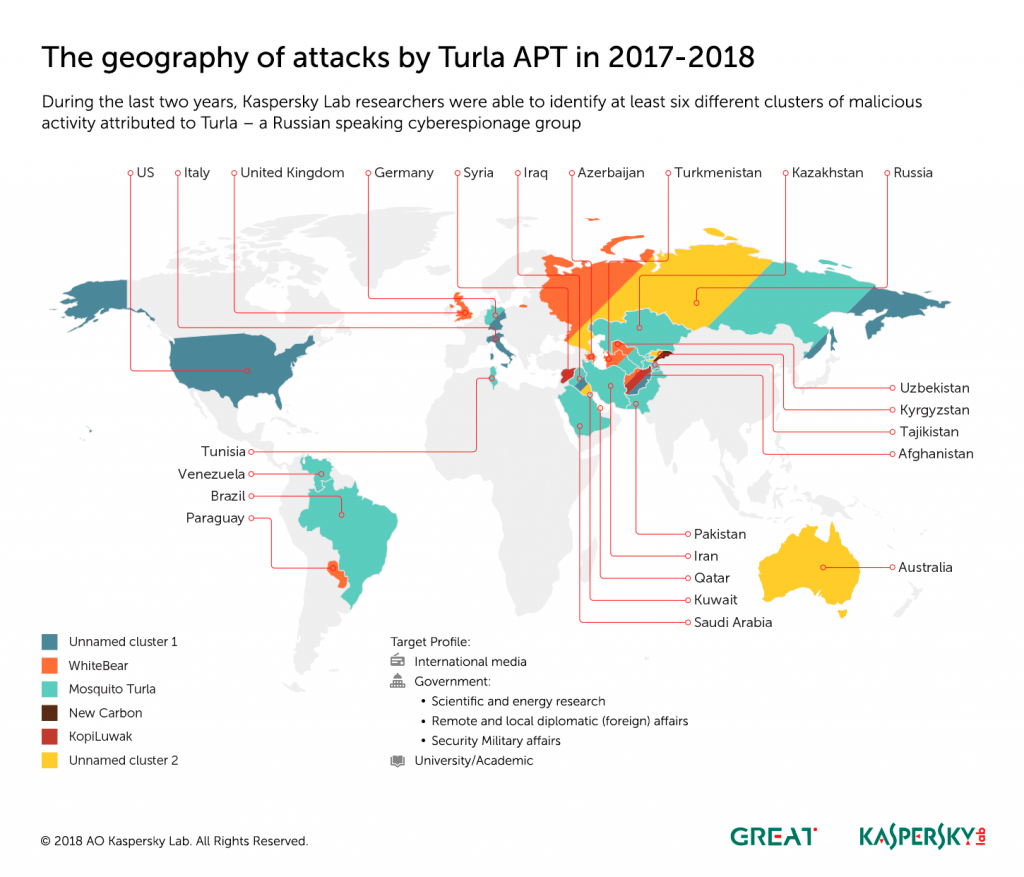
Researchers from Kaspersky Lab collected evidence that demonstrates overlaps between the activity of Russian APT groups Turla and Sofacy. In March, during the Kaspersky Security Analyst Summit held in Cancun, Kurt Baumgartner, Kaspersky principal security researcher, revealed the activity associated with Sofacy APT group appears to overlap with campaigns conducted by other cyber espionage groups. Baumgartner […]
 Pierluigi Paganini
October 05, 2018
The United States Department of Homeland Security (DHS) is warning of ongoing activity from an advanced persistent threat (APT) actor targeting global managed service providers (MSPs). The DHS issued an alert on ongoing attacks aimed at global managed service providers (MSPs) that are carried out by an advanced APT group. Managed services is the practice of outsourcing on a […]
 Pierluigi Paganini
October 04, 2018
Security experts from FireEye published a report on the activity of financially motivated threat actors, tracked as APT38, linked to the North Korean government. The attacks aimed at financial institutions, FireEye estimates APT38 has stolen at least a hundred million dollars from banks worldwide. APT38 appears to be a North Korea-linked group separate from the […]
 Pierluigi Paganini
September 06, 2018
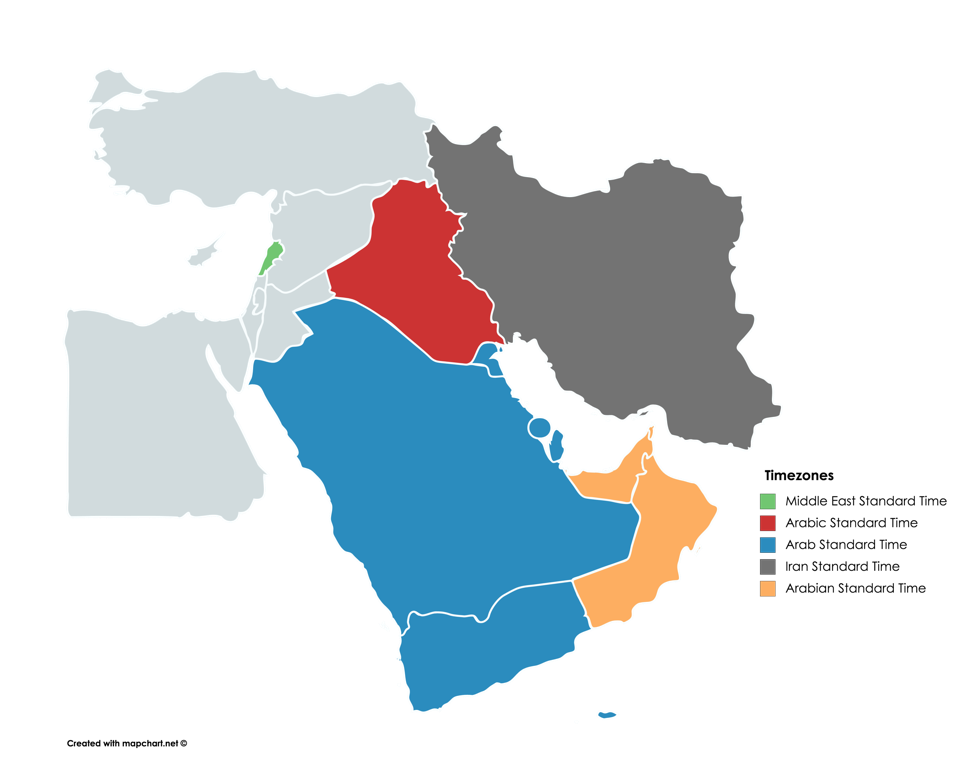
The Iran-linked APT group OilRig was recently observed using a new variant of the OopsIE Trojan that implements news evasion capabilities. Experts at Palo Alto Networks observed a new campaign carried out by the Iran-linked APT group OilRig that was leveraging on a new variant of the OopsIE Trojan. The OilRig hacker group is an Iran-linked APT that has been […]
 Pierluigi Paganini
September 05, 2018
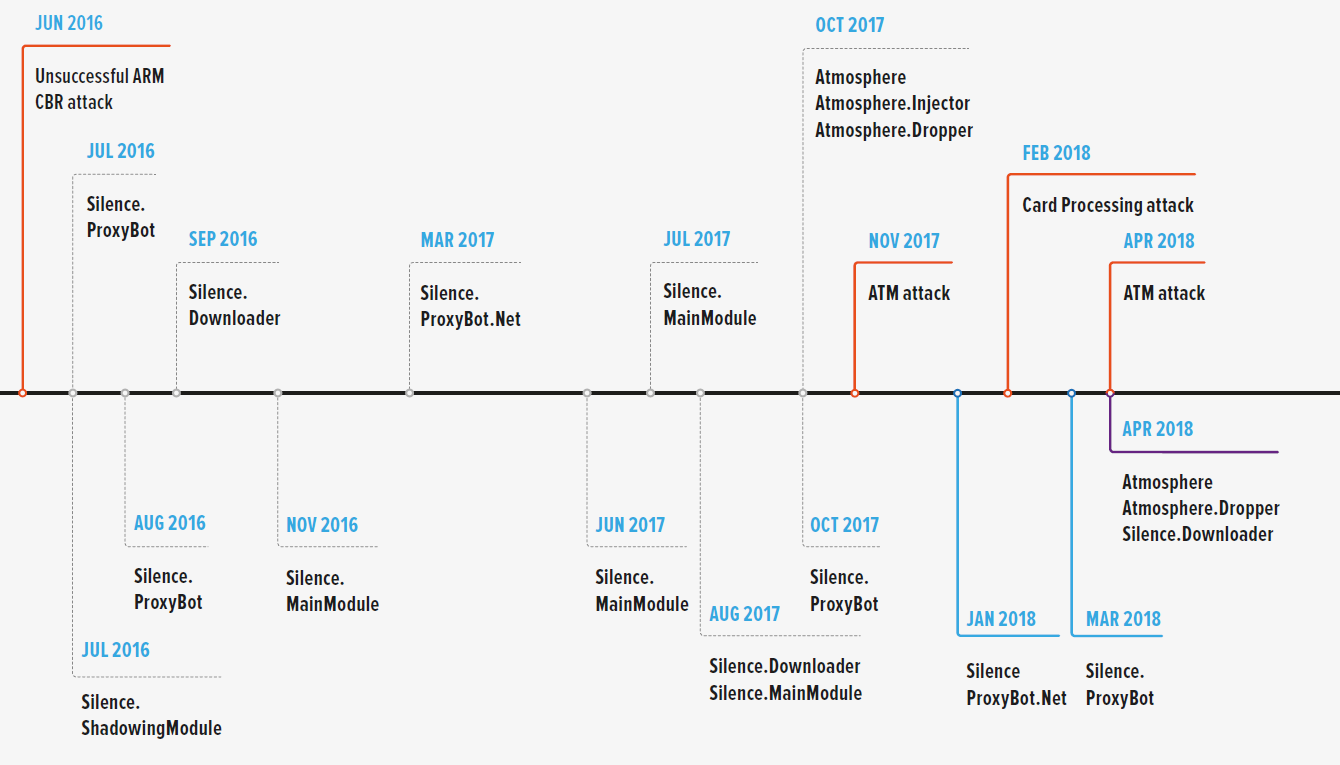
Researchers at security firm Group-IB have exposed the attacks carried out by the Silence cybercriminal group, providing details on its tactics and tools. Experts at security firm Group-IB have exposed the attacks committed by Silence cybercriminal group. While the gang had previously targeted Russian banks, Group-IB experts also have discovered evidence of the group’s activity in more than 25 countries worldwide. Group-IB […]
Pierluigi Paganini
September 05, 2018
Researchers from security firm CrowdStrike have observed a new campaign associated with the GOBLIN PANDA APT group. Experts from security firm CrowdStrike have uncovered a new campaign associated with the GOBLIN PANDA APT group. The group also knows as Cycldek was first spotted in September 2013, it was mainly targeting entities in Southeast Asia using different malware variants mainly PlugX and […]
 Pierluigi Paganini
August 28, 2018
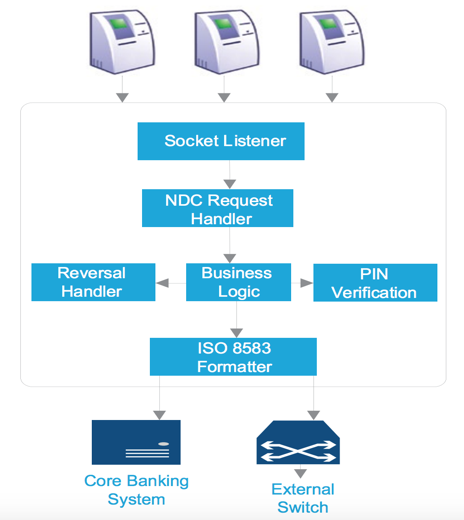
Security experts from Securonix have published a report that attributes the attack against on the Cosmos Bank to the Lazarus APT group. Cosmos Bank is one of the largest Indian cooperative banks, it was the victim of a cyberheist a couple of weeks ago when hackers stole over 940 million rupees ($13.5 million) in just three […]
 Pierluigi Paganini
August 24, 2018
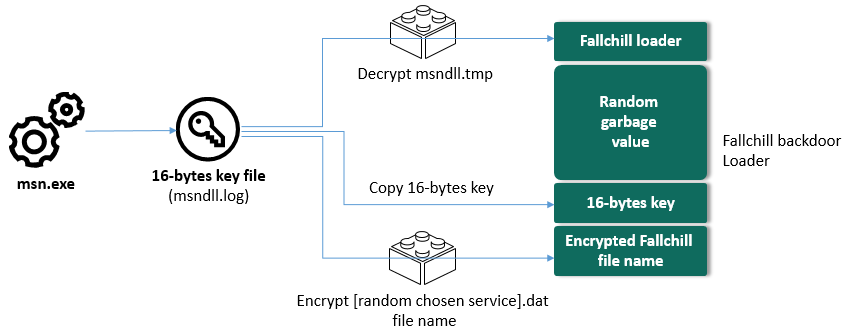
North Korea-linked Lazarus APT group leveraged for the first time on a MacOS variant of the Fallchill malware in a cryptocurrency exchange attack. According to Kaspersky, the North Korea-linked Lazarus group used a macOS malware to target a cryptocurrency exchange in a recent attack. The activity of the Lazarus Group surged in 2014 and 2015, […]
 Pierluigi Paganini
August 23, 2018
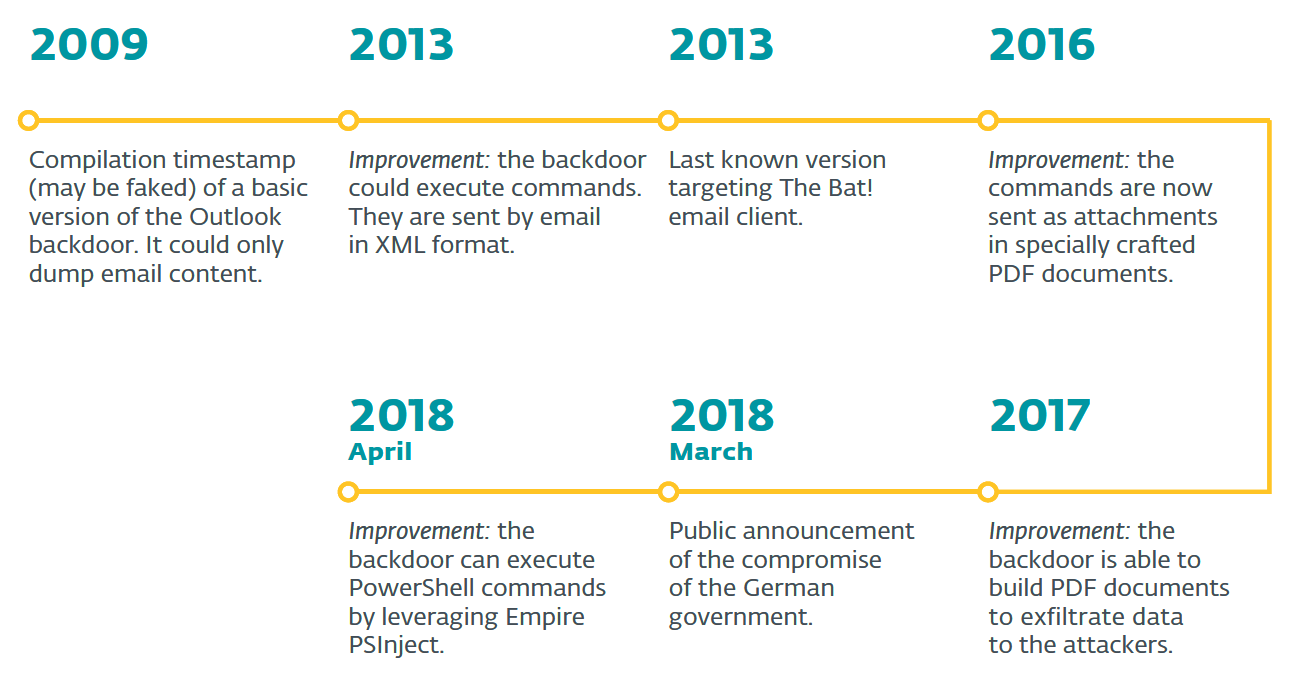
Malware researchers from ESET have published a detailed report on the latest variant of the Turla backdoor that leverages email PDF attachments as C&C. Malware researchers from ESET have conducted a new analysis of a backdoor used by the Russia-linked APT Turla in targeted espionage operations. The new analysis revealed a list of high-profile victims that was […]
Security / November 02, 2026