 Pierluigi Paganini
 June 02, 2016
The Analysis of SWIFT attacks revealed five additional pieces of malware containing portions of code shared by Lazarus Group. While security experts continue to investigate the cyber heists that involved SWIFT systems, new evidence collected by a senior security researcher from Anomali Labs link the malware to the North Korean hacker crew known as Lazarus Group. The expert discovered that five […]
 Pierluigi Paganini
May 28, 2016
PaloAlto Networks has spotted a new campaign conducted by the Wekby APT that leverages on a malware that uses DNS requests for C2 communications. Security experts at Palo Alto Networks have spotted a China-linked APT group that has been using a strain of malware that leverages DNS requests for command and control (C&C) communications. The group […]
 Pierluigi Paganini
May 19, 2016
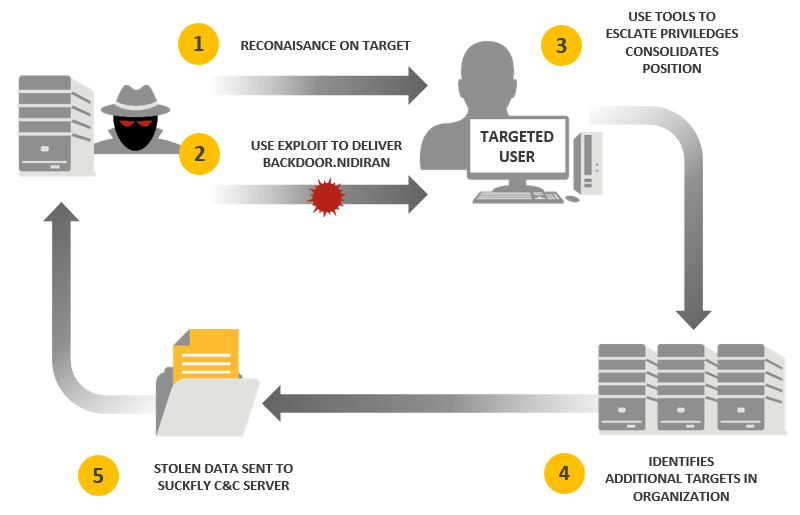
A crew of cyber spies named Suckfly group is targeting organizations in India, it conducted long-term espionage campaigns against entities in the country. A group of high professional hackers called Suckfly is targeting organizations in India, according to the experts at Symantec the crew conducted long-term espionage campaigns against the country. Symantec did not disclose the […]
 Pierluigi Paganini
April 28, 2016
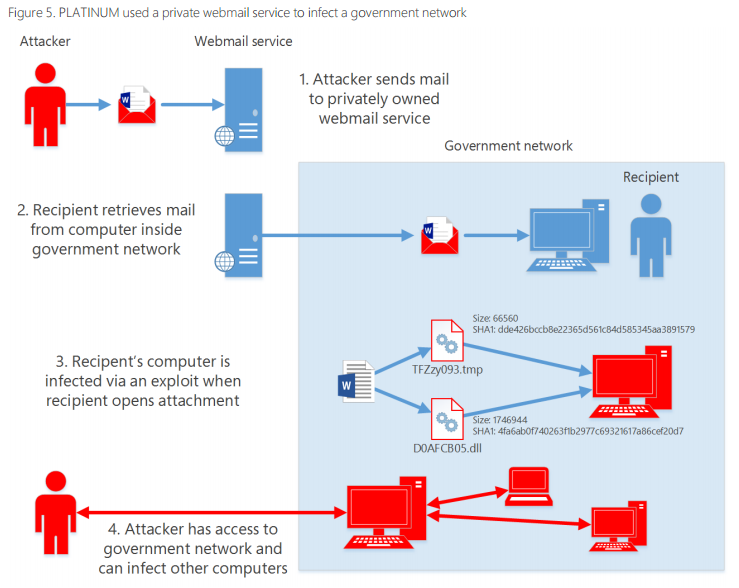
Microsoft issued a detailed report on the activity of the hacking crew dubbed Platinum APT group that leveraged a Windows patching system in its attacks. The hacker crew discovered by Microsoft and dubbed Platinum APT group conducted cyber espionage against organizations in South and Southeast Asia leveraging a Windows patching system. According to Microsoft, the Platinum has […]
 Pierluigi Paganini
April 19, 2016
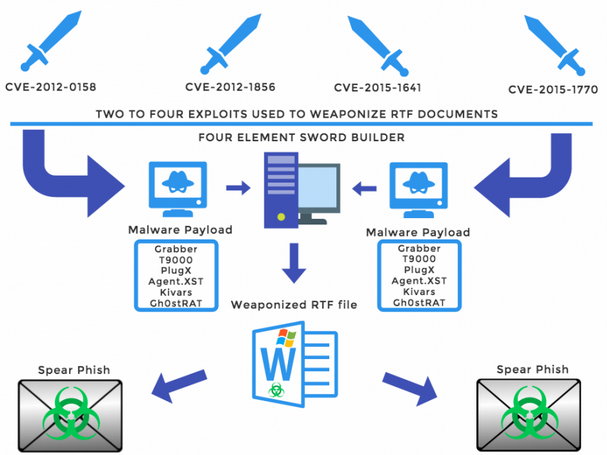
Experts analyzed a dozen attacks that leveraged on malicious RTF documents created using the same Four Element Sword builder. Security experts at Arbor Networks’ Security Engineering and Response Team (ASERT) have spotted a tool used in advanced persistent threat (APT) attacks against organizations in East Asia. The researchers have analyzed a dozen attacks that leveraged on malicious Rich […]
 Pierluigi Paganini
April 13, 2016
Swedish experts warned of an electronic warfare attack on its air traffic control systems occurred in November. Is it electronic warfare? Swedish experts suspect that the attack on its air traffic control systems last November was operated by Russian nation-state hackers, the Arlanda, Landvetter and Bromma airport reported the major problems. The Swedish experts believe the cyber attacks were […]
 Pierluigi Paganini
February 24, 2016
Japanese commercial and critical infrastructure organizations have been targeted a long-running campaign dubbed Operation Dust Storm. Security firm Cylance have uncovered a long-running hacking campaign dubbed ‘Operation Dust Storm’ targeting commercial and critical infrastructure organizations in Japan. Threat actors behind the Operation Dust Storm have been active since at least 2010, the hackers targeted several organizations in Japan, […]
 Pierluigi Paganini
February 18, 2016
In May 2015, the Chinese security firm Qihoo 360 published a report on a Trojan called OceanLotus that was being used since 2012 for APT attacks in the Chinese market. The APT attacks based on the OceanLotus focused on government organizations, research institutes, maritime agencies, and companies specializing in other activities. At the time were […]
 Pierluigi Paganini
February 17, 2016
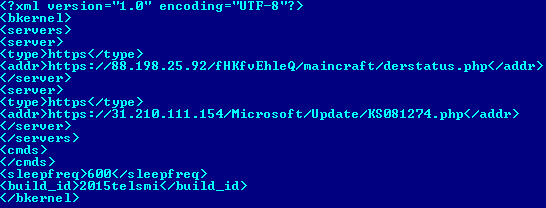
Malware researchers at PaloAlto discovered the Fysbis Trojan, a simple and an effective Linux threat used by the Russian cyberspy group Pawn Storm. Do you remember the Pawn Storm hacking crew? Security experts have identified this group of Russian hackers with several names, including APT28, Sofacy or Sednit, it has been active since at least 2007. The name Pawn Storm is used by security […]
 Pierluigi Paganini
February 13, 2016
Experts at Trend Micro discovered strains of BlackEnergy malware involved in the recent attacks against Ukrainian Mining and Railway Systems. BlackEnergy was in the headlines when the security industry examined the power outage occurred in Ukraine in December 2015. The BlackEnergy malware is a threat improved to target SCADA systems, the latest variant includes the KillDisk component developed to wipe […]
Malware / November 02, 2026
Security / November 02, 2026