 Pierluigi Paganini
 September 21, 2015
The 8th International Conference on Cyber Conflict (CyCon 2016) will be held in Tallinn, Estonia from 31st of May to 3th of June next year, what’s new? The 8th International Conference on Cyber Conflict (CyCon 2016) will be held in Tallinn, Estonia from 31st of May to 3th of June next year, in order to […]
 Pierluigi Paganini
September 21, 2015
The Egyptian security researcher Mohamed M. Fouad has spotted three critical vulnerabilities in the StarBucks website that open users to cyber attacks. If you are one of the millions StarBucks users don’t waste time and change your password as soon as possible. StarBucks users who have registered an account and linked their credit card to it […]
 Pierluigi Paganini
September 20, 2015
It seems incredible, but as already happened for Skype it is possible to crash the latest version of Google Chrome with a simple tiny URL. The flaw was discovered last week by the expert Andris Atteka who filed also a bug report. “Recently I reported a crash bug in Google Chrome (issue #533361). This issue reminded […]
 Pierluigi Paganini
September 19, 2015
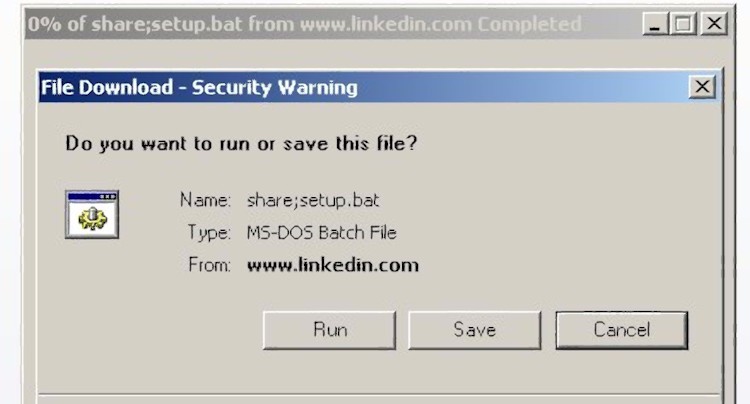
The Security researcher David Sopas at WebSegura discovered a Reflected Filename Download vulnerability in the popular professional social network LinkedIn. He was analyzing another website when he discovered the following XHR request on Google Inspector on LinkedIn: https://www.linkedin.com/countserv/count/share?url=http://www.site_i_was_in.pt It seems a simple request to make by websites to count how many shares their site have on […]
 Pierluigi Paganini
September 19, 2015
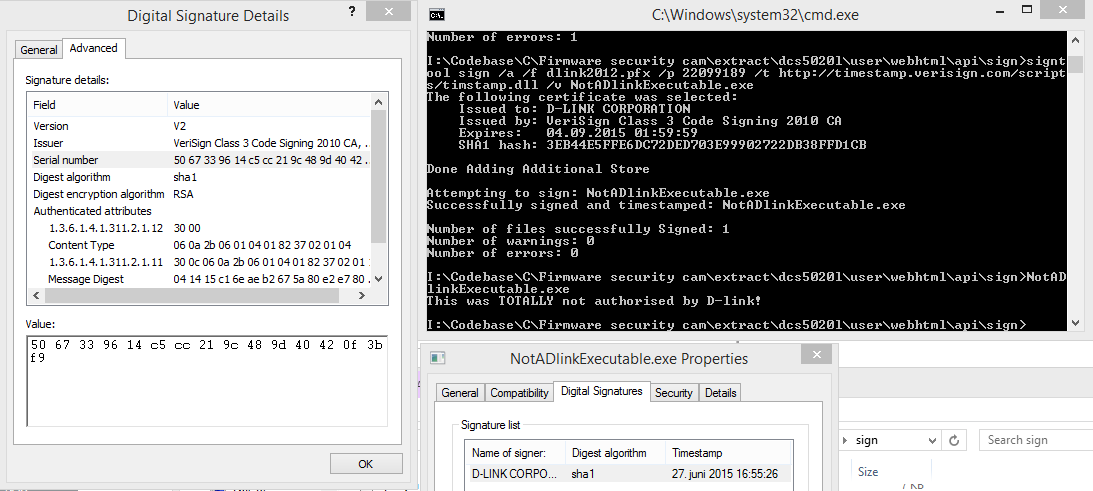
The Taiwanese networking equipment manufacturer D-Link has accidentally published its private code signing keys in the source of one of its firmware update. According to the Dutch news site Tweakers, the Taiwan-based networking equipment manufacturer D-Link accidently published its private code signing keys inside its open source firmware packages. One of the readers of the Dutch news […]
 Pierluigi Paganini
September 19, 2015
The popular group of hackers dubbed w0rm breached the hacking forum “Monopoly” offering for sale all data present in its database. This is the classic example of the lack of rules within underground communities, today we will speak about a group of hackers who targeted another group and is offering their data for sale at $500. […]
 Pierluigi Paganini
September 18, 2015
A Critical vulnerability affects Mozilla Bugzilla bug-tracking software could be exploited to access details of non-public vulnerabilities stored in its database. The open source Bugzilla bug-tracking system is used hundreds of thousands of software organizations that track the evolution of software bugs discovered in their applications. Development team urge to upgrade Bugzilla bug tracking system to fix the […]
 Pierluigi Paganini
September 18, 2015
Sucuri has noticed a spike in the number of compromised websites as part of a malware campaign which relies on thousands of compromised WordPress sites. According to security experts at Sucuri, threat actors have hijacked thousands of websites running the WordPress CMS to serve malware. The technique is not new, legitimate compromised websites host malicious […]
 Pierluigi Paganini
September 17, 2015
Experts at Trend Micro uncovered the Operation Iron Tiger, a cyber espionage campaign carried out by Chinese hackers on United States Defense Contractors. Security experts at Trend Micro have uncovered a new targeted attack campaign dubbed Operation Iron Tiger. Threat actors behind the Operation Iron Tiger have stolen trillions of data from defense contractors in […]
 Pierluigi Paganini
September 17, 2015
A new evil vulnerability affecting the AirDrop service could be exploited by attackers to silently infect iPhones and Apple Macs. Versions prior to the latest Apple OS version, the newborn iOS 9, are affected by a serious AirDrop Bug. The AirDrop Bug could be exploited by hackers to take full control of Apple iPhone or Mac machines. […]