


 Pierluigi Paganini
 October 29, 2015
Adobe has released a critical update to fix a flaw in the Shockwave player that could be exploited to compromise hundreds of millions of machines. Adobe has released a critical update to fix a vulnerability in the Shockwave player (CVE-2015-7649) that could be exploited by threat actors to compromise hundreds of millions of machines. The […]
 Pierluigi Paganini
October 28, 2015
Free Web Hosting 000Webhost company hacked, data belonging to more than 13 Million customers have been leaked online by the attackers. Another company has suffered a major data breach, this time in the headlines there is the world’s most popular Free Web Hosting company 000Webhost. The 000Webhost data breach has exposed more than 13.5 Million […]
 Pierluigi Paganini
October 28, 2015
Security experts at Sucuri reported a number of attacks exploiting a critical SQL injection flaw recently disclosed in the Joomla Content Management System. A few days ago, security experts disclosed a critical SQL injection vulnerability in the Joomla Content Management System (CVE-2015-7858), but as expected, threat actors in the wild are exploiting it in attacks against websites […]
 Pierluigi Paganini
October 27, 2015
A group of experts has conducted a research that demonstrates the type of data that can be gathered through the forensic study of WhatsApp. A new research conducted by forensic researchers at the University of New Haven (F. Karpisek of Brno University of Technology in the Czech Republic, and Ibrahim Baggili and Frank Breitinger, co-directors of the Cyber […]
 Pierluigi Paganini
October 26, 2015
The Google Project Zero hacker James Forshaw assessed Windows 10 analyzing the big risks related with the new OS from Microsoft. James Forshaw, a member of the Google Project Zero hacking crew, was given the task to asses Windows 10, and see if there were big risks related with the new OS from Microsoft. Forshaw talked […]
 Pierluigi Paganini
October 24, 2015
How much cost a zero-day for an industrial control system? Where is to possible to buy them and who are the main buyers of these commodities? We have discussed several times about the importance of zero-day in cyber attacks against computer systems, the exploitation of previously unknown vulnerabilities is a prerogative of well-funded hacking groups such as state-sponsored crews. […]
 Pierluigi Paganini
October 24, 2015
Now that it is known a critical flaw in the Diffie-Hellman key-exchange protocol was exploited by the NSA to break the internet encryption, how to stop it? Recently a group of researchers has revealed how the NSA has cracked HTTPS, SSH, and VPNs rely on the Diffie-Hellman encryption by exploiting a wrong implementation of the cryptographic algorithm. The […]
 Pierluigi Paganini
October 23, 2015
Imperva has discovered that attackers hijack CCTV cameras to launch powerful DDoS attacks exploiting weak credentials and poor configurations of IoT devices. Internet of Things devices are becoming privilege targets of threat actors that daily abuse of their resources to run cyber attacks or to organize frauds or to spy on unaware users. Unfortunately, most IoT devices […]
 Pierluigi Paganini
October 22, 2015
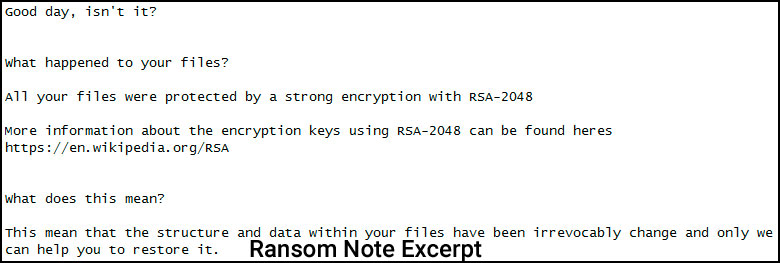
Experts at Bleeping Computer blog are reporting a new strain of ransomware dubbed LowLevel04 that is spreading via Remote Desktop and Terminal Service. Security experts at Bleeping Computer blog are reporting a new strain of ransomware dubbed LowLevel04 that is using an unusual infection mechanism, it is being spread via Remote Desktop and Terminal Service. […]
 Pierluigi Paganini
October 21, 2015
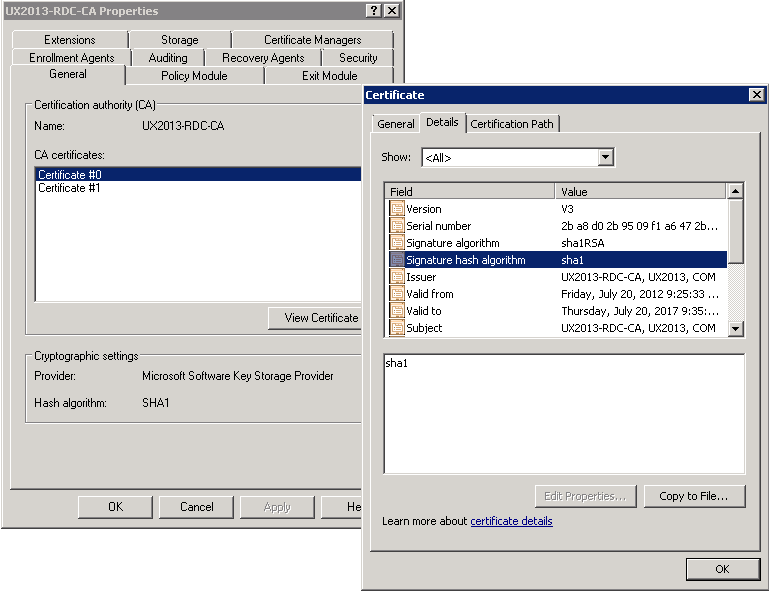
Experts at Netcraft discovered that nearly a million SSL SHA-1 certificates were signed with the potentially vulnerable SHA-1 hashing algorithm. Businesses Using Millions of Flawed Certificates, the news is shocking and refers the adoption of SHA-1 certificates, despite the algorithm is considered no more secure. Many big businesses, including firms like Deloitte, are still using SHA-1 certificates, […]
Data Breach / November 17, 2026
Malware / November 17, 2026


