


 Pierluigi Paganini
 October 16, 2015
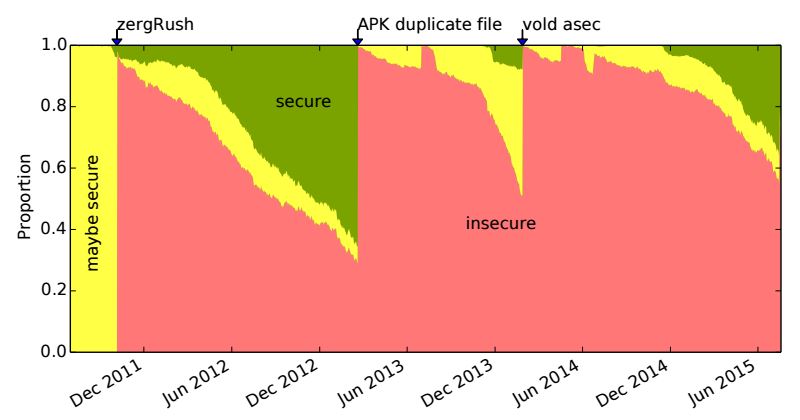
Researchers probed 20,400 Android devices and found 87.7 per cent contained at least one exploitable vulnerability due to a slow patch management. New Android vulnerabilities are discovered every day, but it looks like that, some Android vendors are very slow in applying the necessary patch to fix the security issues. Some Android vendors are only […]
 Pierluigi Paganini
October 15, 2015
5 Guidelines in Battling Cyber Criminals Over Precious Business Data, lets’s try to understand how to Ensure Enterprise Security. You would think that a company that stores their clients’ money and handles investments would have tight security measures on their system against cyber attacks. Apparently, this is not always the case. In 2014, Scottrade, a […]
 Pierluigi Paganini
October 14, 2015
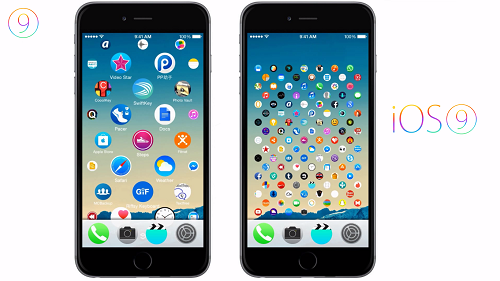
The Chinese jailbreaking team Pangu has just released a software (iOS 9 jailbreak) that allows Apple users to jailbreak their mobile devices using iOS 9. Every time a new release of the popular Apple iOS is presented, hackers and experts start the competition to jailbreak it. One of the most active hacking crew in this […]
 Pierluigi Paganini
October 14, 2015
FireEye has uncovered a new hacking group dubbed FIN5 hacked payment systems of an un-named Casino and it has stolen nearly 150,000 credit cards. The fact that the game can create problems is not a novelty, news of the day is that an un-named Casino has lost 150,000 credit cards. The cause of the data […]
 Pierluigi Paganini
October 14, 2015
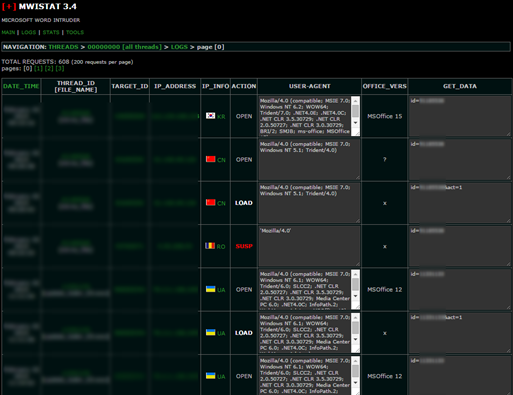
Check Point discovered a series of malware-based attacks on Israeli public sector organizations that were infected by the Zeus Trojan via RTF files. Security experts at Check Point have detected a series of attacks on high-profile companies, victims were targeted by a malicious spam campaign that relies on bogus RTF file. The campaign targeted several individuals […]
 Pierluigi Paganini
October 13, 2015
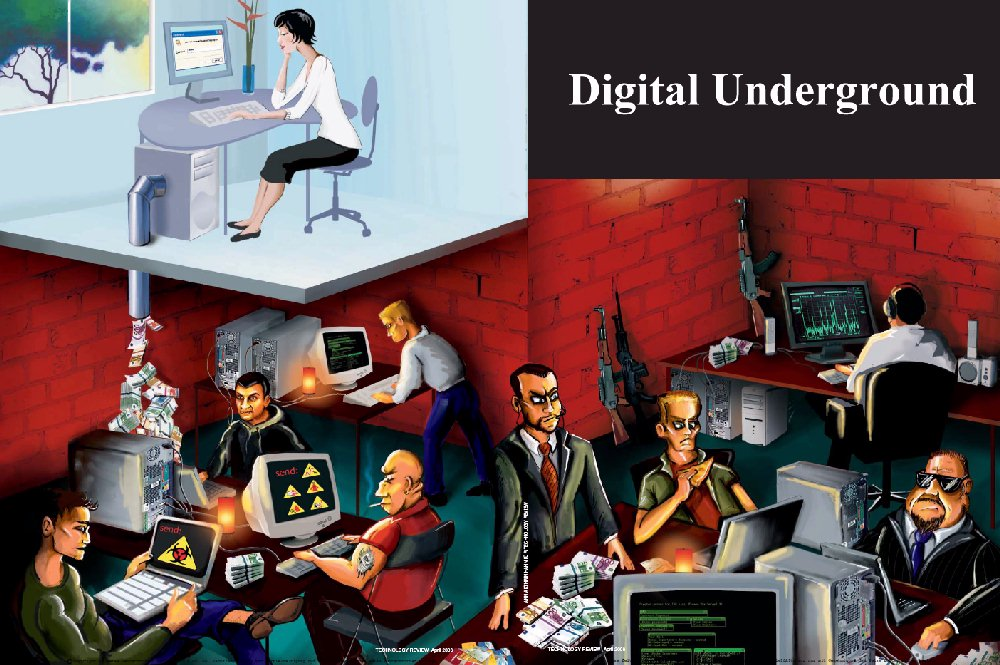
Researchers at Trend Micro have issued a new report on the Japanese Cybercrime Underground, a growing criminal community with his characteristics. Cybercrime underground is a growing and prolific industry that knows no crisis as demonstrated by the numerous reports issued by principal security companies and law enforcement. In the past we have analyzed criminal most […]
 Pierluigi Paganini
October 12, 2015
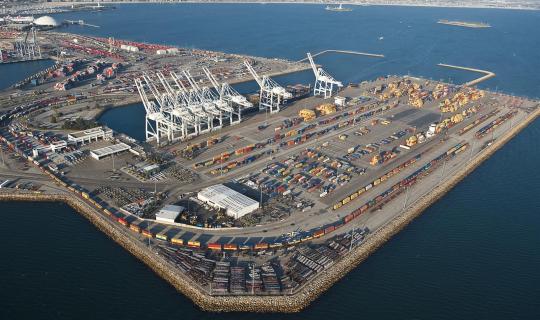
US Ports are still vulnerable to cyber attacks that release dangerous chemicals, cybersecurity in the maritime industry is crucial for Homeland security. Critical infrastructure across the world are vulnerable to cyber attacks, this is not novelty, but it is interesting to explore how many infrastructure is open to hacking assaults. US ports are also vulnerable to cyber […]
 Pierluigi Paganini
October 12, 2015
Apple has removed mobile apps from the iOS Apple store that are installing root CA certificates that enable traffic to be intercepted. Apple has pulled several apps out from the official iOS App Store over SSL/TLS security concerns, this means that the security issues could allow threat actors to compromise encrypted connections between the servers […]
 Pierluigi Paganini
October 11, 2015
For the first time, hackers have been arrested in China by law enforcement at the behest of the US government. Is it true cooperation? It is probably the first time that Chinese authorities have arrested hackers in China following a request of the US Government. Two weeks, before the visit of the Chinese President Xi Jinping in the […]
 Pierluigi Paganini
October 10, 2015
Security experts at Sucuri have uncovered threat actors abusing an XML-RPC method to run Brute-Force amplification attacks on WordPress websites. According to the experts at security firm Sucuri, threat actors are exploiting the XML-RPC protocol implemented by WordPress and other popular content management systems to run brute-force amplification attacks. The XML-RPC protocol allows users to […]
Data Breach / November 17, 2026
Malware / November 17, 2026


