 Pierluigi Paganini
 September 09, 2015
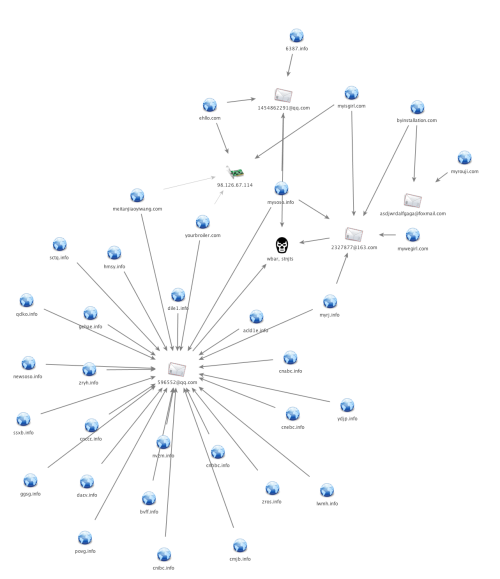
Security experts at Paloalto Networks have uncovered a multiyear espionage campaign dubbed Musical Chairs Involving New Variant of Gh0st RAT Malware. The Gh0st RAT malware is a popular remote administration tool (RAT) created in China in the early 2000s that was used in a number of cyber espionage operations. Targeted espionage operations on Tibetan activists, including the Operation Night Dragon and the GhostNet attacks, […]
 Pierluigi Paganini
September 09, 2015
A number of recent discoveries suggest as more HTTPs websites, chat applicationss, and other services online are actualizing perfect forward secrecy. As per a Red Hat (a Linux distributor) security specialist, system equipment sold by few makers neglected to appropriately execute a broadly utilized cryptographic standard, an information releasing weakness that can permit spammers to […]
 Pierluigi Paganini
September 08, 2015
Security experts at Check Point security discovered a flaw in WhatsApp Web that could be exploited by attackers to compromise hundreds of millions users, According to the security firm Check Point a vulnerability in the popular messaging service WhatsApp Web exposes up to 200 million of its users at risk of cyber attack. WhatsApp Web allows […]
 Pierluigi Paganini
September 08, 2015
Heimdal Security published an interesting post on the increase in malicious scripts that are being injected into legit websites in order to serve ransomware. Heimdal Security recently published an interesting blog post on the increase in malicious scripts that are being injected into legit websites in order to serve malware. The attackers compromise websites running […]
 Pierluigi Paganini
September 07, 2015
Security experts at Vulnerability Lab have discovered a restriction filter bypass vulnerability affecting the PayPal mobile app. Under specific conditions, PayPal can ask users to confirm their identity to prevent frauds. When users are asked to verify their identity, their account is not accessible and in order to unblock it PayPal request them to make […]
 Pierluigi Paganini
September 07, 2015
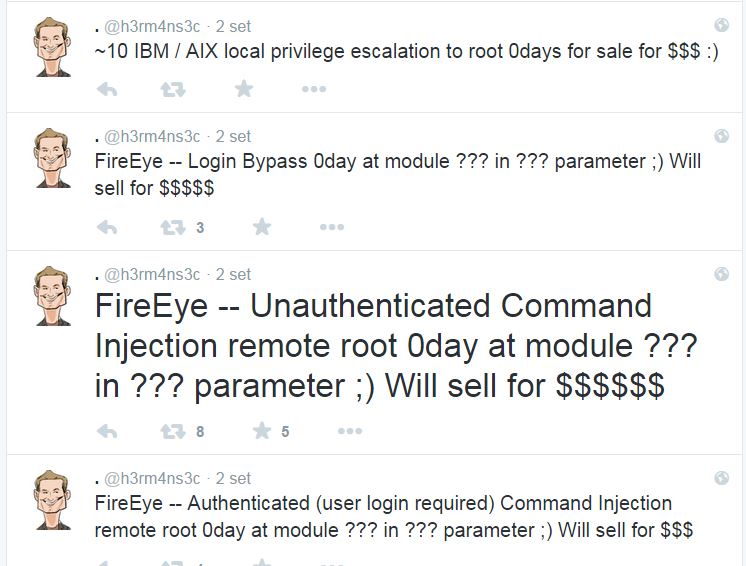
The expert Kristian Erik Hermansen disclosed a zero-day flaw in the FireEye core appliance that could be exploited to gain remote root file system access. Yesterday security researcher Kristian Erik Hermansen disclosed a zero-day vulnerability in the FireEye core appliance that could be exploited to gain remote root file system access. Hermansen told to CSOonline that he […]
 Pierluigi Paganini
September 07, 2015
The CERT_org issued an alert on Seagate wireless disks because they contain multiple flaws that could be exploited to download their entire content. CERT.org issued a warning related Seagate wireless disk because they include a hidden login, most exactly a Telnet services that is not documented. This security issue allows anonymous attackers to download every file on […]
 Pierluigi Paganini
September 07, 2015
Fiat Chrysler has recalled nearly 8,000 Jeep Renegade SUVs in the US to update the software that could be exploited by attackers to hack the vehicles. No peace for Fiat Chrysler Automobiles after the disclosure of the attack against its Jeep Cherokee model made by the popular hackers Charlie Miller and Chris Valasek. The duo of […]
 Pierluigi Paganini
September 06, 2015
The CSIS Security Group has spotted a new version of the notorious Carbanak Trojan in the wild targeting financial organizations in Europe and US. Do you remember the Carbanak gang? In February, researchers from Kaspersky discovered that a multinational gang of hackers dubbed Carbanak that swiped 1 Billion dollars from 100 financial institutions across 30 countries, most of the […]
 Pierluigi Paganini
September 06, 2015
The decision of Fiat Chrysler for providing a software update via Mailed USB is considered disconcerting for the security industry. Do you remember the hack of the Fiat Chrysler Jeep? In response to the disclosure of the details of the successful attack, the company recalled nearly 1.4 vehicles in the US in order to update the firmware running […]

Data Breach / November 17, 2026