 Pierluigi Paganini
 November 16, 2013
Researcher Dan Melamed recently discovered an open url redirection flaw in Facebook that allowed to have a facebook.com link redirect to any website. A Facebook Open URL Redirection vulnerability is the last discovery of security expert Dan Melamed that reported it in a recent post. Dan is an old acquaintance of Security Affairs, he revealed […]
 Pierluigi Paganini
November 15, 2013
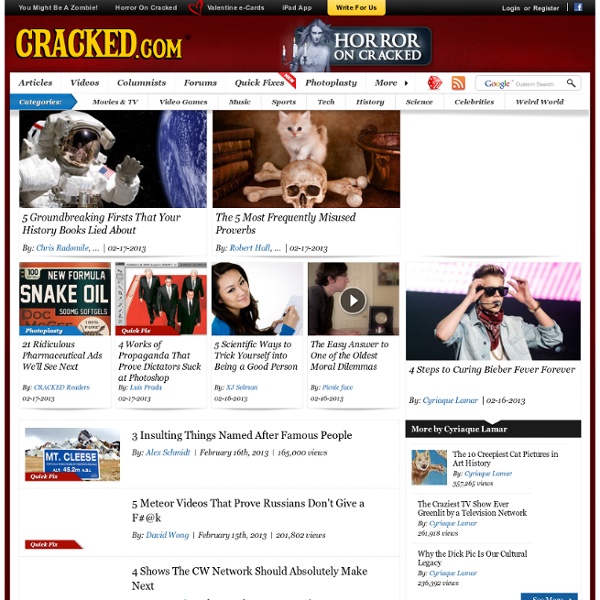
Barracuda Labs researches discovered that the popular humor website Cracked_com was compromised used by attackers to serve malware. Cracked_com, the popular humor website, was compromised and used to serve malware that infected its visitors during the weekend and according to Barracuda Labs research the alarm could be not considered closed. The attackers used the classic […]
 Pierluigi Paganini
November 15, 2013
At last HP’s Pwn2Own 2013 contest hacking teams from Japan and China compromised iPhone 5 running iOS 6 and iOS 7 and a Samsung Galaxy S4. During the last HP’s Pwn2Own 2013 contest at Information Security Conference PacSec 2013 in Tokyo, two teams of Chinese and Japanese hackers demonstrated the exploitation of zero-day vulnerability in Apple’s Safari browser for […]
 Pierluigi Paganini
November 14, 2013
Happy Birthday Security Affairs Two years ago I started Security Affairs for joke motivated by my passion in the security, day after day it is growing thanks to your affection and your precious support. I wish you were all here to hug you and have a coffee together, the Italians love coffee 😉 … Maybe […]
 Pierluigi Paganini
November 14, 2013
Security researcher Dancho Danchev profiled a new commercially modular malware platform recently released on the underground marketplace. A new commercially modular malware platform has been released on the underground marketplace, the news is posted by the security expert Dancho Danchev. Danchev recently observed a new modular malware platform specifically designed to provide a series of powerful features […]
 Pierluigi Paganini
November 13, 2013
MacRumors, the Mac news and information website and user forums, was hacked, more than 860,000 accounts were potentially compromised. MacRumors, the popular Mac news and information website and user forums have been hacked this week, according the first news circulating on the internet more than 860,000 accounts were potentially compromised on the total of 1.8 million registered […]
 Pierluigi Paganini
November 13, 2013
TrendLabs has just published the third quarterly report, titled The Invisible Web Unmasked, on the evolution of cybercrime observed in recent months. TrendLabs have published an interesting report titled titled “The Invisible Web Unmasked” to provide a picture of cybercrime evolution observed in recent months. The takedown of the virtual currency Liberty Reserve, the seizure […]
 Pierluigi Paganini
November 12, 2013
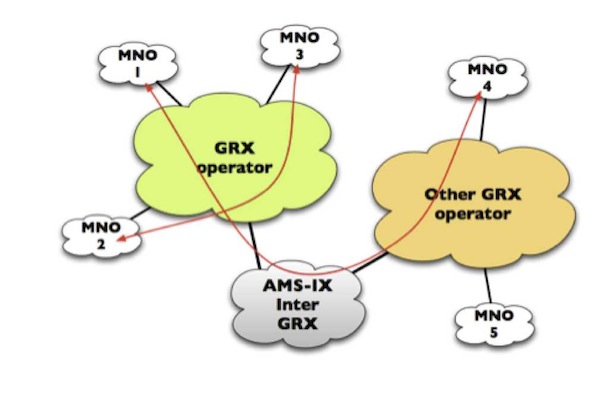
The GCHQ (British Government Communications Headquarters) used fake LinkedIn and Slashdot to hack Belgacom, OPEC & others GRX providers. According to the German weekly news magazine Der Spiegel the British signals intelligence spy agency has again adopted a “quantum insert” technique to target employees of two companies that are GRX (Global Roaming Exchange) providers. The […]
 Pierluigi Paganini
November 11, 2013
The clients of the Brazilian financial institutions have been hit by a banking trojan embedded in RTF file and spread through a spam campaign. The banking is one of the most targeted sector by cybercrime that exploit always new vector to infect a customer’s machine of the clients of banks. I decided to write this […]
 Pierluigi Paganini
November 11, 2013
FireEye Labs has identified a new IE zero-day exploit used for a watering hole attack in the US. As usual it is crucial to track and mitigate so dangerous threats in time to avoid serious problems. FireEye Labs has detected a new series of attacks based on the exploit of a new IE zero-day vulnerability […]