 Pierluigi Paganini
 October 12, 2022
Aruba addressed multiple critical severity vulnerabilities in the EdgeConnect Enterprise Orchestrator. Aruba addressed multiple critical severity vulnerabilities in the EdgeConnect Enterprise Orchestrator that can be exploited by remote attackers to compromise the vulnerable host. Aruba EdgeConnect Orchestrator is a centralized SD-WAN management solution that allows enterprises to control their WAN. Below are the vulnerabilities addressed […]
 Pierluigi Paganini
October 11, 2022
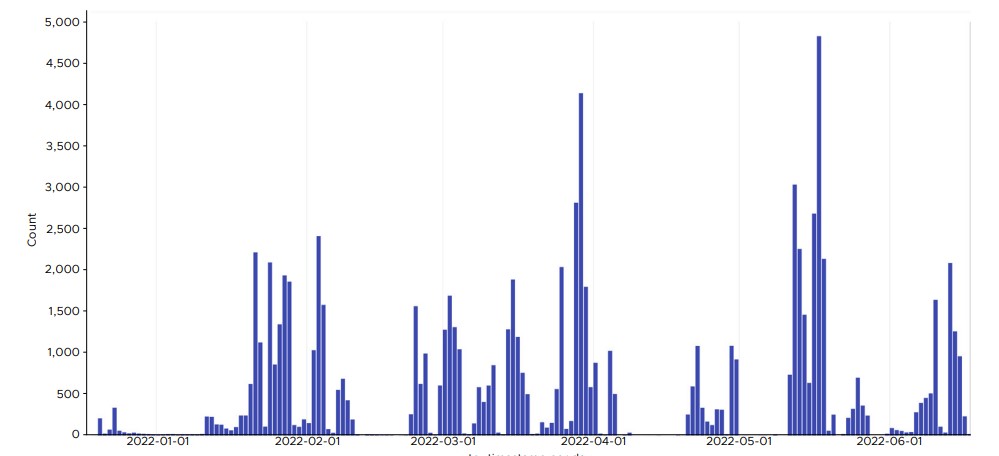
Threat actors behind the Emotet bot are continually improving their tactics, techniques, and procedures to avoid detection. VMware researchers have analyzed the supply chain behind the Emotet malware reporting that its operators are continually shifting their tactics, techniques, and procedures to avoid detection. The Emotet banking trojan has been active at least since 2014, the botnet is operated by […]
 Pierluigi Paganini
October 11, 2022
Toyota Motor Corporation discloses data leak, customers’ personal information may have been exposed after an access key was exposed on GitHub. Toyota Motor Corporation warns customers that their personal information may have been accidentally exposed after an access key was publicly available on GitHub for almost five years. The carmaker discovered recently that a portion […]
 Pierluigi Paganini
October 10, 2022
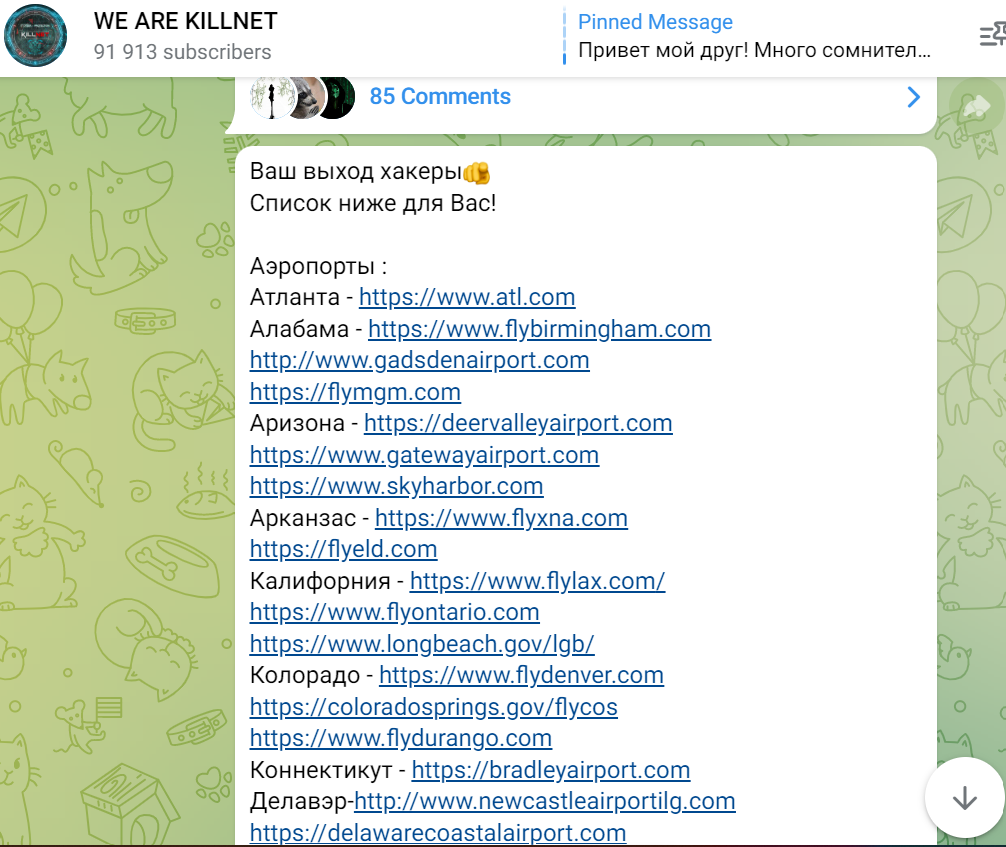
The pro-Russia hacktivist group ‘KillNet’ is behind massive DDoS attacks that hit websites of several major airports in the US. The pro-Russia hacktivist group ‘KillNet‘ is claiming responsibility for massive distributed denial-of-service (DDoS) attacks against the websites of several major airports in the US. The DDoS attacks have taken the websites offline, users were not […]
 Pierluigi Paganini
October 10, 2022
Threat actors got to a database with over 152,000 customer records before its owner, the Turkish branch of Harvard Business Review, closed it. Crooks left a ransom note, threatening to leak the data and inform authorities of the EU’s General Data Protection Regulation (GDPR) violations. Original Post published on CyberNews A recent discovery by the […]
 Pierluigi Paganini
October 09, 2022
Everest ransomware operators claimed to have hacked South Africa state-owned company ESKOM Hld SOC Ltd. In March 2022, the Everest ransomware operators published a notice announcing the sale of “South Africa Electricity company’s root access” for $125,000. Eskom transforms inputs from the natural environment – coal, nuclear, fuel, diesel, water, and wind – into more […]
 Pierluigi Paganini
October 09, 2022
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. If you want to also receive for free the newsletter with the international press subscribe here. BlackByte Ransomware abuses vulnerable driver to bypass security solutions Unpatched remote code execution flaw in Zimbra […]
 Pierluigi Paganini
October 08, 2022
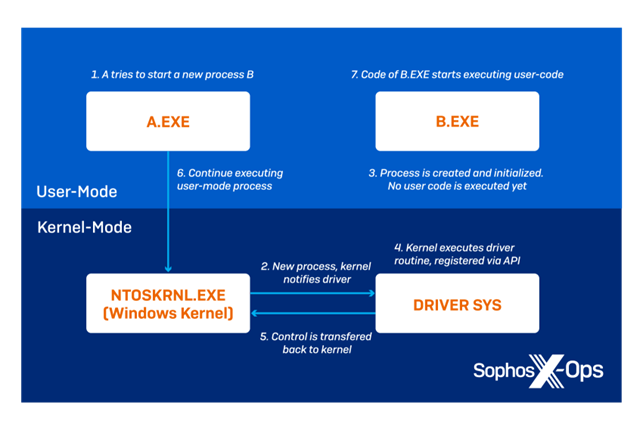
The BlackByte ransomware operators are leveraging a flaw in a legitimate Windows driver to bypass security solutions. Researchers from Sophos warn that BlackByte ransomware operators are using a bring your own vulnerable driver (BYOVD) attack to bypass security products. In BYOVD attacks, threat actors abuse vulnerabilities in legitimate, signed drivers, on which security products rely, […]
 Pierluigi Paganini
October 08, 2022
Threat actors are exploiting an unpatched severe remote code execution flaw (CVE-2022-41352) in the Zimbra collaboration platform. Researchers from Rapid7 are warning of the exploitation of unpatched zero-day remote code execution vulnerability, tracked as CVE-2022-41352, in the Zimbra Collaboration Suite. Rapid7 has published technical details, including a proof-of-concept (PoC) code and indicators of compromise (IoCs) […]
 Pierluigi Paganini
October 07, 2022
Fortinet addressed a critical authentication bypass vulnerability that impacted FortiGate firewalls and FortiProxy web proxies. Fortinet addressed a critical authentication bypass flaw, tracked as CVE-2022-40684, that impacted FortiGate firewalls and FortiProxy web proxies. An attacker can exploit the vulnerability to log into vulnerable devices. “An authentication bypass using an alternate path or channel [CWE-88] in […]