 Pierluigi Paganini
 June 09, 2019
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Kindle Edition Paper Copy Once again thank you! ESET analyzes Turla APTs usage of weaponized PowerShell Leicester City Football Club disclosed a card breach ProtonMail denies that it spies on users for government agencies Expert shows how […]
 Pierluigi Paganini
June 09, 2019
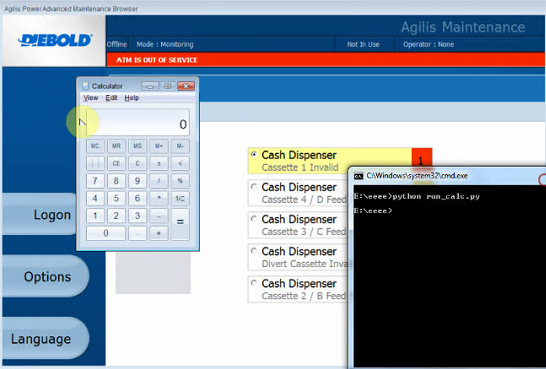
Automated teller machine vendor Diebold Nixdorf has released security updates to address a remote code execution vulnerability in older ATMs. Diebold Nixdorf discovered a remote code execution vulnerability in older ATMs and is urging its customers in installing security updates it has released to address the flaw. The vulnerability affects older Opteva model ATMs, Diebold Nixdorf […]
 Pierluigi Paganini
June 08, 2019
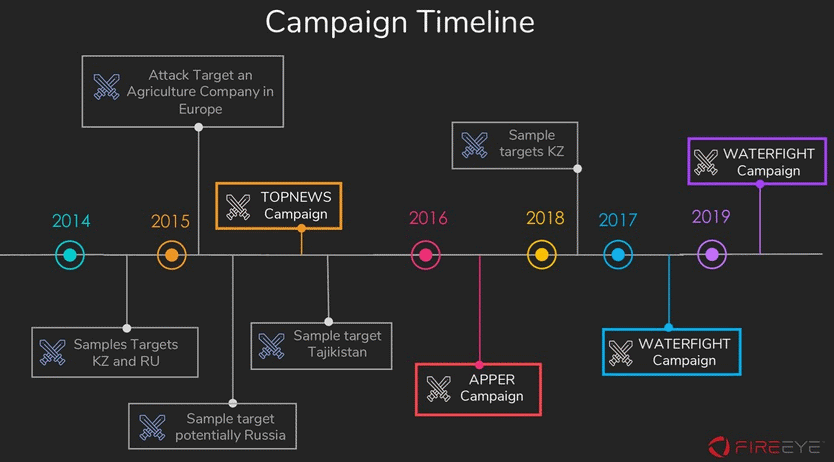
A security researcher found new evidence of activities conducted by the ICEFOG APT group, also tracked by the experts as Fucobha. Chi-en (Ashley) Shen, a senior security researcher at FireEye, collected evidence that demonstrates that China-linked APT group ICEFOG (aka Fucobha) is still active. The activities of the APT group were first uncovered by Kaspersky […]
 Pierluigi Paganini
June 08, 2019
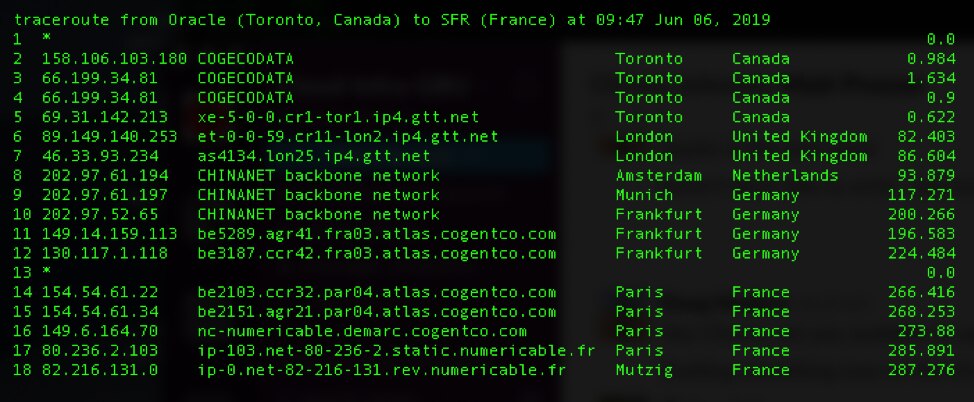
On June 6, for more than two hours China Telecom re-routed through its infrastructure a large chunk of European mobile traffic. In November security researchers Chris C. Demchak and Yuval Shavitt published a paper that detailed how China Telecom has been misdirecting Internet traffic through China over the past years. The experts speculate that they were […]
 Pierluigi Paganini
June 08, 2019
Cisco Talos experts uncovered a new wave of attacks tracked as Frankenstein campaign, attackers used tools built by combining four open-source techniques. Security experts at Cisco Talos uncovered a series of highly targeted attacks, tracked as Frankenstein campaign, hackers used tools built by combining four different open-source techniques. Attackers behind the Frankenstein campaign carried out […]
 Pierluigi Paganini
June 07, 2019
SandboxEscaper publicly disclosed a second Windows zero-day exploit dubbed ByeBear to bypass a recently patched elevation of privilege issue. SandboxEscaper is a well of neverending surprises, today publicly disclosed a second Windows zero-day exploit (dubbed ByeBear) to bypass a recently patched elevation of privilege issue. SandboxEscaper is well-known researchers that publicly disclosed several zero-day exploits […]
 Pierluigi Paganini
June 07, 2019
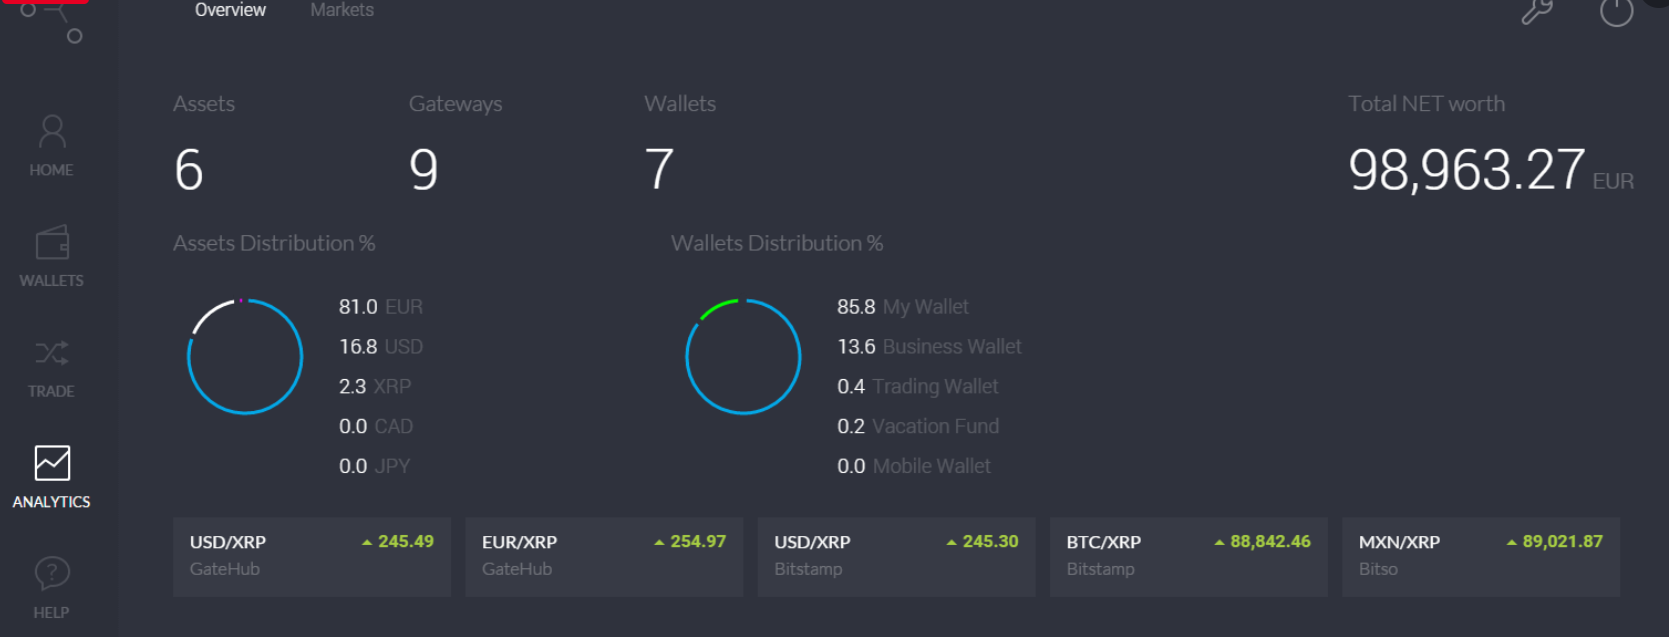
Cyber criminals stole 3.2 million Ripple coins (XRP), worth nearly $10 million, from the users of the GateHub cryptocurrency wallet service. A new cyber heist made the headlines, crooks stole 3.2 million Ripple coins (XRP), worth nearly $10 million, from the users of the GateHub cryptocurrency wallet service. “Recently, we have been notified by our […]
 Pierluigi Paganini
June 07, 2019
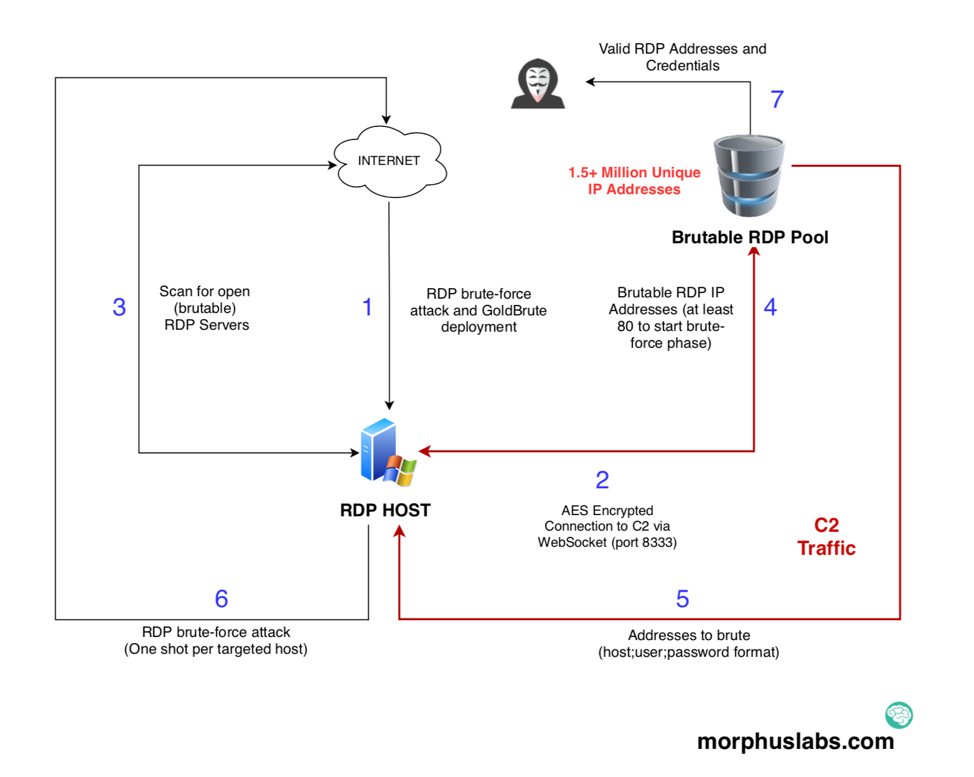
A new botnet tracked as GoldBrute is scanning the web for Windows machines with Remote Desktop Protocol (RDP) connection enabled. A new botnet tracked as GoldBrute has appeared in the threat landscape, it is scanning the web for Windows machines with Remote Desktop Protocol (RDP) connection enabled. The botnet is currently targeting over 1.5 million […]
 Pierluigi Paganini
June 07, 2019
The Cryptocurrency startup Komodo hacked itself to protect the funds of its users and avoid that hackers steal them exploiting a flaw in its Agama wallet. The story I’m going to tell you is amazing, the Cryptocurrency startup Komodo hacked itself after discovered a backdoor in its Agama wallet. Komodo’s Agama Wallet allows users to […]
 Pierluigi Paganini
June 06, 2019
VMware has informed its users that it has patched two high-severity vulnerabilities that affect its Tools and Workstation software. VMware has patched two high-severity flaws that affect its Tools and Workstation software. The first security flaw, tracked as CVE-2019-5522, affects VMware Tools 10.x on Windows. The vulnerability is an out-of-bounds read issue in the vm3dmp driver in […]
Uncategorized / September 21, 2026

Security / September 20, 2026