 Pierluigi Paganini
 October 21, 2021
Threat actors are continually looking for better ways to target organizations, here are the top five attack vectors to look out for in 2022. Malicious actors are continually looking for better ways to carry out successful cyber attacks. Whether motivated by a potential payday or the ability to access confidential information, cybercriminals have plenty of […]
 Pierluigi Paganini
October 20, 2021
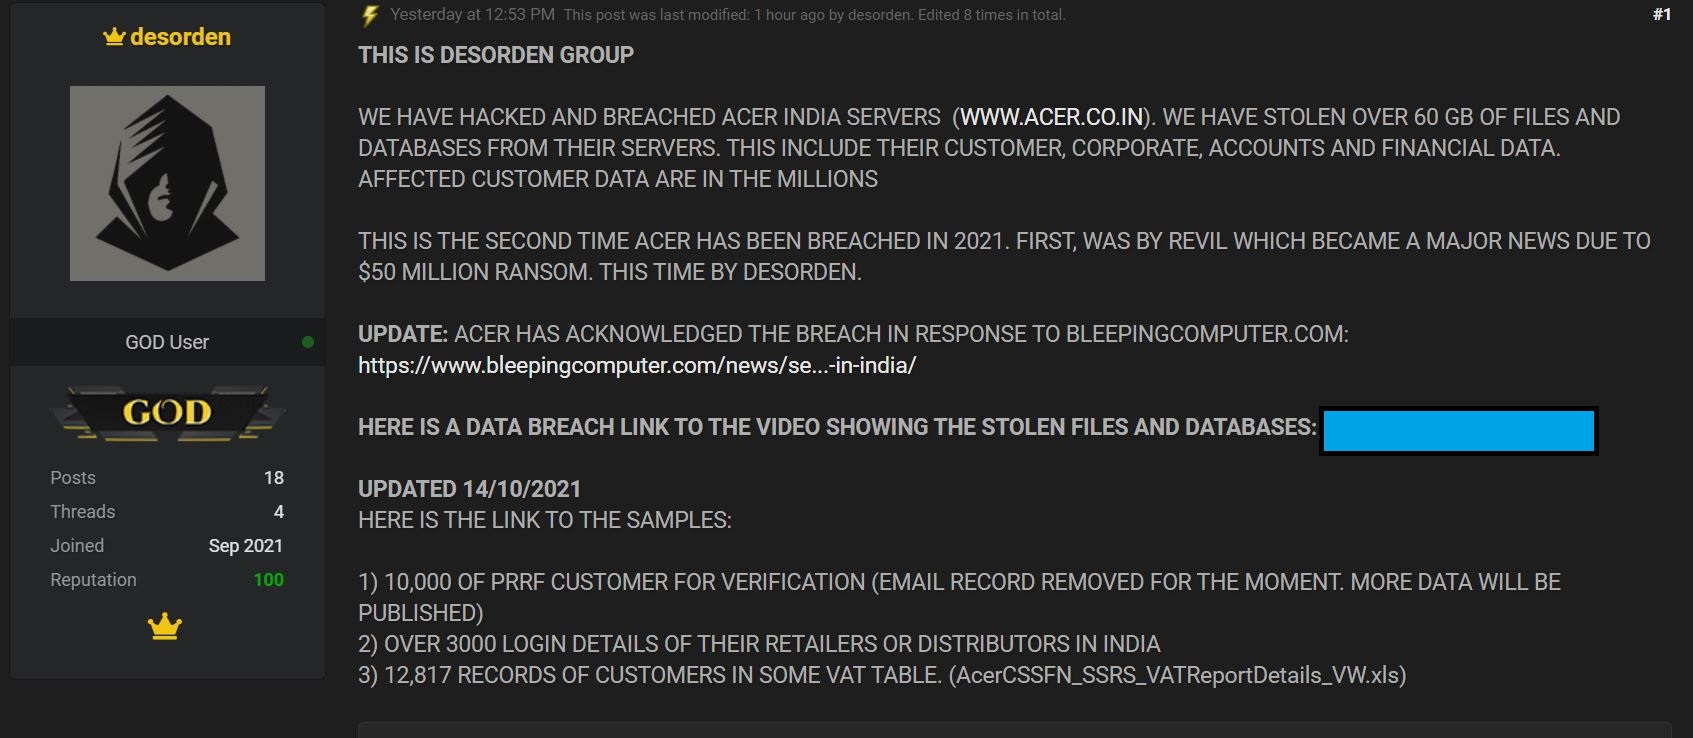
Tech giant Acer was hacked again in a few days, after the compromise of the servers in India, threat actors also breached some of its systems in Taiwan. Tech giant Acer was hacked twice in a week, the same threat actor (Desorden) initially breached some of its servers in India, now it is claiming to […]
 Pierluigi Paganini
October 20, 2021
China-linked cyberespionage group LightBasin hacked mobile telephone networks around the world and used specialized tools to access calling records. A China-linked hacking group, tracked as LightBasin (aka UNC1945), hacked mobile telephone networks around the globe and used specialized tools to access calling records and text messages from telecommunications companies. The cyberespionage group has been active […]
 Pierluigi Paganini
October 20, 2021
Zero-day exploit broker Zerodium announced it is looking for zero-day vulnerabilities in the Windows clients of ExpressVPN, NordVPN, and Surfshark. Zerodium is looking to pay for zero-day exploits for vulnerabilities in the Windows clients of three virtual private network (VPN) service providers, ExpressVPN, NordVPN, and Surfshark. The company announced with a message posted on Twitter: […]
 Pierluigi Paganini
October 19, 2021
FBI, CISA, NSA have published a joint advisory about the operation of the BlackMatter ransomware gang and provides defense recommendations. The Cybersecurity and Infrastructure Security Agency (CISA), the Federal Bureau of Investigation (FBI), and the National Security Agency (NSA) have published an advisory that provides details about the BlackMatter ransomware operations and defense recommendations. This advisory provides […]
 Pierluigi Paganini
October 18, 2021
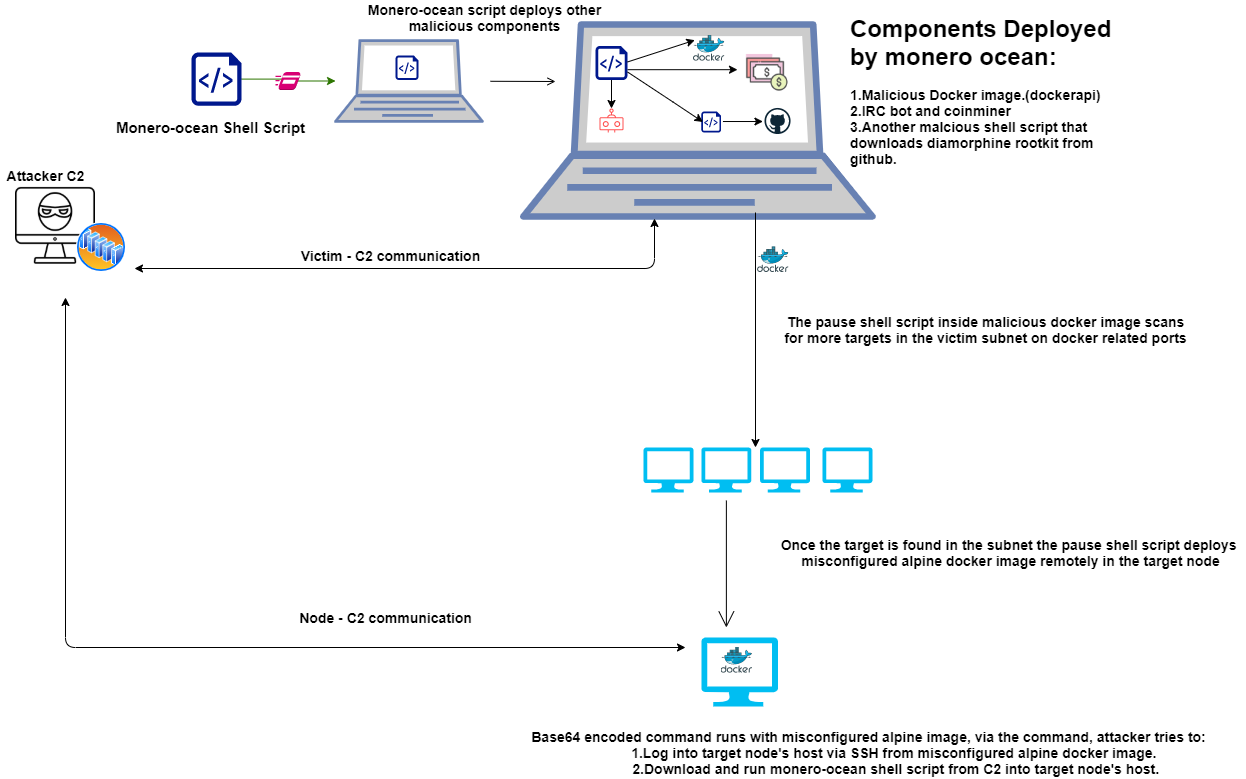
The Uptycs Threat Research Team spotted a campaign in which the TeamTNT threat actors deployed a malicious container image on Docker hub. The Uptycs Threat Research Team recently identified a campaign in which the TeamTNT threat actors deployed a malicious container image (hosted on Docker Hub) with an embedded script to download Zgrab scanner and masscanner—penetration testing tools […]
 Pierluigi Paganini
October 18, 2021
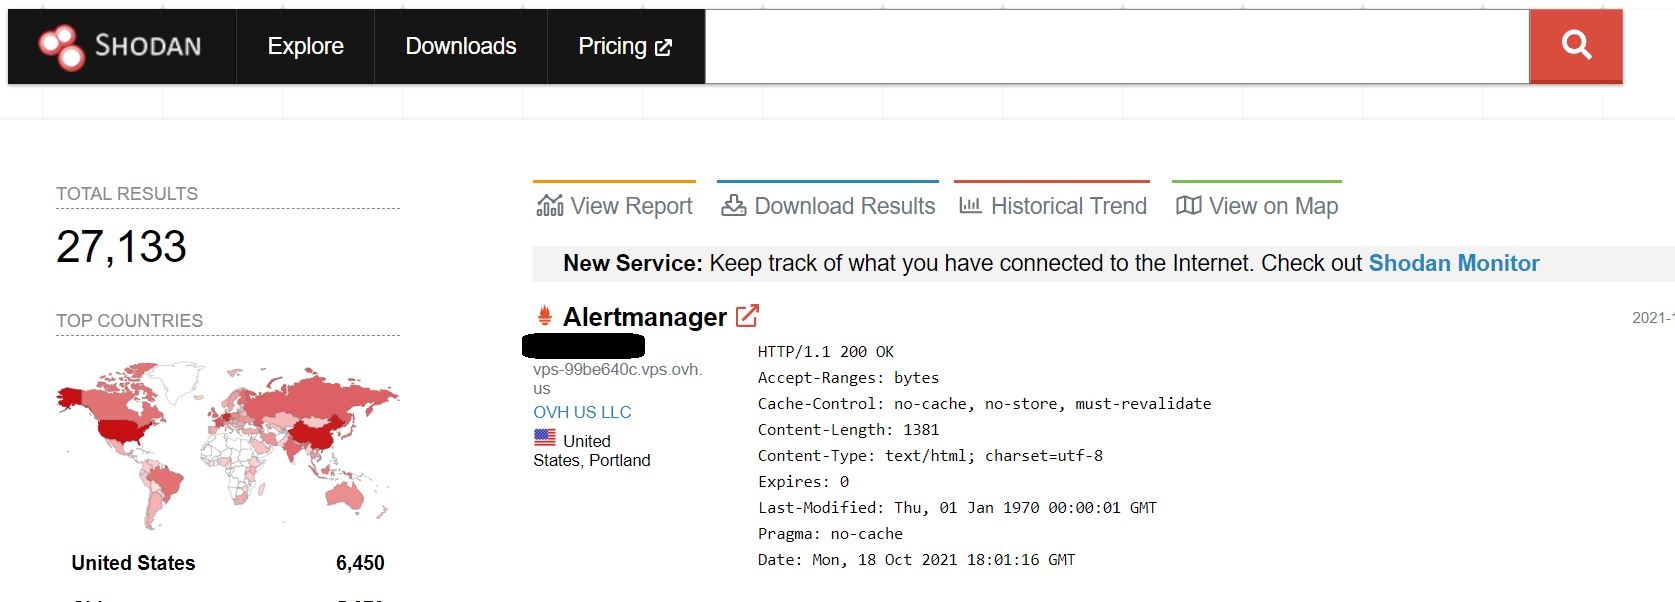
Experts discovered several unprotected installs of open source event monitoring solution Prometheus that may expose sensitive data. JFrog researchers have discovered multiple unprotected instances of open source event monitoring solution Prometheus that may leak sensitive data. The solution scrapes real-time metrics from multiple endpoints, it is used by several major organizations such as Uber. Prometheus’ […]
 Pierluigi Paganini
October 18, 2021
A ransomware attack is likely the cause of the recent downtime for TV stations owned by the Sinclair Broadcast Group broadcast television company. TV stations owned by the Sinclair Broadcast Group went down over the weekend officially due to technical issues, but some media [1,2] reported that it was a victim of a ransomware attack. […]
 Pierluigi Paganini
October 18, 2021
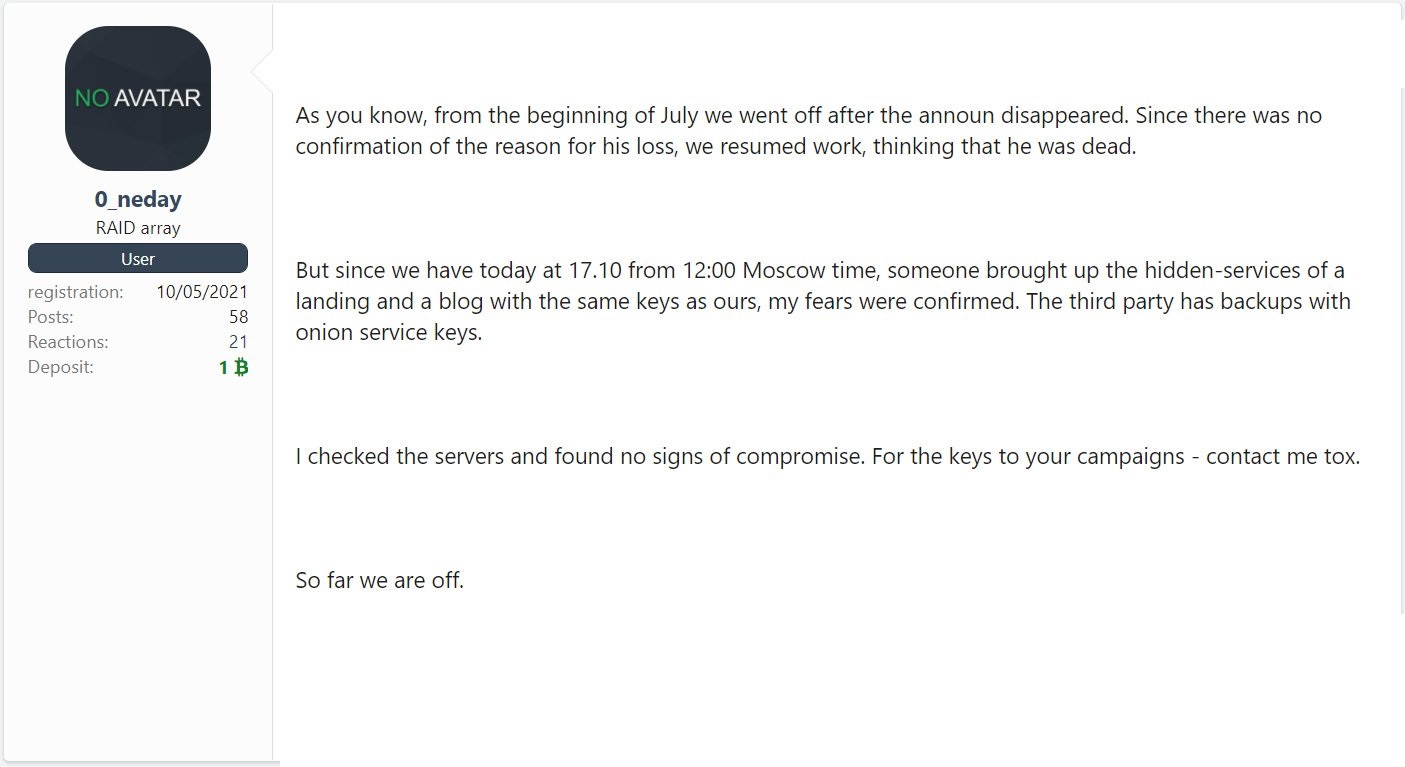
It seems that the REvil ransomware operation has shut down once again after a threat actor has hijacked their Tor hidden service. The REvil ransomware gang has shut down its operation once again after a threat actor has hijacked their Tor leak site and payment portal. The news of the hack was shared by the […]
 Pierluigi Paganini
October 18, 2021
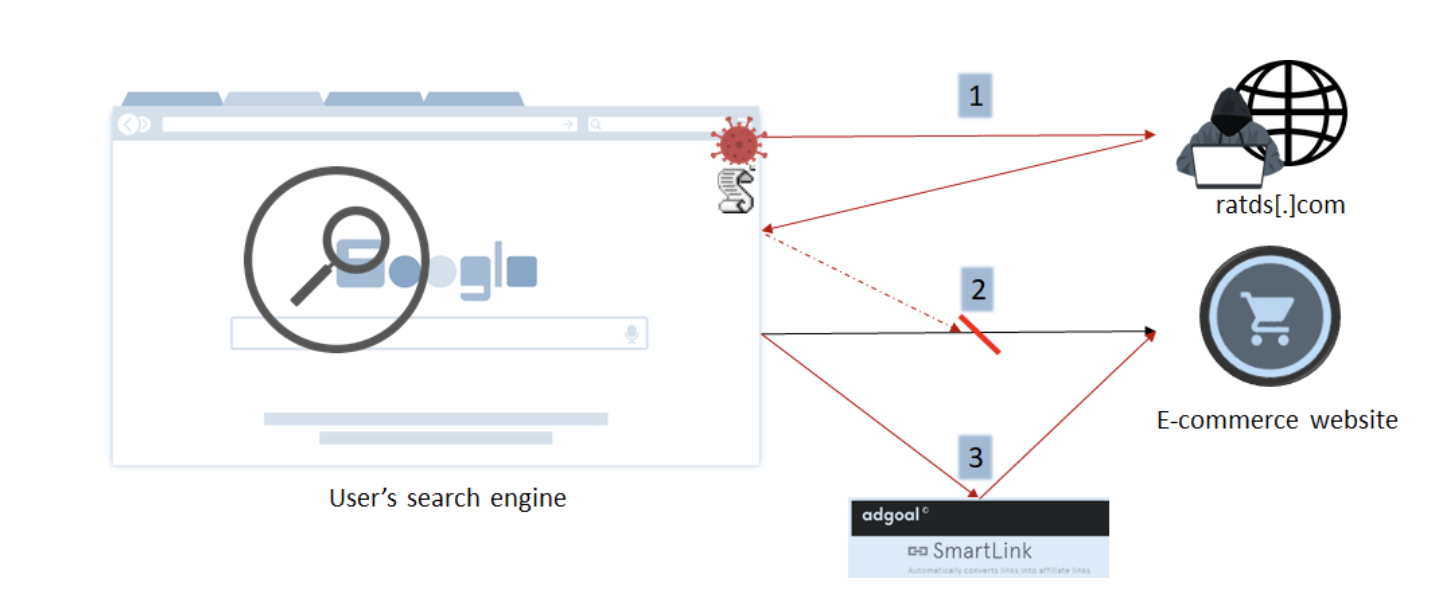
Researchers warn of an Ad-Blocking Chrome extension that was abused by threat actors to Injecting Ads in Google search pages. Researchers from Imperva have spotted a new deceptive ad injection campaign that is targeting users of some large websites leveraging an AD-blocking extension, named AllBlock, that is available on both Chrome and Opera browsers. Ad […]