 Pierluigi Paganini
 March 10, 2023
An international law enforcement operation seized the infrastructure associated with the NetWire RAT and resulted in the arrest of its administrator. A coordinated international law enforcement operation resulted in the seizure of the infrastructure associated with the NetWire RAT, the police also arrested its administrator. Law enforcement seized the website www.worldwiredlabs[.]com and its alleged administrator, […]
 Pierluigi Paganini
March 09, 2023
Alleged China-linked threat actors infected unpatched SonicWall Secure Mobile Access (SMA) appliances with a custom backdoor. Mandiant researchers reported that alleged China-linked threat actors, tracked as UNC4540, deployed custom malware on a SonicWall SMA appliance. The malware allows attackers to steal user credentials, achieve persistence through firmware upgrades, and provides shell access. The analysis of a […]
 Pierluigi Paganini
March 09, 2023
The recently discovered Windows ransomware IceFire now also targets Linux enterprise networks in multiple sectors. SentinelLabs researchers discovered new Linux versions of the recently discovered IceFire ransomware that was employed in attacks against several media and entertainment organizations worldwide. The ransomware initially targeted only Windows-based systems, with a focus on technology companies. IceFire was first detected in […]
 Pierluigi Paganini
March 09, 2023
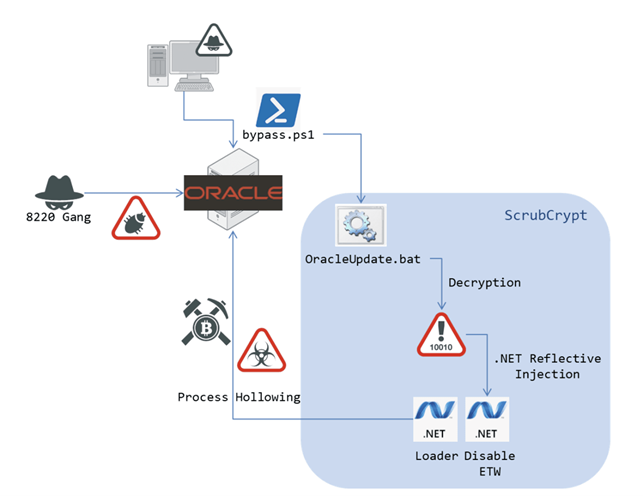
A threat actor tracked as 8220 Gang has been spotted using a new crypter called ScrubCrypt in cryptojacking campaigns. Fortinet researchers observed the mining group 8220 Gang using a new crypter called ScrubCrypt in cryptojacking attacks. “Between January and February 2023, FortiGuard Labs observed a payload targeting an exploitable Oracle Weblogic Server in a specific […]
 Pierluigi Paganini
March 08, 2023
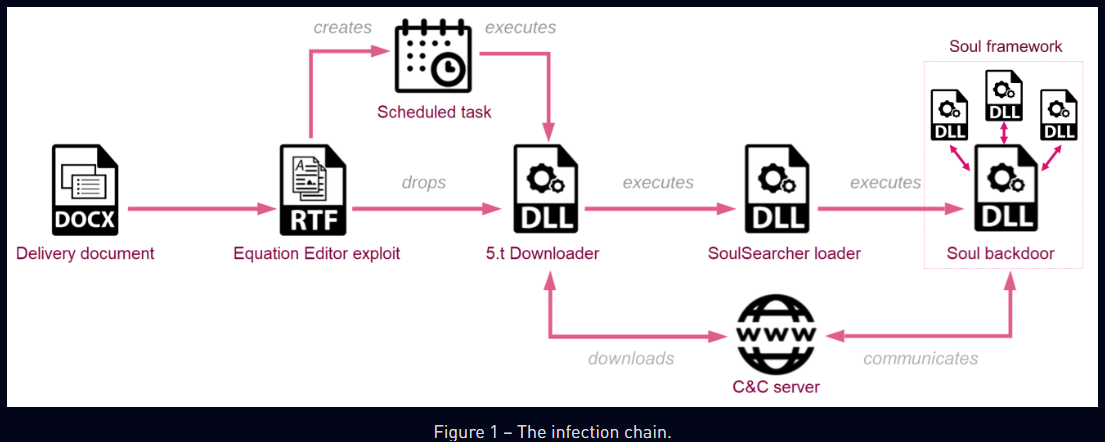
China-linked APT group Sharp Panda targets high-profile government entities in Southeast Asia with the Soul modular framework. CheckPoint researchers observed in late 2022, a campaign attributed to the China-linked APT group Sharp Panda that is targeting a high-profile government entity in the Southeast Asia. The state-sponsored hackers used a new version of the SoulSearcher loader, which eventually loads a new […]
 Pierluigi Paganini
March 07, 2023
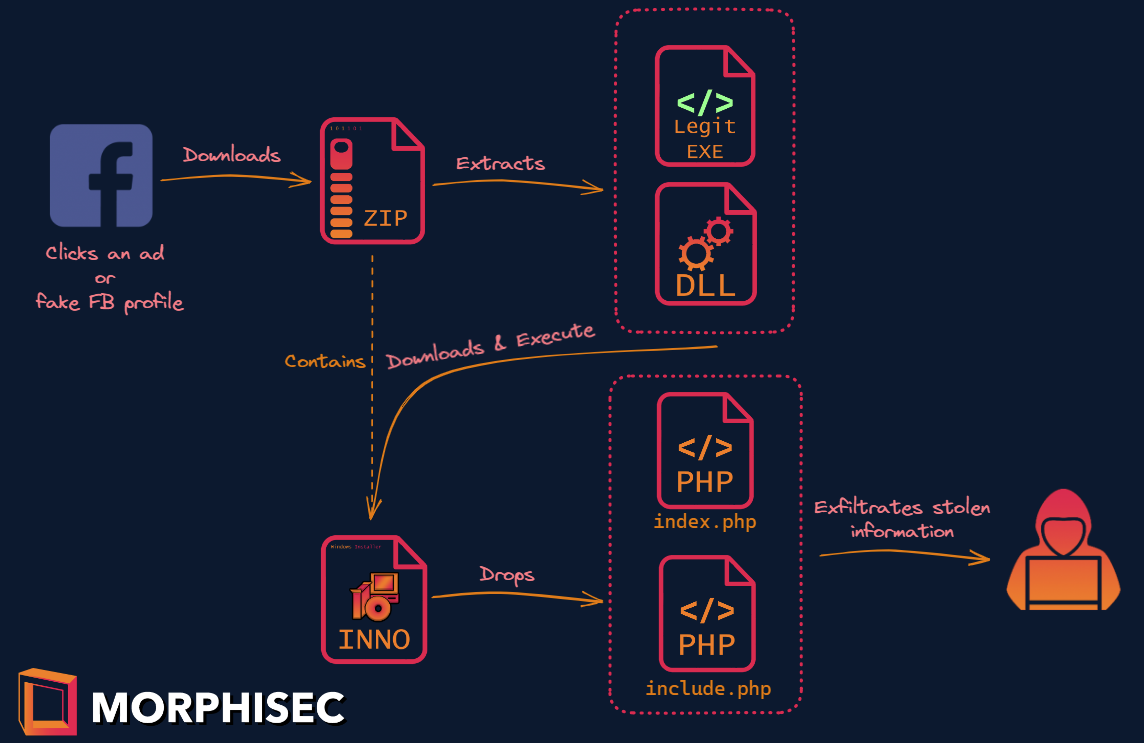
Researchers discovered a new info stealer dubbed SYS01 stealer targeting critical government infrastructure and manufacturing firms. Cybersecurity researchers from Morphisec discovered a new, advanced information stealer, dubbed SYS01 stealer, that since November 2022 was employed in attacks aimed at critical government infrastructure employees, manufacturing companies, and other sectors. The experts found similarities between the SYS01 stealer and another […]
 Pierluigi Paganini
March 06, 2023
Hospital Clinic de Barcelona, one of the main hospitals in the Spanish city, suffered a cyber attack that crippled its computer system. On Sunday, a ransomware attack hit the Hospital Clinic de Barcelona, one of the main hospitals of the Catalan city. The attack crippled the center’s computer system, 150 nonurgent operations and up to […]
 Pierluigi Paganini
March 06, 2023
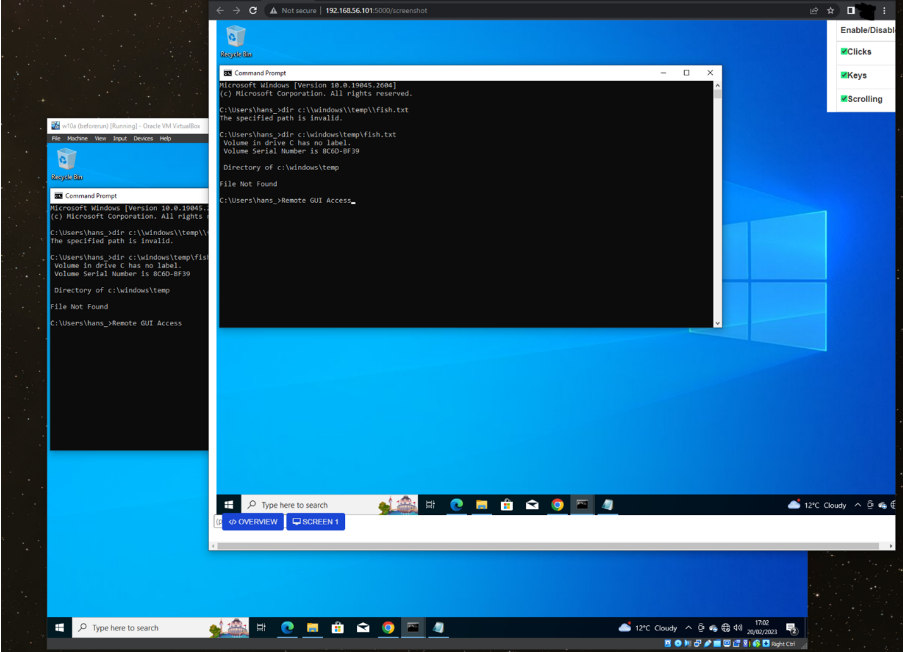
Experts discovered a fully featured information stealer, tracked as ‘Colour-Blind’ in the Python Package Index (PyPI). Researchers from Kroll’s Cyber Threat Intelligence team discovered a malicious Python package uploaded to the Python Package Index (PyPI) that contained a fully-featured information stealer and remote access trojan tracked as Colour-Blind. Below is the list of capabilities supported […]
 Pierluigi Paganini
March 05, 2023
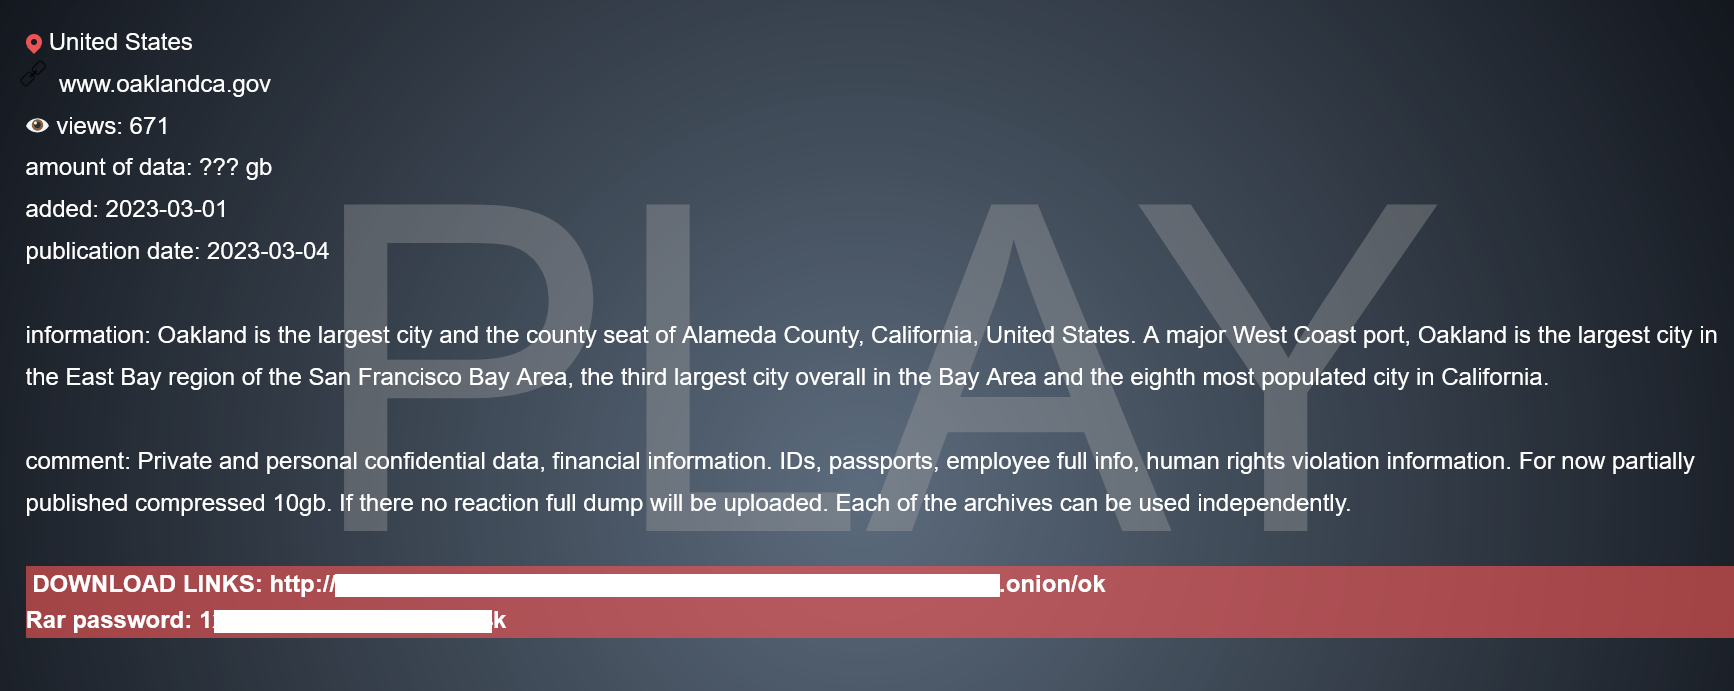
The Play ransomware gang has finally begun to leak the data stolen from the City of Oakland in a recent attack. The Play ransomware gang has begun to leak data they have stolen from the City of Oakland (California) in a recent cyberattack. Oakland is the largest city in the East Bay region of the […]
 Pierluigi Paganini
March 04, 2023
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs are free for you in your email box. If you want to also receive for free the newsletter with the international press subscribe here. FiXS, a new ATM malware that is targeting Mexican banks BidenCash leaks 2.1M stolen credit/debit […]