 Pierluigi Paganini
 May 02, 2026
Two US security experts were sentenced to 4 years for helping ransomware attacks. A third accomplice pleaded guilty and awaits sentencing. Two US cybersecurity professionals, Ryan Goldberg and Kevin Martin, were sentenced to four years in prison for their role in supporting ransomware attacks. Both pleaded guilty to conspiracy involving extortion. A third individual, Angelo […]
 Pierluigi Paganini
May 02, 2026
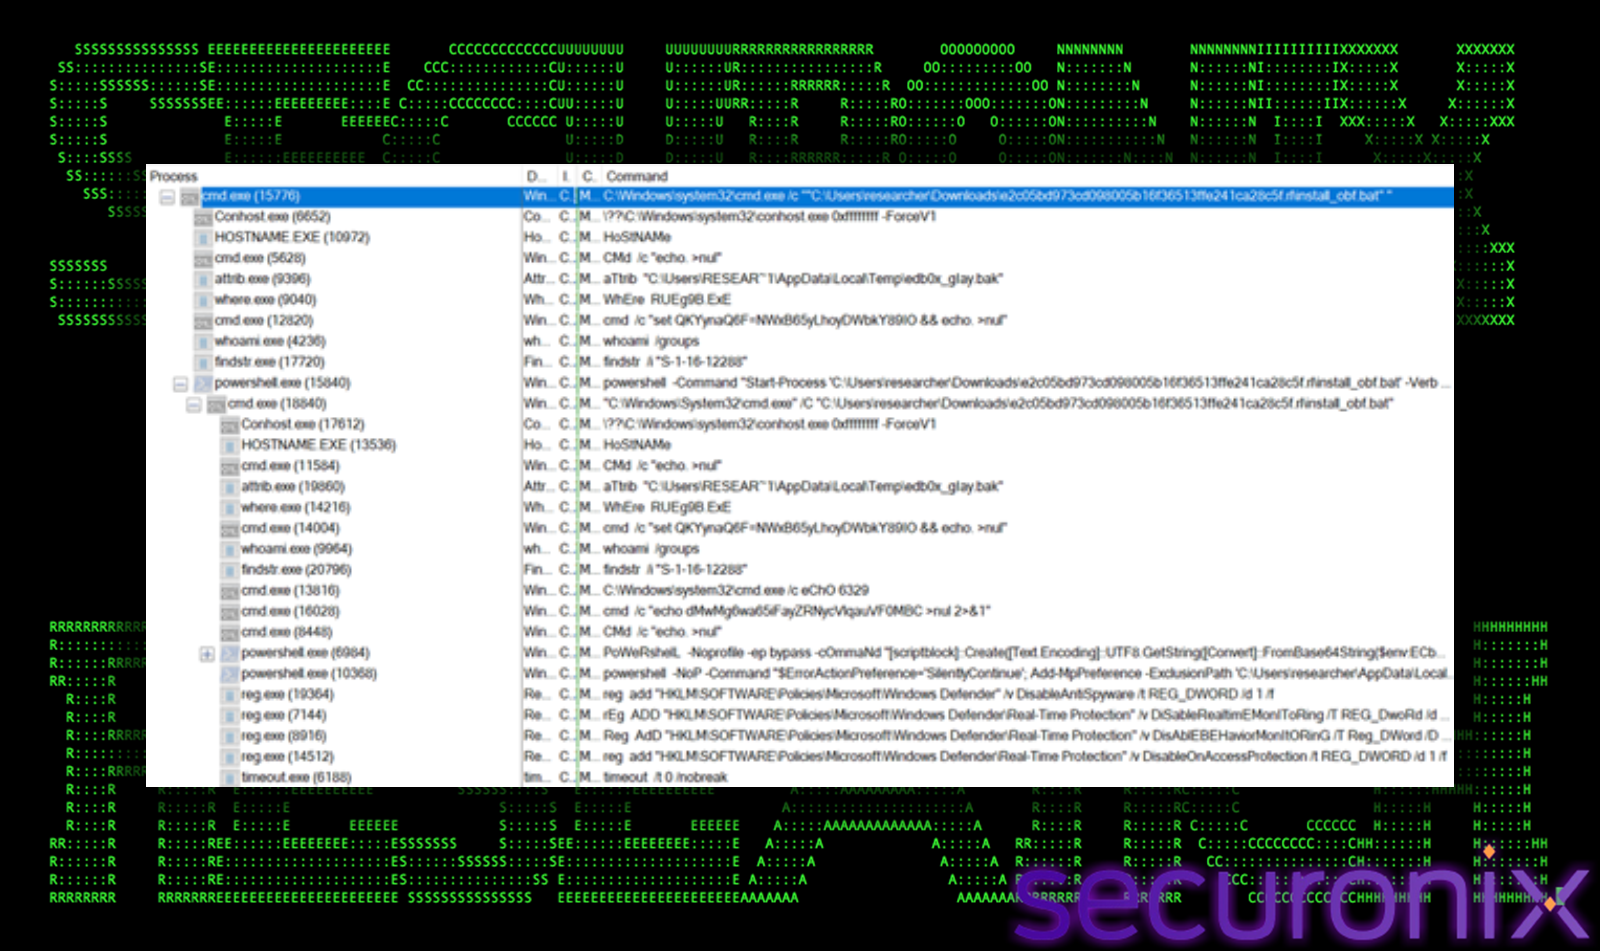
Deep#Door hides a Python RAT inside a batch file, kills Windows defenses, survives via multiple persistence methods, and exfiltrates data through a public TCP tunnel. Security researchers at Securonix uncovered a sophisticated malware campaign called Deep#Door. Threat actors employed a stealthy Python-based backdoor that uses a surprisingly simple delivery method to achieve deep, persistent access […]
 Pierluigi Paganini
April 28, 2026
Osservatorio Nessuno uncovered Morpheus spyware spreading via fake Android apps to steal data, highlighting rising covert surveillance tools. The non-partisan, non-religious, nonprofit organization Osservatorio Nessuno exposed a new spyware called Morpheus, distributed through fake Android apps posing as updates. Once installed, it can steal extensive data from the infected devices. The report shows strong demand […]
 Pierluigi Paganini
April 27, 2026
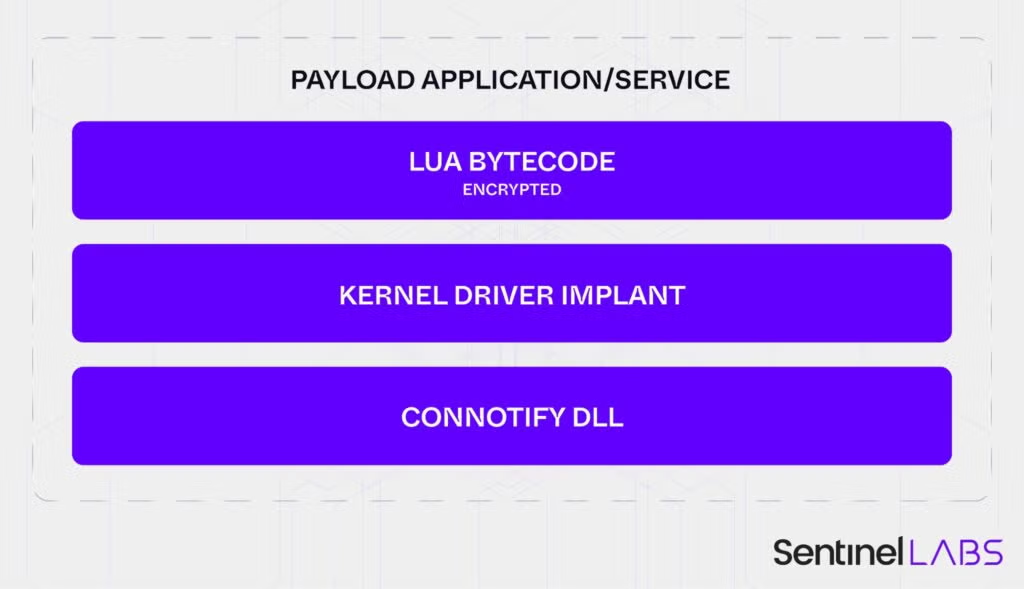
Fast16 is a pre-Stuxnet malware that tampered with precision software and spread itself. Evidence suggests links to U.S. operations during early cyber tensions. SentinelOne uncovered Fast16, a sabotage malware used in 2005, years before Stuxnet. The malicious code is written in Lua and targeted high-precision calculation software, altering results and spreading across systems. The malware […]
 Pierluigi Paganini
April 26, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Morpheus: A new Spyware linked to IPS Intelligence The iPhone — invincible no more: a look at DarkSword and Coruna Lotus Wiper: a new threat targeting the energy and utilities sector New NGate variant hides in […]
 Pierluigi Paganini
April 26, 2026
Trigona ransomware now uses a custom command-line tool to steal data faster and evade detection, replacing tools like Rclone and MegaSync. Symantec researchers report that recent Trigona ransomware attacks used a custom-built data exfiltration tool instead of common utilities like Rclone or MegaSync. This shift, seen in March 2026 incidents, gives attackers more control and […]
 Pierluigi Paganini
April 26, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. U.S. CISA adds SimpleHelp, Samsung, and D-Link flaws to its Known Exploited Vulnerabilities catalog Over 400,000 […]
 Pierluigi Paganini
April 25, 2026
CISA said a federal Cisco Firepower ASA device was infected with the FIRESTARTER backdoor in Sept 2025, and it survived security patches. CISA revealed that a U.S. federal civilian agency’s Cisco Firepower device running ASA software was compromised in September 2025 by the FIRESTARTER backdoor. The malware reportedly persisted even after security patches were applied, […]
 Pierluigi Paganini
April 24, 2026
UK National Cyber Security Centre (NCSC) warns China-linked hackers use hijacked devices as proxy networks to hide activity and evade detection. UK National Cyber Security Centre (NCSC) and global partners warn that China-linked threat actors now rely on large proxy networks built of hacked consumer devices. Groups control routers, cameras, video recorders, and NAS systems […]
 Pierluigi Paganini
April 23, 2026
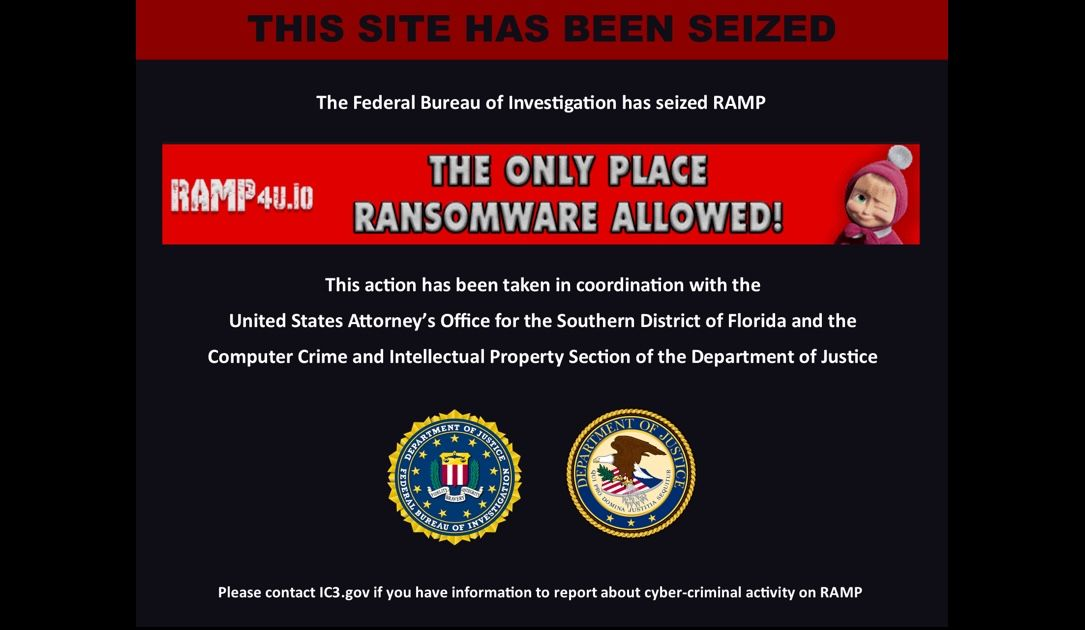
Leaked data from RAMP reveals Russia’s ransomware ecosystem, analyzing 1,732 threads, 7,707 users, and 340,000 IP records from the forum. RAMP was not just another dark web forum. It was one of the clearest examples of how ransomware has become an organized marketplace, with sellers, buyers, brokers, and recruiters all playing different roles in the […]