 Pierluigi Paganini
 April 08, 2026
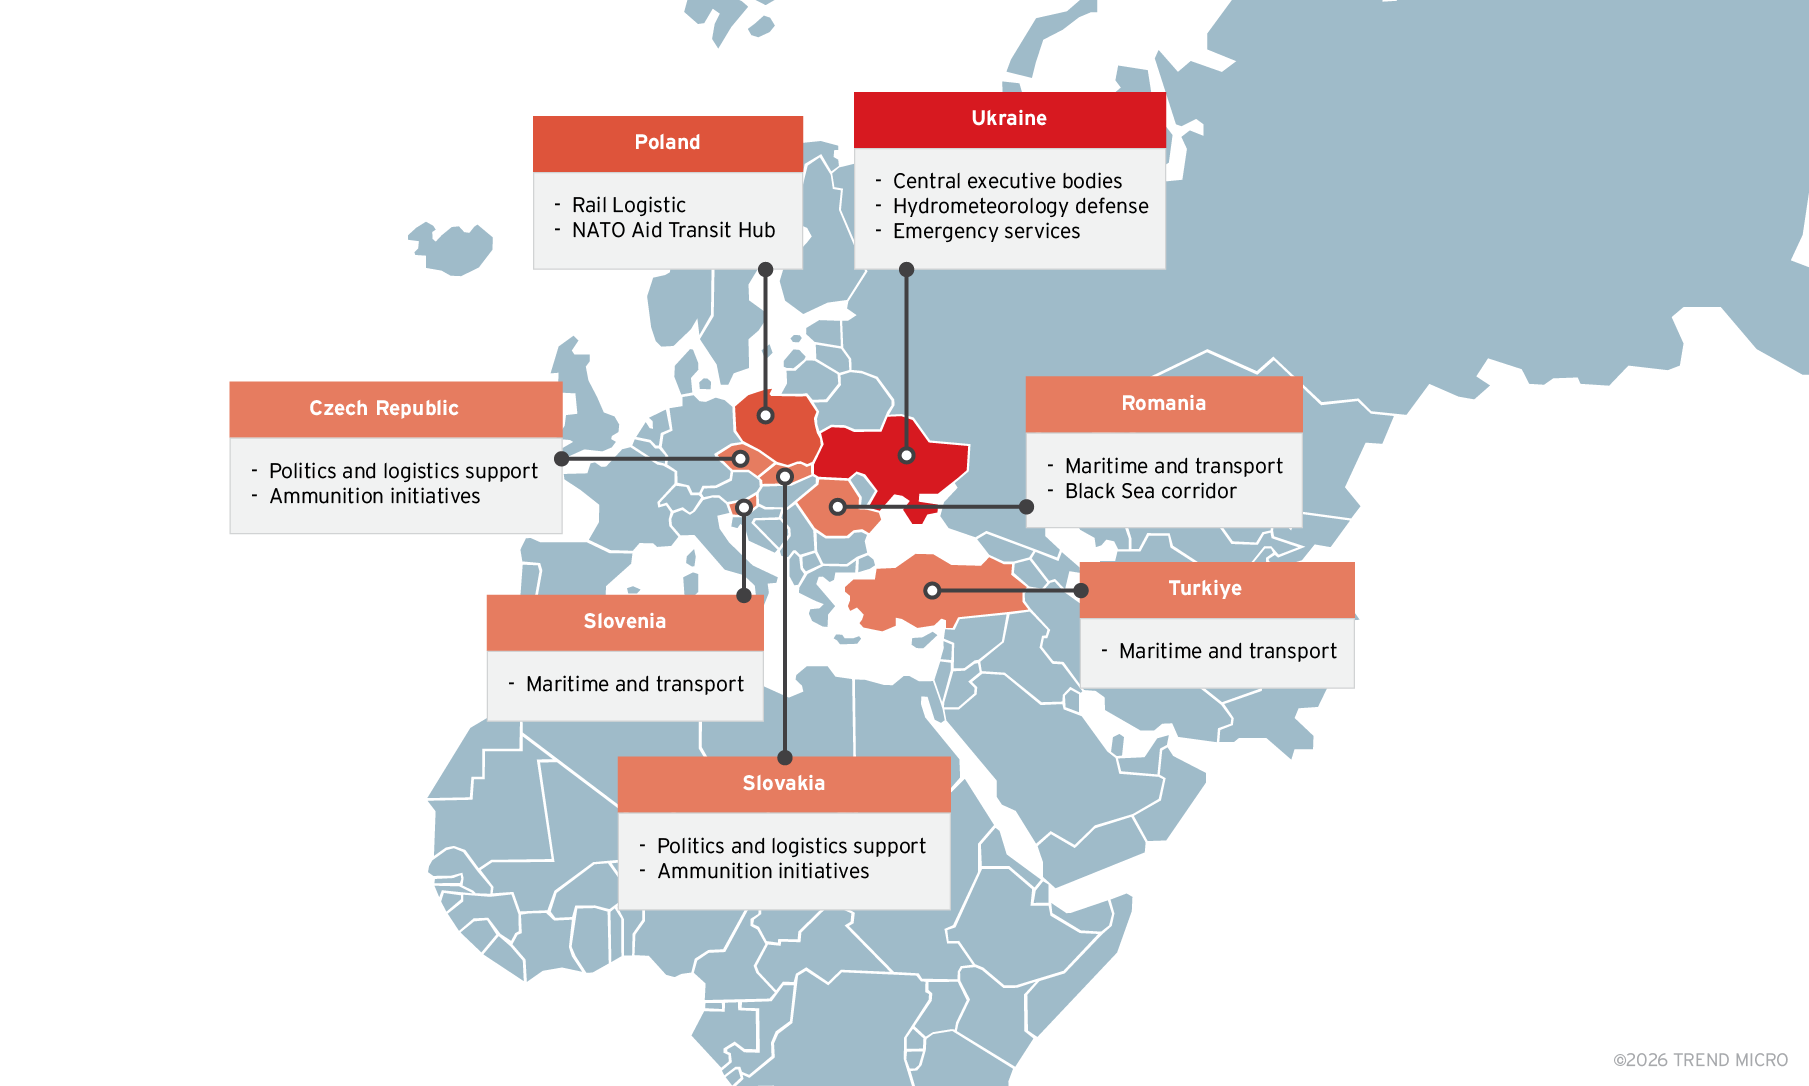
APT28 targets Ukraine and allies with PRISMEX malware, using stealthy techniques for espionage and command-and-control. Russia-linked group APT28 (aka UAC-0001, aka Fancy Bear, Pawn Storm, Sofacy Group, Sednit, BlueDelta, and STRONTIUM) is running a spear-phishing campaign against Ukraine and its allies, deploying a new malware suite called PRISMEX. Active since September 2025, the campaign uses advanced stealth techniques like steganography and […]
 Pierluigi Paganini
April 07, 2026
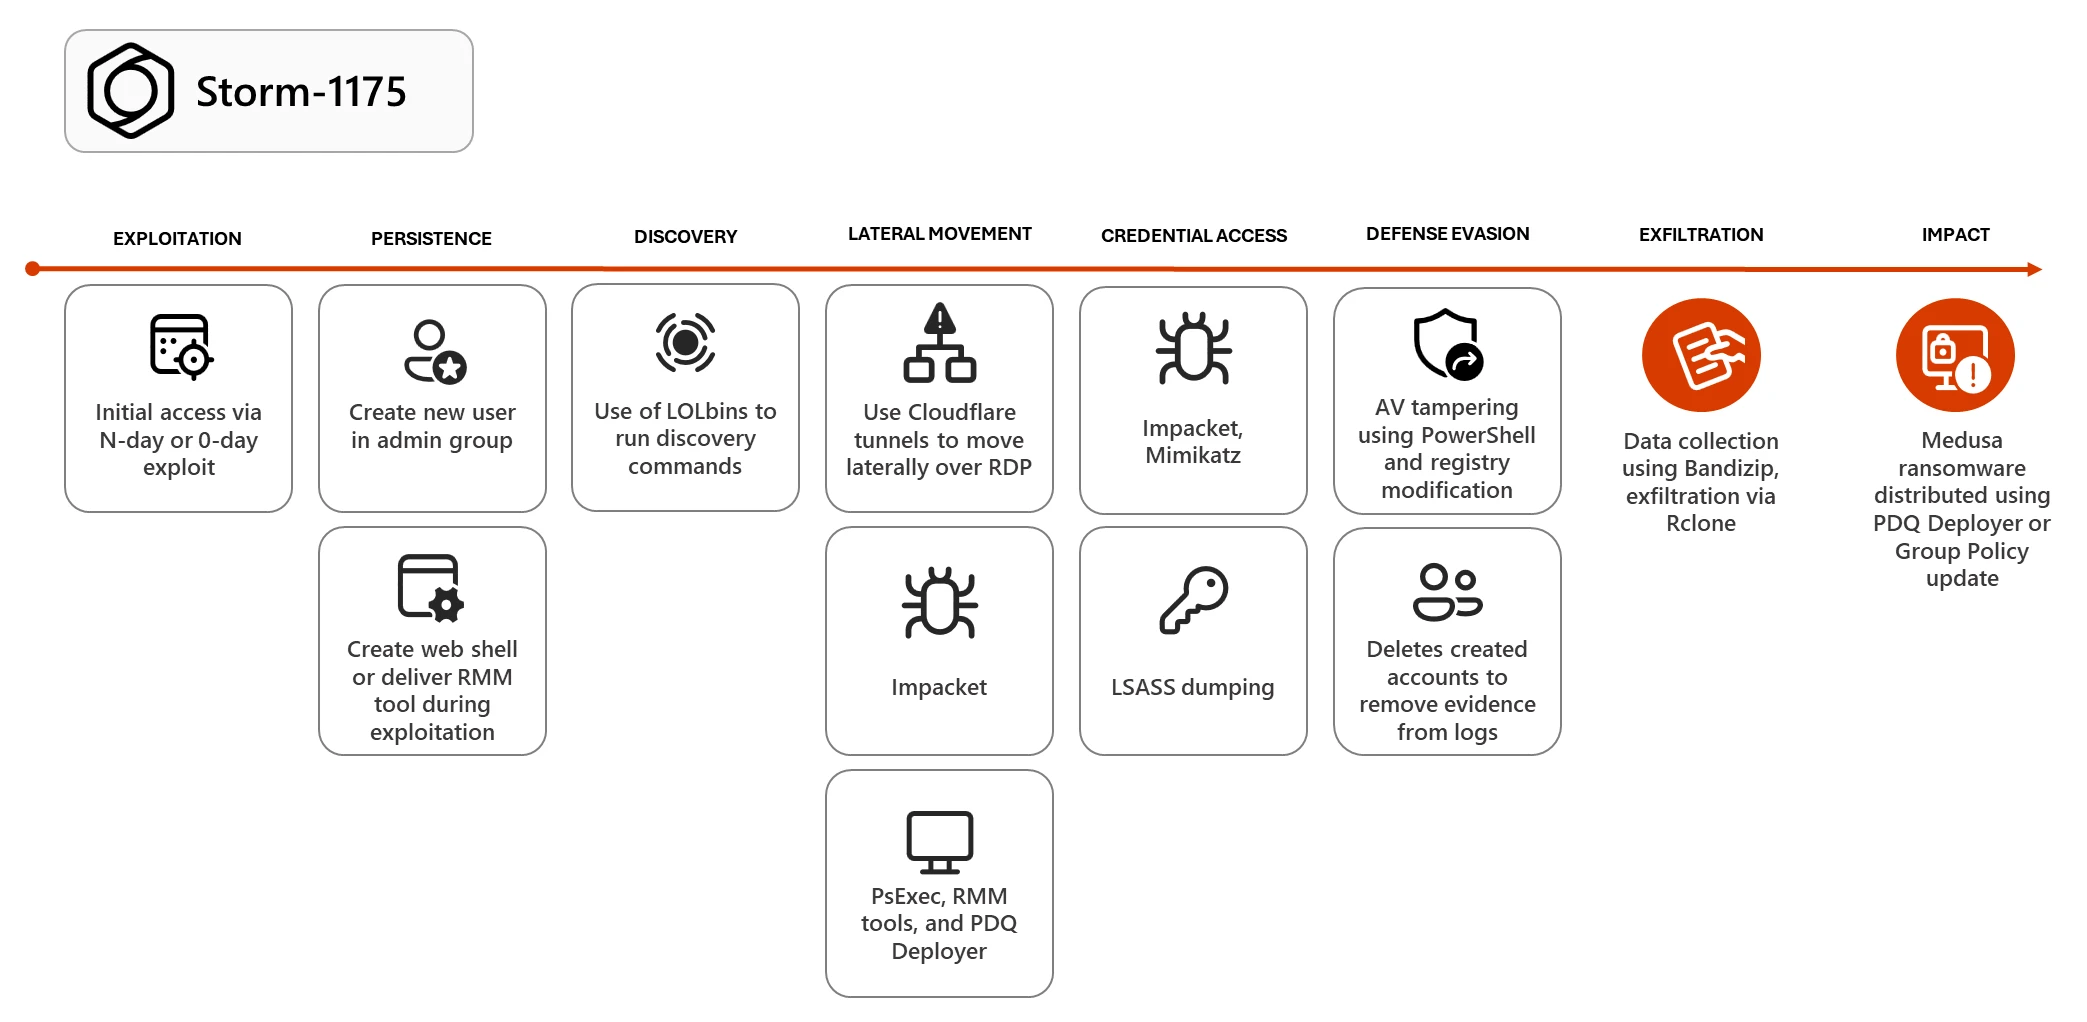
China-based actor Storm-1175 runs fast ransomware attacks, exploiting new flaws to breach systems and quickly deploy Medusa ransomware. China-based actor Storm-1175 carries out fast, financially driven ransomware attacks by exploiting newly disclosed vulnerabilities before organizations patch them. The group targets exposed systems and quickly moves from initial access to data theft and Medusa ransomware deployment, […]
 Pierluigi Paganini
April 06, 2026
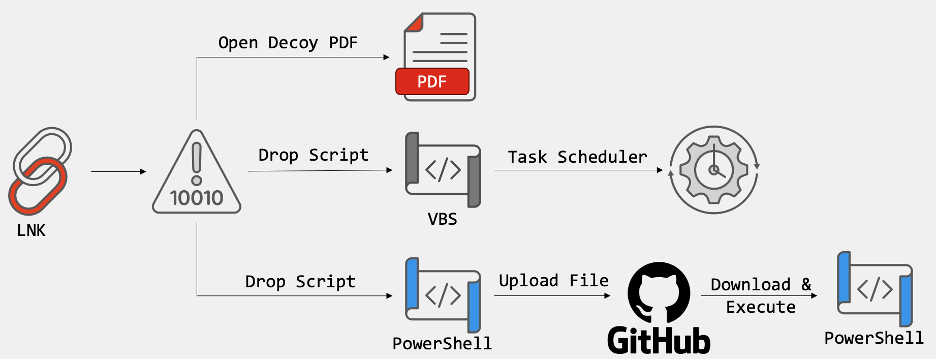
DPRK-linked hackers use GitHub C2s, starting attacks via phishing LNK files that drop a PDF and PowerShell script in South Korea. North Korea-linked threat actors target South Korean organizations using GitHub as C2 servers. The attack chain starts with phishing emails carrying obfuscated LNK files that drop a decoy PDF and a PowerShell script to […]
 Pierluigi Paganini
April 06, 2026
German police BKA identified two key REvil ransomware members, linking them to over 130 attacks in Germany. Germany’s Federal Criminal Police (BKA) has identified two key figures behind the REvil ransomware group, linking them to more than 130 attacks in the country. The first suspect is Daniil Maksimovich Shchukin (31), a Russian national known online […]
 Pierluigi Paganini
April 05, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Infiniti Stealer: a new macOS infostealer using ClickFix and Python/Nuitka Converging Interests: Analysis of Threat Clusters Targeting a Southeast Asian Government RoadK1ll: A WebSocket Based Pivoting Implant axios Compromised: npm Supply Chain Attack via Dependency Injection […]
 Pierluigi Paganini
April 05, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. Qilin ransomware group claims the hack of German political party Die Linke U.S. CISA adds a […]
 Pierluigi Paganini
April 04, 2026
Qilin ransomware claims it stole data from Germany’s Die Linke and threatens to leak it; the party confirmed the incident, but not a breach. The Qilin ransomware group claims it stole data from Die Linke, a German political party, and is threatening to release it. Die Linke is a left-wing political party in Germany. Its […]
 Pierluigi Paganini
April 04, 2026
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a flaw in TrueConf Client to its Known Exploited Vulnerabilities catalog The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a flaw in TrueConf Client, tracked as CVE-2026-3502 (CVSS score of 7.8), to its Known Exploited Vulnerabilities (KEV) catalog. TrueConf is a videoconferencing platform often used in secure, offline […]
 Pierluigi Paganini
April 03, 2026
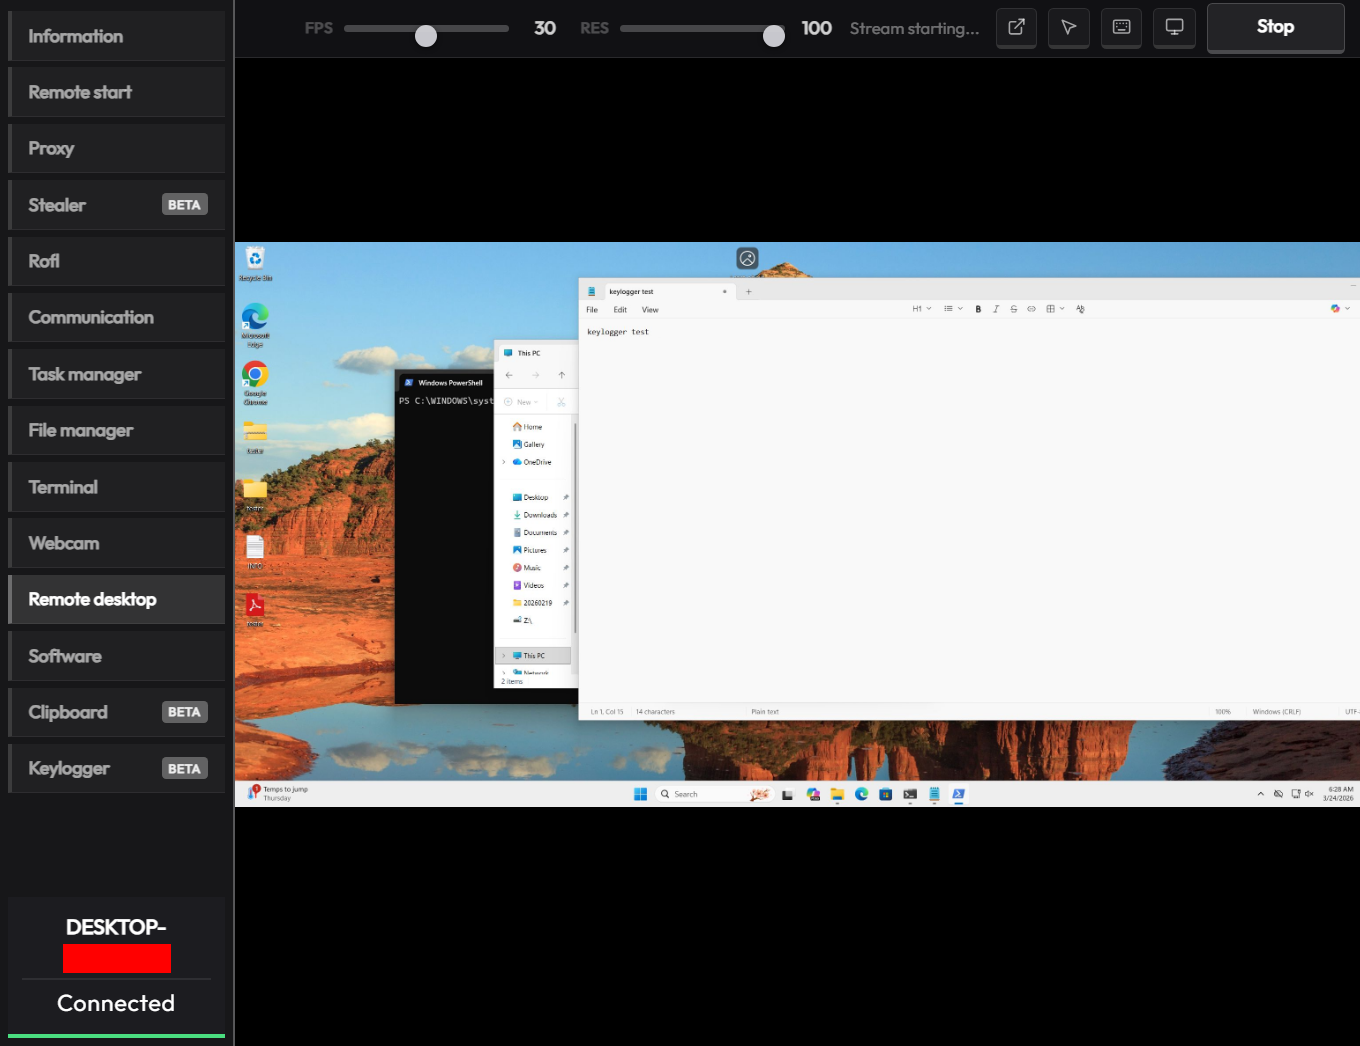
CrystalX RAT, a new sophisticated MaaS malware, combines spyware, data theft, and remote access, allowing attackers to monitor victims. In March 2026, Kaspersky researchers uncovered a Telegram-based campaign promoting a previously unknown malware sold as a MaaS with three subscription tiers. The Trojan offers a wide range of features, including RAT capabilities, data theft, keylogging, […]
 Pierluigi Paganini
April 02, 2026
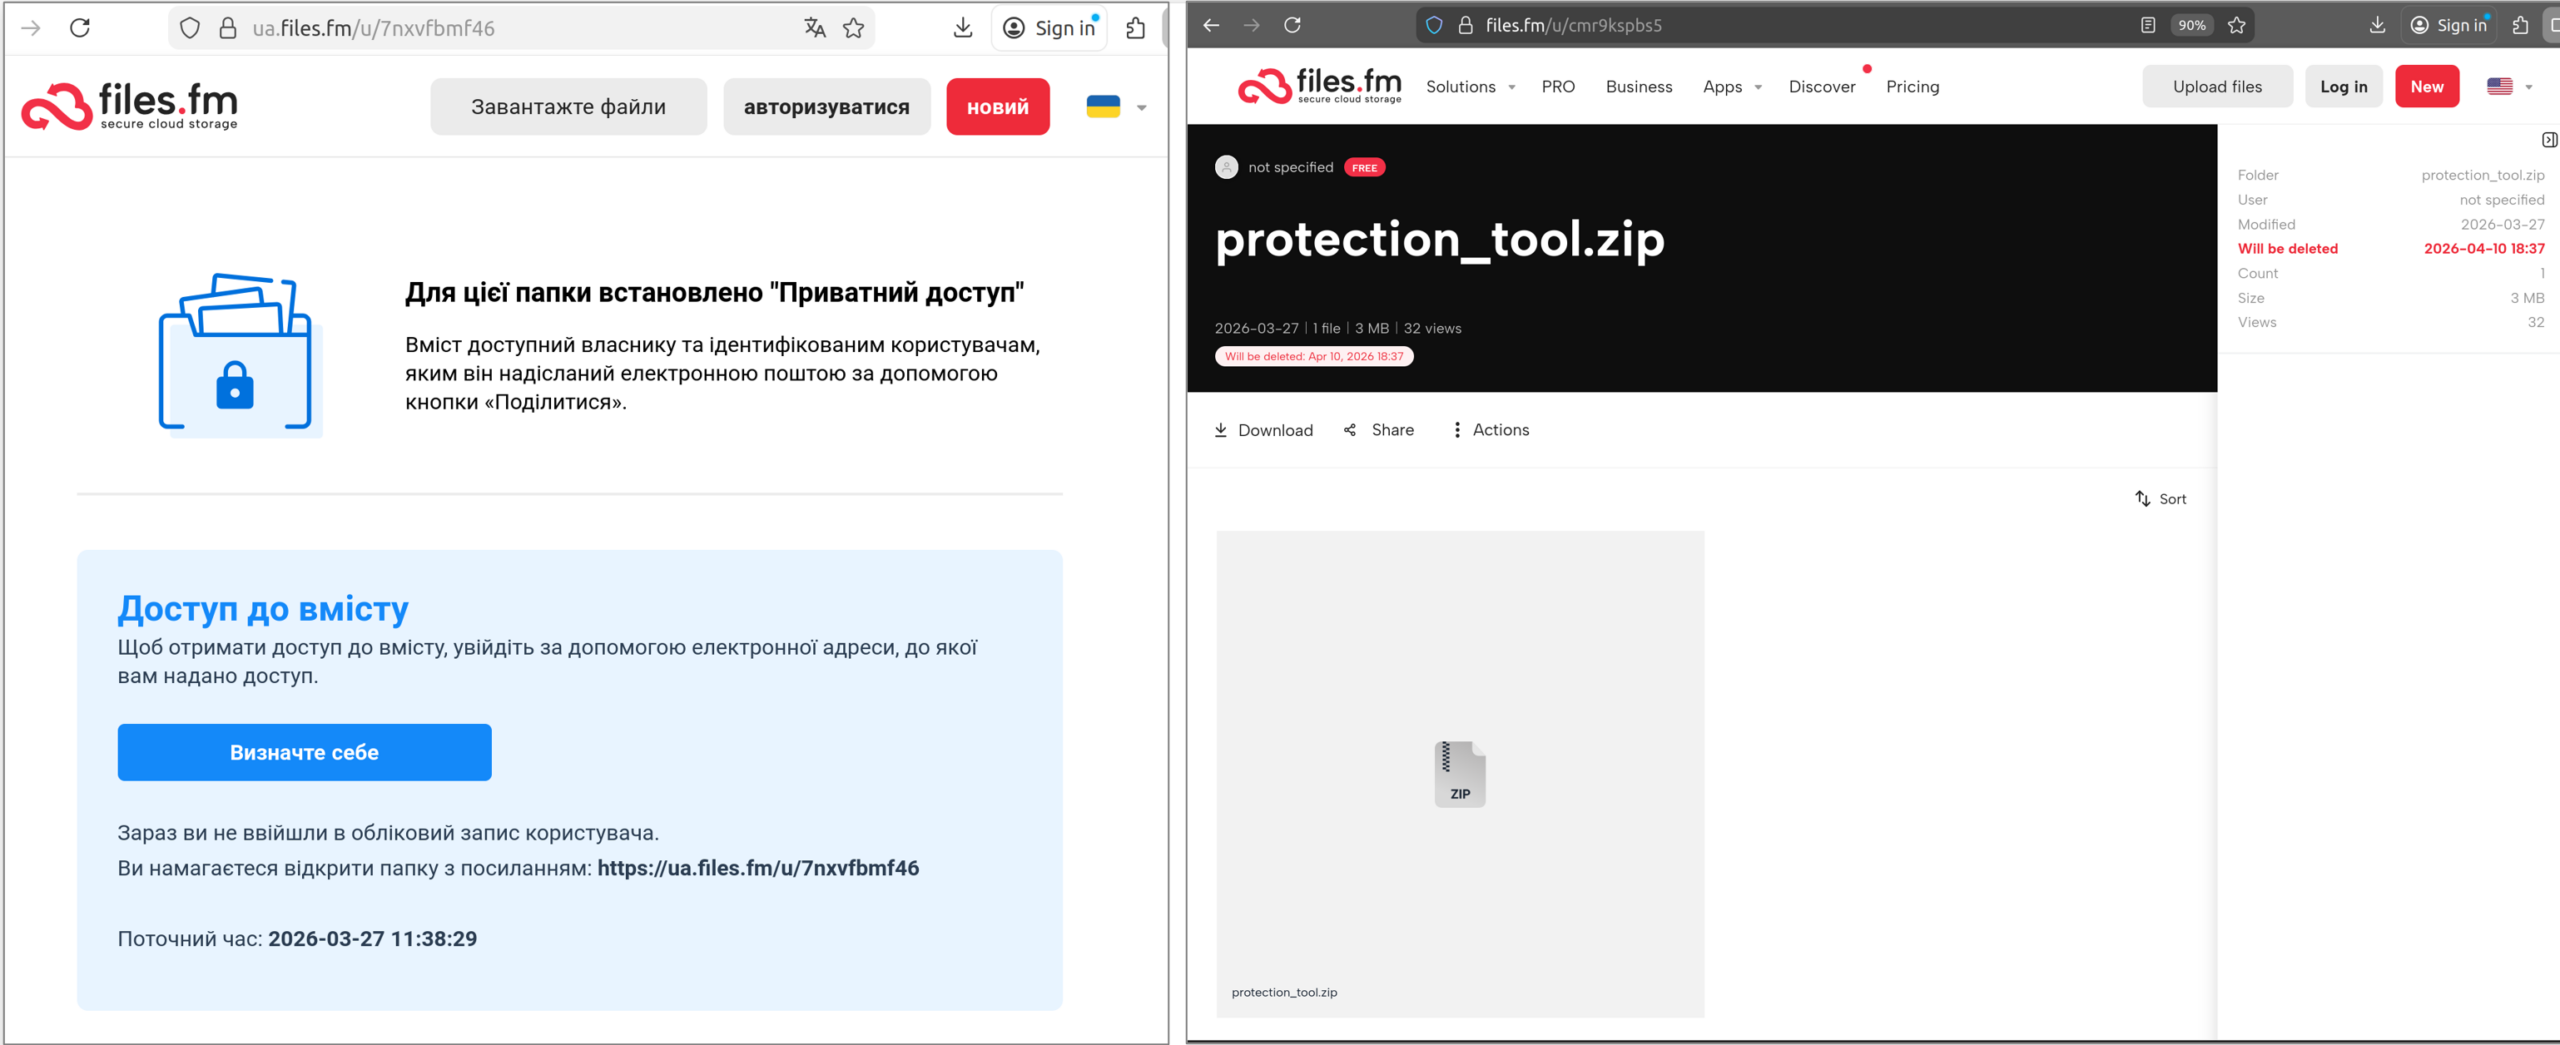
Threat actors impersonated CERT-UA to send phishing emails with AGEWHEEZE malware, tricking victims into installing a fake “security tool.” A threat actor, tracked as UAC-0255, impersonated CERT-UA in a phishing campaign, sending emails to about 1 million users. The messages urged victims to download a password-protected archive from Files.fm and install a fake “specialized software,” […]