 Pierluigi Paganini
 April 09, 2018
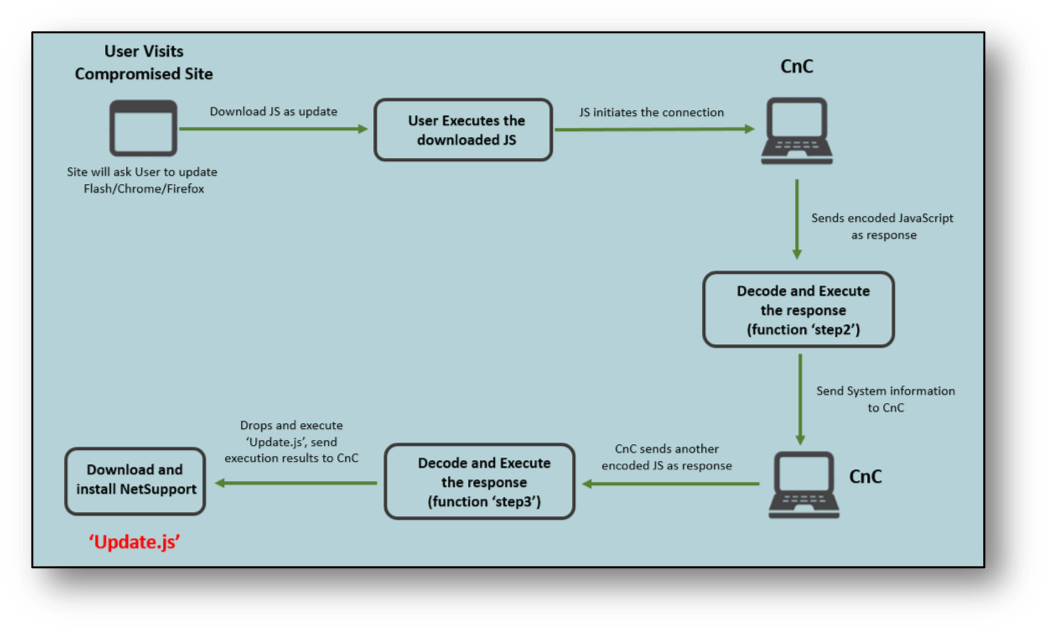
Researchers at FireEye have spotted a hacking campaign leveraging compromised websites to spread fake updates for popular software that were also used to deliver the NetSupport Manager RAT. NetSupport is an off-the-shelf RAT that could be used by system admins for remote administration of computers. In the past, crooks abuse this legitimate application to deploy malware on victim’s […]
 Pierluigi Paganini
April 08, 2018
A new round of the weekly SecurityAffairs newsletter arrived! The best news of the week with Security Affairs. Let me inform you that my new book, “Digging in the Deep Web” is online Kindle Edition Paper Copy Once again thank you! · Airbnb China will share hosts information with the government · Any social media […]
 Pierluigi Paganini
April 08, 2018
A new variant of the infamous Agent Tesla spyware was spotted by experts at Fortinet, the malware has been spreading via weaponize Microsoft Word documents. Agent Tesla is a spyware that is used to spy on the victims by collecting keystrokes, system clipboard, screenshots, and credentials from the infected system. To do this, the spyware […]
 Pierluigi Paganini
April 06, 2018
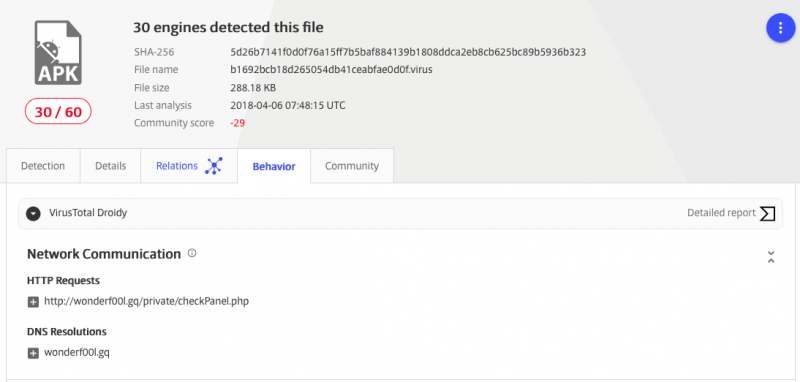
VirusTotal announced on Thursday the launch of a new Android sandbox, named Droidy sandbox, that will replace the previous one that was designed in 2013. “Recently we called out Additional crispinness on the MacOS box of apples sandbox, continuing with our effort to improve our malware behavior analysis infrastructure we are happy to announce […]
 Pierluigi Paganini
April 04, 2018
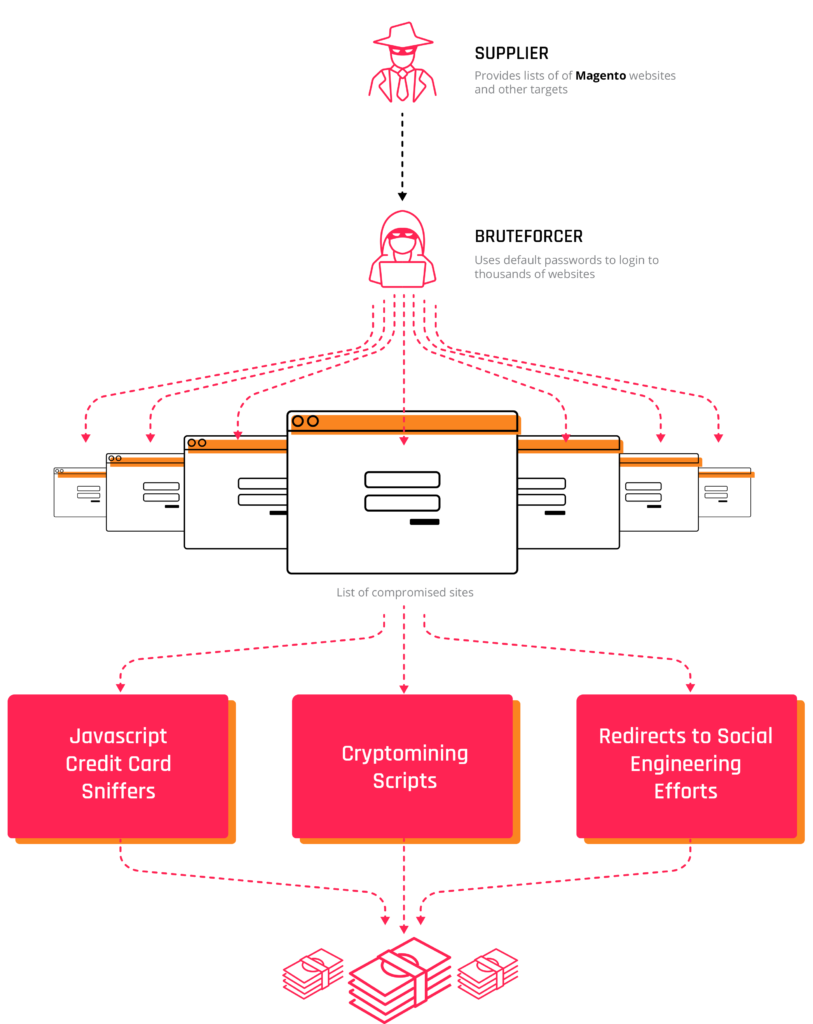
Hackers compromised hundreds of Magento e-commerce websites to steal credit card numbers and install crypto-mining malware. According to the security firm Flashpoint, hackers launched brute-force attacks against Magento installs, they used a dictionary composed of common and known default Magento credentials. “Ecommerce websites running on the popular open-source Magento platform are being targeted by attackers who are using […]
 Pierluigi Paganini
April 04, 2018
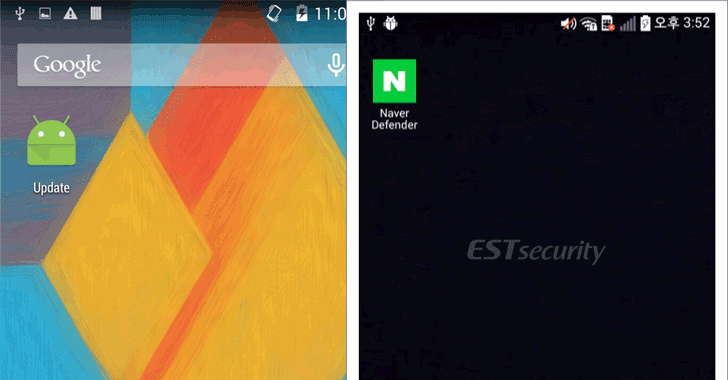
Security researchers discovered a new Android Remote Access Trojan (RAT) dubbed KevDroid that can steal private data and record phone calls. Security researchers at South Korean cybersecurity firm ESTsecurity have discovered a new strain of Android Trojan KevDroid that is being distributed disguised as a fake anti-virus application, dubbed “Naver Defender.” “Spear phishing attacks targeting Android […]
 Pierluigi Paganini
April 02, 2018
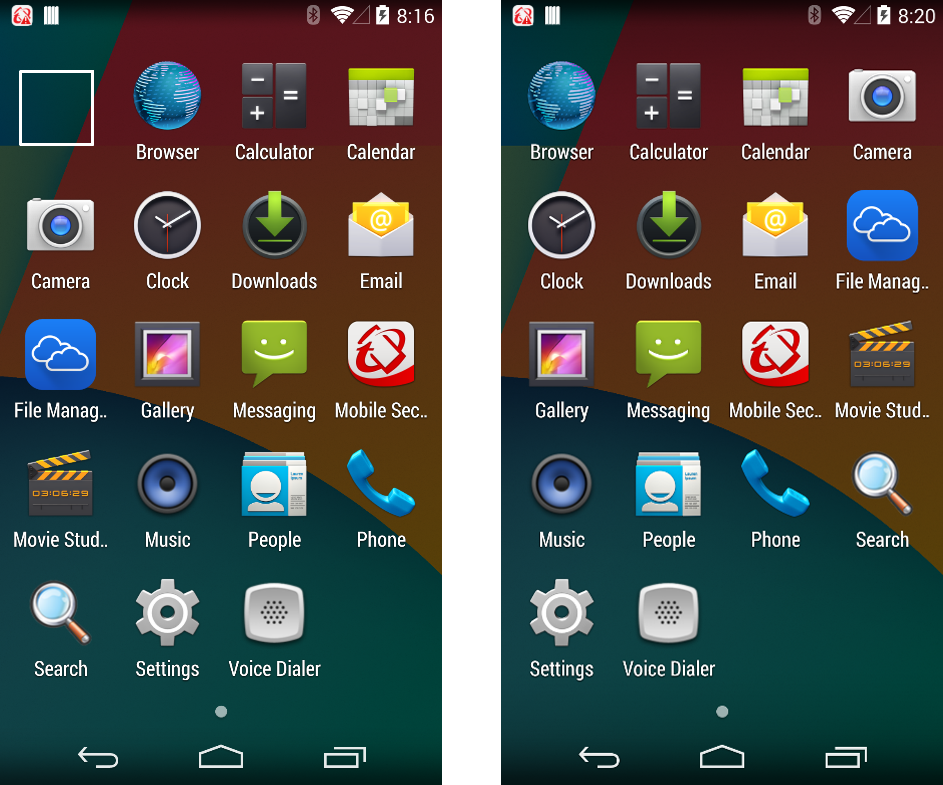
Researchers at Trend Micro recently discovered a new strain of Android miner dubbed ANDROIDOS HIDDENMINER that can brick infected devices Crooks are looking with increasing interest cryptocurrency mining malware developed for mobile devices. Researchers at Trend Micro recently discovered a new strain of Android malware dubbed ANDROIDOS HIDDENMINER that abuse device CPU to mine Monero cryptocurrency. HiddenMiner […]
 Pierluigi Paganini
March 31, 2018
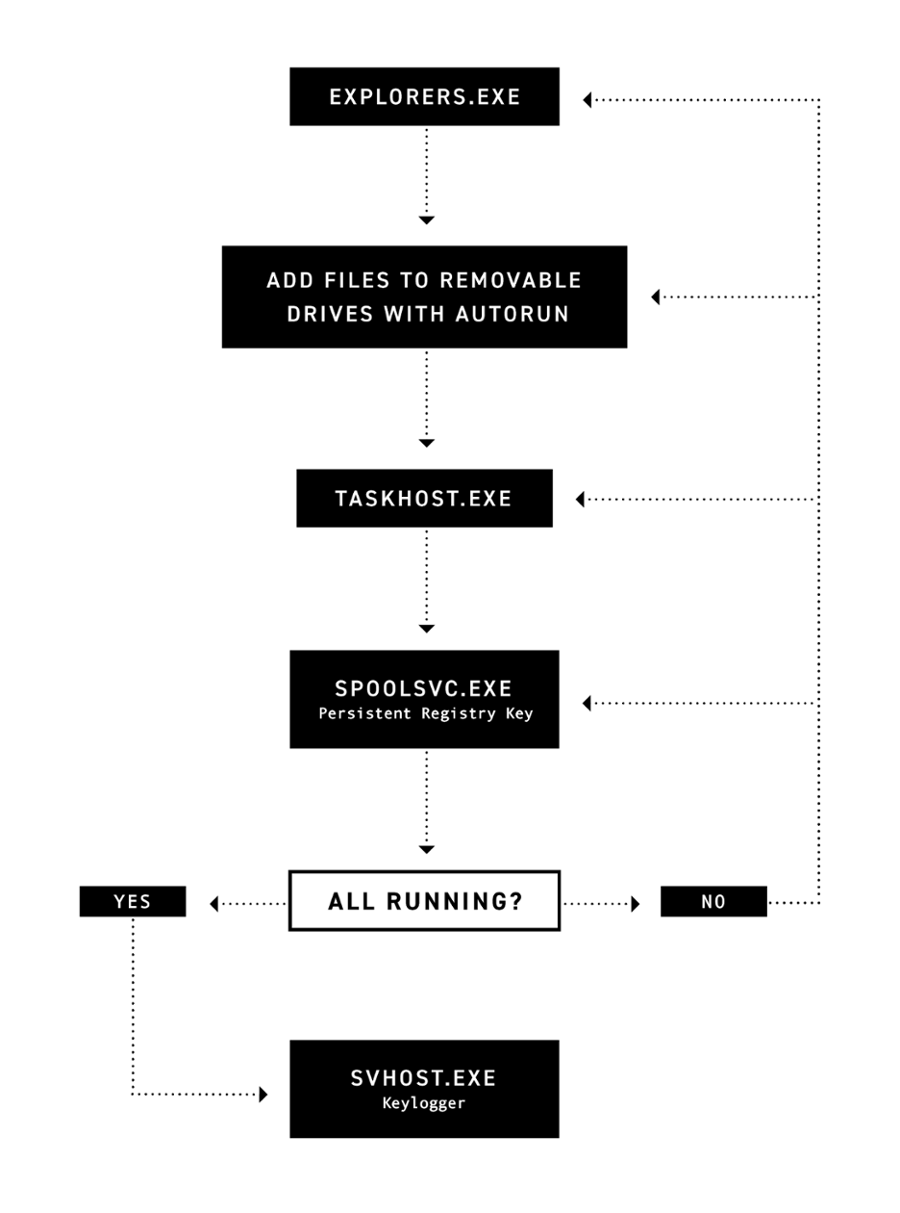
Security researchers at Cybereason recently discovered a credential-stealing malware dubbed Fauxpersky, that is masquerading as Kaspersky Antivirus and spreading via infected USB drives. Fauxpersky was written in AutoIT or AutoHotKey, which respectively are a freeware BASIC-like scripting language designed for automating the Windows GUI and general scripting and a free keyboard macro program to send keystrokes to […]
 Pierluigi Paganini
March 30, 2018
A ransomware infected systems at the Uttar Haryana Bijli Vitran Nigam power company in India, crooks demanded 10 million Rupees to get the data back. The Uttar Haryana Bijli Vitran Nigam power company in India was hacked last week, attackers breached into its computer systems and stole the billing data of their customers. The hackers demanded 10 million Rupees to […]
 Pierluigi Paganini
March 29, 2018
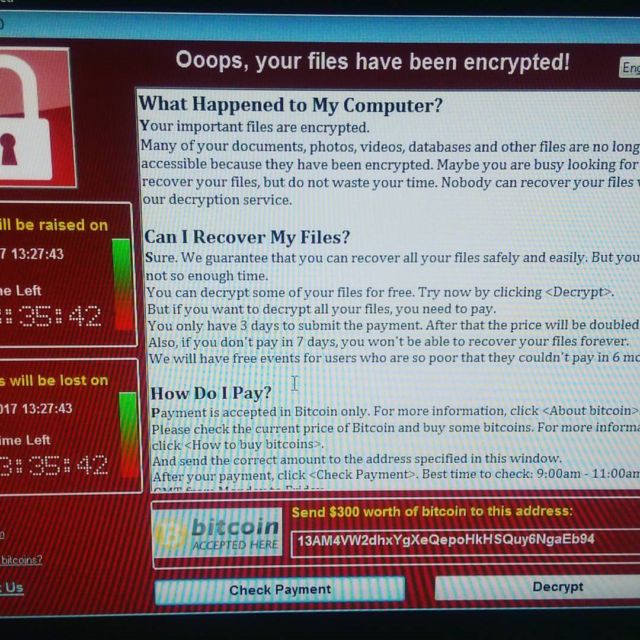
According to a report from the Seattle Times, the dreaded WannaCry ransomware hit a Boeing production plant in Charleston, South Carolina on Wednesday. WannaCry is back, this time it infected some systems belonging to US aircraft manufacturer Boeing. According to a report from the Seattle Times, the dreaded ransomware hit a Boeing production plant in Charleston, South Carolina on […]