 Pierluigi Paganini
 February 21, 2018
Javascript evasion technique – Security Expert Marco Ramilli detailed a fun and innovative way to evade reverse-engineering techniques based on Javascript technology. Understanding the real code behind a Malware is a great opportunity for Malware analysts, it would increase the chances to understand what the sample really does. Unfortunately it is not always possible figuring […]
 Pierluigi Paganini
February 21, 2018
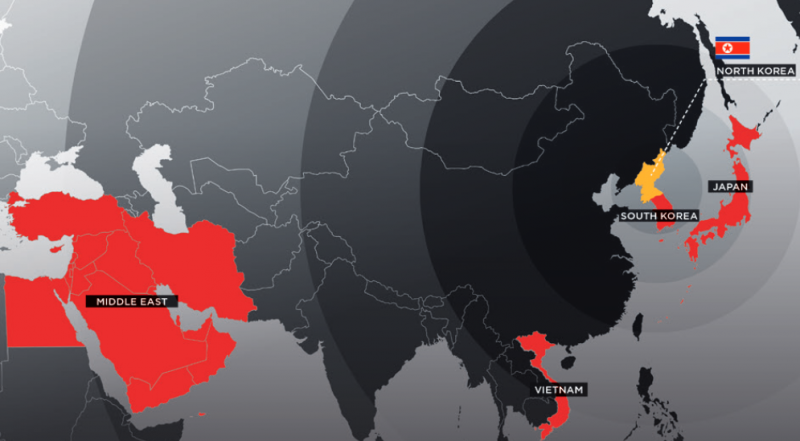
Researchers at FireEye speculate that the APT group tracked as APT37 (aka Reaper, Group123, ScarCruft) operated on behalf of the North Korean government. Here we are to speak about a nation-state actor dubbed APT37 (aka Reaper, Group123, ScarCruft) that is believed to be operating on behalf of the North Korean government. APT37 has been active since at least […]
 Pierluigi Paganini
February 20, 2018
The former NSA hacker and malware researcher Patrick Wardle is back, this time he spotted a new remote access Trojan dubbed Coldroot RAT. The Coldroot RAT is a cross-platform that is targeting MacOS systems and the bad news is that AV software is not able to detect it. The malware acts as a keylogger on MacOS systems prior to […]
 Pierluigi Paganini
February 20, 2018
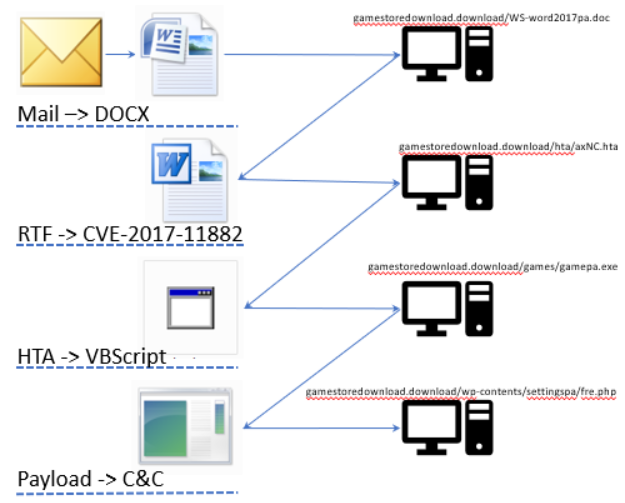
Security researchers at Trustwave spotted a new malicious campaign that uses a multi-stage attack to deploy a password stealer. Researchers at Trustwave have spotted a new malware-based campaign that uses a multi-stage infection to deploy a password stealer malware. Hackers leverage the infamous Necurs botnet to distribute spam emails delivering Microsoft Office documents that embedded malicious macros. DOCX […]
 Pierluigi Paganini
February 18, 2018
Hacker Group Makes $3 Million by Installing Monero Miners on Jenkins Servers A criminal organization has made $3.4 million by compromising Jenkins servers and installing a Monero cryptocurrency miner dubbed JenkinsMiner. “The perpetrator, allegedly of Chinese origin, has been running the XMRig miner on many versions of Windows, and has already secured him over $3 million worth […]
 Pierluigi Paganini
February 17, 2018
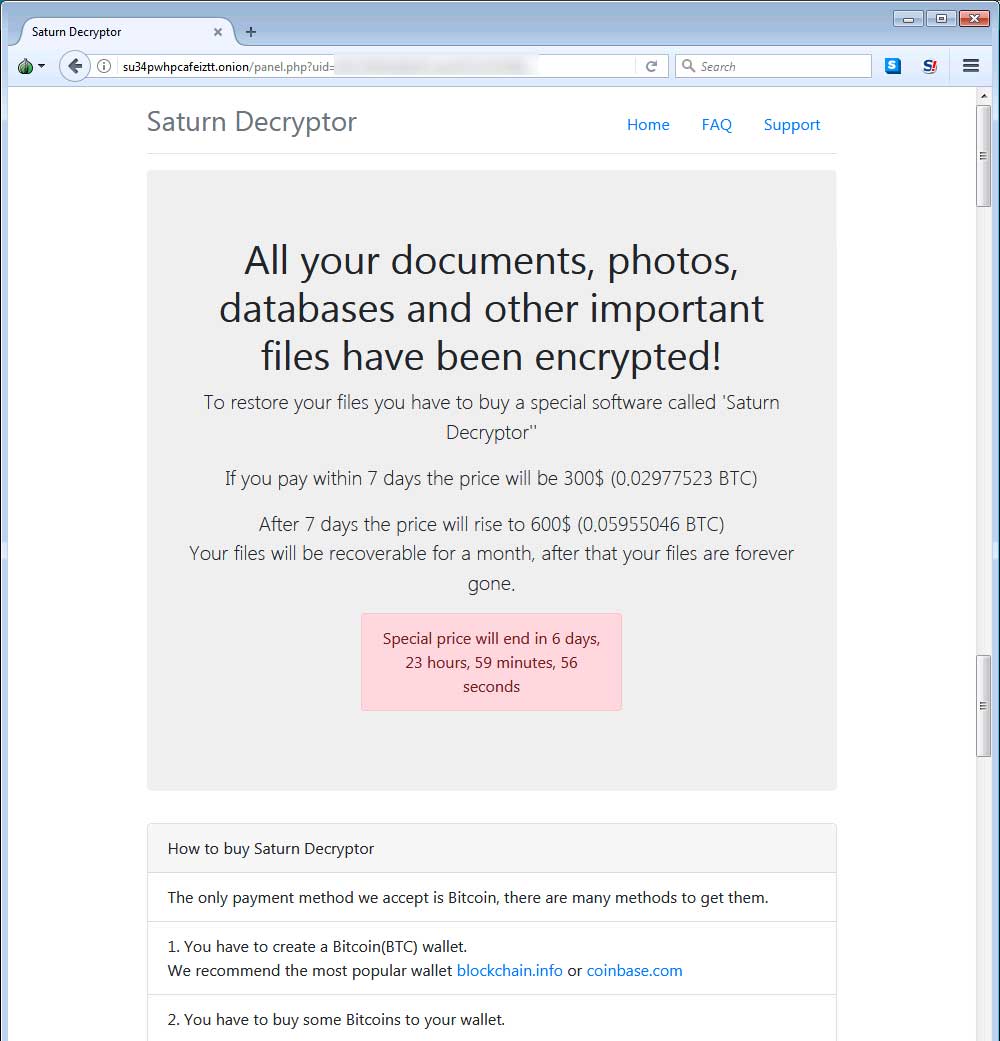
Researchers at the MalwareHunterTeam spotted a new strain of ransomware called Saturn Ransomware, the name derives from the .saturn extension it appends to the name of the encrypted files. Currently, the malware requests victims of $300 USD payment that doubles after 7 days. Once infected a system, the Saturn Ransomware checks if it is running in a […]
 Pierluigi Paganini
February 15, 2018
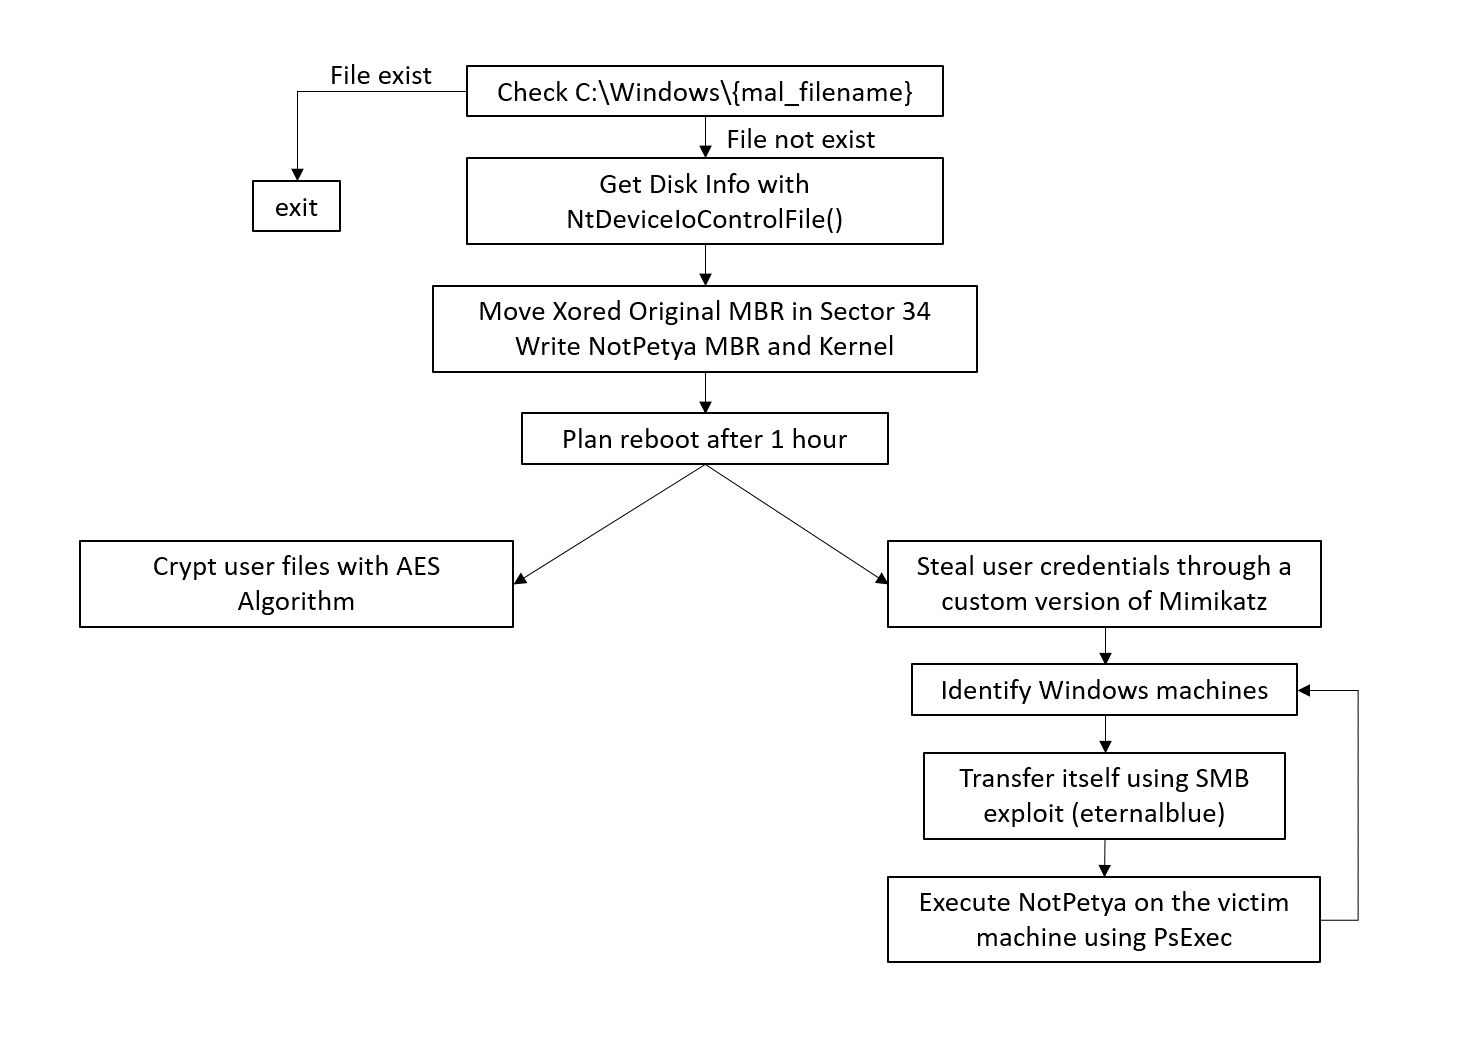
The United Kingdon’s Foreign and Commonwealth Office formally accuses the Russian cyber army of launching the massive NotPetya ransomware attack. The UK Government formally accuses the Russian cyber army of launching the massive NotPetya ransomware attack. The United Kingdon’s Foreign and Commonwealth Office “attributed the NotPetya cyber-attack to the Russian Government.” According to the UK, […]
 Pierluigi Paganini
February 14, 2018
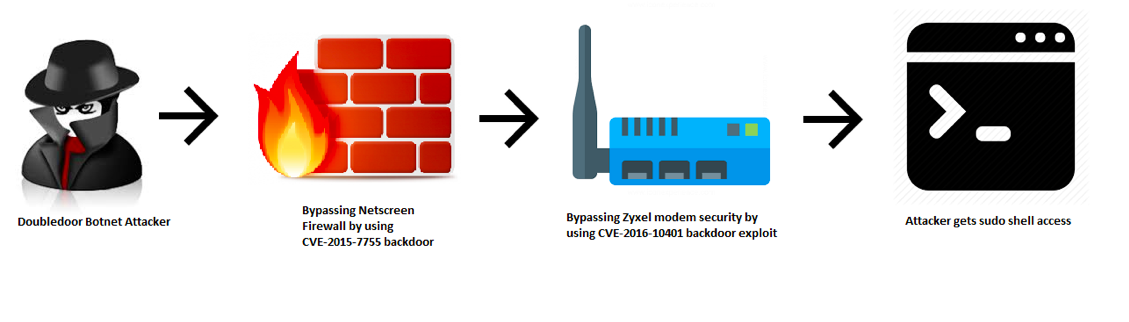
Security researchers spotted a new IoT botnet dubbed DoubleDoor that is able to bypass firewall as well as modem security using two backdoor exploits. IoT devices continue to be a privileged target of cyber criminals, cyber attackers against so-called smart objects has seen a rapid evolution. Security researchers at NewSky Security (NewSky Security) have detected a new IoT botnet […]
 Pierluigi Paganini
February 13, 2018
Security researchers from Trend Micro detected a new variant of the popular AndroRAT Android RAT in the criminal ecosystem. Security experts from Trend Micro reported the availability of a new variant of the popular AndroRAT. The malware was first born in 2012 as a university project, designed as an open-source client/server application to offer remote […]
 Pierluigi Paganini
February 13, 2018
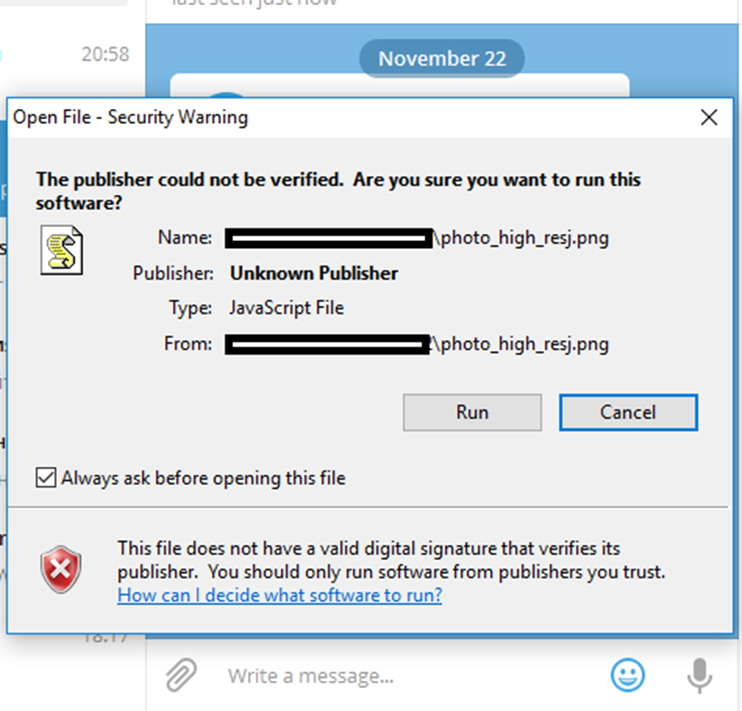
Security researcher Alexey Firsh at Kaspersky Lab last discovered a Telegram zero-day in the desktop Windows version that was exploited in attacks in the wild. Security researcher Alexey Firsh at Kaspersky Lab last discovered a zero-day vulnerability in the desktop Windows version of the popular Telegram instant messaging app. The bad news is that the […]