 Pierluigi Paganini
 March 03, 2017
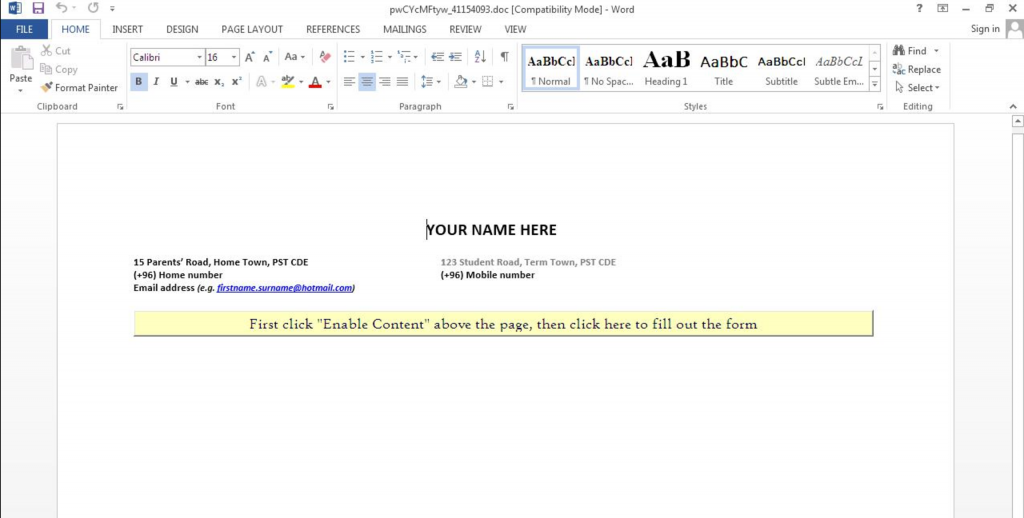
Researchers from Cisco Talos team spotted a new strain of malware that leverages PowerShell scripts to fetch commands from DNS TXT records. Malware researchers at Cisco Talos have published a detailed analysis on a targeted attack leveraging a weaponized Microsoft Word document that is spread in spam emails as an attachment. The malicious code used in the […]
 Pierluigi Paganini
March 02, 2017
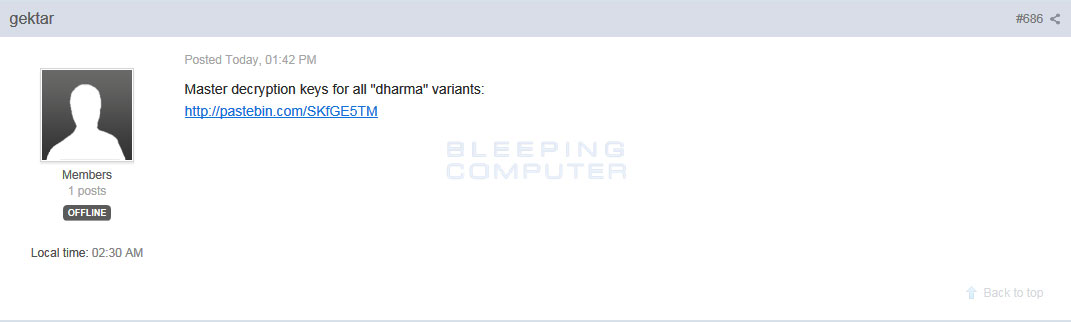
Good news for the victims of the Dharma Ransomware, someone has released the alleged Master Keys on the BleepingComputer.com forums. The alleged Master Keys for the Dharma Ransomware has been released by someone on BleepingComputer.com forums. A member using the online moniker ‘gektar‘ published a post containing a Pastebin link to a header file in C programming […]
 Pierluigi Paganini
February 27, 2017
The Necurs botnet is evolving and recently the experts at BitSight’s Anubis Labs discovered that it was improved to launch DDoS attacks. The Necurs botnet continues to evolve and recently it was used by crooks not only to spread the dreaded Locky ransomware but he was improved to launch DDoS attacks. According to the researchers BitSight’s […]
 Pierluigi Paganini
February 26, 2017
A study commissioned by Siemens revealed that US oil and gas industry is unprepared to mitigate cybersecurity risks in operational technology environments. A new study commissioned by the engineering firm Siemens revealed that oil and gas industry in the United States is largely unprepared to mitigate cybersecurity risks in operational technology (OT) environments. The survey was conducted […]
 Pierluigi Paganini
February 26, 2017
The analysis conducted by Arbor Networks on the Shamoon 2 malware has shed light on the control infrastructure and the infection process. Security researchers from Arbor Networks’ Security Engineering and Response Team (ASERT) have conducted a new analysis of the Shamoon 2 malware discovering further details on the tools and techniques used by the threat […]
 Pierluigi Paganini
February 25, 2017
Apple’s design lab internal development servers was infected by a malware so the company ended its relationship with Supermicro server supplier. It was mid-2016 when Apple’s design lab internal development servers was infected by a malware that was masquerading as a fake firmware patch. In response to the security incident, Apple purged its data centers of […]
 Pierluigi Paganini
February 23, 2017
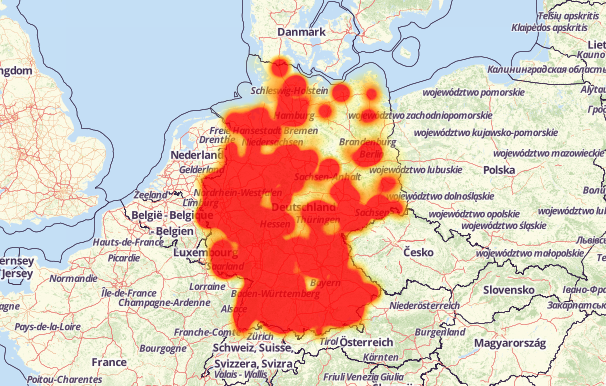
The prosecutor’s office in Cologne and the Federal Criminal Police Office have arrested the alleged mastermind of the MIRAI attack on Deutsche Telekom The agents at the UK National Crime Agency (NCA) have a man that is suspected to be involved with the massive attack on Deutsche Telekom that affected more than 900k routers in […]
 Pierluigi Paganini
February 23, 2017
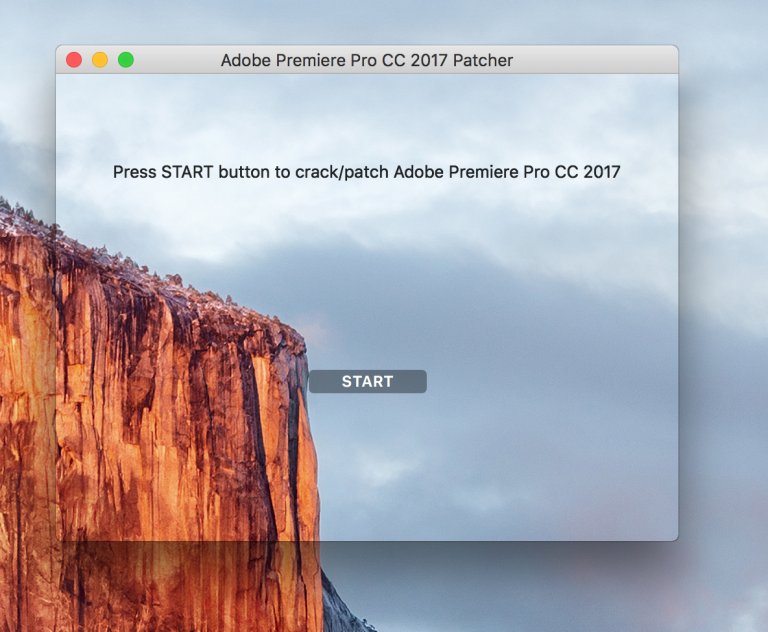
A few days ago experts at antivirus firm ESET spotted a new MacOS ransomware, a rarity in the threat landscape, but it has a serious problem. Malware experts from antivirus vendor ESET have discovered a new file-encrypting ransomware, dubbed OSX/Filecoder.E, targeting MacOS that is being distributed through bittorrent websites.“Early last week, we have seen a new ransomware campaign for […]
 Pierluigi Paganini
February 21, 2017
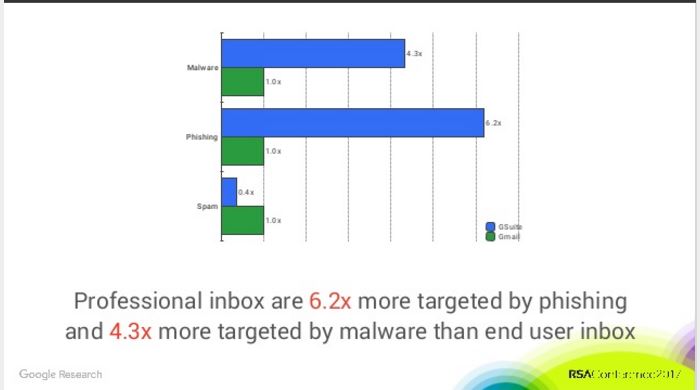
At the RSA security conference in San Francisco, the experts at Google Research explained that Corporate email addresses are privileged targets for hackers. At the RSA security conference in San Francisco, the experts at the Google Research team at the Google Research team have shared the results of an interesting study on cyber attacks against emails accounts. Corporate […]
 Pierluigi Paganini
February 21, 2017
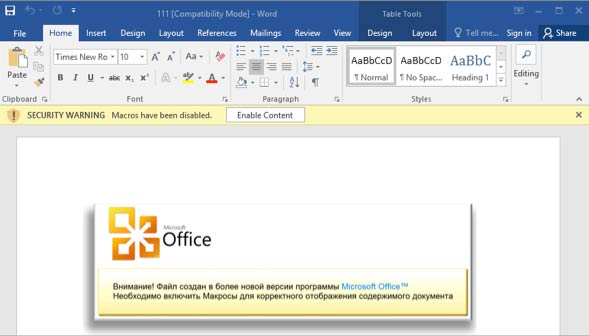
Security firm CyberX uncovered the Operation Bugdrop, a cyber espionage campaign that mostly targeted Ukrainian organizations. Researchers at Security firm CyberX have discovered a cyber espionage campaign that siphoned more than 600 gigabytes from about 70 targets in several industries, including critical infrastructure and news media. The list of targets includes: A company that designs […]