 Pierluigi Paganini
 November 17, 2016
CryptoLuck ransomware is a new strain of malware discovered by the researcher Kafeine, that is being distributed via the RIG-E exploit kit. The notorious researcher Kafeine has spotted a new strain of ransomware dubbed CryptoLuck. The malware leverages DLL hijacking and exploits the legitimate GoogleUpdate.exe executable to infect computers. The ransomware appends the .[victim_id]_luck extension to the encrypted […]
 Pierluigi Paganini
November 15, 2016
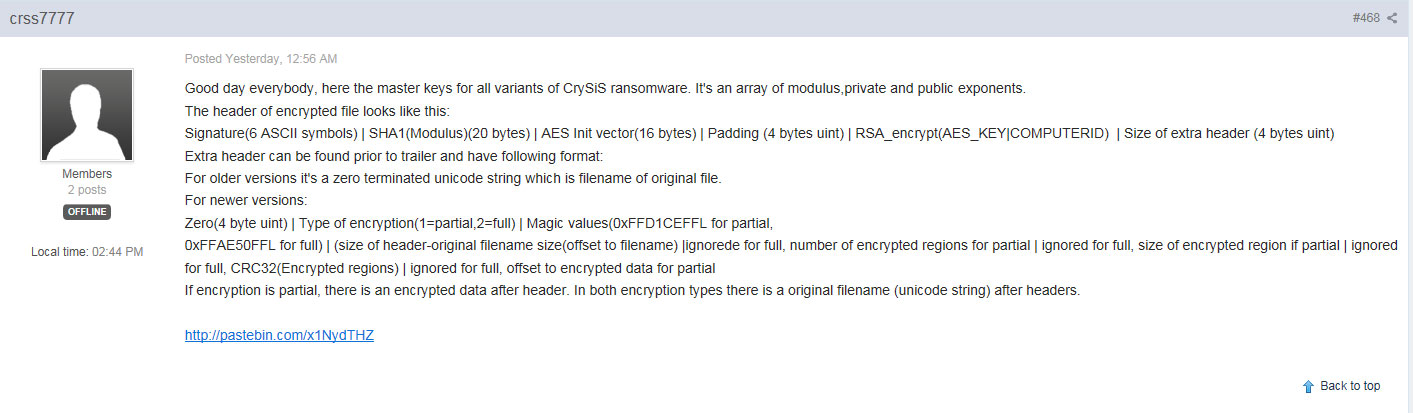
The decryption keys for the CrySis ransomware were posted online on the BleepingComputer.com forum by a user known as crss7777. Good news for the victims of the CrySis ransomware, on Sunday the master decryption keys were released to the public. Security experts from Kaspersky Lab have already included the decryption keys in the Rakhni decryptor allowing victims […]
 Pierluigi Paganini
November 11, 2016
Telecrypt ransomware is a new malware that abuses the instant messaging service Telegram for command and control (C&C) communications. Security experts from Kaspersky Lab have spotted a new Ransomware, called Telecrypt (Trojan-Ransom.Win32.Telecrypt), that abuses the Telegram instant messaging service for communications with command and control (C&C). The Delphi-written Trojan, which is currently targeting only Russian users, it exploits […]
 Pierluigi Paganini
November 08, 2016
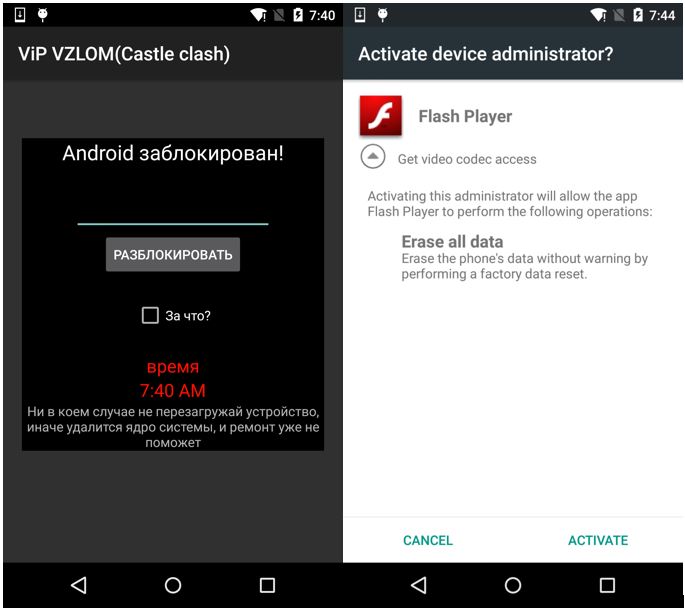
Security experts from Cheetah Mobile Security Research Lab published an interesting Technical analysis of the mobile variant of the Locker virus. Blatant malicious behavior of the Locker virus The Locker virus can easily be identified by its blatant malicious behavior. Here are the tell-tail signs: Windows appear on the top of the home screen that […]
 Pierluigi Paganini
November 06, 2016
Security researchers at Skycure have discovered a new commodity Android Spyware, dubbed Exaspy, targeting high-level executives. While in many countries the number of Smartphone and Tables is greater of desktop PC, new threats are targeting mobile devices. Researchers at Skycure have discovered a new strain of Android spyware, dubbed Exaspy, that has been used in targeted attacks against […]
 Pierluigi Paganini
November 05, 2016
At the Black Hat Europe 2016 two security researchers devised undetectable attacks that could be used to hack PLC systems avoid being detected. Security researchers at the Black Hat Europe 2016 have presented a new attack method that could be used to hack programmable logic controllers avoid being detected. programmable logic controllers are essential components for […]
 Pierluigi Paganini
November 04, 2016
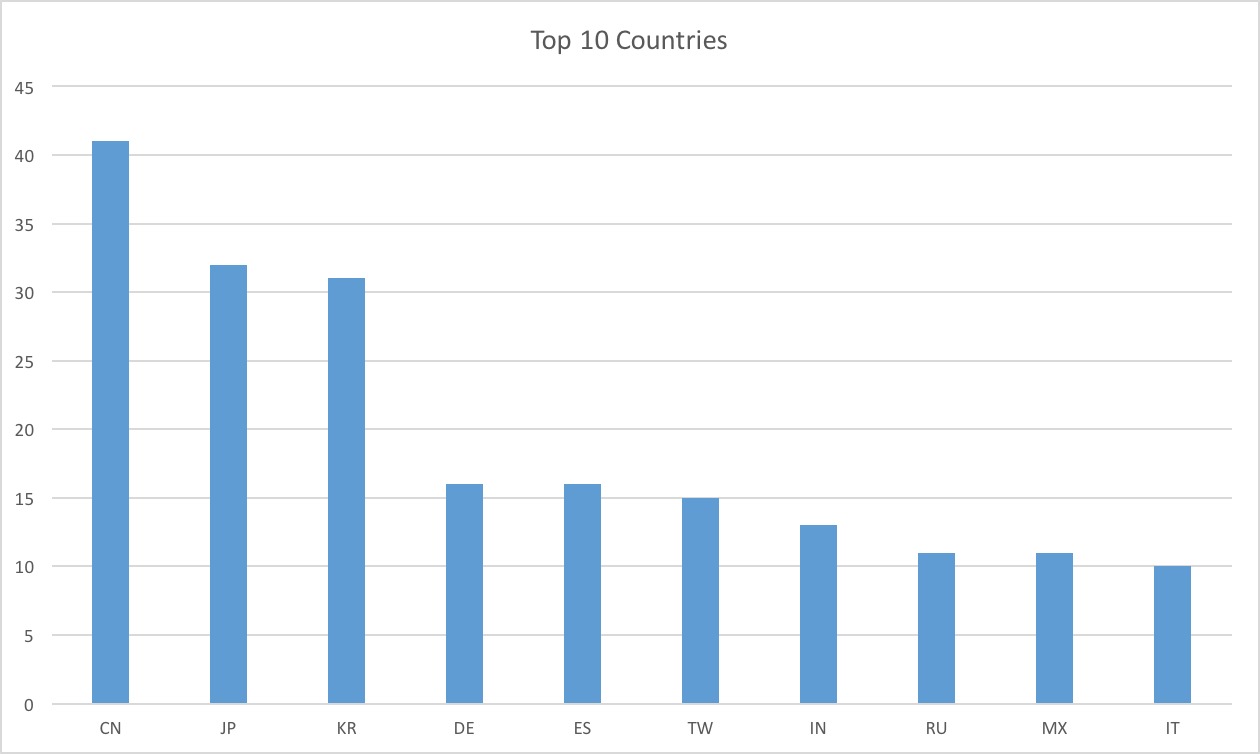
Switzerland’s attorney general has confirmed to have investigated the presence of spyware in a venue that also hosted talks on Iran’s nuclear negotiations. Swiss officials confirmed to have found an espionage malware in the computer equipment at Geneva venue, a five-star hotel (believed to be Hotel Président Wilson) that has hosted sensitive talks including Iranian nuclear negotiations. […]
 Pierluigi Paganini
October 31, 2016
The ShadowBrokers hacker group leaked a fresh dump containing a list of servers that were hacked by the NSA-linked group known as Equation Group. The notorious Shadow Brokers hacker group has posted a fresh dump containing a list of servers that were hacked by the NSA-linked group known as Equation Group. The hackers disclosed the […]
 Pierluigi Paganini
October 30, 2016
According to a study published by the independent anti-virus testing outfit AV-TEST, the number of malicious search engine results has been increasing. The vast majority of the Internet users blindly trust data provided in response to their queries to the search engines. Actually, search engine results are increasingly poisoned with malicious links, the experts noticed a […]
 Pierluigi Paganini
October 29, 2016
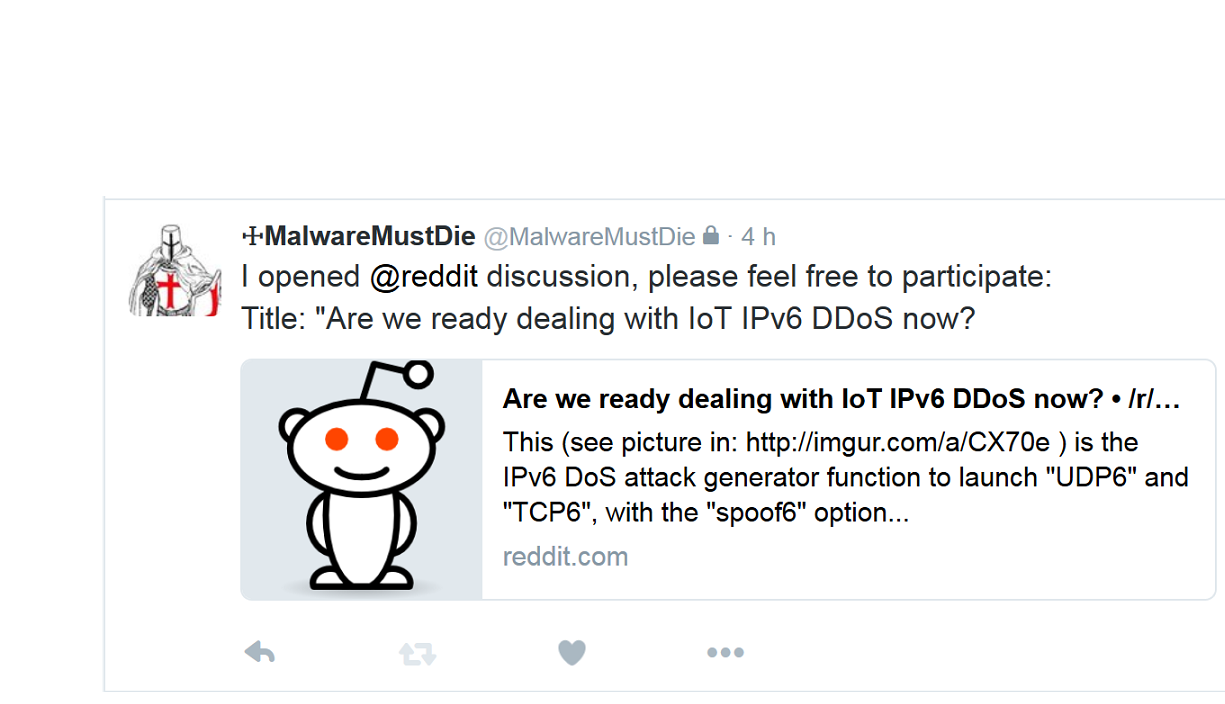
Exclusive: The security researcher MalwareMustDie has found a new Linux/IRCTelnet malware– made in Italy – that aims IoT botnet connected by IRC and Telnet. It is able to generate an IPv6 DDoS and performing NEW dangerous capabilities that Mirai was unable to cover. In a brief interview to Security Affairs @unixfreakjp of MalwareMustDie group explains […]