 Pierluigi Paganini
 September 12, 2016
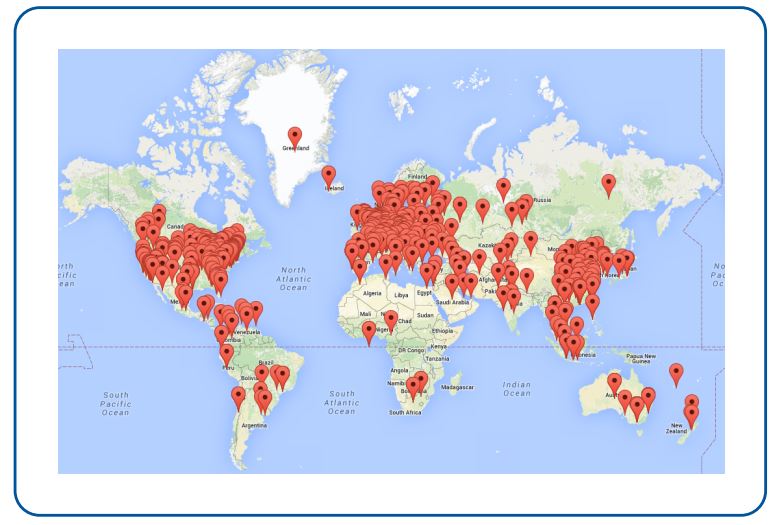
Experts from Sophos discovered Mal/Miner-C, a malware designed to abuse resources of the infected machine to mine Monero (XMR) cryptocurrency. Malware researchers from security firm Sophos have analyzed a new strain of malware detected as Mal/Miner-C that was designed to abuse resources of the infected machine to mine Monero (XMR) cryptocurrency. The experts discovered that the new […]
 Pierluigi Paganini
September 11, 2016
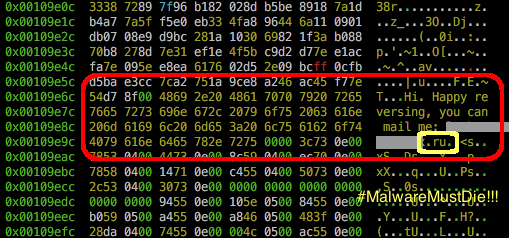
The researcher MalwareMustDie discovered LuaBot, a trojan completely coded in Lua language that is targeting Linux platforms to recruit them in DDoS botnet. Let’s continue our tour in Linux security, focusing on malicious code specifically designed to target such systems. The popular security researcher MalwareMustDie, who recently reported the new ELF trojan backdoorLinux/Mirai, also discovered a […]
 Pierluigi Paganini
September 10, 2016
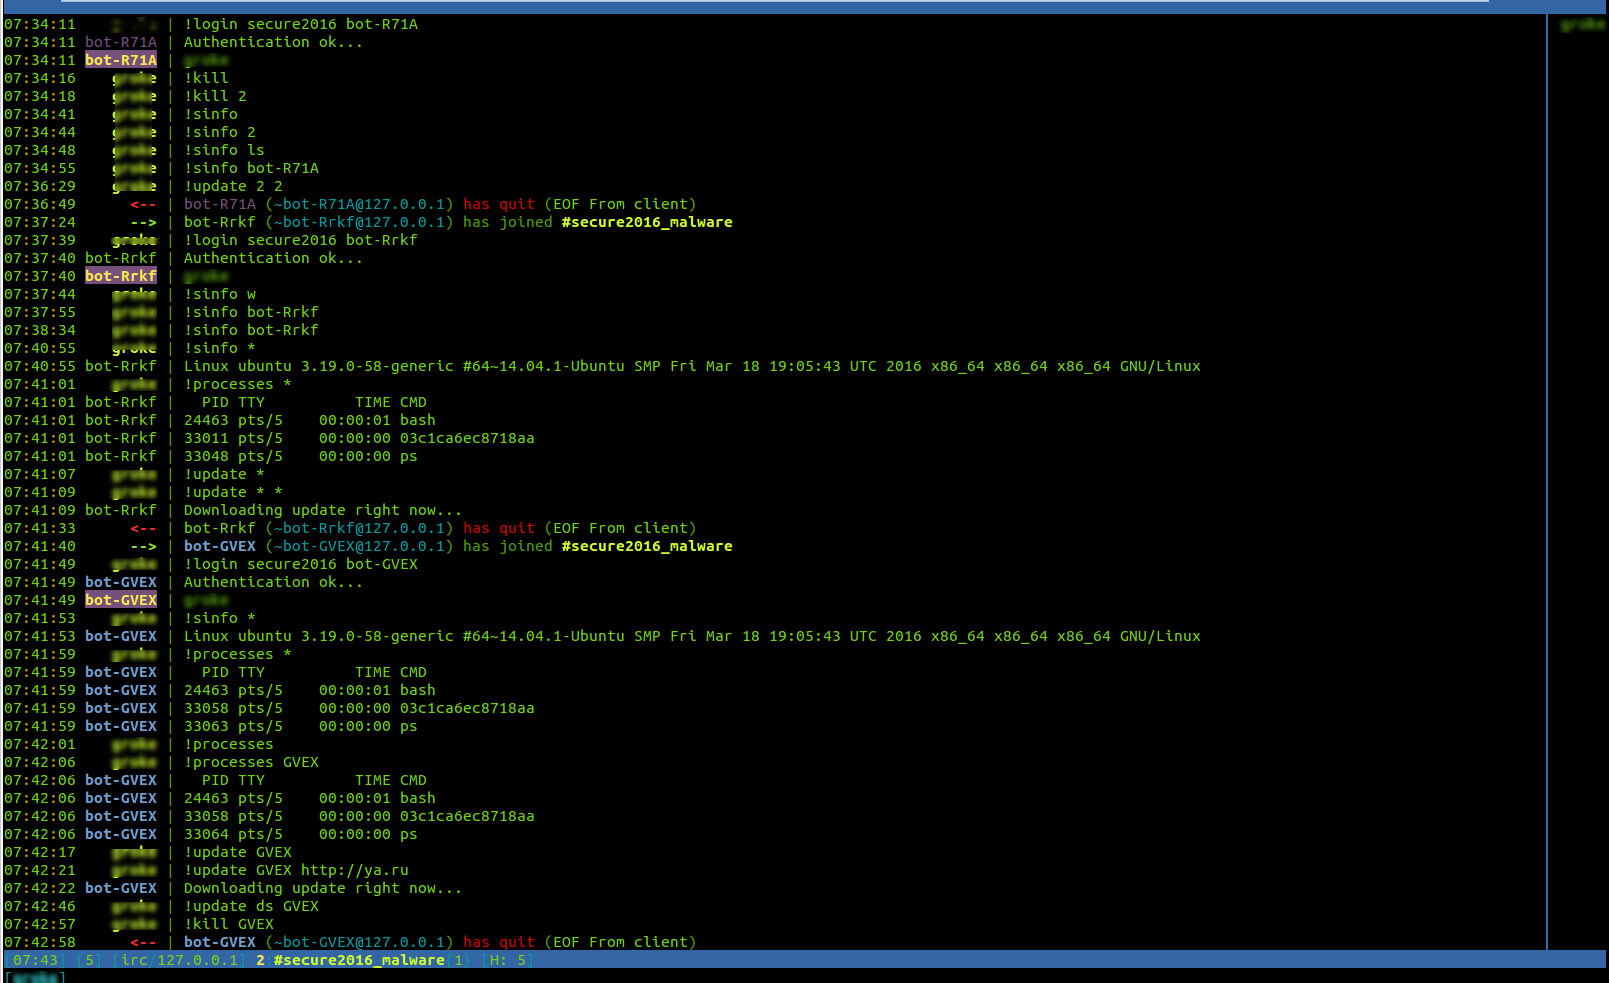
Experts from Dr Web discovered a new Linux Trojan called Linux.BackDoor.Irc.16 that is written in the Rust programming language. It is a prolific period for Vxers working on Linux Trojan, a new strain was recently spotted by experts from Doctor Web. The new Linux Trojan has been named Linux.BackDoor.Irc.16 and is written in the Rust programming language.Rust […]
 Pierluigi Paganini
September 08, 2016
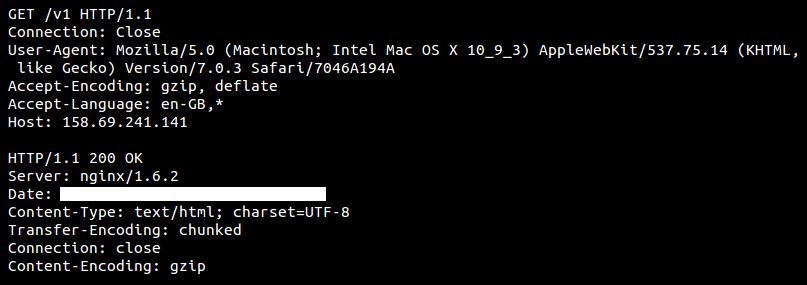
Malware researchers from Kaspersky Lab confirmed the existence of an OS X variant of the Mokes backdoor discovered in January by Kaspersky. Malware researchers from Kaspersky Lab confirmed the existence of an OS X variant of a recently discovered family of cross-platform backdoors. The backdoors family was named Mokes and a strain of malware was […]
 Pierluigi Paganini
September 06, 2016
Security researchers from TrendMicro have published an interesting analysis on the Linux Umbreon rootkit, a new malware developed by a Pokemon-fan VXer. Malware researchers from TrendMicro have obtained samples of a new strain of Linux rootkit from one of its trusted partners. The new rootkit family was called Umbreon (ELF_UMBREON family), from the name of one of […]
 Pierluigi Paganini
September 05, 2016
Experts from MalwareMustDie spotted a new ELF trojan backdoor, dubbed ELF Linux/Mirai, which is now targeting IoT devices. Experts from MalwareMustDie have analyzed in August samples of a particular ELF trojan backdoor, dubbed ELF Linux/Mirai, which is now targeting IoT devices. The name of the malware is the same of the binary,”mirai.*,” and according to the […]
 Pierluigi Paganini
September 04, 2016
Two Hong Hong government departments were targeted by Chinese hackers belonging the APT3 group just before the legislative elections. Security experts from FireEye have discovered a new cyber espionage campaign launched by the Chinese APT3 group against Hong Kong Government before upcoming parliamentary elections that are to be held today September 4. The hackers targeted two Hong Kong government departments […]
 Pierluigi Paganini
September 02, 2016
It has happened again, Mac users who were looking for the BitTorrent client Transmission might have been infected by the OSX/Keydnap malware. Security experts from ESET have spotted the popular BitTorrent client called Transmission distributing Mac malware called OSX/Keydnap that is used to steal the content of OS X’s keychain and maintain a permanent backdoor on victims’PC. […]
 Pierluigi Paganini
September 01, 2016
SWIFT discloses more attacks against banks worldwide, pressures banks on security and urged member banks to implement the new SWIFT software by November 19. In the last months, a worrisome string of attacks against banks worldwide through the SWIFT system has alarmed the banking industry. The so-called “SWIFT hackers” have conducted multiple cyber attacks against […]
 Pierluigi Paganini
September 01, 2016
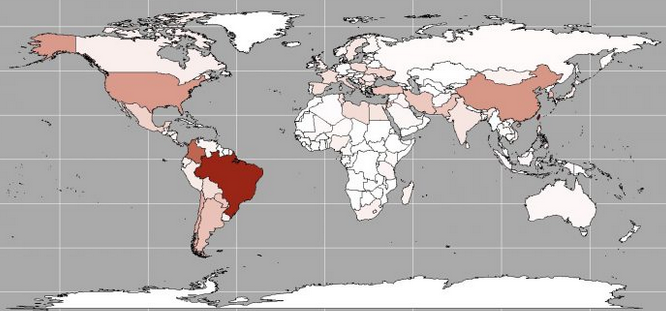
A joint research conducted by Level 3 Communications and Flashpoint allowed the identification of a million devices infected by the BASHLITE malware. Do you remember the BASHLITE malware? It was a strain of malware (also known as Lizkebab, Torlus and Gafgyt) detected by experts at Trend Micro shortly after the public disclosure of the ShellShock bug. The BASHLITE malware includes the […]