 Pierluigi Paganini
 August 17, 2016
Security experts from Fidelis firm spotted a new version of the Vawtrak banking Trojan that includes significant improvements such as the SSL pinning. Malware researchers from security firm Fidelis have spotted a new strain of the infamous Vawtrak banking Trojan that leverages on a DGA mechanism to generates .ru domains with a pseudorandom number generator (PRNG) […]
 Pierluigi Paganini
August 17, 2016
According to the popular whistleblower Edward Snowden, the hack of the NSA Equation Group may be a Russian response to the US. The public auction of stolen NSA exploits and hacking tools may be the response of the Russian Government to the US Government, which is blaming it for the DNC hack. This is also […]
 Pierluigi Paganini
August 16, 2016
A group of hackers claims to have hacked the NSA Equation Group, it is selling hacking tools and exploits in online auction. Security experts discussed several times about potential effects of the militarization of the cyberspace. Government-built malware and cyber weapons may run out of control, cyber weapons and hacking tools developed by nation-state hackers […]
 Pierluigi Paganini
August 16, 2016
Hackers that breached Oracle MICROS systems have infected systems of other five PoS vendors that supply hundreds of thousands of companies in the US. Last week the systems of the Oracle MICROS payment terminals division have been infected by a malware, MICROS payment terminals are installed in the most important retail chains worldwide as well […]
 Pierluigi Paganini
August 14, 2016
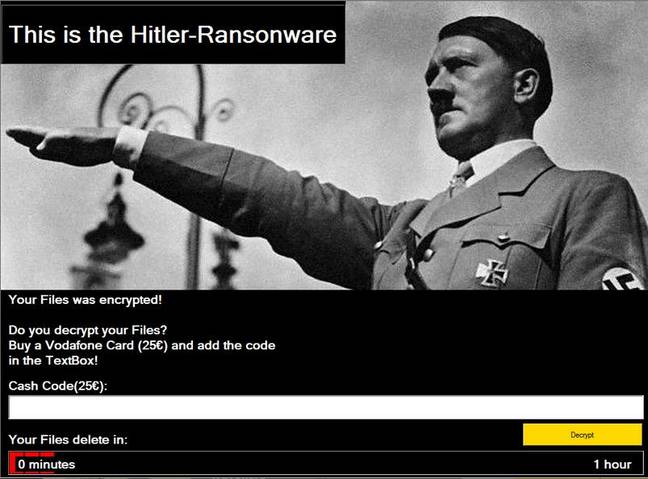
Security experts detected and analyzed a new threat, the Hitler ransomware, that doesn’t encrypt files but simply deletes them. Ransomware is one of the most dreaded threats for Internet users and a profitable business for crooks. In the last months, we have seen a number of malware belonging to this category, one of the most recent is […]
 Pierluigi Paganini
August 13, 2016
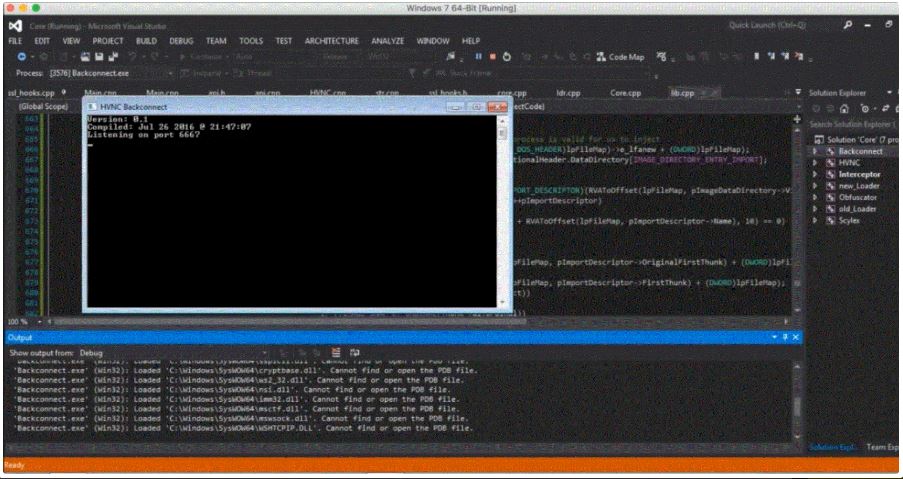
Experts from Heimdal security firm discovered a new crimeware kit, the Scylex malware kit, that aims to provide Zeus-grade Capabilities. Security experts from the Heimdal security firm have discovered a new DIY financial crime kit offered for sale on a notorious malicious hacker forum on the dark web called Lampeduza. The new crime kit, dubbed Scylex malware kit, […]
 Pierluigi Paganini
August 09, 2016
The systems of the Oracle MICROS payment terminals division have been infected by a malware, systems worldwide are potentially at risk. The hack that I’m going to tell you could have a serious and a huge impact, the systems of the Oracle MICROS payment terminals division have been infected. MICROS is among the top three […]
 Pierluigi Paganini
August 08, 2016
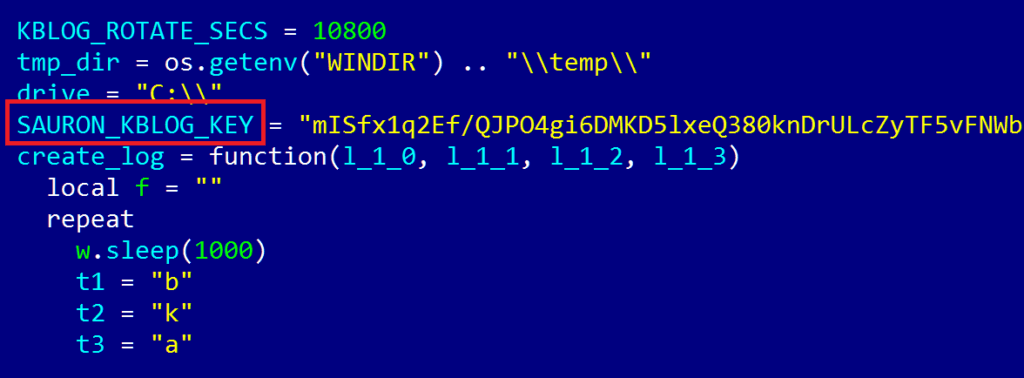
Experts spotted a previously unknown APT group dubbed Strider or ProjectSauron that carried out surgical cyber-espionage attacks against targets worldwide. A previously unknown hacking group variously dubbed ‘Strider’ or ‘ProjectSauron’ has been conducting a surgical cyber espionage campaign against targets in Russia, Belgium, China, Iran, Sweden, and Rwanda. According to experts from Symantec, the Strider crew […]
 Pierluigi Paganini
August 08, 2016
The experts from the Irish Garda are investigating a malware-based attack that forced it to shut down its data systems. No system was breached. The Garda Síochána, the national police service of Ireland, was forced to shut down its data systems in response to a malware-based attack. The Ireland’s national police put in place the emergency […]
 Pierluigi Paganini
August 06, 2016
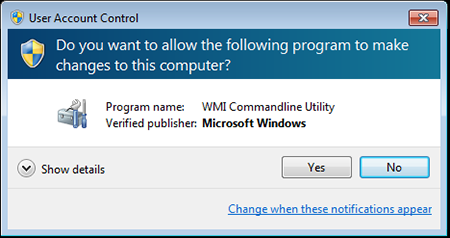
Experts from Dr Web discovered a new PoS malware dubbed Kasidet that can bypass User Account Control (UAC) by posing as a legitimate Microsoft application. A new strain of PoS malware is in the wild, experts from security firm Doctor Web named it Trojan.Kasidet.1 and it is able to bypass defense mechanism such as the Microsoft […]