 Pierluigi Paganini
 July 28, 2016
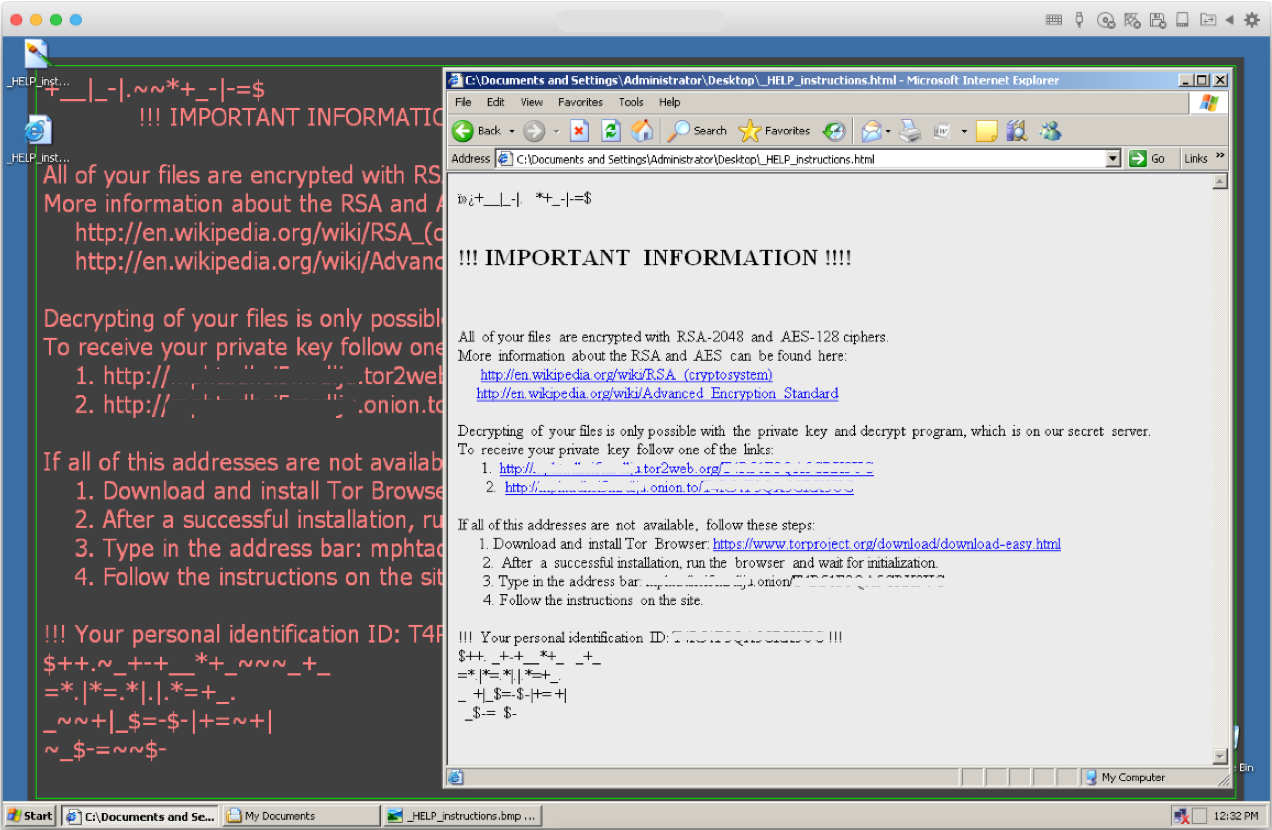
A new ransomware campaign relies on a Locky variant that is distributed through JavaScript that includes the binary of the threat itself. Locky is one of the most infamous threats of the ransomware family and according to the experts it is in continuous evolution. The threat has been using JavaScript attachments as a distribution mechanism, but most […]
 Pierluigi Paganini
July 26, 2016
The No More Initiative aims to spread information about ransomware and the risk of exposure,providing suggestions to avoid falling victim to the threat. A joint operation conducted by the Europol with police and cyber security firms worldwide aims to tackle the Ransomware threat. It has been estimated that the ransomware victims tripled in the first quarter of […]
 Pierluigi Paganini
July 23, 2016
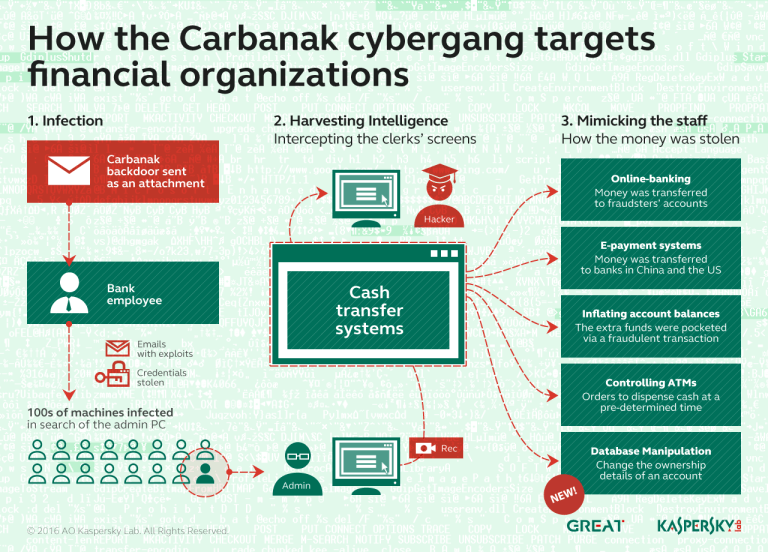
The security expert Brian Krebs investigated the links between the Carbanak cybercrime gang and the Infocube security firm. Today I want to share with you the findings of an investigation of the popular cyber security expert Brian Krebs. This time, Krebs investigated the link between a cybercrime gang and a security firm. The security company […]
 Pierluigi Paganini
July 21, 2016
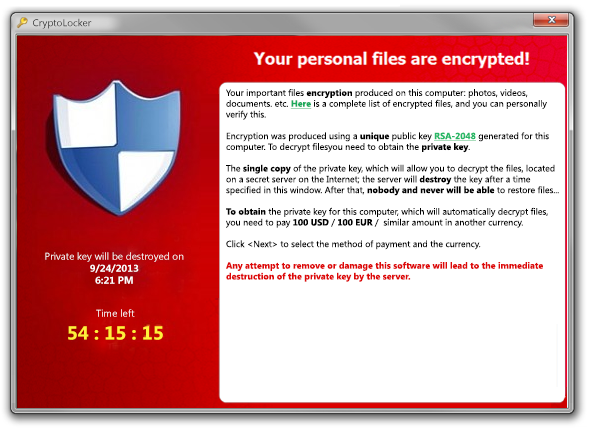
Recently, Reuters reported that the FBI sent an urgent confidential ‘Flash’ message to businesses and organizations to warn them about ransomware. Sponsored Content It is that dangerous. This is a new version of the ransom note, a form of malware that interferes with access to user files and data by encrypting it. Those running the […]
 Pierluigi Paganini
July 21, 2016
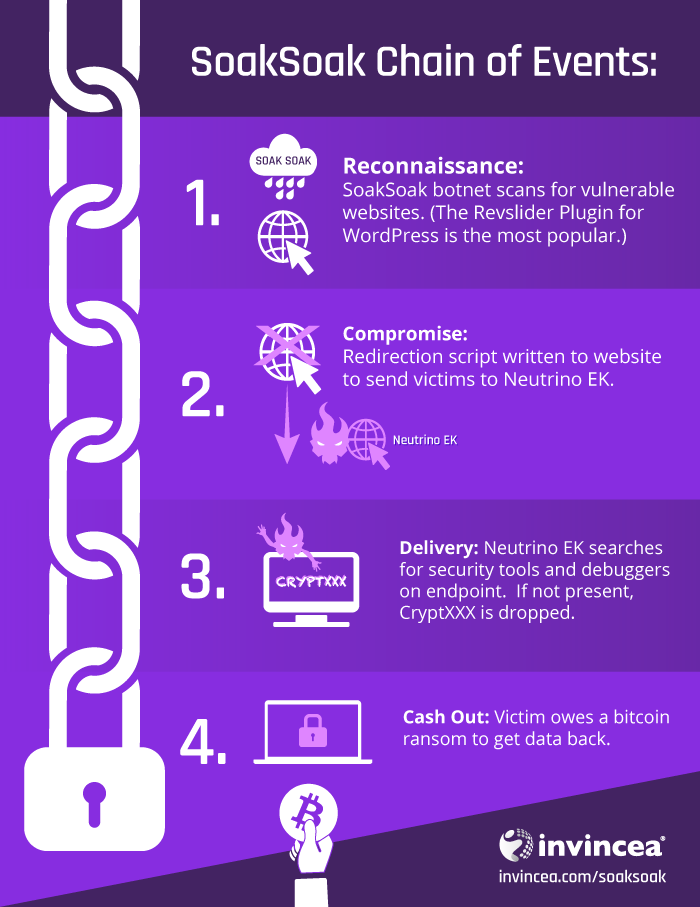
A large number of business websites have been compromised by the SoakSoak gang to deliver ransomware. Security experts from Invincea firm have discovered that a large number of websites were recruited by the SoakSoak botnet to deliver CryptXXX malware. The list of compromised sites is long and includes the tourism website for Guatemala and the do-it-yourself project […]
 Pierluigi Paganini
July 20, 2016
Delilah is the first extortion trojan that spies on victims and collects information to force them in doing malicious activities from inside. Delilah is a strain of malware developed to extort victims into stealing insider data, it was first discovered on crime forums by the Israeli intelligence firm Diskin Advanced Technologies. Deliah is not distributed in […]
 Pierluigi Paganini
July 19, 2016
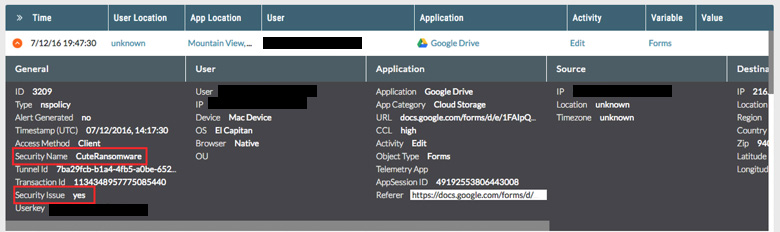
A newly strain of ransomware dubbed cuteRansomware leverages on a Google Doc to host the decryption key and command-and-control features. A recently discovered strain of ransomware, dubbed cuteRansomware, shows that your enterprise isn’t the only one thinking about cloud transition. Modern day hackers are loving the Cloud too. The cuteRansomware was discovered by Netskope security firm which observes an increase […]
 Pierluigi Paganini
July 17, 2016
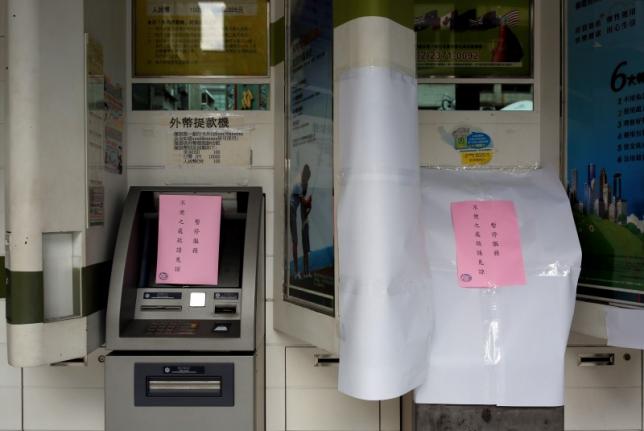
Taiwanese law enforcement agencies are investigating malware-based attacks against ATMs of a national bank that resulted in a $2 million theft. Law enforcement in Taiwan investigating the attacks against ATMs of a major nations bank, the Taiwan’s First Bank. Crooks used a malware to withdraw more than $2 million from dozens of ATMs in the country, it […]
 Pierluigi Paganini
July 15, 2016
Operators behind the Neutrino EK have added the code to exploit an Internet Explorer flaw that was recently patched with the release of the MS16-053. Operators behind the infamous Neutrino EK have recently added the code to exploit an Internet Explorer vulnerability that was patched with the release of the MS16-053 security bulletin. The MS16-053 bulletin patched […]
 Pierluigi Paganini
July 15, 2016
The Labs team at SentinelOne recently discovered a sophisticated malware dubbed Furtim specifically targeting at least one European energy company. In May of this year, security researcher Yotam Gottesam with enSilo, began unraveling a mystery that continues to unravel. First reported by FireF0X, a self-proclaimed “ex-malware analyst” located in the Russian Federation, the Furtim malware […]