 Pierluigi Paganini
 July 15, 2015
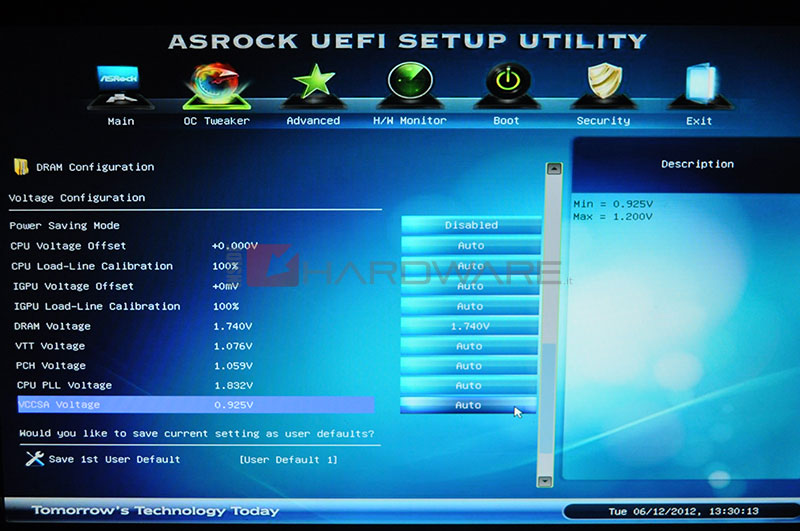
Documents leaked online after the Hacking Team hack revealed that the company used a UEFI BIOS rootkit to gain persistence for its spyware software. The recent data breach suffered by the surveillance firm Hacking Team is shocking the IT security industry, the hackers leaked company emails, source codes and contracts revealing uncomfortable truths. Security experts mainly […]
 Pierluigi Paganini
July 15, 2015
The Hacking Team CEO David Vincenzetti announced that the popular surveillance company will be back to business vert soon, but experts have many doubts. After the embarrassing data breach suffered by the Hacking Team, the surveillance company plans to rebuild the “empire”. The hackers likely haven’t stolen the entire intellectual property of the firm, which […]
 Pierluigi Paganini
July 14, 2015
Security researchers at Symantec have analyzed Seaduke, a sophisticated Trojan used by threat actors behind the “Duke” malware family. Security experts at Symantec security firm have analyzed the Trojan.Seaduke, a malware that was used by the APT group behind the Duke espionage campaigns that targeted numerous government organizations worldwide. The Seaduke has many similarities with other […]
 Pierluigi Paganini
July 14, 2015
Following the Hacking Team data breach, the security researchers discovered the third Adobe Flash Player zero-day vulnerability. A third Adobe Flash Player zero-day has been discovered since the HackingTeam breach. Thanks to the breach of the Hacking Team‘s private files, the third Adobe Flash zero-day has been made publicly accessible. “After two Adobe Flash player zero-days disclosed […]
 Pierluigi Paganini
July 12, 2015
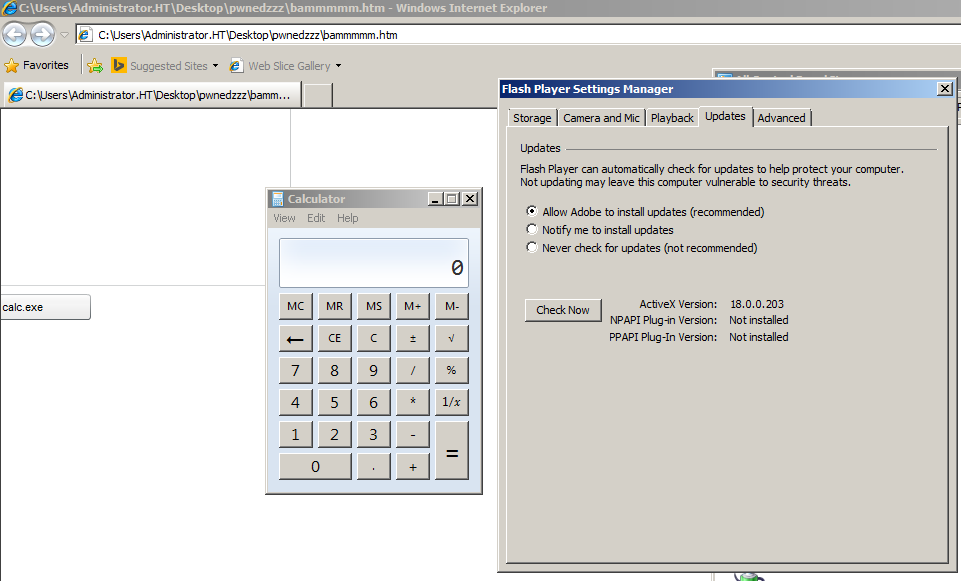
Following the Hacking Team data breach, yet another Adobe Flash Player zero-day vulnerability has been found actively exploited in-the-wild. Another Flash Zero-Day: CVE-2015-5122 Yet another Adobe Flash Player zero-day has been found actively exploited in-the-wild. Thanks to the breach of the HackingTeam’s private files, another Adobe Flash zero-day has been made publicly accessible and hackers […]
 Pierluigi Paganini
July 12, 2015
Security Researchers at Trend Micro have discovered a second Zero-Day Vulnerability that arises from Hacking Team cyber attack. Just Three days ago, Adobe released a new version of Flash to patch the zero-day vulnerability that was disclosed as part of the Hacking Team hack. Security experts at Trend Micro confirmed that the Adobe Flash vulnerability […]
 Pierluigi Paganini
July 08, 2015
Hackers are using a new search engine poisoning method to circumvent Google’s page ranking-algorithms, the technique relies on PDF documents. Researchers from Sophos discovered the new search poisoning method used to circumvent cloaking-detection mechanisms implemented by Google. The experts found hundreds of thousands of unique PDF documents per day implementing the poisoning technique. The term cloaking indicates the […]
 Pierluigi Paganini
July 06, 2015
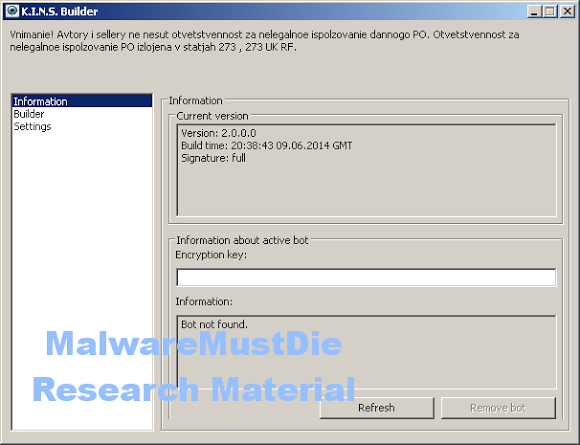
Researchers at MalwareMustDie group have discovered a KINS Malware builder leaked online, it is easy to predict a rapid diffusion of the banking trojan. Security experts at the MalwareMustDie revealed that the source code of the popular KINS malware was leaked online. Early 2013, experts at RSA discovered traces the banking trojan named KINS by analyzing the offer for […]
 Pierluigi Paganini
July 04, 2015
Security researcher discovered a strain of the Kovter trojan that has been updating Flash Player and Internet Explorer to prevent further infections. The French security expert Kafeine have discovered a new strain of the Kovter malware noticing that the instance of the malicious code he was analyzing was attempting to download the latest version of the Flash […]
 Pierluigi Paganini
July 02, 2015
FBI has published the lists of most wanted hackers, the rewards for their capture reach $4.2 million. They have stolen hundreds of millions of dollars. Cybercrime represents one of the most serious threat to Governments and private industries worldwide, law enforcement hunt down this emerging class of criminals who are able to influence the social […]