


 Pierluigi Paganini
 May 22, 2015
Security experts at AppRiver firm have discovered a malicious campaign that is distributing a strain of ransomware via SVG files. Researchers at the AppRiver security firm have uncovered a malicious campaign that is distributing a strain of ransomware by exploiting SVG files. The SVG (Scalable Vector Graphics) is an XML-based vector image format for two-dimensional graphics […]
 Pierluigi Paganini
May 22, 2015
A security researcher has compiled the Ransomware Removal kit that could be used in the process of responding to ransomware infections. CryptoLocker, CoinVault, and TeslaCrypt are the names of some of the most dreaded ransomware that infected million of users worldwide. The extortion is a very common practice in the cyber criminal underground and ransomware are […]
 Pierluigi Paganini
May 15, 2015
Oil and gas industry targeted by hackers with a genuine looking windows file, not a malware. The attacks are ongoing for about two years. A unique targeted attack being underway for about two consecutive years exploits Windows file functions that look legitimate and a couple of homemade scripts – but not malware – in order […]
 Pierluigi Paganini
May 13, 2015
Several dozen Imperva Incapsula customers were targeted by a DDoS botnet comprised of tens of thousands of hijacked SOHO routers. Security experts at Incapsula firm spotted a DDoS botnet composed of tens of thousands of malware-infected Small Office / Home Office SOHO routers engaged in application layer HTTP flood attacks. The SOHO routers were infected with a strain […]
 Pierluigi Paganini
May 11, 2015
Patrick Wardle is a former NSA staffer that turned to a security researcher, the expert explained that his main concern is that MAC OS X security tools in the market are trivial and easy to bypass. One of the most known applications in Macs its Gatekeeper, but Patrick says that Gatekeeper can be easily misguided […]
 Pierluigi Paganini
May 08, 2015
Malware developers have presented two proof-of-concept malware, a rootkit and a keylogger, which exploit the GPU of the infected host. Malware authors always demonstrate a great creativity and the ability to propose even more effective solutions, recently developers have published two strains of malware, Jellyfish rootkit and the Demon keylogger, that implement an unusual way to run on a victim’s […]
 Pierluigi Paganini
May 06, 2015
Canadian mobile users were targeted by the latest variant of the Koler Android mobile ransomware after visiting websites proposing adult content. Once again, visitors of websites proposing adult content are targeted by cyber criminals. Last week a malvertising campaign hit visitors of the adult website XHamster, now Canadian Internet users victims were targeted by a […]
 Pierluigi Paganini
May 03, 2015
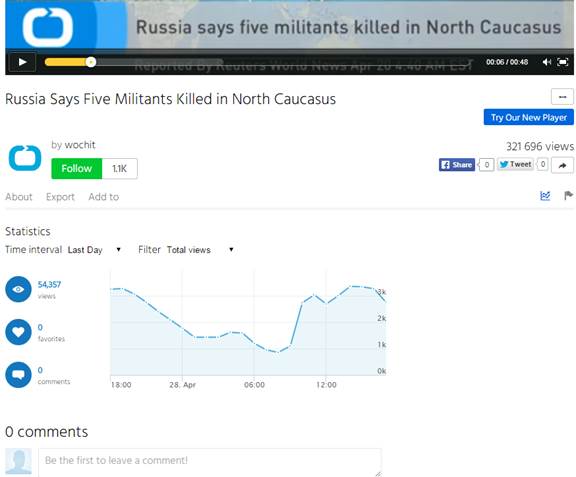
Experts at Trustwave observed a group of cyber criminals helping spread pro-Russia propaganda by inflating video views with a malvertising campaign. Security experts at Trustwave have discovered a botnet, originally designed for malvertising purpose, used redirect unaware users to view some pro-Russian videos on the website DailyMotion. The event is very interesting due to the political motivation […]
 Pierluigi Paganini
May 02, 2015
The sophisticated Mumblehard spamming malware infects thousands of Linux and FreeBSD servers going under the radar for at least five years. In the last seven months, several thousand Linux and FreeBSD machines have been infected with a sophisticated malware dubbed Mumblehard. The infected machines were part of a botnet used, in the last five years, to […]
 Pierluigi Paganini
May 01, 2015
Chinese Antivirus vendor Qihoo submitted products specifically tuned for the major testing labs, while was offering something different to its users. The news is disconcerting, the Chinese security firm Qihoo (CHEE-hoo) 360, is providing to its hundreds of millions of users a product that differs from the one the it has submitted to the major testing […]







