


 Pierluigi Paganini
 October 17, 2014
Two researchers analyzed Smart meters widely used in Spain and discovered that can be hacked by attackers to harm the overall National power network. Internet of things devices are becoming a privileged target of cyber criminals, recently Akamai disclosed the existence of the Spike botnet which used by bad actors to run DDoS attacks through desktops and IoT devices. Another report issued by the same vendor […]
 Pierluigi Paganini
October 15, 2014
Last ICS-CERT MONITOR report reveals that hackers had access to the systems of an unnamed manufacturing organization for several months. According to the ICS-CERT MONITOR report, which summarizes the Industrial Control Systems Cyber Emergency Response Team’s (ICS-CERT) activities between May – August 2014, threat actors had access to the systems of an unnamed manufacturing organization for […]
 Pierluigi Paganini
October 14, 2014
A security expert defined a new attack technique dubbed Reflected File Download that allows to serve a ‘Zero-Day’ Worm without possibility of defense. The security expert Oren Hafif has invented a new attack technique dubbed Reflected File Download (RFD) that could be adopted to hack victim’s computer when he tries and logs in to popular and trusted website like Google and […]
 Pierluigi Paganini
October 10, 2014
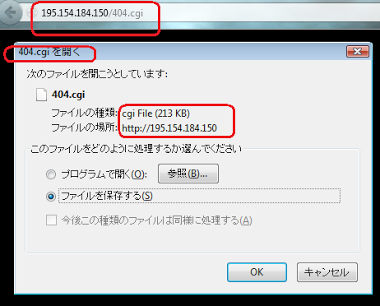
The experts at The Malware Must Die detected numerous attack worldwide exploiting the Bash Bug flaw to spread the Mayhem botnet. The researchers at Malware Must Die published a report warning of Mayhem Shellshock attack, the experts explained to have detected a significant number of Linux and UNIX systems infected by several IP addresses belonging to […]
 Pierluigi Paganini
October 09, 2014
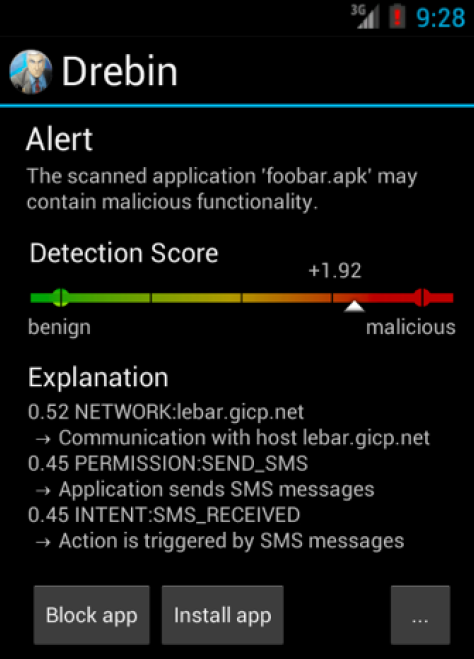
A team of German researchers developed an innovative Android app dubbed DREBIN capable of detecting 94 percent of mobile malware. A team of German researchers composed by Daniel Arp, Konrad Rieck, Malte Hubner, Michael Spreitzenbarth of Siemens computer emergency response team and Hugo Gascon of the University of Gottingen have developed an Android app capable […]
 Pierluigi Paganini
October 08, 2014
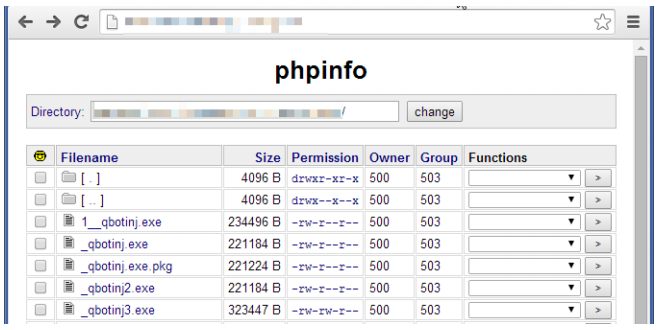
Proofpoint firm uncovered a malicious campaign run by the Northern Gold criminal group which is targeting online banking users with a botnet of 500,000 PCs . Security experts at Proofpoint firm have identified a Russian-speaking cybercrime gang, dubbed Northern Gold, that has compromised more than 500,000 machines worldwide to steal users’ online credentials for major banks in the […]
 Pierluigi Paganini
October 08, 2014
Criminal gangs have stolen millions of dollars from ATMs worldwide using the Tyupkin malware which forces machines to dispense cash. Criminal gangs in Eastern Europe are increasing the number of attacks against automated teller machines (ATMs), not only tampering the machine with card skimmers which steal debit card data, but also using malware. The malicious code used by […]
 Pierluigi Paganini
October 06, 2014
Cybercrime expert explains anyone with technical knowledge, a malware and the help of an insider could easily hack an ATM machine. A RM100 chip, specific technical knowledge and a free malware obtained over the Internet is all the necessary to hack Automated Teller Machines (ATMs), this is the opinion of a cybercrime expert, which released an exclusive […]
 Pierluigi Paganini
October 04, 2014
DrWeb firm discovered a Mac Botnet which already has infected more than 17,000 PCs and exploits Reddit platform to provide list of C&Cs servers to the bot. Security experts at Russian anti-virus company Dr Web have uncovered a new botnet, which is composed by thousands of Mac computers. The researchers dubbed the new sophisticated strain […]
 Pierluigi Paganini
October 03, 2014
A digitally signed version of the popular CryptoWall ransomware is distributed via five Alexa top-ranked websites in a widespread malvertising campaign. Security experts at Barracuda Labs have discovered a new variant of CryptoWall ransomware in the wild, the new strain of malware presents a valid digital signature and it is being delivered as part of a widespread malvertising […]







