


 Pierluigi Paganini
 May 18, 2014
Security Experts at Intercrawler have discovered in the underground a new Exploit-Kit dubbed “Infinity” which might be a new replacement of “Blackhole” Security expert at IntelCrawler, a cyber threat intelligence firm based in Los Angeles, discovered a new private exploit-kit called “Infinity” in the underground. It isn’t a distribution on a large-scale, authors reserved it […]
 Pierluigi Paganini
May 13, 2014
FireEye published a report titled “Operation Saffron Rose” to document the activities of the Iranian hacking group named Ajax Security Team According to a recent report titled “Operation Saffron Rose” published by cybersecurity company FireEye, a group called the Ajax Security Team is the principal Iranian hacking group, it is responsible for different espionage campaigns on custom-built malicious software. “This group, which […]
 Pierluigi Paganini
May 13, 2014
Unknown hackers have stolen files on the Ukraine crisis from the Belgian Foreign Ministry, causing the crackdown of targeted servers. A new cyber espionage campaign hit the Belgian foreign ministry, unknown hackers have stolen data related to the Ukraine crisis last week. The cyber attack has caused the crackdown of targeted servers which has left diplomats without […]
 Pierluigi Paganini
May 12, 2014
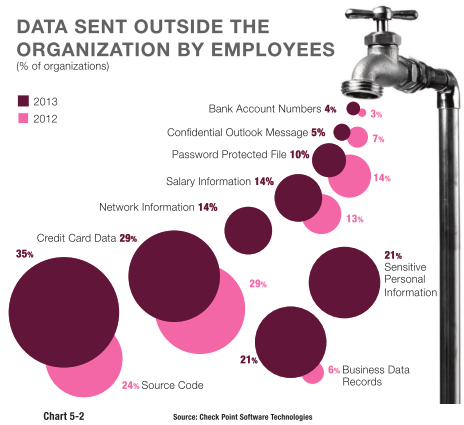
Check Point 2014 Security Report shows major security events occurred in 2013 show and provides useful information on current malware trends. Check Point Software Technologies published 2014 Security Report to highlight major security events occurred last year and show current malware trends. The data were collected monitoring network traffic from 996 organizations of various industries. Nearly 84 percent […]
 Pierluigi Paganini
May 07, 2014
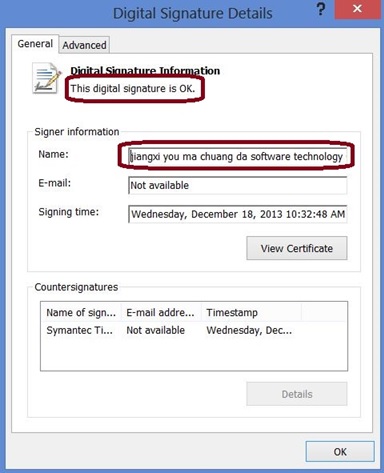
Security experts at McAfee Labs have discovered a new cyber espionage based on the malware digitally signed with stolel certificates. A recent research of McAfee Labs has identified a series of spear phishing attacks against non governmental entities and activists, the offensives which interested mainly organizations in China were conducted using malicious code signed with stolen digital […]
 Pierluigi Paganini
May 06, 2014
Discover how it is possible to apply steganography to hide secret messages in common tweets (or any text) with steg.js-of-the-dump. In the past we have discussed many times on the adoption of steganography to hide messages within images and video, a technique exploited also by authors of malware to hide configuration file and command sent by the C&C […]
 Pierluigi Paganini
May 05, 2014
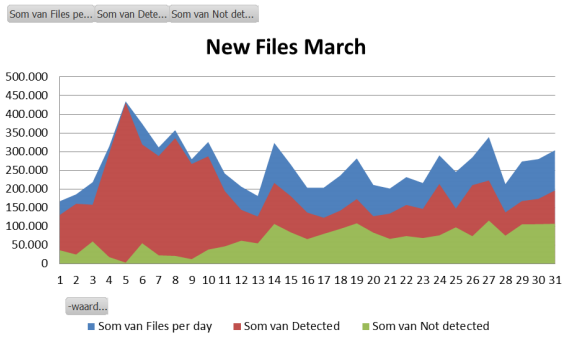
Dutch malware detection company RedSocks has issued its first Malware Trend Report related to the malicious code trends observed in the first quarter of 2014. RedSocks, a Dutch malware detection company which provides netflow-based malware detection service, has published its first Malware Trend Report Labs related to the first quarter of 2014. The report provides precious insights into the trends […]
 Pierluigi Paganini
May 04, 2014
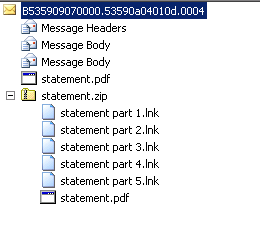
Expert at Trustwave explained the tactics adopted by cyber criminals how to serve malware in phishing attacks exploiting .lnk files. Phil Hay, expert at Trustwave SpiderLab, explained how cyber criminals are using .lnk files to serve malware via email. I have chosen to detail this tactic to demonstrate how much creative is the criminal ecosystem, even if it […]
 Pierluigi Paganini
April 30, 2014
Romanian Researcher discovered that Skype application store sensitive User Data Unencrypted on a local database. A Romanian programmer at Hackyard Security Group, Dragoş Gaftoneanu, revealed through a blog post that the popular VOIP application Skype leaves its local database unencrypted. Unfortunately the problem is very common, many applications, especially mobile apps, don’t encrypt application data exposing user’s information to serious risks for their privacy. According Gaftoneanu, […]
 Pierluigi Paganini
April 28, 2014
Securi firm has published an interesting post to explain how malware authors could hide a backdoor using PHP Callback functions. Security expert Peter Gramantik at Security Firm has written an interesting blog post to describe how it is possible to hide a backdoor using common PHP callback functions. The technique could surprise the laymen, but malware authors are […]







