Pierluigi Paganini
 November 15, 2026
A Microsoft 365 outage stopped a hotel’s email chlorine alert in Germany, and 15 guests were poisoned. A hotel in Germany had a maintenance safety system for its sauna area. If the chlorine level got too high, the system emailed the operators. When Microsoft’s cloud services failed, those emails couldn’t go out, the chlorine rose, […]
 Pierluigi Paganini
November 12, 2026
A Microsoft outage disrupted Outlook, Teams and Copilot, also breaking OpenAI and Anthropic connectors to Microsoft 365 accounts. Microsoft 365, Outlook and Teams went down for thousands of US users on Thursday, November 12. Reuters reported that the disruption also hit the connectors OpenAI’s and Anthropic’s AI services use to reach Microsoft accounts. “Microsoft 365, […]
 Pierluigi Paganini
November 11, 2026
Microsoft November Patch Tuesday security updates fix 1,090 flaws, including one exploited Outlook bug and 30 potentially wormable issues. Microsoft November Patch Tuesday addressed about 1,090 new vulnerabilities, which is less than the roughly 1,400 last month. Two months in a row now exceed every previous year from Microsoft, and the overall count is a […]
 Pierluigi Paganini
October 14, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Microsoft Windows Shell flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Microsoft Windows Shell flaw, tracked as CVE-2026-96951 (CVSS score of 8.8), to its Known Exploited Vulnerabilities (KEV) catalog. Microsoft Patch Tuesday security updates for October 2026 address a […]
 Pierluigi Paganini
October 06, 2026
Microsoft released emergency updates for Exchange Server to fix CVE-2026-96940, a high-severity flaw that can let attackers gain higher privileges. Microsoft has released out-of-band security updates for Exchange Server to fix a high-severity vulnerability tracked as CVE-2026-96940 (CVSS score of 8.8). The flaw is caused by weak authorization and can allow an authenticated attacker to […]
 Pierluigi Paganini
September 21, 2026
A 2017 UK assessment warned that police data on Microsoft Azure could face foreign access risks. The risks may still exist. A Guardian investigation has surfaced a 2017 document signed off by then City of London police commissioner Ian Dyson, who also held the title of senior information risk owner for the entire country. That […]
Pierluigi Paganini
August 12, 2026
Microsoft Patch Tuesday for August 2026 fixes 398 CVEs, including an actively exploited zero-day and a wormable DNS flaw enabling remote code execution. Microsoft released its Patch Tuesday security updates for August 2026 on Tuesday, covering 398 new CVEs across Windows, Office, Azure, Exchange Server, SharePoint, Teams, GitHub Copilot, .NET, and a range of other […]
 Pierluigi Paganini
July 15, 2026
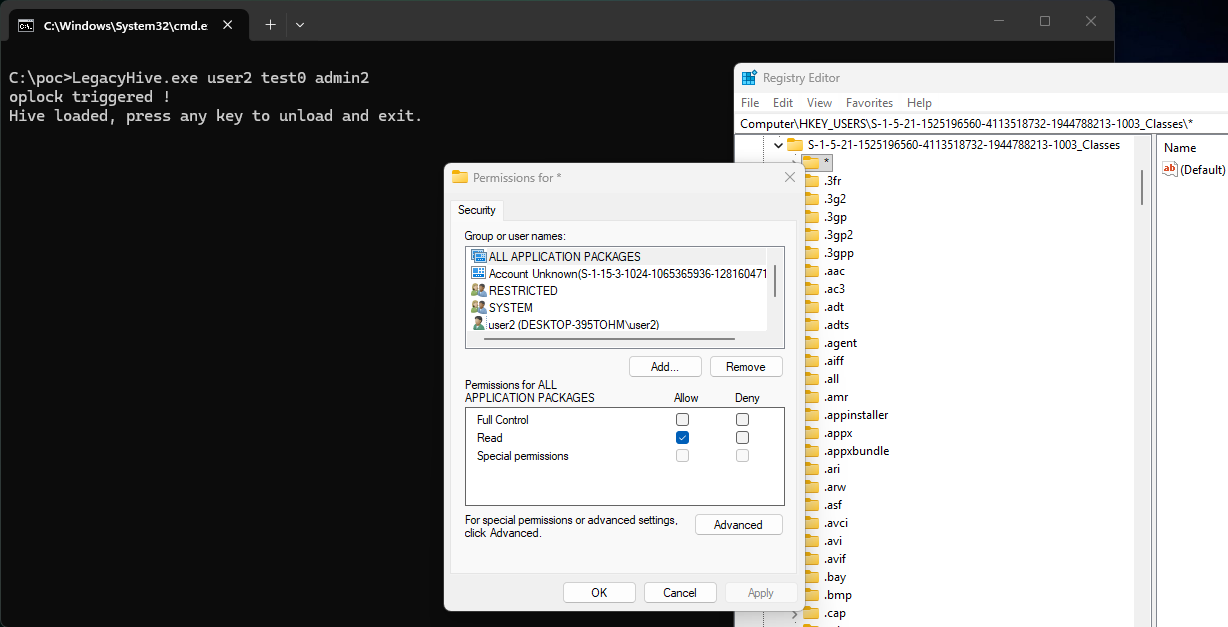
LegacyHive PoC exposes a Windows Privilege Escalation flaw affecting fully patched Windows desktop and server systems. Just hours after Microsoft’s July 2026 Patch Tuesday, security researcher Nightmare Eclipse, also known as Chaotic Eclipse, published a new Windows zero-day proof-of-concept called LegacyHive. This time, the target is the Windows User Profile Service (ProfSvc), and unlike the […]
Pierluigi Paganini
July 15, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds SonicWall and Microsoft flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added SonicWall and Microsoft flaws to its Known Exploited Vulnerabilities (KEV) catalog. The flaws added to the catalog are: This week, SonicWall confirmed the active exploitation of two zero-day vulnerabilities […]
Pierluigi Paganini
July 14, 2026
Patch Tuesday: Microsoft fixes a record 621 CVEs, including 2 exploited zero-days and critical flaws affecting SharePoint, RDP, Hyper-V, and AD FS. Microsoft’s July 2026 Patch Tuesday is, by a significant margin, the largest single-month security release in the company’s history. The Zero Day Initiative counted 621 new Microsoft CVEs for the month, and the […]