


 Pierluigi Paganini
 April 07, 2015
A security expert has discovered a severe vulnerability in BitTorrent Sync that can be exploited by a remote attacker to execute arbitrary code on a vulnerable machine. The security expert Andrea Micalizzi, also known as “rgod,”, has discovered a serious vulnerability in BitTorrent Sync (CVE-2015-2846) can be exploited by a remote attacker to execute arbitrary code. […]
 Pierluigi Paganini
April 06, 2015
The Turkish Government has blocked the access to YouTube, Facebook and Twitter in the country over Istanbul prosecutor siege images. Once again, I’m writing about online censorship, once again the protagonist is the Turkish Government that this time has blocked the access to popular social media sites, including Twitter and YouTube. The ban follows a court ruling […]
 Pierluigi Paganini
April 01, 2015
A security researcher discovered a couple of security issues on GitHub platform explaining how it is possible to exploit them in real attack scenarios. The researcher David Sopas (@dsopas) from Websegura discovered a couple of security issues in the coding website GitHub that were ranked by the company as minor, but that could expose users to cyber attacks. […]
 Pierluigi Paganini
March 25, 2015
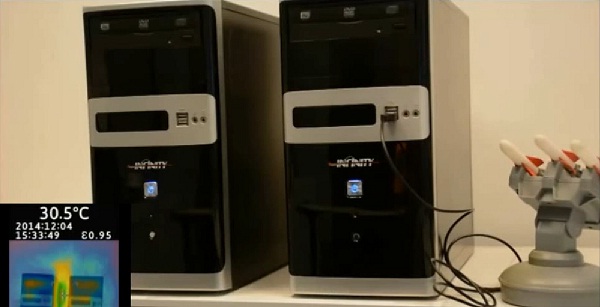
Israeli Researchers have defined a new exfiltration technique dubbed BitWhisper that is based on the heat emissions and built-in thermal sensors. According researchers at the Ben Gurion University in Israel, by detecting the heat from one computer to an adjacent computer, is possible to establish a channel that can claiming can facilitate the spread of keys, malicious […]
 Pierluigi Paganini
March 24, 2015
Security experts discovered that the Adobe CVE-2011-2461 vulnerability is exploitable by at least four years despite the company has issued a patch. Four years ago Adobe released a patch for the vulnerability CVE-2011-2461 that was affecting the Adobe Flex SDK 3.x and 4.x. The flaw was a cross-site scripting (XSS) vulnerability that allowed remote attackers to inject arbitrary […]
 Pierluigi Paganini
March 23, 2015
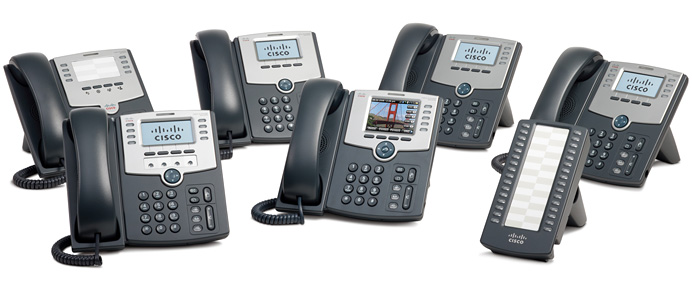
Chris Watts discovered a security flaw affecting some models of Cisco IP Phones that could be exploited to eavesdrop on conversations and make phone calls. Some models of Cisco IP phones for small businesses are affected by a vulnerability, coded as CVE-2015-0670 that could be exploited by a remote attacker to eavesdrop on conversations and make phone calls […]
 Pierluigi Paganini
March 22, 2015
Cisco Security Team has spotted in the wild a new Point-of-Sale malware dubbed PoSeidon that is more sophisticated than previously detected PoS malware. Expert at Cisco have discovered a new Point-of-Sale (PoS) malware dubbed PoSeidon. The experts have discovered many similarities with the popular Zeus Trojan and use sophisticated methods to find card data respect other POS malware like BlackPoS, which was used […]
 Pierluigi Paganini
March 18, 2015
DLL hijacking is not a prerogative for Windows systems, it is a common hacking technique that is very effective against OS X based machines. As you may know, DLL hijacking it’s something that its around since around 2000 and allows hackers to exploit a machine with a vulnerable application ( just one of the possibilities […]
 Pierluigi Paganini
March 13, 2015
Security Experts at Malwarebytes security firm spotted a new Facebook worm that spreads itself by leveraging multiple cloud services. Social media are a privileged attack vector, recent reports published by the principal security firms confirm that cyber criminal are exploiting these platforms for illegal activities. Last disastrous news for the users of the popular social […]
 Pierluigi Paganini
March 11, 2015
Microsoft and Apple released security updates to fix the FREAK vulnerability recently discovered and affecting their products. FREAK is a major security flaw recently discovered that left users of Apple and Google devices exposed to MITM attack while visiting supposedly secure Websites. At the same time Microsoft issued a specific security advisory to inform its […]

Artificial Intelligence / September 17, 2026
Hacking / September 17, 2026





