 Pierluigi Paganini
 October 16, 2026
The regulated utility company CenterPoint Energy says a data breach exposed the personal information of more than 1 million people in Texas. CenterPoint Energy is a regulated utility company used to deliver natural gas and electricity infrastructure, maintain power grids and pipelines, and restore service across parts of Texas, Indiana, Ohio, and Minnesota. The organization […]
 Pierluigi Paganini
October 15, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Palo Alto Networks PAN-OS, Ahsay AhsayCBS, and Cisco Secure Email Gateway flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: Cisco confirmed this week that threat actors are exploiting a critical vulnerability […]
 Pierluigi Paganini
October 15, 2026
Silent Lynx, a group likely based in Kazakhstan, targets Russian energy and government entities in espionage campaigns across Central Asia. Researchers from Cisco Talos and Recorded Future published a detailed paper on a threat actor they call Silent Lynx (aka UAT-6275, TAG-193), a Kazakhstan nexus group conducting espionage across Central Asia. The targets include the […]
 Pierluigi Paganini
October 15, 2026
Spyware vendors use online ad infrastructure to profile targets and deliver exploits without requiring users to click anything. The investigation links Discover-Tech to Candiru, an Israeli spyware vendor that the US government placed on its Entity List in 2021. Candiru has since used the name Integrity Labs. Citizen Lab also identified links involving other surveillance […]
 Pierluigi Paganini
October 15, 2026
Attackers exploit a critical Cisco email gateway flaw to gain root access. Cisco urges customers to update scanner tools and check for compromise. Cisco confirmed this week that threat actors are exploiting a critical vulnerability in Cisco Secure Email Gateway, tracked as CVE-2026-76519 with a CVSS score of 9.8. An attacker can exploit the flaw […]
Pierluigi Paganini
October 14, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Microsoft Windows Shell flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Microsoft Windows Shell flaw, tracked as CVE-2026-96951 (CVSS score of 8.8), to its Known Exploited Vulnerabilities (KEV) catalog. Microsoft Patch Tuesday security updates for October 2026 address a […]
 Pierluigi Paganini
October 14, 2026
Microsoft Patch Tuesday security updates for October 2026 address a record 1,415 vulnerabilities. Prioritize the exploited zero-day, critical bugs and potentially wormable vulnerabilities. Microsoft just shattered every patch record in the book. October 2026 brought us a staggering 1,415 new CVEs from Microsoft alone. “Well, it’s a new record release from Microsoft, again. This is […]
 Pierluigi Paganini
October 14, 2026
OpenAI employee charged with planting hidden audio recorders to capture sensitive discussions about AI research and company strategy. On September 30, OpenAI staff found a small audio recording device jammed into a USB port on the back of a television in an executive conference room in their San Francisco office. The device had been there […]
 Pierluigi Paganini
October 14, 2026
Ivanti VPN zero-days let attackers gain root access, steal credentials, evade detection, and prepare for wider network compromise. On October 5, Volexity started investigating suspicious activity at one of its monitoring customers and traced everything back to an Ivanti Connect Secure VPN appliance running version 22.8R2.4, the latest build available at the time. Three chained […]
 Pierluigi Paganini
October 14, 2026
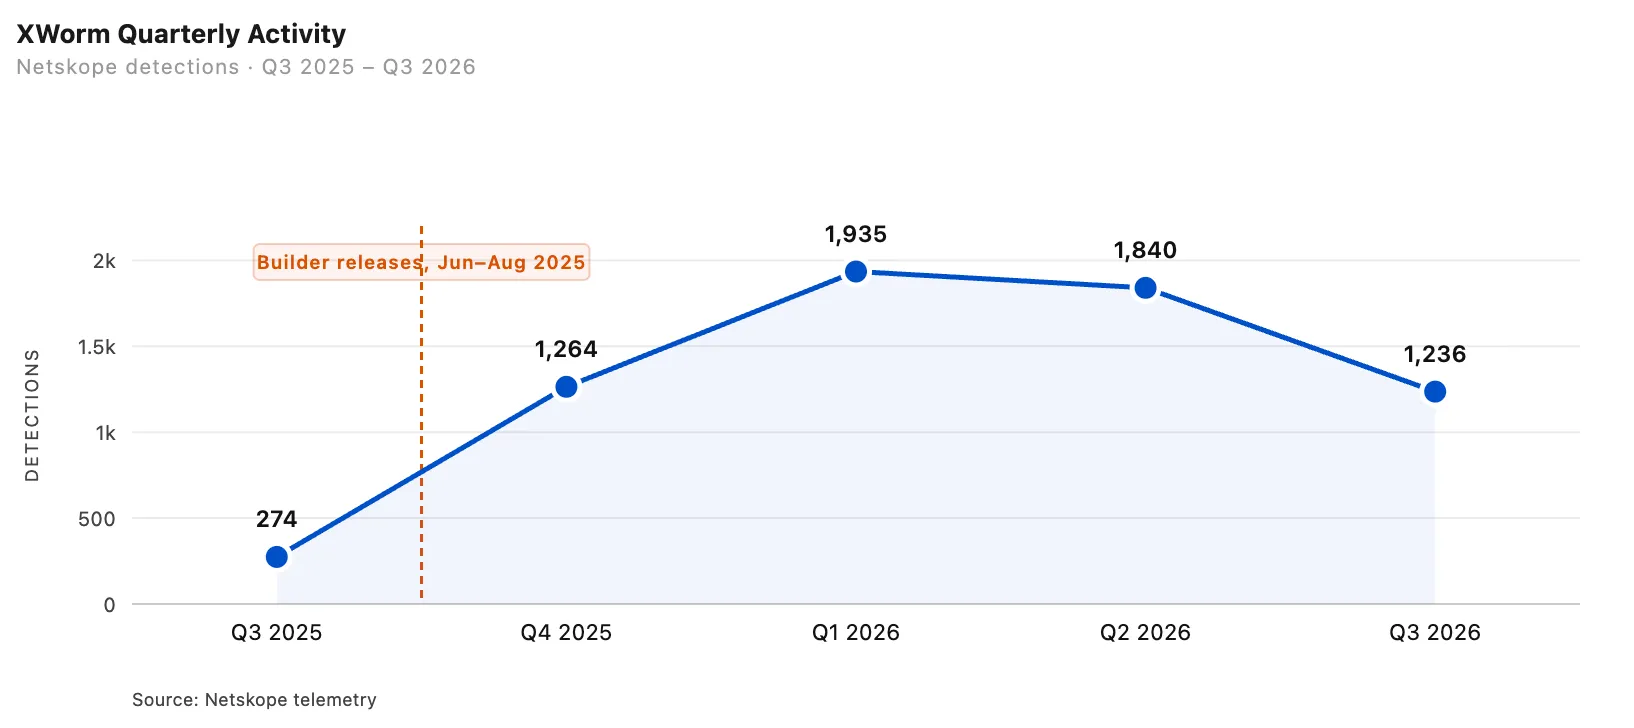
Netskope tracks four XWorm versions in the wild, 46 plugins, and new tools for location, audio and live browser control, with detections up fourfold. Netskope Threat Labs has been following XWorm since September 2024, and its latest report shows the malware has changed a lot. Over the past year the team identified four distinct versions […]

Hacking / October 22, 2026