 Pierluigi Paganini
 April 03, 2021
The Avaddon ransomware operators updated their malware after security researchers released a public decryptor in February 2021. The Avaddon ransomware family first appeared in the threat landscape in February 2020, and its authors started offering it with a Ransomware-as-a-Service (RaaS) model in June, 2020. In August 2020, cybersecurity intelligence firm Kela was the first to report that […]
 Pierluigi Paganini
March 29, 2021
Harris Federation, the multi-academy trust of 50 primary and secondary academies in and around London, was hit by a ransomware attack. A ransomware attack hit the IT systems of London-based nonprofit multi-academy trust Harris Federation on Saturday, March 27. Harris Federation is a multi-academy trust of 50 primary and secondary academies in and around London […]
 Pierluigi Paganini
March 28, 2021
A cyber attack has disrupted the Australian Channel Nine’s live broadcasts, the company was unable to transmit its Sunday morning news program. A cyber attack has hit the Australian Channel Nine’s live broadcasts causing the disruption of its operations. The broadcaster was unable to air its Sunday morning news program, which runs from 7:00 am to 1:00 […]
 Pierluigi Paganini
March 28, 2021
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. If you want to also receive for free the international press subscribe here. CISA releases CHIRP, a tool to detect SolarWinds malicious activity Microsoft Defender can now protect servers against ProxyLogon […]
 Pierluigi Paganini
March 27, 2021
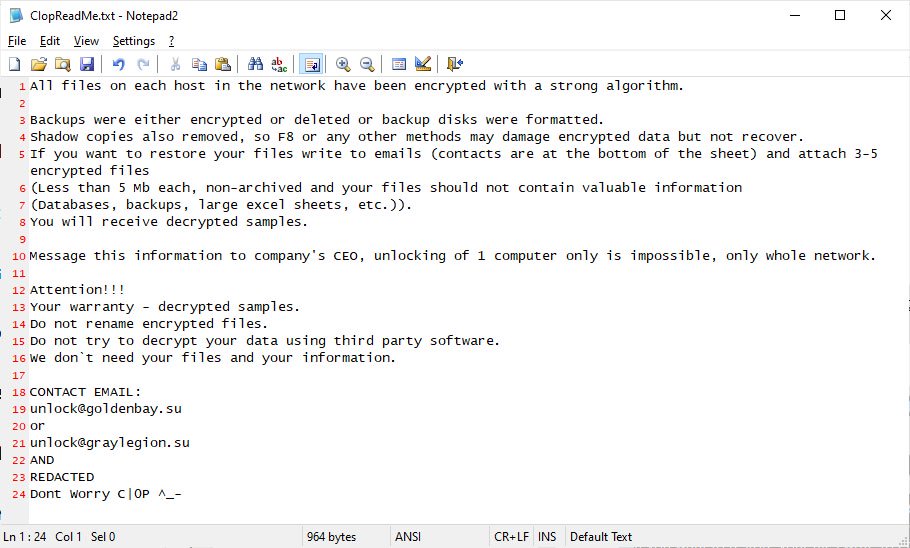
Clop ransomware operators now email victim’s customers and ask them to demand a ransom payment to protect their privacy to force victims into paying the ransom. Clop ransomware operators are switching to a new tactic to force victims into paying the ransom by emailing their customers and asking them to demand a ransom payment to […]
 Pierluigi Paganini
March 24, 2021
Security experts reported that a second ransomware gang, named Black Kingdom, is targeting Microsoft Exchange servers. After the public disclosure of ProxyLogon vulnerabilities, multiple threat actors started targeting vulnerable Microsoft Exchange servers exposed online. The first ransomware gang exploiting the above issues in attacks in the wild was a group tracked as DearCry. Last crew […]
Pierluigi Paganini
March 23, 2021
This week, IoT company Sierra Wireless disclosed a ransomware attack that hit its internal IT systems on March 20 and disrupted its production. Sierra Wireless is a Canadian multinational wireless communications equipment designer and manufacturer headquartered in Richmond, British Columbia, Canada. The company sells mobile computing and machine-to-machine (M2M) communications products that work over cellular […]
Pierluigi Paganini
March 21, 2021
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. If you want to also receive for free the international press subscribe here. Experts found 15 flaws in Netgear JGS516PE switch, including a critical RCE Google releases Spectre PoC code exploit […]
 Pierluigi Paganini
March 17, 2021
The FBI has issued an alert to warn about an increase in PYSA ransomware attacks on education institutions in the US and UK. The FBI has issued Tuesday an alert to warn about an increase in PYSA ransomware attacks against education institutions in the United States and the United Kingdom. In March 2020, CERT France cyber-security […]
Pierluigi Paganini
March 14, 2021
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. If you want to also receive for free the international press subscribe here. Chinese hackers allegedly hit thousands of organizations using Microsoft Exchange REvil Ransomware gang uses DDoS attacks and voice […]
Malware / November 02, 2026
Security / November 02, 2026