


 Pierluigi Paganini
 August 24, 2026
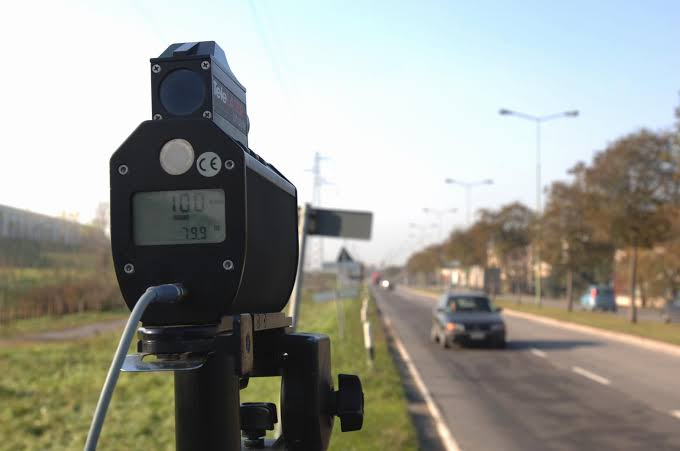
Slovakia warns that vulnerable speed cameras could expose vehicle data, enable remote access and provide attackers with a foothold into public networks. Slovakia’s National Security Authority, NBÚ, recently issued a warning about several road speed cameras, calling them a significant cyber threat. The alert is not about someone deleting a speeding ticket. It is about […]
 Pierluigi Paganini
August 24, 2026
TikTok will pay $400 million to settle U.S. claims that it violated child privacy laws by collecting data from users under 13. The U.S. Department of Justice announced that TikTok will pay $400 million to settle a 2024 lawsuit over children’s privacy. “Today, the Department of Justice announced a $400 million settlement with TikTok, ByteDance, […]
 Pierluigi Paganini
August 24, 2026
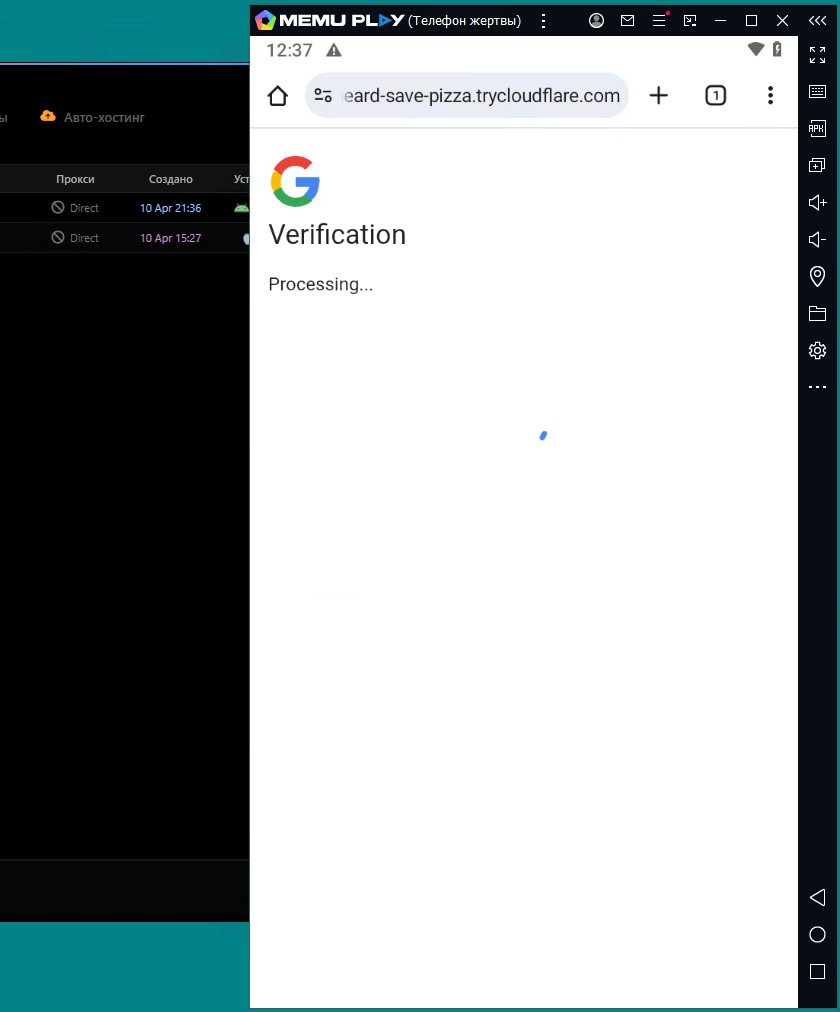
iAuthFlow v2 phishing toolkit uses a phished Google session to enroll an attacker-controlled passkey that survives password resets. Abnormal Security researchers have published an analysis of iAuthFlow v2, a phishing toolkit sold on a Russian-language cybercrime forum for $10,000 base price. The author also offers for sale additional capability modules separately. The headline feature is […]
 Pierluigi Paganini
August 23, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Akira Hits Safe Mode: Ransomware Rebooting Around EDR Multi-Functional Linux Botnet “Evooo1Bot” StubMaker RubyGems Campaign Delivers a Windows Infostealer Hunting MacSync Stealer infrastructure through behavioral pivots Manic: Blend between Banking Malware & Spyware […]
 Pierluigi Paganini
August 23, 2026
Iran-linked hackers shut down a UK power plant for four days in the first confirmed attack of its kind, concurrent with water infrastructure attacks across 12 US states. Iran-linked hackers shut down a British power plant for four days in what The Telegraph describes as the most successful cyberattack of its kind against UK energy […]
 Pierluigi Paganini
August 23, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. ToxicPanda 2.0 Gets a Major Upgrade, Expanding Attacks Across 16 Countries Malware Hijacks Android Car Head Units […]
 Pierluigi Paganini
August 22, 2026
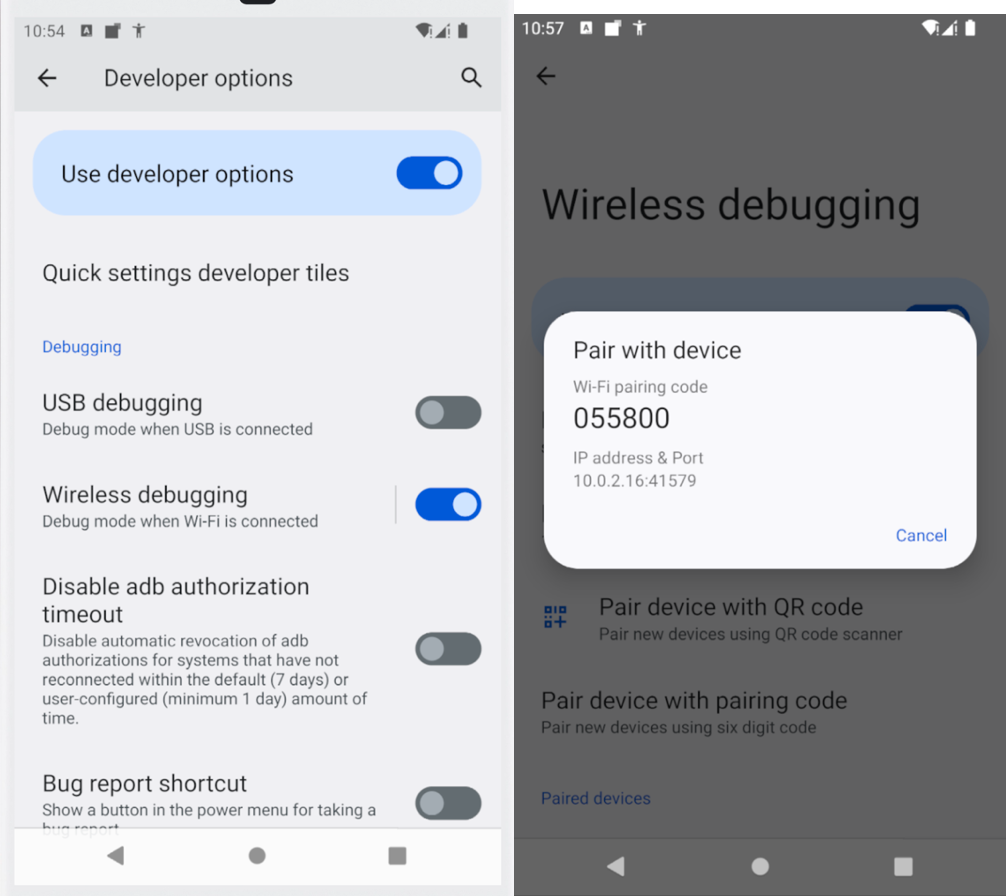
ToxicPanda 2.0 targets 349 financial apps and abuses Android Wireless Debugging to gain deeper device access and steal banking credentials. ToxicPanda used to be a Europe-focused nuisance targeting a manageable list of banks. That version is gone. Zimperium’s zLabs team just documented ToxicPanda 2.0, and the numbers alone tell the story: 349 targeted financial institutions […]
 Pierluigi Paganini
August 22, 2026
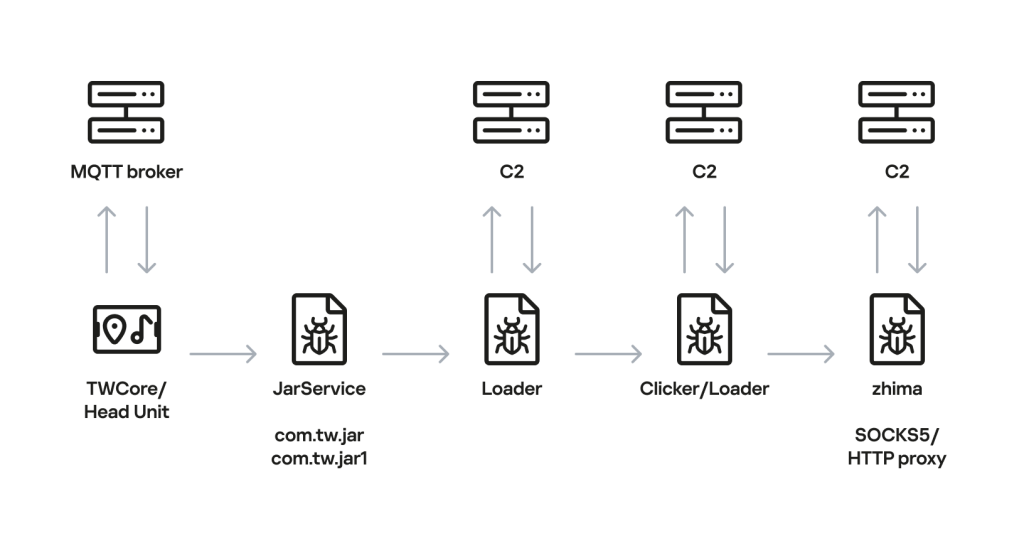
Malware is abusing car infotainment updates to install proxy software, turning Android head units into nodes for the BADBOX network. Kaspersky researchers found something in June 2026 that made them stop and look twice: an Android app with no interface at all, installed like any ordinary app but making zero effort to disguise itself as […]
 Pierluigi Paganini
August 22, 2026
A critical flaw (CVSS 9.4) in NASA/JPL’s AIT-GUI let anyone send unauthenticated commands to spacecraft instruments. Cycode researchers found that AIT-GUI, the browser-based operator console in NASA/JPL open-source AMMOS Instrument Toolkit, shipped with no authentication, no session checks, and no CSRF protection on any of its state-changing endpoints. “AIT-GUI, the web front end of NASA/JPL’s […]
 Pierluigi Paganini
August 22, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Zimbra Collaboration Suite (ZCS) flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the Zimbra Collaboration Suite (ZCS) flaw CVE-2026-73570 to its Known Exploited Vulnerabilities (KEV) catalog. CERT Polska, Poland’s national computer emergency response team, confirmed this week that threat actors […]
Hacking / September 17, 2026





