Pierluigi Paganini
 September 26, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds WordPress flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a WordPress Core flaw, tracked as CVE-2026-87902 (CVSS score of 9.2), to its Known Exploited Vulnerabilities (KEV) catalog. CVE-2026-87902 allows an unauthenticated attacker to make the get_page_template() function include a readable local […]
 Pierluigi Paganini
September 23, 2026
WordPress 7.1.2 fixes an unauthenticated file inclusion bug active since version 4.7, patchable but exploitable into remote code execution. WordPress 7.1.2 shipped on September 22 address an unauthenticated local file inclusion, tracked as CVE-2026-87902 (CVSS score of 9.2), which stems of how the CMS resolves page templates, with a real path to remote code execution. […]
 Pierluigi Paganini
August 31, 2026
A critical GiveWP flaw lets unauthenticated attackers execute server commands. Version 4.16.7.2 fixes the PHP object injection chain. A critical vulnerability in GiveWP, one of the most widely used WordPress plugins for online donations and fundraising, can let an unauthenticated attacker execute commands on the server. Patchstack disclosed the flaw on August 28, after researcher […]
Pierluigi Paganini
August 25, 2026
Two CVSS 9.8 miniOrange SAML WordPress plugin auth bypasses were exploited while paid editions never appeared in any vulnerability database. Manual patch required. Two critical authentication bypass vulnerabilities in the miniOrange SAML 2.0 Single Sign On WordPress plugin, both rated CVSS 9.8, are under active exploitation. Both CVE-2026-61979 and CVE-2026-15981 allow an unauthenticated attacker to […]
 Pierluigi Paganini
August 20, 2026
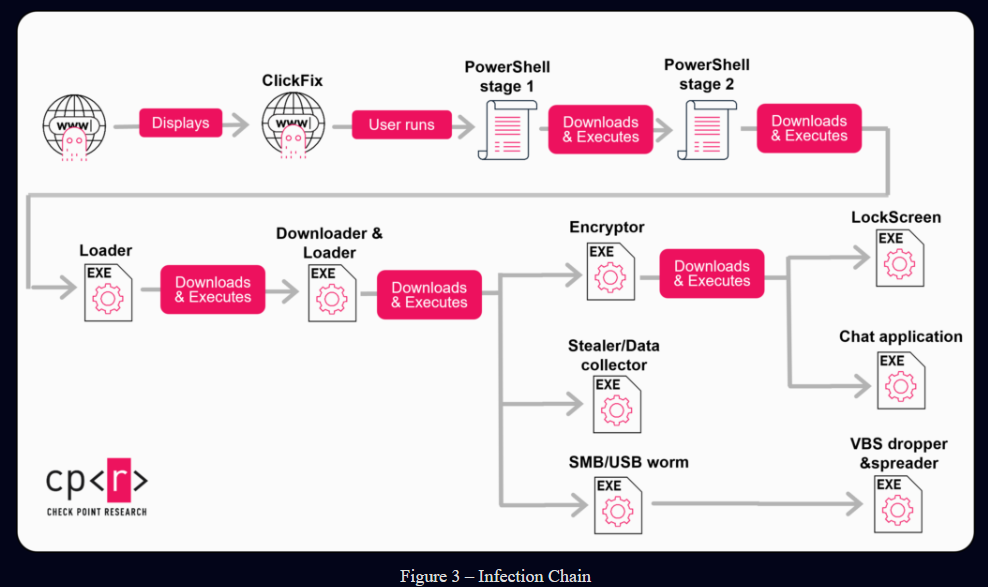
StopAndProtect turned nearly 2,000 hacked WordPress sites into a criminal network for malware delivery, data theft, surveillance and ransomware. Check Point Research uncovered a cybercrime operation, dubbed StopAndProtect, that has turned thousands of hacked WordPress websites into a shared platform for malware delivery, data theft, surveillance and ransomware. The operation is a good reminder that […]
 Pierluigi Paganini
August 07, 2026
WordPress XSS2Shell flaw enables admin takeover and remote code execution. Users should update to patched versions. Researchers at Pwn just published a report on a vulnerability chain they’re calling XSS2Shell, and the entry point is quite simple: type a username that doesn’t exist, and WordPress echoes it back with a tiny formatting flaw baked into […]
Pierluigi Paganini
July 22, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds DD-WRT, Langflow, and WordPress flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added DD-WRT, Langflow, and WordPress flaws to its Known Exploited Vulnerabilities (KEV) catalog. Below are the flaws added to the KeV catalog: The first issue added to the catalog […]
Pierluigi Paganini
July 19, 2026
Public exploits are now available for two critical WordPress flaws that attackers can chain to gain remote code execution without authentication. Public proof-of-concept exploits are now available for the critical wp2shell vulnerabilities affecting WordPress Core. The flaws, tracked as CVE-2026-63030 and CVE-2026-60137, can be chained to achieve pre-authentication remote code execution on default WordPress installations […]
Pierluigi Paganini
June 23, 2026
Attackers backdoored ShapedPlugin Pro updates, deploying malware that steals credentials, 2FA secrets, and grants full site access. If you installed a ShapedPlugin Pro plugin between April and June 2026 and kept it updated, your site may be compromised. Not because you did something wrong, but because the vendor’s own build and distribution pipeline was breached. […]
Pierluigi Paganini
June 15, 2026
Attackers compromised Awesome Motive CDN files, backdooring WordPress sites running OptinMonster, TrustPulse, and PushEngage. Sansec researchers discovered an active supply chain attack hitting WordPress sites running OptinMonster, TrustPulse, and PushEngage, three plugins operated by Awesome Motive, one of the largest WordPress plugin companies in the world. The malicious JavaScript wasn’t sitting on any victim’s server. […]