 Pierluigi Paganini
 September 15, 2026
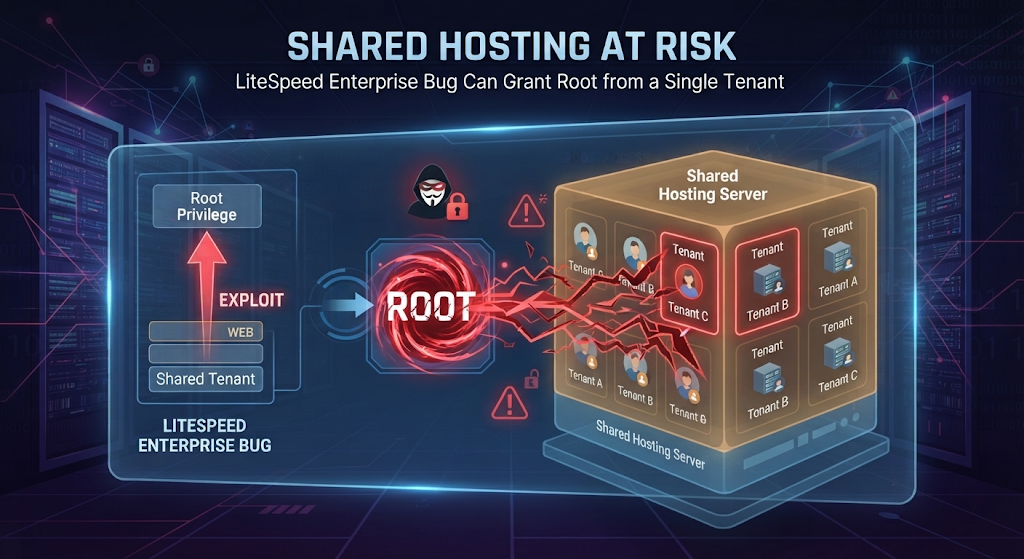
Critical LiteSpeed Enterprise flaw lets one shared hosting account gain root, bypassing CageFS; patch now to 6.3.7 via forced update. cPanel warned that a critical flaw in LiteSpeed Enterprise can let a low‑privilege website user break out of their account and gain root on the whole server. On a box where dozens or hundreds of […]
 Pierluigi Paganini
June 16, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco Catalyst and LiteSpeed cPanel plugin flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Cisco Catalyst and LiteSpeed cPanel plugin flaws to its Known Exploited Vulnerabilities (KEV) catalog. The two flaws added to the catalog are: CVE-2026-20262 is an arbitrary […]
Malware / September 25, 2026
Malware / September 25, 2026