Pierluigi Paganini
 November 02, 2011
The Duqu trojan main purpose is to obtain a remote access allowing an adversary to gather information from a compromised computer and of course to download and run arbitrary programs. Duqu malware s ...
Pierluigi Paganini
November 01, 2011
Welcome on board Welcome! If you are curious, interested in the subject and looking for a place with a few clicks you canbe updated on what happens in the world … well you you’ve fo ...
 April 23, 2026
November 17, 2026
November 16, 2026
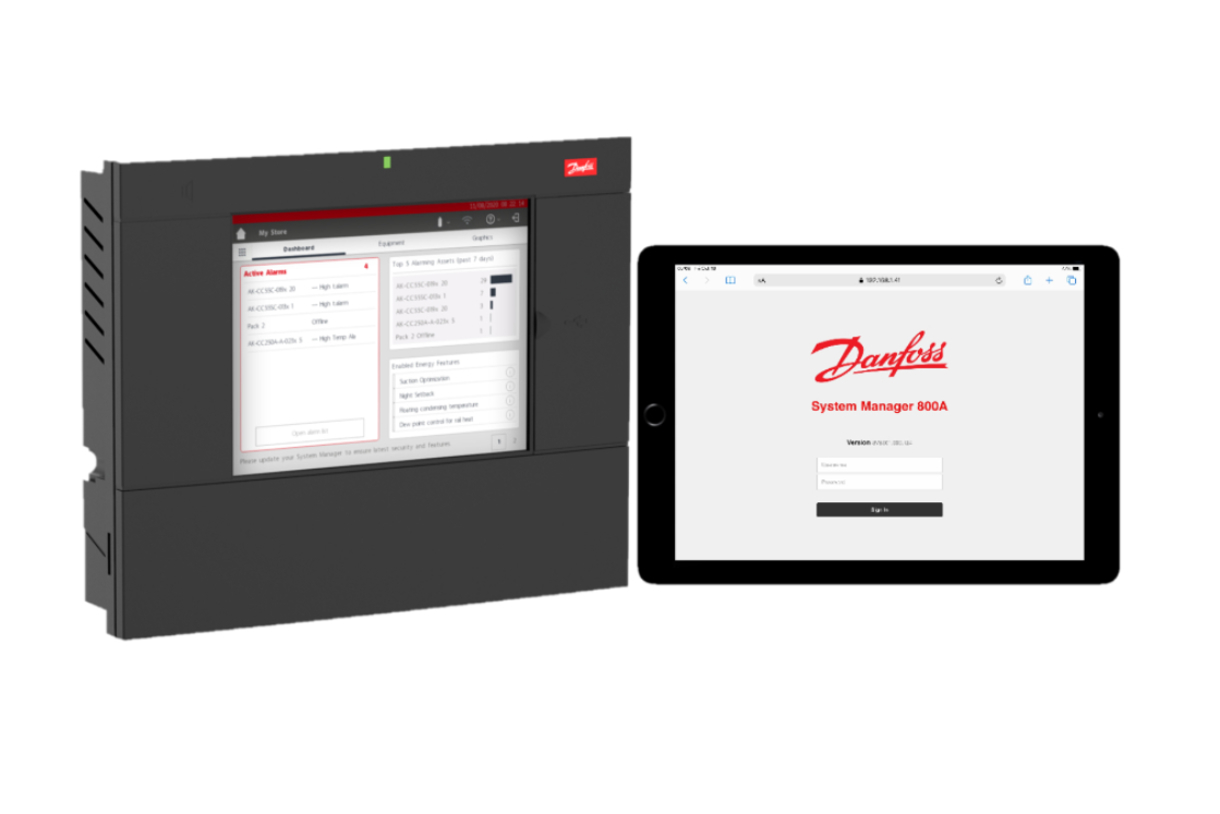
Midnight Blue found six unpatched remote takeover flaws in Danfoss AK-SM800A controllers in under an hour. Agencies agree: take them off the internet. Since 11 October, attackers have been hitting ...
Pierluigi Paganini
November 17, 2026
A breach at an Infoblox supplier exposed customer network snapshots and employee data, highlighting the risks of trusted third-party access. Infoblox, one of the major players in cybersecurity and ...
Pierluigi Paganini
November 17, 2026
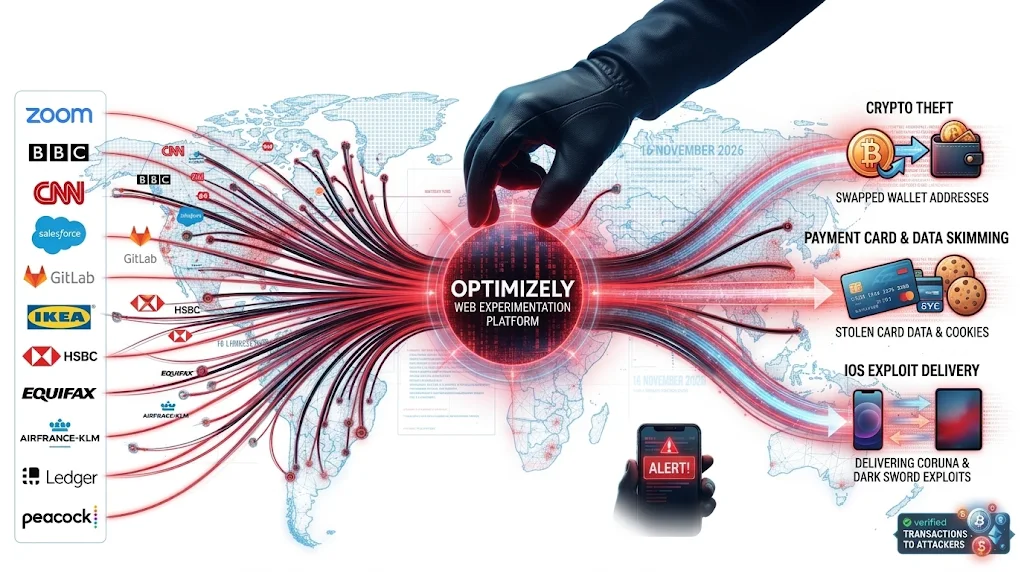
OPTIMJACK: Attackers hijacked Optimizely scripts on 178 organizations' websites, spreading malware to steal crypto, payment card data and target iPhones. Visitors to 178 organizations received mal ...
Pierluigi Paganini
November 17, 2026
Greiz hospital reopens its emergency room after an extortion attack. Investigators are probing the case, but no state links have emerged. The Greiz-Ronneburg district hospital in Thuringia reporte ...
Pierluigi Paganini
November 17, 2026
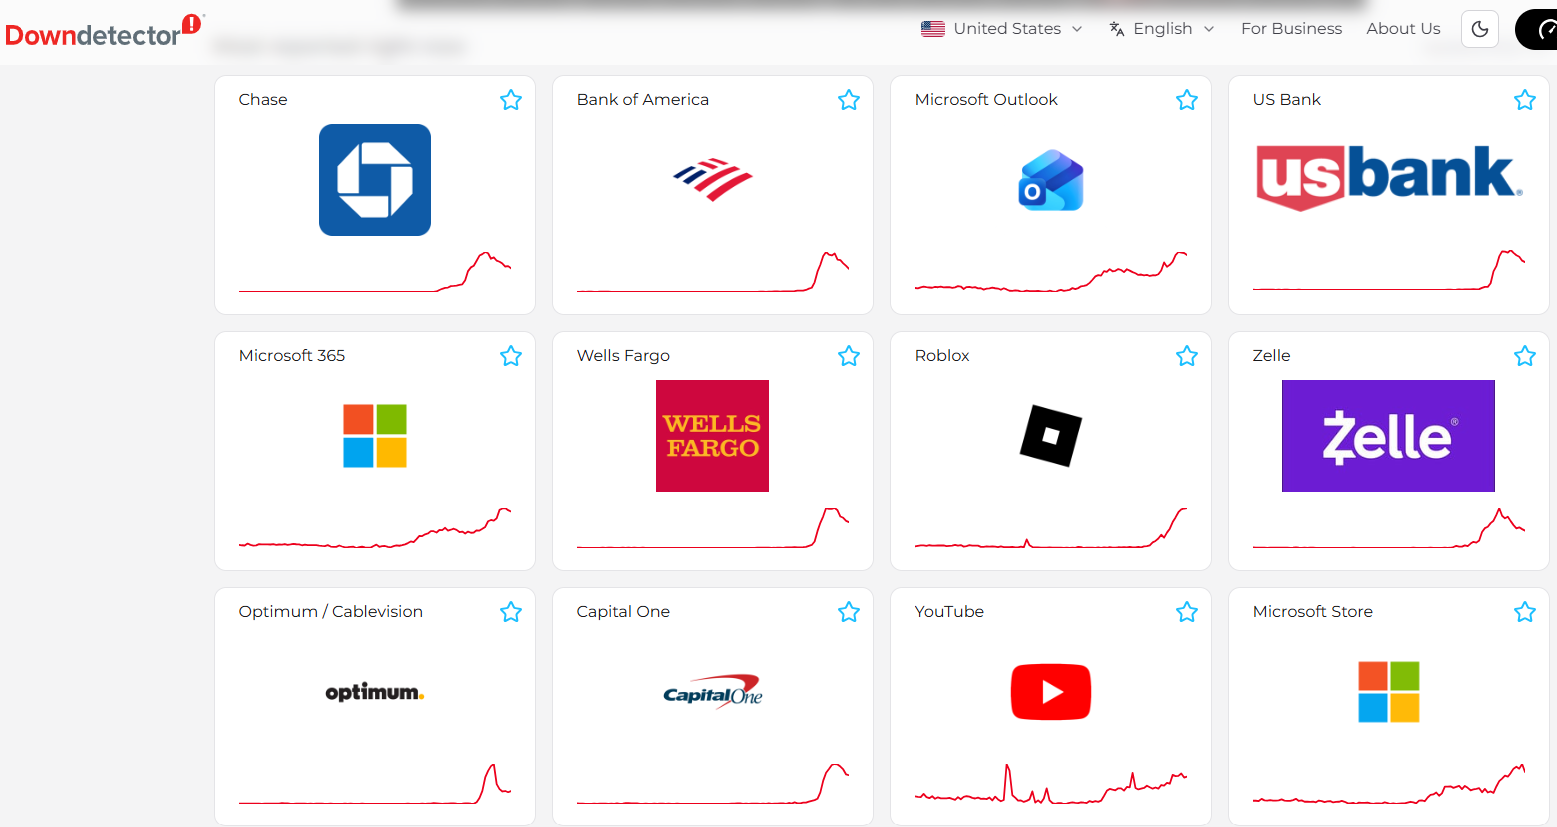
U.S. banks suffered widespread outages, disrupting online banking and payments and raising concerns about technology dependencies and resilience. A wave of service disruptions affected several maj ...
Pierluigi Paganini
November 16, 2026
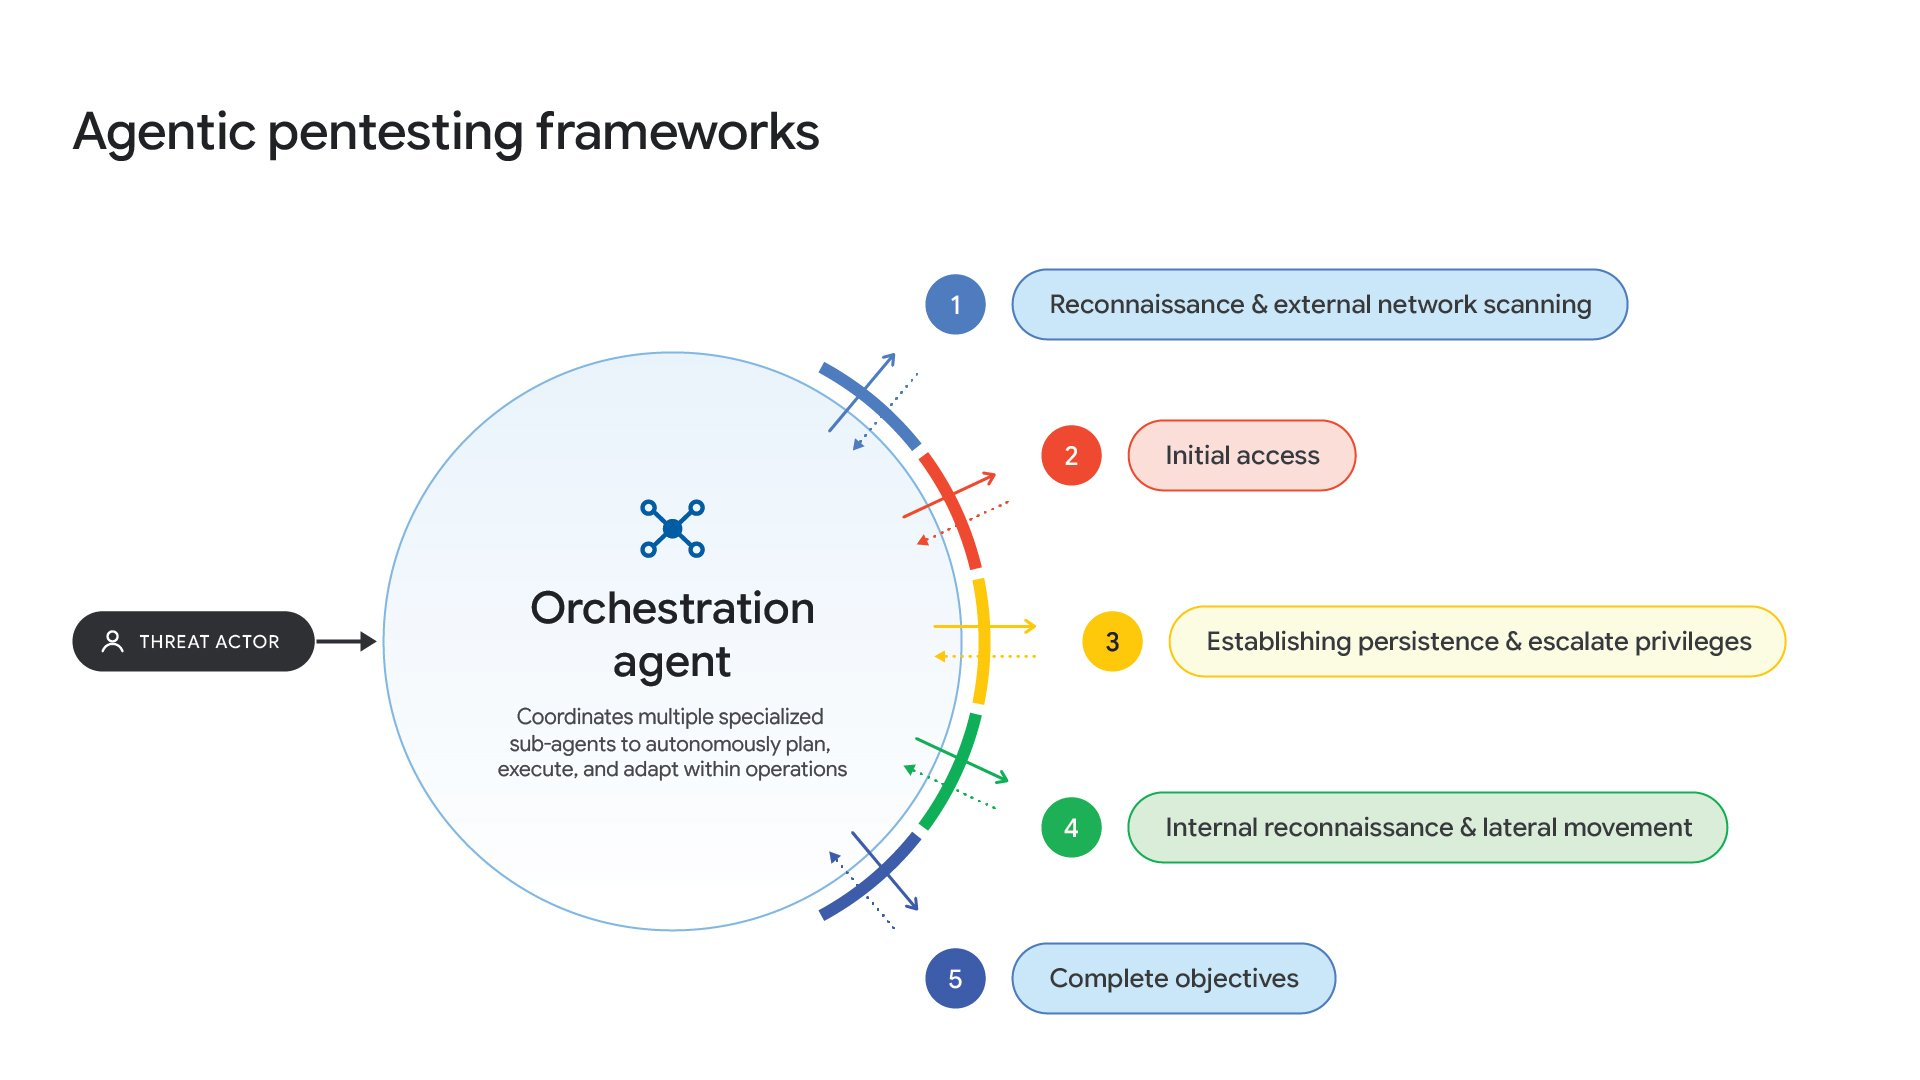
Google finds attackers using autonomous AI agents to automate exploits, steal AI access and scale intrusions, often sacrificing stealth for speed. Google’s Threat Intelligence Group (GTIG) says ...
Pierluigi Paganini
November 16, 2026
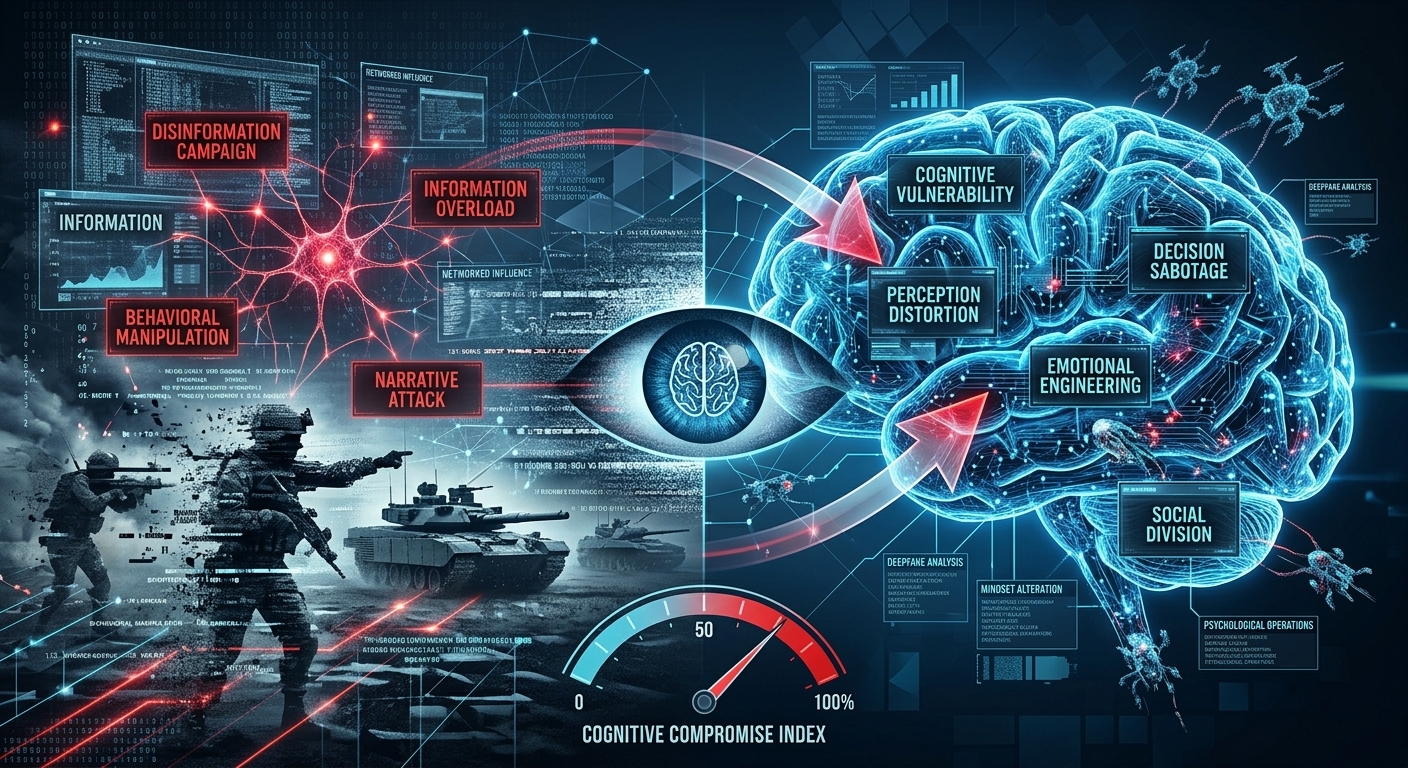
Cognitive warfare uses AI, deepfakes and fear to manipulate opinions, erode trust and disrupt society. Contemporary warfare is no longer fought solely through armies, weapons, and technological i ...
Pierluigi Paganini
November 16, 2026
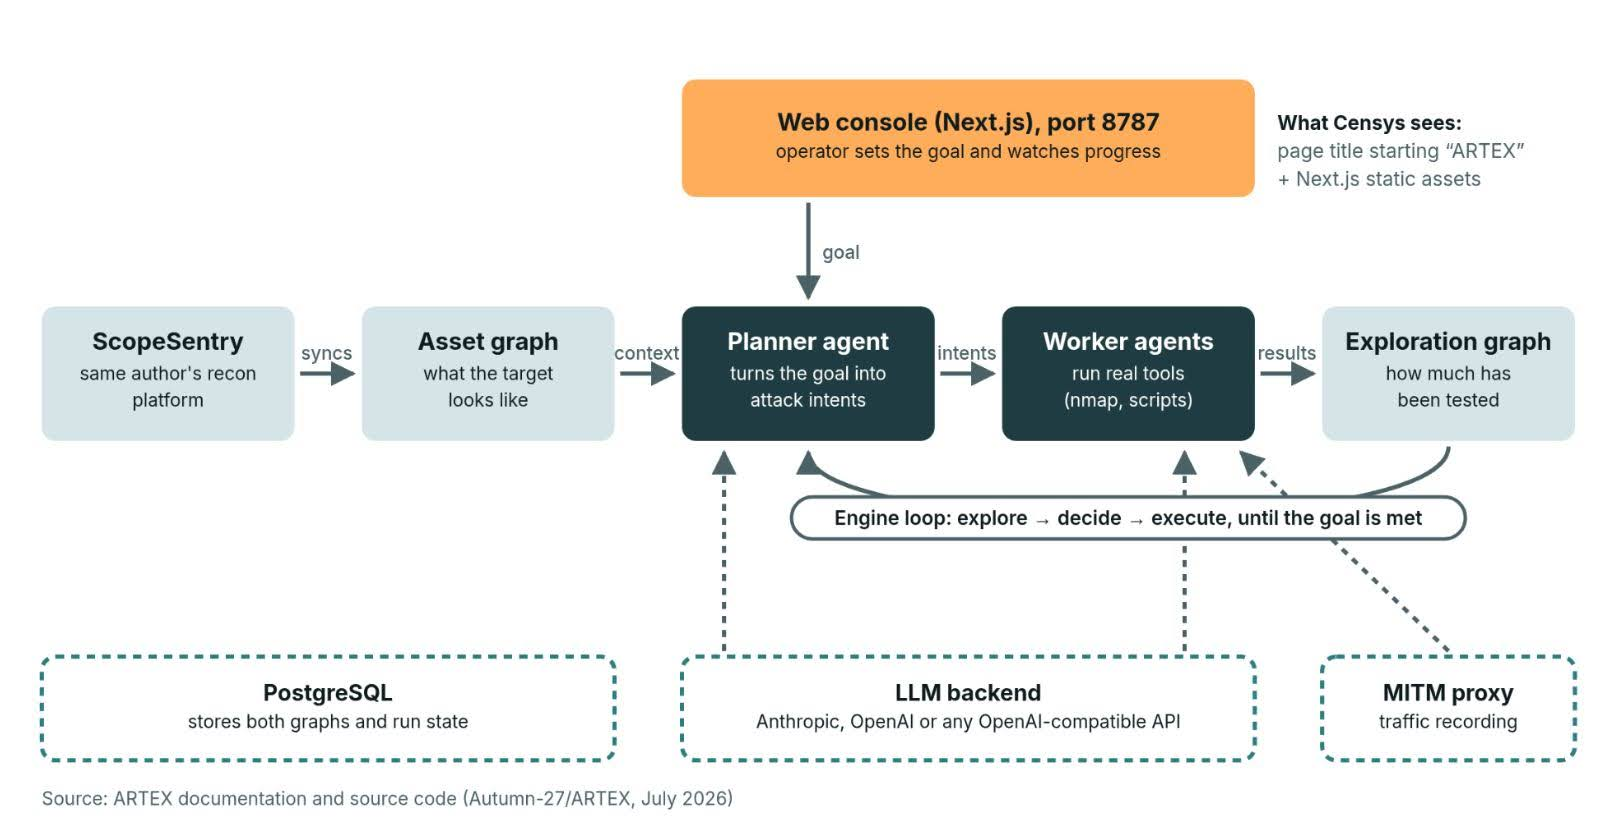
The researcher MalwareMustDie released an open ARTEX detection pack in seven formats, built on behavior and a repeatable playbook, because attackers now turn weeks into hours. The researcher Malwa ...
Pierluigi Paganini
November 16, 2026
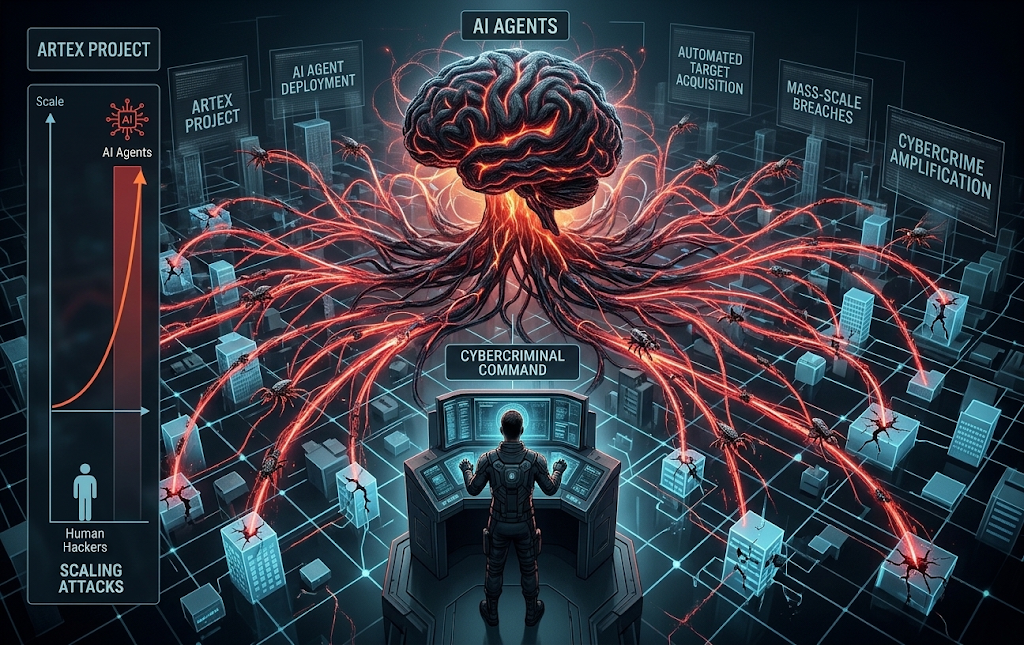
Amazon spotted AI agents running on ARTEX steal AI credentials and test deepfake ID bypasses. Amazon’s threat intelligence team published findings on criminals running offensive campaigns with ...
Pierluigi Paganini
November 16, 2026
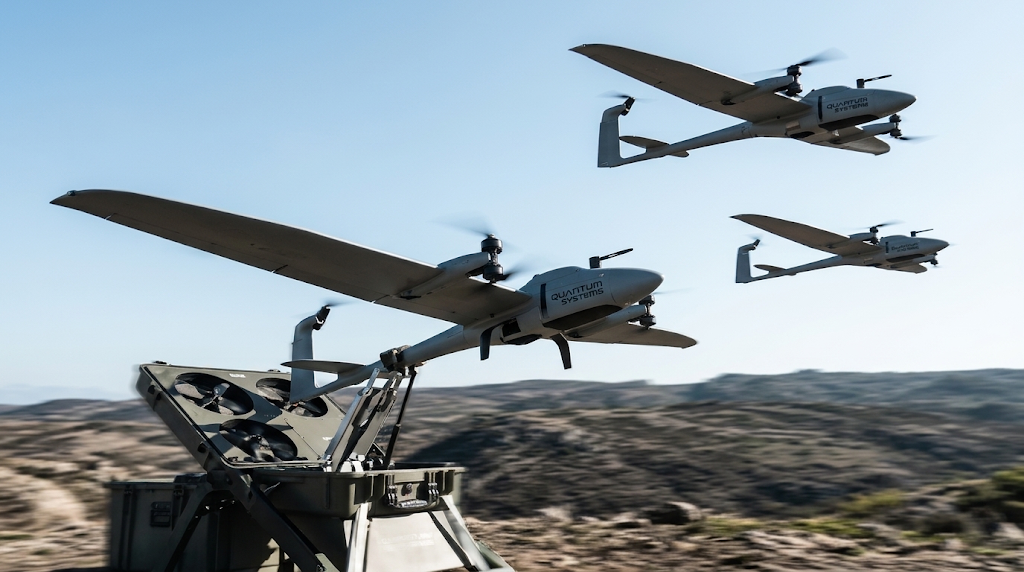
German drone maker Quantum Systems confirms a cyberattack that disrupted operations, with reports pointing to a malicious software update. Quantum Systems, a German defense company that builds rec ...
Pierluigi Paganini
November 16, 2026

Researchers uncover two threat groups, SilentAir and LIMINAL PANDA, exploiting mobile networks to spy on users and intercept calls and text messages. Telecom security firm Enea published research ...
Pierluigi Paganini
November 16, 2026

A Microsoft 365 outage stopped a hotel’s email chlorine alert in Germany, and 15 guests were poisoned. A hotel in Germany had a maintenance safety system for its sauna area. If the chlorine lev ...
Pierluigi Paganini
November 15, 2026

Italy fines Meta €805 million over Facebook's access to Android users' photo galleries without specific consent, affecting around 20 million people. Italy’s data protection authority, the Gara ...
Pierluigi Paganini
November 15, 2026

Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, ...
Pierluigi Paganini
November 15, 2026

Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Exchange for breakfast: Turla’s Cereal ...
Pierluigi Paganini
November 15, 2026

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly Security ...
Pierluigi Paganini
November 15, 2026
A cyberattack on La Poste subsidiary Maileva exposed the names and postal addresses of 22 million people, including patients and tenants. Maileva, a subsidiary of the La Poste group, was hit in mi ...
Pierluigi Paganini
November 15, 2026
Russian extortion group n0n claims to have stolen nearly one billion Expedia traveler records through a compromised third-party provider. A newly formed Russian cyber extortion group called n0n cl ...
Pierluigi Paganini
November 14, 2026

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Check Point and UnrealIRCd flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Securit ...
Pierluigi Paganini
November 14, 2026
The DOJ seized over $1.2 billion from North Korea 's Binance theft, and says the same hackers are targeting open-source developers The U.S. Department of Justice announced two separate but connect ...
Pierluigi Paganini
November 13, 2026